About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: ISO 42001 & AI governance

ISO/IEC 42001 is the first certifiable management-system standard for artificial intelligence. Published in 2023, it specifies how to establish and run an AI Management System — governance for how AI is developed, deployed, monitored and retired.
It follows the same Annex SL structure as ISO 27001 and ISO 9001, so organisations with an existing management system can extend rather than rebuild. What is distinctive is Annex A’s AI-specific controls and the AI impact assessment, which considers effects on individuals and society, not just on the organisation.
Its commercial relevance is tied to the EU AI Act, the world’s first comprehensive AI law, which classifies systems into prohibited, high-risk, limited-risk and minimal-risk tiers and imposes substantial obligations on high-risk systems. ISO 42001 does not make you compliant with the Act, but it is the most credible way to evidence that AI governance is being managed systematically.
The NIST AI Risk Management Framework covers similar ground through four functions — Govern, Map, Measure and Manage — but is voluntary and not certifiable. Many organisations use the RMF to do the risk work and ISO 42001 to get it certified.
The guides below cover ISO 42001’s requirements and Annex A controls, the certification path, the EU AI Act’s risk tiers, deadlines, documentation requirements and scope, and how ISO 42001 compares with the NIST AI RMF.


ISO 42001 internal audit explained

ISO 42001 Internal Audit: A Clear 2026 Guide to Clause 9.2

Governance Docs13th September 2026

An ISO 42001 internal audit under clause 9.2: the 6 things it must show, how it differs from…
Read More
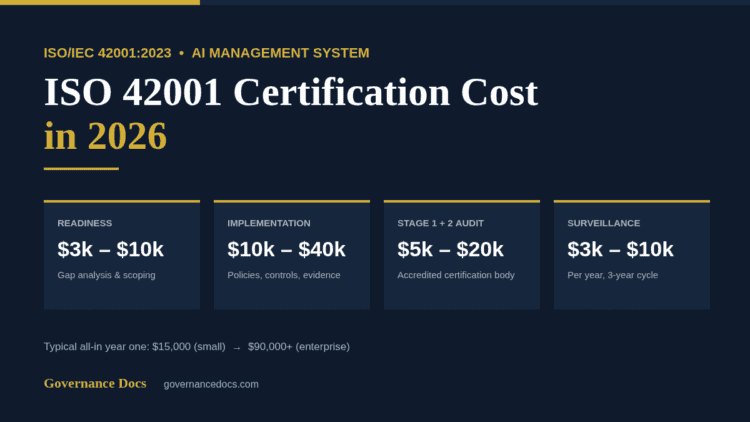
ISO 42001 certification cost breakdown for 2026 showing readiness, implementation, audit and surveillance ranges

ISO 42001 Certification Cost in 2026: A Complete Breakdown

Governance Docs24th August 2026

A practical 2026 breakdown of ISO 42001 certification cost - readiness, implementation, Stage 1 and Stage 2 audit…
Read More
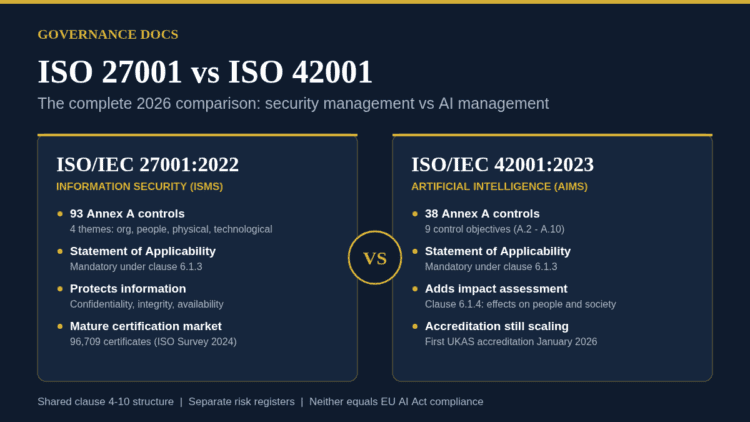
ISO 27001 vs ISO 42001 comparison chart showing 93 security controls against 38 AI controls

ISO 27001 vs ISO 42001: The Complete 2026 Comparison Guide

Governance Docs20th August 2026

ISO 27001 vs ISO 42001 compared for 2026: 93 security controls versus 38 AI controls, the shared clause…
Read More
ISO 42001 controls in Annex A explained including AI policy, data, lifecycle and transparency

ISO 42001 Annex A Controls Explained

Governance Docs17th July 2026

The ISO 42001 Annex A controls turn responsible-AI principles into auditable practice. Here is what they cover and…
Read More
ISO 42001 vs NIST AI RMF comparison of the certifiable standard and the voluntary risk framework

ISO 42001 vs NIST AI RMF: Which AI Framework?

Governance Docs17th July 2026

ISO 42001 vs NIST AI RMF: one is a certifiable standard, the other a voluntary framework. Here are…
Read More
ISO 42001 certification process step by step from building the AIMS to the stage 2 audit

How to Get ISO 42001 Certified: A Step-by-Step Guide

Governance Docs17th July 2026

ISO 42001 certification proves you govern AI responsibly. Here is the step-by-step process, how long it takes, and…
Read More
EU AI Act documentation requirements checklist for high-risk AI systems and deployers

EU AI Act Documentation Requirements Checklist

Governance Docs17th July 2026

Compliance rests on evidence. This EU AI Act documentation requirements checklist covers every record high-risk systems and deployers…
Read More
EU AI Act deadlines and compliance timeline from 2024 to 2027 with key milestones

EU AI Act Compliance Deadlines & Timeline (2025-2028)

Governance Docs17th July 2026

The EU AI Act applies in phases, not on one date. The current timeline from 2024 to 2028…
Read More
EU AI Act risk categories - unacceptable, high, limited and minimal risk tiers explained

EU AI Act Risk Categories: Prohibited, High-Risk & Limited

Governance Docs17th July 2026

Every AI system falls into one of four EU AI Act risk tiers. Here is what prohibited, high,…
Read More
Who does the EU AI Act apply to - provider, deployer, importer and distributor roles

Who Does the EU AI Act Apply To? Provider vs. Deployer

Governance Docs17th July 2026

The EU AI Act applies by role and reaches far beyond Europe. Learn the difference between providers and…
Read More
EU AI Act compliance guide showing the four risk tiers and key obligations

The EU AI Act Explained: A Complete Compliance Guide

Governance Docs17th July 2026

The EU AI Act is the world's first comprehensive AI law. A clear guide to who it applies…
Read More
ISO 42001 explained - the AI management system standard structure and Annex A controls

ISO 42001 Explained: The AI Management System Standard

Governance Docs12th April 2026

ISO 42001 is the world's first AI management system standard. A complete guide to the AIMS, its structure,…
Read More
    ←
  • 1
  • 2
  • 3
  • →

Recent Posts

ISO 27001 information transfer infographic: the three channels under Annex A 5.14 - electronic, physical media and verbal - and the three Statement of Applicability rows they create
ISO 27001 Information Transfer: Complete A.5.14 Guide 2026

October 13, 2026

ISO 27001 ICT readiness (Annex A 5.30): the four verbs in the control statement — planned, implemented, maintained and tested
ISO 27001 ICT Readiness: Complete A.5.30 Guide 2026

October 12, 2026

iso 30301 — ISO 30301 vs ISO 15489: Which Records Standard Do You Need?
ISO 30301 vs ISO 15489: Which Records Standard Do You Need?

October 12, 2026

legal hold — Legal Hold: How to Suspend Records Destruction Properly (2026)
Legal Hold: How to Suspend Records Destruction Properly (2026)

October 12, 2026

records retention schedule — Records Retention Schedule: How to Build One in 2026
Records Retention Schedule: How to Build One in 2026

October 12, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA