

BSI C5 Report Review: A Customer Checklist for 2026
A practical checklist for cloud customers reading a BSI C5 attestation report: scope, deviations, shared responsibility and subservice…
CART
A practical checklist for cloud customers reading a BSI C5 attestation report: scope, deviations, shared responsibility and subservice…
A practical guide to AS9100D clause 8.1.2: how to scope, identify and control configuration, with change control steps…
A practical guide to service provider oversight in your written information security plan under the FTC Safeguards Rule.
Choosing between the UK IDTA and the Addendum for restricted transfers, and the transfer risk assessment that must…
SWIFT CSP non-compliance is visible to supervisors and counterparties. Learn the categories, consequences and a practical recovery plan.
A practical guide to SOX after an IPO: what applies immediately, what the SEC transition period defers and…
Understand how SOC 1 treats subservice organizations: carve-out versus inclusive, CSOCs and the monitoring evidence auditors expect.
Article 12 of the Saudi PDPL requires a privacy policy before collection. See the eight required elements, timing…
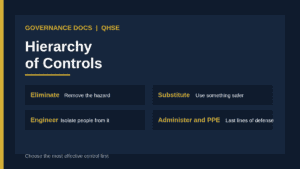
How to use the hierarchy of controls: the five levels from elimination to PPE, how ISO 45001 applies…
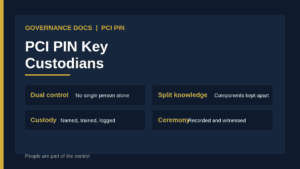
A guide to PCI PIN key custodians: their role, dual control and split knowledge in key components, key…
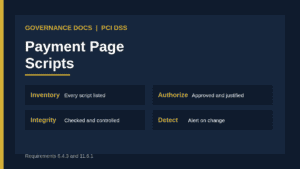
How to meet PCI DSS payment page script requirements 6.4.3 and 11.6.1: script inventory, authorization, integrity, change detection,…
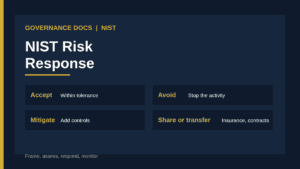
How NIST risk response works: the five response options in SP 800-39, how to choose between them using…
October 19, 2026
October 19, 2026
October 18, 2026
October 18, 2026
October 15, 2026