

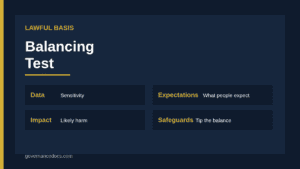
Legitimate Interests Balancing Test Explained 2026
How to run the legitimate interests balancing test: data sensitivity, reasonable expectations, likely impact and safeguards, with a…
CART
How to run the legitimate interests balancing test: data sensitivity, reasonable expectations, likely impact and safeguards, with a…
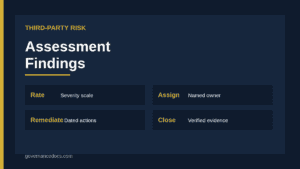
How to record, rate and close third party risk assessment findings so vendor assessments lead to real remediation,…
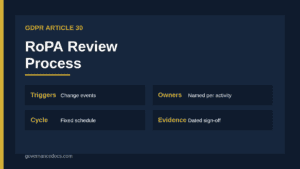
A practical RoPA review process for Article 30 records: what to check, who owns it, how often to…
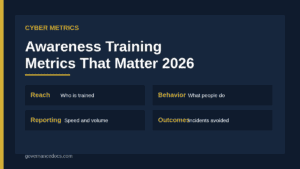
Which security awareness training metrics prove behavior change: reporting rates, phishing outcomes, incident data and program health.
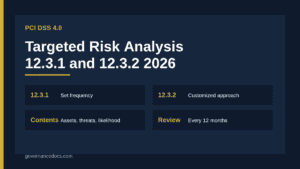
How to write a PCI DSS targeted risk analysis for flexible-frequency requirements and the customized approach, with content…
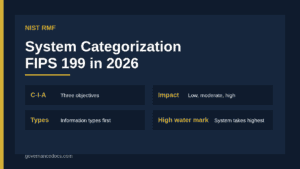
How NIST RMF system categorization works with FIPS 199: impact levels, information types, the high water mark and…
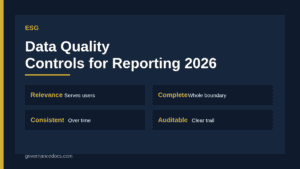
How to improve ESG data quality using the five GHG Protocol principles, data owners, controls and an audit…
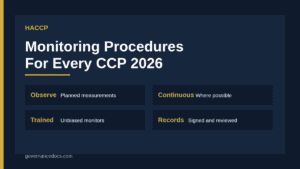
How to set HACCP monitoring procedures for critical control points: methods, frequency, who monitors and record review.
What NCA ECC third-party cybersecurity controls require for contracts, outsourcing and managed services in Saudi Arabia.
What the FTC Safeguards Rule requires for encryption and multi-factor authentication, plus logging, disposal and testing.
How to build one integrated management system risk register that covers quality, environmental and safety risks and opportunities.
A guide to SAMA CSF section 3.3.15: define, approve and test an incident management process and prepare evidence…
October 19, 2026
October 19, 2026
October 18, 2026
October 18, 2026
October 15, 2026