About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 28, 2026

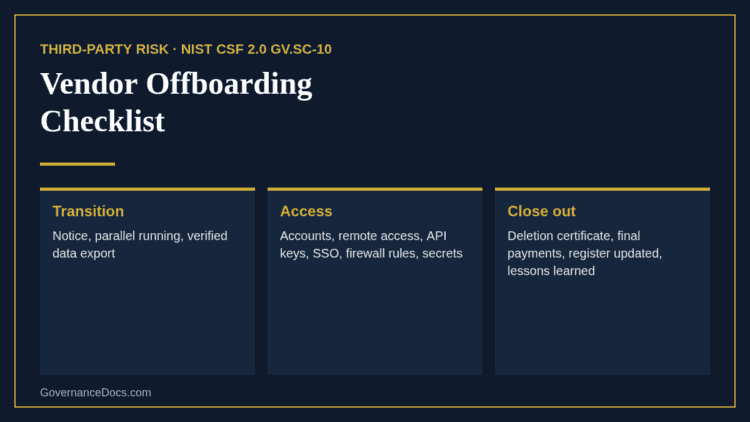
Vendor offboarding checklist phases: transition, access removal and close out

Vendor Offboarding Checklist: The Complete 2026 Guide to Exiting a Vendor

Governance Docs28th September 2026

A vendor offboarding checklist by phase: before notice, transition, access removal, data return and deletion, and close out,…
Read More
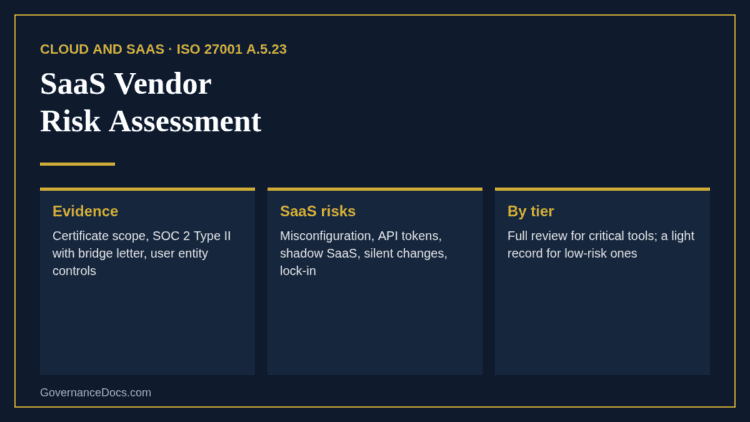
SaaS vendor risk assessment checks: evidence to request, SaaS-specific risks and depth by tier

SaaS Vendor Risk Assessment: The Essential 2026 Guide

Governance Docs28th September 2026

What a SaaS vendor risk assessment should check: assurance scope, tenant isolation, SSO, sub-processors, logs, AI features and…
Read More
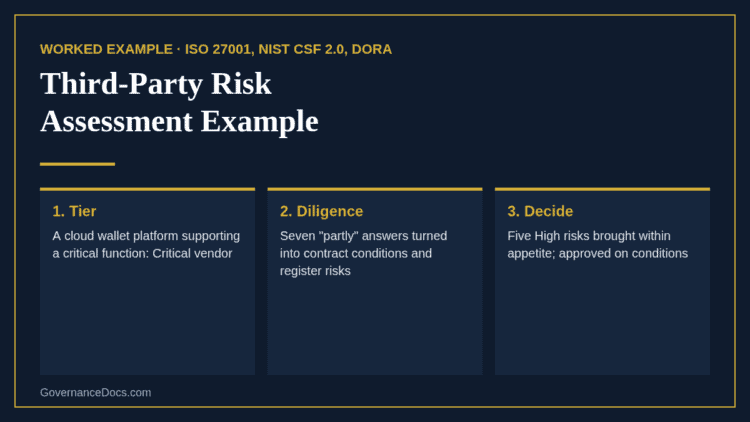
Third-party risk assessment example showing the tier, due diligence and decision for a critical cloud vendor

Third-Party Risk Assessment Example: A Complete 2026 Walkthrough

Governance Docs28th September 2026

A third-party risk assessment example for a fictional payments firm: tiering, the vendor profile, due diligence, five High…
Read More
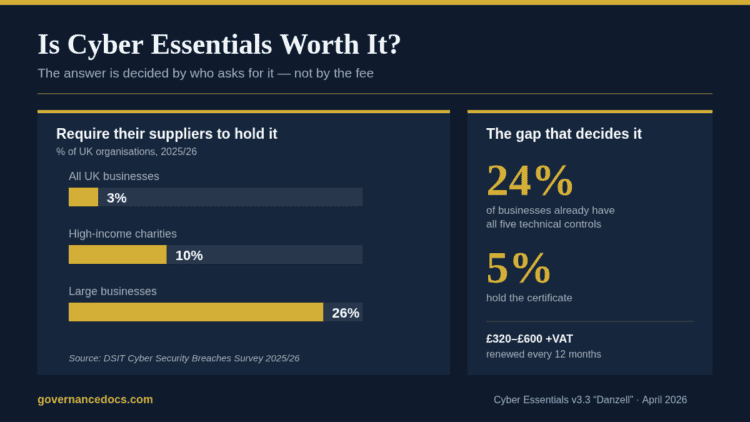
Chart showing why the answer to is Cyber Essentials worth it depends on buyer demand: 3% of UK businesses, 10% of high-income charities and 26% of large businesses require suppliers to hold Cyber Essentials

Is Cyber Essentials Worth It? The Complete 2026 Cost-Benefit Case

Governance Docs28th September 2026

Is Cyber Essentials worth it in 2026? Only 3% of UK businesses require it from suppliers, yet the…
Read More
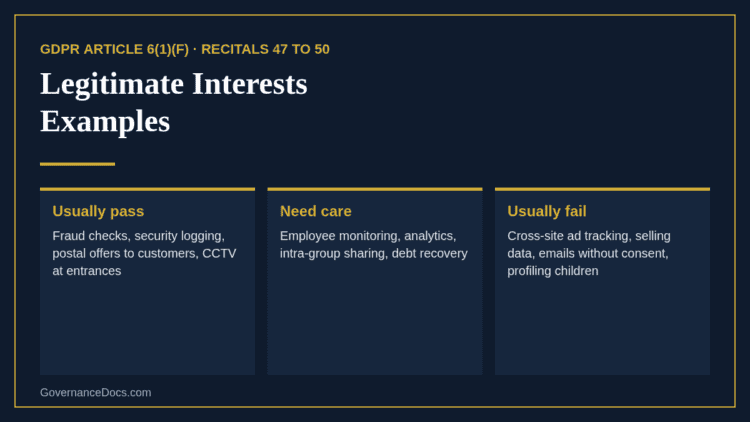
Legitimate interests examples grouped into those that usually pass, need care or usually fail

Legitimate Interests Examples: 12 Proven Cases and Where They Fail (2026)

Governance Docs28th September 2026

Legitimate interests examples from the GDPR recitals and everyday practice: fraud, marketing, security, CCTV, staff monitoring and analytics,…
Read More
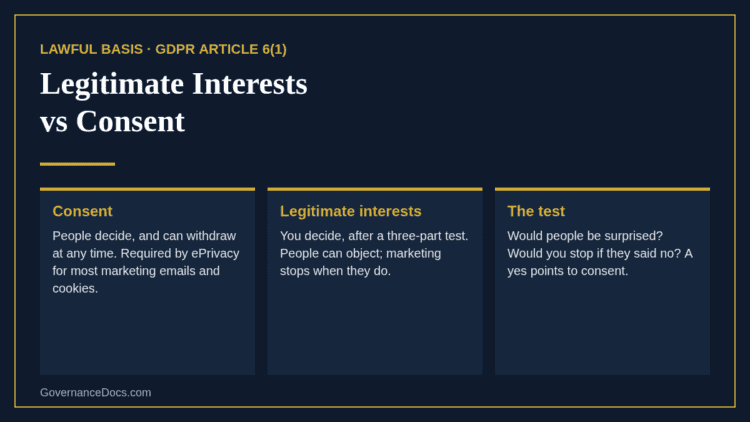
Legitimate interests vs consent compared: who decides, what the law requires and a two-question test

Legitimate Interests vs Consent: The Essential 2026 Guide to Choosing

Governance Docs28th September 2026

Legitimate interests vs consent compared: who decides, what each requires, when ePrivacy rules force consent, the usual basis…
Read More
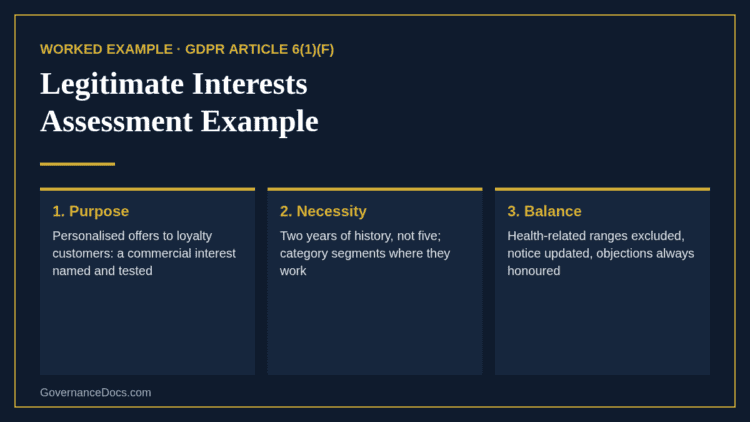
Legitimate interests assessment example showing the purpose, necessity and balancing tests for personalised offers

Legitimate Interests Assessment Example: A Complete 2026 Walkthrough

Governance Docs28th September 2026

A legitimate interests assessment example for a fictional retailer: the screening, the purpose, necessity and balancing tests, the…
Read More
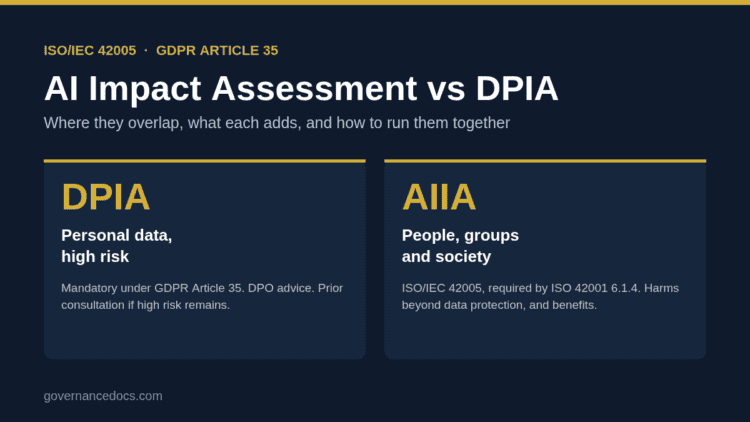
AI impact assessment vs DPIA: ISO 42005 impacts on people and society compared with the GDPR Article 35 DPIA

AI Impact Assessment vs DPIA: The Essential 2026 Guide to Running Both

Governance Docs28th September 2026

AI impact assessment vs DPIA: how an ISO 42005 AI system impact assessment and a GDPR Article 35…
Read More
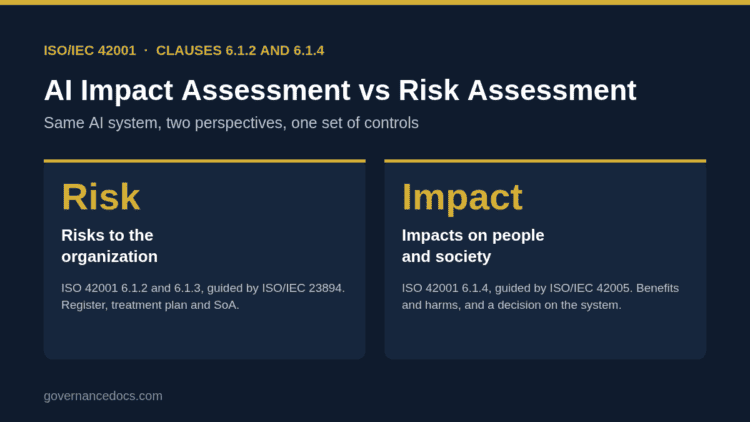
AI impact assessment vs risk assessment: risks to the organization compared with impacts on people and society

AI Impact Assessment vs Risk Assessment: The Essential 2026 Guide for ISO 42001

Governance Docs28th September 2026

AI impact assessment vs risk assessment under ISO 42001: what each covers, how they differ, how the impacts…
Read More
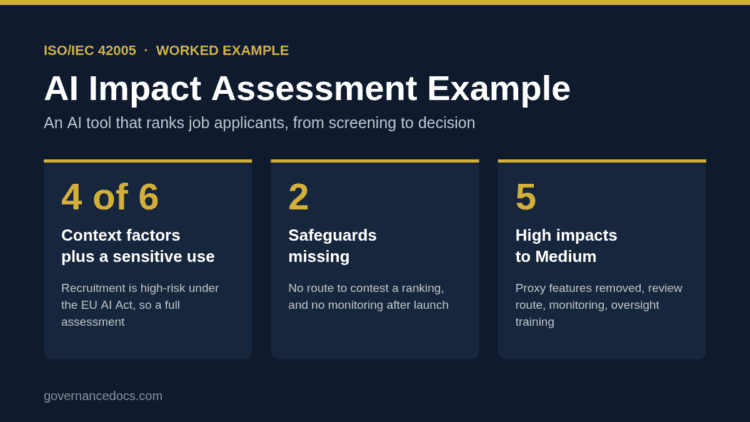
AI impact assessment example: screening, safeguards and impacts for an AI tool that ranks job applicants

AI Impact Assessment Example: A Complete 2026 Walkthrough for ISO 42005

Governance Docs28th September 2026

An AI impact assessment example for a recruitment agency using an AI tool to rank job applicants: screening,…
Read More
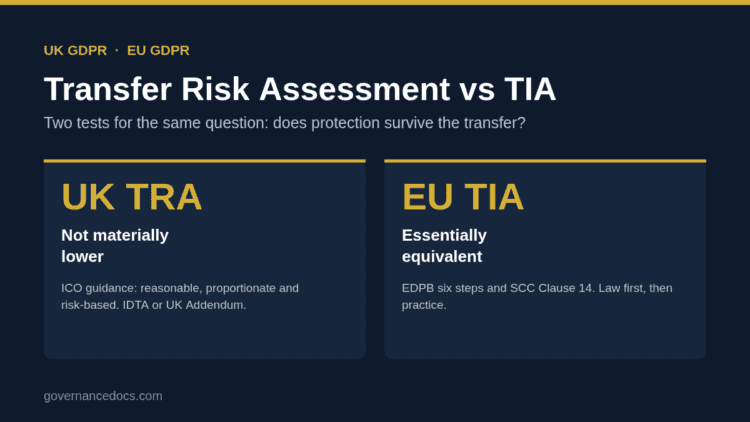
Transfer risk assessment vs TIA: the UK not materially lower test compared with the EU essential equivalence test

Transfer Risk Assessment vs TIA: The Essential 2026 Guide to UK and EU Rules

Governance Docs28th September 2026

Transfer risk assessment vs TIA: how the UK TRA and the EU transfer impact assessment differ, where the…
Read More
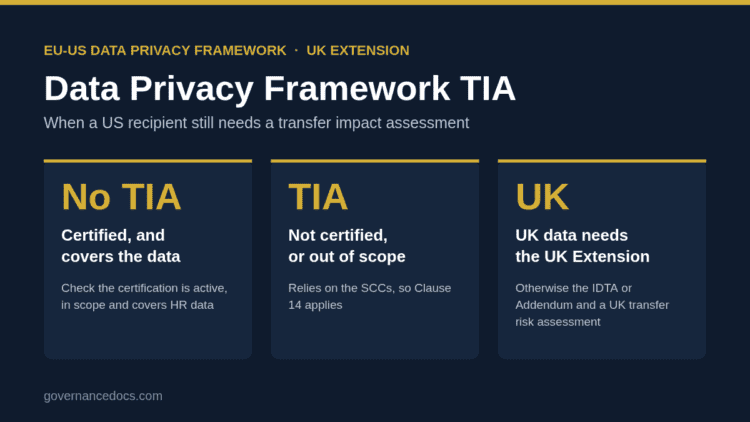
Data Privacy Framework TIA: when a certified US recipient still needs a transfer impact assessment

Data Privacy Framework TIA: When You Still Need One (The Essential 2026 Guide)

Governance Docs28th September 2026

Data Privacy Framework TIA rules: when a DPF certification removes the need for a transfer impact assessment, when…
Read More

  • 1
  • 2
  • →

Recent Posts

ISO 27001 acceptable use policy requirements under Annex A control A.5.10
ISO 27001 Acceptable Use Policy: Complete 2026 Guide

October 19, 2026

ISO 27001 network security controls A.8.20, A.8.21 and A.8.22 compared
ISO 27001 Network Security: Complete A.8.20–8.22 Guide 2026

October 18, 2026

ISO 27001 malware protection under Annex A 8.7: tooling, awareness, controlled access and change management
ISO 27001 Malware Protection: Complete A.8.7 Guide 2026

October 18, 2026

ISO 27001 capacity management under Annex A 8.6 - the three in-scope domains and the two ways to meet the control
ISO 27001 Capacity Management: Complete A.8.6 Guide 2026

October 15, 2026

ISO 27001 web filtering under Annex A 8.23: DNS filtering, network URL filters and endpoint enforcement, with the encrypted DNS bypass gap
ISO 27001 Web Filtering: Complete A.8.23 Guide 2026

October 15, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA