ISO 27001 information security objectives are the part of clause 6 an auditor can test in about five minutes, and the part most documentation sets get wrong. The objectives are usually either slogans nobody can measure — “improve security awareness” — or a wish list copied from a template and never looked at again. Both read the same way in a stage 2 audit: a nonconformity against clause 6.2.
This guide covers what the clause actually demands, the seven tests every objective has to pass, twelve measurable examples you can adapt, and the five mistakes that reliably produce findings.
Free gap assessment
Where do you actually stand against ISO 27001?
Score every management system clause and all 93 Annex A controls, free, and get a prioritised gap list back.
What ISO 27001 Information Security Objectives Actually Are
An objective is a measurable outcome the management system is supposed to deliver. It is not a control, it is not a risk, and it is not a line in the security team’s budget request. Clause 6.2 requires the organization to establish objectives “at relevant functions and levels” — so one corporate objective plus a handful owned by IT, HR and operations is a normal shape, not a sign you have overcomplicated it.
The distinction that matters at audit is objectives versus controls. The 93 Annex A controls in ISO/IEC 27001:2022 — organized into four themes, with 37 organizational, 8 people, 14 physical and 34 technological — are how you treat risk. Objectives are what you are trying to achieve. “Implement multi-factor authentication” is a control decision that belongs in your risk treatment plan and your Statement of Applicability. “Reduce successful credential-phishing logins to zero across all privileged accounts by Q3” is an objective.
Free ISO 27001 risk assessment
Which of your risks sit above your appetite line?
Set your own risk criteria, pick from 61 information security risk scenarios, rate likelihood and impact, and decide how to treat each one. You get a heat map, a process score and the findings an auditor would raise, free.
One more thing worth being clear about: ISO 27001 information security objectives are themselves mandatory documented information. Clause 6.2 g) says they shall be available as documented information, so an ISMS with objectives that live only in a slide deck from last year’s kickoff is non-conformant on paper before an auditor looks at a single metric.
Clause 6.2: The Seven Tests Every Objective Must Pass
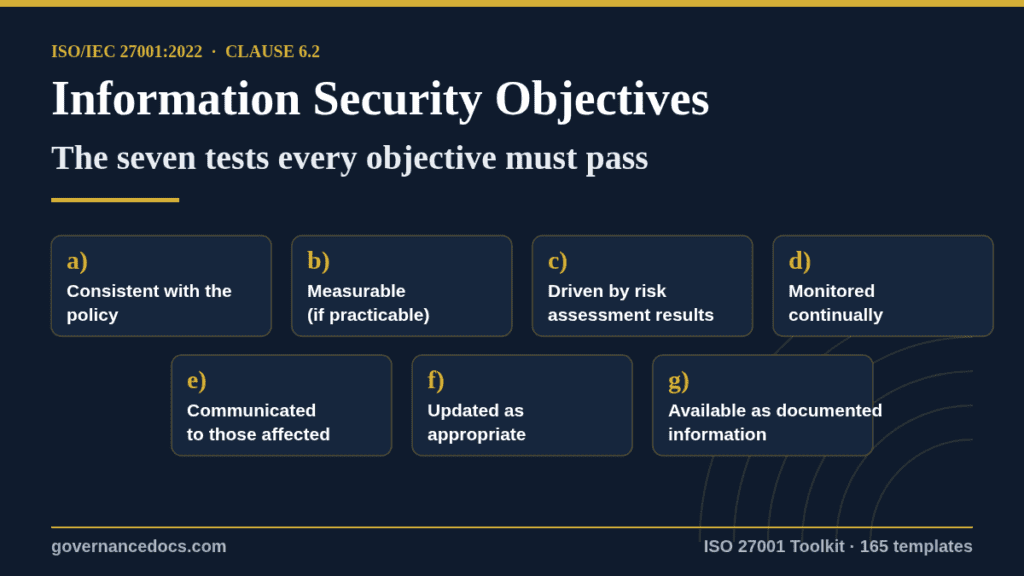
Clause 6.2 lists seven characteristics that ISO 27001 information security objectives must have. Treat them as a checklist and run every objective through it before it goes into your register.
Clause 6.2
Requirement
What the auditor asks to see
a)
Consistent with the information security policy
A traceable line from a policy commitment to the objective
b)
Measurable, if practicable
A number, a unit and a baseline — not an adjective
c)
Take into account applicable information security requirements and the results of risk assessment and risk treatment
Which risk, contract clause or legal duty drove this objective
d)
Be monitored
Dated measurement records across the year, not one reading
e)
Be communicated
Evidence the owners and affected staff were actually told
f)
Be updated as appropriate
A revision history showing objectives changed when risks did
g)
Be available as documented information
A controlled objectives register with an approval record
Two of those seven are additions in the 2022 edition relative to 2013: d) be monitored, and g) be available as documented information. If your objectives register was written against the old edition and you transitioned late — the 2013 to 2022 transition period closed on 31 October 2025, so every certificate in force now is a 2022 certificate — these are the two gaps most likely to still be open. Monitoring is the one that bites: a single annual reading taken the week before the audit does not demonstrate that an objective is monitored.
The Planning Half of the Clause Most Registers Miss
Clause 6.2 does not stop at the characteristics. It then requires that, when planning how to achieve its objectives, the organization determines what will be done, what resources will be required, who will be responsible, when it will be completed, and how the results will be evaluated.
Those five determinations are why a two-column table of ISO 27001 information security objectives fails. A compliant register needs columns for the objective, the target and baseline, the actions, the resources, the owner, the due date and the evaluation method. Most organizations already hold this information — it is scattered across a project plan, a budget line and someone’s head. The clause just requires it in one place you can hand over.
12 Measurable ISO 27001 Information Security Objectives Examples
These are illustrative. Copy the shape — a metric, a baseline, a target and a date — and set the numbers from your own risk assessment results and your own starting position. An objective with a target you cannot justify from a baseline is worse than no objective at all.
#
Objective
Metric and target
Typical owner
1
Close critical technical vulnerabilities inside the agreed window
% of CVSS-critical findings remediated within 14 days; target 95% each quarter
IT operations
2
Eliminate standing privileged access
Number of permanent domain admin accounts; target 0 by year end
Infrastructure lead
3
Keep the risk treatment plan current
% of treatment actions past due date; target under 10% at every monthly review
ISMS manager
4
Detect and report incidents faster
Median time from detection to internal report; target under 4 hours
Security operations
5
Complete role-based security training
% of staff in scope completing assigned training; target 100% within 30 days of hire
HR
6
Reduce phishing susceptibility
Click rate in simulated phishing; target below 5% by Q4 from a measured baseline
Awareness owner
7
Assess every new supplier before data is shared
% of new suppliers with a completed security assessment before contract signature; target 100%
Procurement
8
Prove backups restore
Number of documented restore tests per year; target 2, both successful
IT operations
9
Keep the asset inventory accurate
% of sampled assets with a correct owner and classification; target 98% per quarter
Asset owner
10
Remove access on the day someone leaves
% of leavers with all access revoked within 24 hours; target 100%
HR and IT jointly
11
Clear internal audit findings on schedule
% of nonconformities closed by their agreed date; target 90%
ISMS manager
12
Hold the certification scope stable through surveillance
Number of major nonconformities at surveillance audits; target 0
Top management
Twelve is not a requirement, and it is more than many organizations need. A 40-person SaaS company with a tight scope can run a credible ISMS on five or six. What matters is that each one traces to something in your risk picture and that somebody is accountable for the number.
How ISO 27001 Information Security Objectives Connect to the Rest of the ISMS
ISO 27001 information security objectives are a hub, not a leaf. Five other clauses reach into them, and a weak objectives register shows up as findings somewhere else entirely.
Clause 5.2 b) — the information security policy must either include the objectives or provide the framework for setting them. Pick one approach and make the policy say which.
Clause 7.4 — communication. Requirement 6.2 e) is satisfied through your communication plan, so the objectives need to appear in it with an audience and a frequency.
Clause 9.1 — monitoring, measurement, analysis and evaluation. This is where the methods behind your metrics get documented. If 9.1 is thin, 6.2 d) has nothing to stand on.
Clause 9.3.2 — management review inputs. Item d) requires feedback on information security performance including trends in nonconformities and corrective actions, monitoring and measurement results, audit results, and fulfilment of the information security objectives. Your management review minutes have to show the objectives were discussed with numbers attached.
Clause 6.3 — planning of changes, new in the 2022 edition. A reorganization or a new product line that shifts your risk profile is the trigger for 6.2 f), updating objectives.
Read in sequence, the chain is simple: the policy frames them, the risk assessment justifies them, clause 9.1 measures them, and management review judges them. Break any link and the others stop making sense.
Five Mistakes That Turn Objectives Into Audit Findings
Most findings against clause 6.2 trace back to the same five problems. Run your ISO 27001 information security objectives past all five before an internal audit, not after one.
1. Objectives that are really controls. “Deploy a SIEM” is a project. Convert it: what will the SIEM let you achieve that you can count?
2. A target with no baseline. “Reduce incidents by 20%” is unauditable if you never recorded last year’s number. Measure first, set the target second.
3. Ownership assigned to a committee. If the owner column says “Security Steering Group,” nobody owns it. Name a role.
4. One annual reading. This is the most common failure against 6.2 d). Decide the measurement cadence — monthly or quarterly for most metrics — and keep the dated records.
5. Objectives nobody outside the ISMS team has seen. Clause 6.2 e) is a separate requirement from documenting them. Auditors test it by asking a department manager what their security objective is.
Worth noting what is not a mistake: having fewer objectives than you had last year. Retiring an objective that has been met and holding steady is a legitimate outcome under 6.2 f), as long as the decision is recorded.
Frequently Asked Questions
Are ISO 27001 information security objectives mandatory documented information?
Yes. Clause 6.2 g) requires them to be available as documented information, which puts the objectives register on the list of documents an auditor will expect to see alongside the scope, the policy and the Statement of Applicability. Our mandatory documents checklist sets out the full set.
How many ISO 27001 information security objectives do you need?
The standard sets no number. It requires objectives at relevant functions and levels, which means the right count is whatever covers your significant risks and your scope without producing a register nobody maintains. Five to twelve is the usual range.
Can an objective be qualitative?
Clause 6.2 b) says measurable “if practicable,” so there is room — but the exception is narrower than people hope. If you claim an objective cannot be measured, record why, and expect the auditor to probe it. In practice almost anything has a countable proxy: coverage, completion rate, elapsed time or defect count.
Who approves them?
Top management, in substance if not in signature. Clause 5.1 makes top management accountable for the ISMS and 5.2 puts the objectives framework in the policy they establish, so approval at management review is the cleanest evidence. A register approved only by the ISMS manager invites a clause 5 question.
Do ISO 27001 information security objectives need to change for the 2022 edition?
The characteristics did change — monitoring and documented information were added — so a register written against the 2013 edition usually needs a measurement cadence and a controlled approval record rather than new objectives. Check it against the seven tests above. The free Amendment 1:2024 climate action change touched clauses 4.1 and 4.2, not clause 6.2, but if climate became a relevant issue in your context analysis, 6.2 c) is the route by which it reaches your objectives.
Where to Start
If you are building the register from scratch, work backwards: take the top five risks from your risk assessment, ask what outcome would tell you each one is under control, then attach a metric and an owner. That produces defensible ISO 27001 information security objectives faster than starting from a list of good ideas. For the wider picture of how clause 6.2 sits inside the standard, start with our guide to ISO 27001 and what it covers, and read the clause text itself on the official ISO 27001 standard page.
If you would rather not draft the register, the objectives form, communication plan and measurement procedure that go with clause 6.2 are already written in the ISO 27001 Toolkit — 165 templates covering the full management system for $99, ready to tailor to your scope.