About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Management systems

A management system is the documented set of policies, processes and records an organisation uses to run one aspect of its business and prove it is under control. ISO publishes them for quality, information security, environment, occupational health and safety, business continuity, IT service management and more.
Since ISO adopted the Annex SL high-level structure, they share a common skeleton: clauses 4 to 10, covering context, leadership, planning, support, operation, performance evaluation and improvement. Clause 4 has the same shape whether you are reading ISO 9001, ISO 14001 or ISO 45001.
That shared structure is what makes an integrated management system practical. Rather than three sets of policies, three internal audit programmes and three management reviews, you run one system that satisfies several standards at once. Organisations that integrate typically cut audit time and eliminate the contradictions that appear when parallel systems drift apart.
The guides below cover integrated and unified management systems, and the individual standards for environment (ISO 14001), occupational health and safety (ISO 45001), business continuity (ISO 22301), IT service management (ISO 20000) and sector-specific quality standards for medical devices, automotive and food safety.


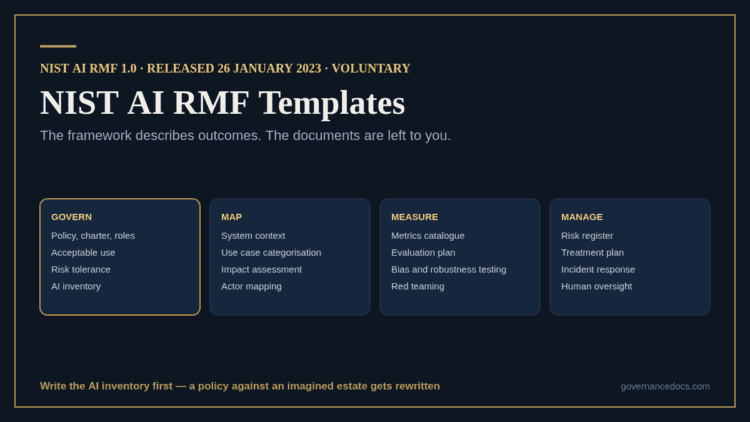
NIST AI RMF templates mapped to the Govern, Map, Measure and Manage functions

NIST AI RMF Templates: A Clear Guide to All 4 Functions

Governance Docs31st August 2026

NIST AI RMF templates are the question the framework will not answer. What Govern, Map, Measure and Manage…
Read More
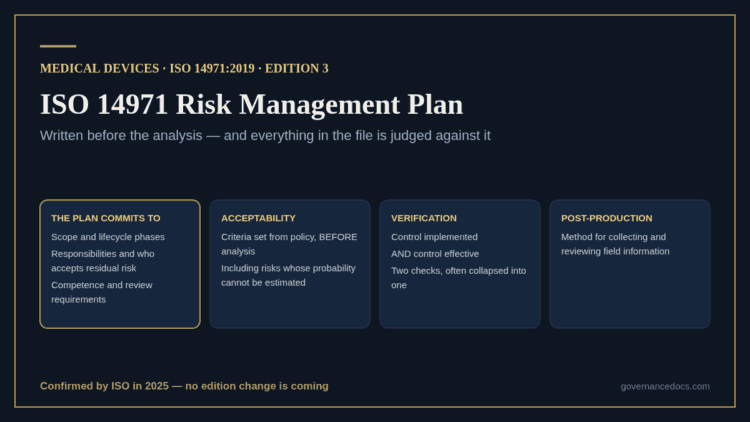
ISO 14971 risk management plan: what it commits you to and how the file is judged against it

ISO 14971 Risk Management Plan: A Clear Guide to Its Content

Governance Docs31st August 2026

The ISO 14971 risk management plan is written before the analysis and judged against everything after it. What…
Read More
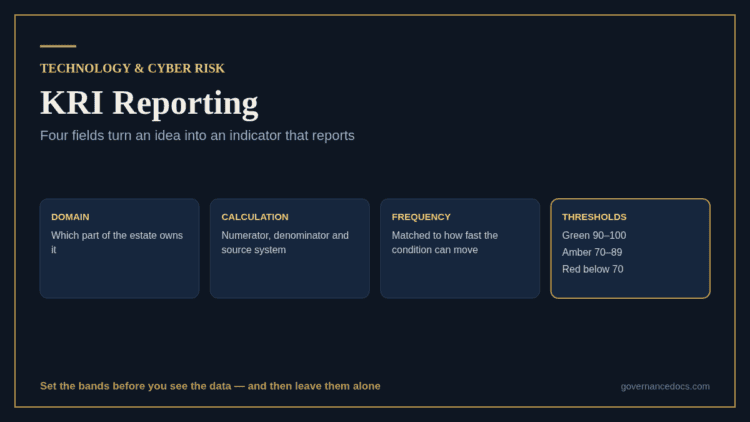
KRI reporting: the four fields every key risk indicator needs before it can report

KRI Reporting: A Clear Guide to the 4 Core Fields

Governance Docs31st August 2026

KRI reporting fails when indicators are picked for easy data. The 4 fields every KRI needs, RAG thresholds…
Read More
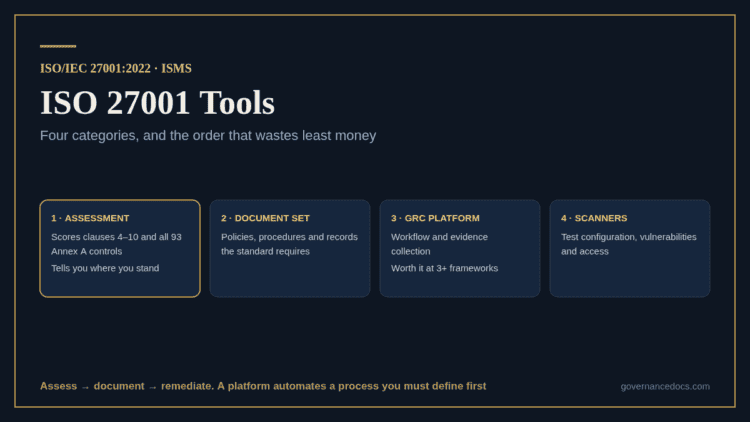
The four categories of ISO 27001 tools and when each one is worth buying

ISO 27001 Tools: Complete Guide to the 4 Categories

Governance Docs31st August 2026

ISO 27001 tools range from a spreadsheet to a GRC platform. The 4 categories, what an assessment tool…
Read More
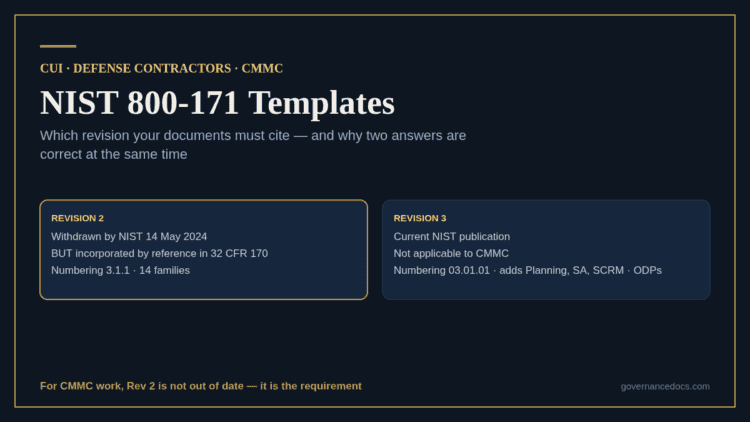
NIST 800-171 templates: why Rev 2 remains the CMMC requirement though NIST withdrew it

NIST 800-171 Templates: Complete Rev 2 Document Set Guide

Governance Docs31st August 2026

NIST 800-171 templates must cite the right revision. Why CMMC still requires Rev 2 though NIST withdrew it,…
Read More
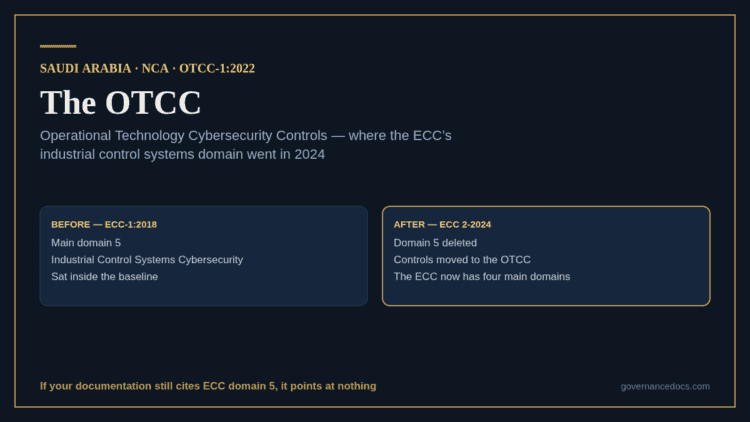
The OTCC absorbed the ECC main domain 5 for industrial control systems

OTCC: A Clear Guide to Saudi OT Cybersecurity in 2026

Governance Docs30th August 2026

The OTCC absorbed the ECC's industrial control systems domain in 2024. What it covers, how it differs from…
Read More
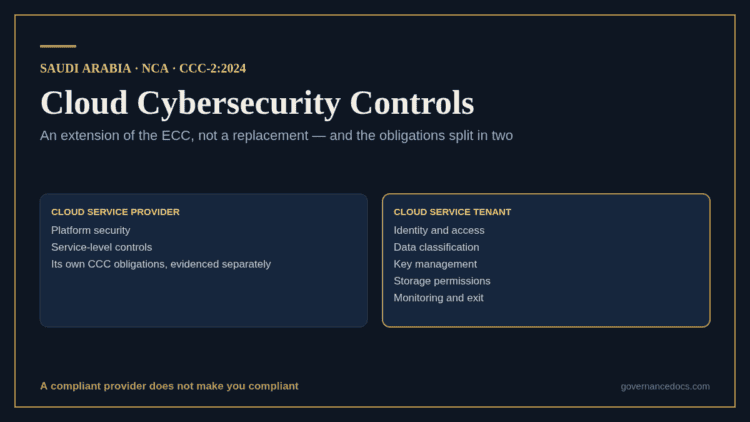
Cloud Cybersecurity Controls: how CCC-2:2024 splits obligations between provider and tenant

Cloud Cybersecurity Controls: A Clear CCC-2:2024 Guide

Governance Docs30th August 2026

The Cloud Cybersecurity Controls split obligations between provider and tenant. CCC-2:2024, the 6 responsibility areas, and what changed…
Read More
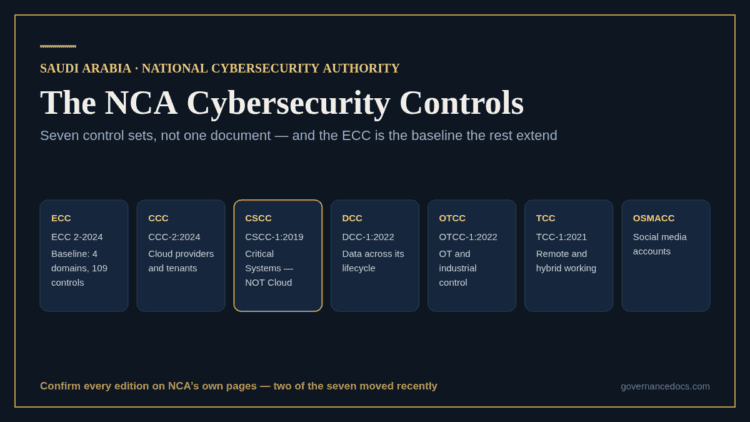
Overview of Saudi Arabia's NCA cybersecurity control sets and standards.

NCA Cybersecurity Controls: A Clear Guide to All 7 Sets

Governance Docs30th August 2026

The 7 NCA cybersecurity controls sets and their current editions, which apply to you, and why CSCC is…
Read More
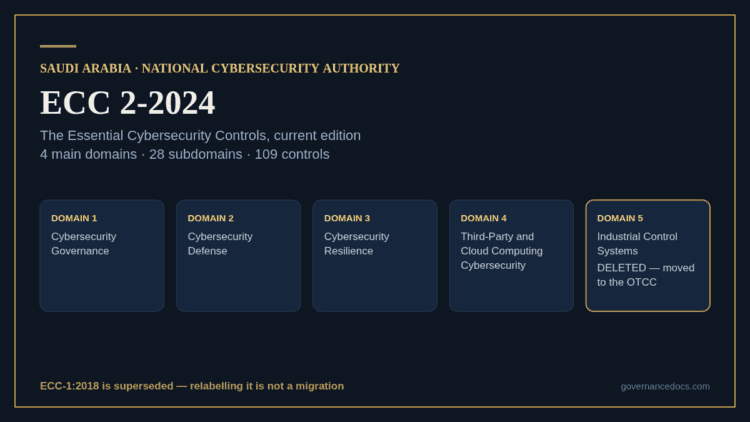
Saudi Arabia National Cybersecurity Authority ECC 2-2024 document overview.

ECC 2-2024: A Clear Guide to All 4 Domains

Governance Docs30th August 2026

ECC 2-2024 replaced ECC-1:2018 and deleted a whole domain. The 4 domains, 109 controls, where the ICS controls…
Read More
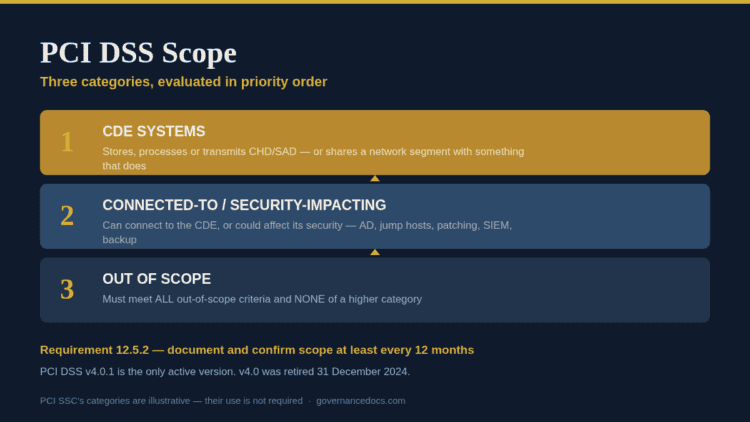
Diagram showing PCI DSS scope categories and their importance in security.

PCI DSS Scope: A Clear Guide to All 3 Categories

Governance Docs30th August 2026

How PCI DSS scope is decided: the 3 system categories in priority order, the annual confirmation under Requirement…
Read More
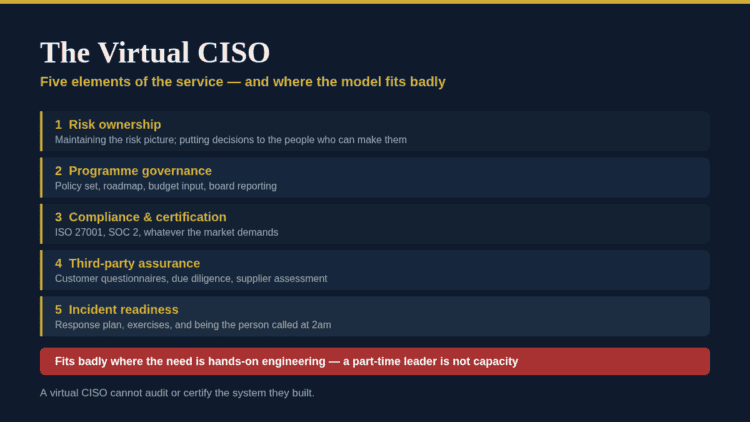
Visual overview of the Virtual CISO's five key service elements for cybersecurity governance.

Virtual CISO: A Clear Guide to All 5 Service Elements

Governance Docs30th August 2026

What a virtual CISO does, the 5 elements of the service, how to structure and price an engagement,…
Read More
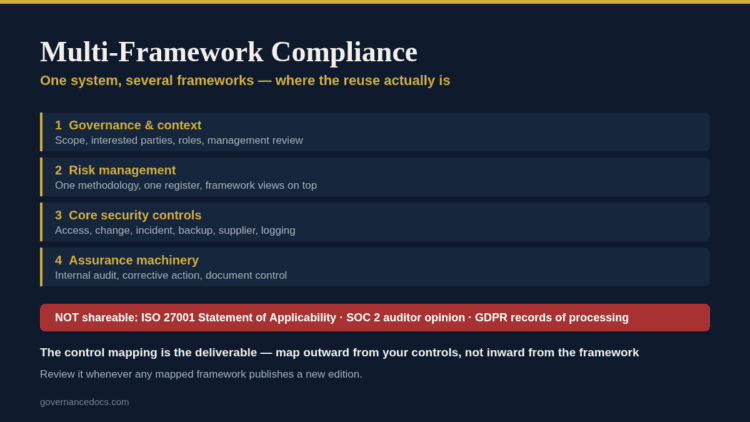
Diagram illustrating multi-framework compliance in governance systems.

Multi-Framework Compliance: A Clear Guide to 4 Overlaps

Governance Docs30th August 2026

Multi-framework compliance done once: the 4 areas that genuinely overlap, what cannot be shared, and why the control…
Read More
    ←
  • 1
  • …
  • 19
  • 20
  • 21
  • 22
  • 23
  • …
  • 36
  • →

Recent Posts

ISO 13485 certification timeline infographic: 6–18 months from kickoff to certificate, phase by phase
ISO 13485 Certification Timeline: The Complete 2026 Guide

September 20, 2026

ISO 27001 vs HIPAA infographic comparing the voluntary ISO/IEC 27001:2022 standard with the HIPAA federal law on scope, controls, proof and consequences
ISO 27001 vs HIPAA: 7 Essential Differences Explained (2026)

September 20, 2026

HITRUST vs ISO 27001 comparison: issuer, controls, scoring, validity and recognition side by side
HITRUST vs ISO 27001: 7 Essential Differences Explained (2026)

September 19, 2026

compliance consultant certifications explained
Compliance Consultant Certifications: 6 Essential Credentials

September 19, 2026

fixed fee vs time and materials explained
Fixed Fee vs Time and Materials: A Clear Guide for Consultants

September 19, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA