About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

Financial services compliance regimes compared: Basel III, the SAMA Cyber Security Framework and MiCA

Financial Services Compliance: 3 Essential Regimes

Governance Docs12th August 2026

There is no single rulebook for finance. Financial services compliance is a patchwork determined by what you do and where you do it — a bank in Riyadh, a European
Read More
QHSE management system combining ISO 9001, ISO 45001, ISO 14001 and ISO 22000

QHSE Management System: 4 Essential Standards Combined

Governance Docs12th August 2026

Most organisations arrive at quality, health and safety, and environment separately — three managers, three manuals, three audit schedules, three sets of paperwork that say much the same thing. A
Read More
SOX compliance and the COSO framework: the five steps of the ICFR cycle

SOX Compliance: 5 Essential Steps to ICFR Readiness

Governance Docs12th August 2026

Sarbanes-Oxley made internal control a named personal responsibility: under Sections 302 and 404, executives sign to say the controls over financial reporting work, and auditors test whether that signature is
Read More
HITRUST vs HIPAA compared: the federal law and the certifiable framework

HITRUST vs HIPAA: 5 Essential Differences and When to Certify

Governance Docs12th August 2026

Healthcare vendors get asked for HIPAA compliance constantly, and increasingly for HITRUST certification as well. The two are often spoken of as if they were alternatives, which they are not.
Read More
Cloud security certification routes compared: FedRAMP, StateRAMP, CSA STAR and BSI C5

Cloud Security Certification: 4 Essential Routes Compared

Governance Docs12th August 2026

Sooner or later a prospect asks a cloud provider to prove its security, and the honest first answer is a question: prove it to whom? There is no single cloud
Read More
NIST SP 800-30 risk assessment — the four-step method for assessing information security risk

NIST SP 800-30 Risk Assessment: The 4 Essential Steps

Governance Docs12th August 2026

A NIST SP 800-30 risk assessment is how you work out which risks actually matter to your organisation. The NIST Cybersecurity Framework tells you what good security looks like. It
Read More
Cybersecurity KRIs versus KPIs — what each indicator measures and what belongs in a board report

Cybersecurity KRIs vs KPIs: 5 Clear Rules for Board Reporting

Governance Docs12th August 2026

Every security team is asked the same question by its board sooner or later: are we getting safer? Answering it means reporting numbers — and that is where cybersecurity KRIs

Read More
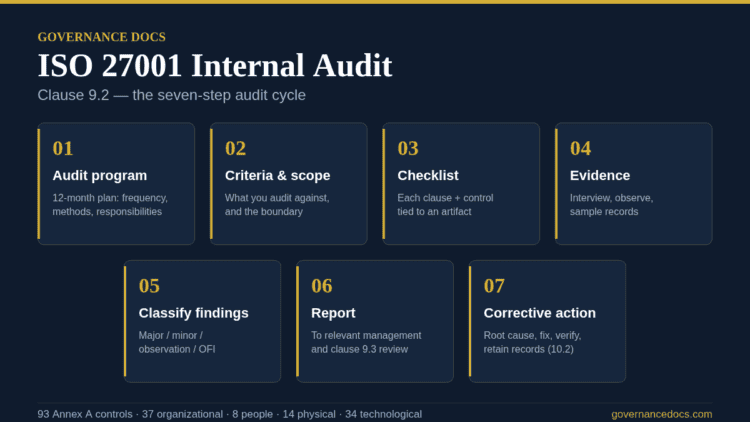
ISO 27001 internal audit seven-step cycle under clause 9.2, from audit program to corrective action

ISO 27001 Internal Audit: The Complete 2026 Guide to Clause 9.2

Governance Docs11th August 2026

What ISO 27001 clause 9.2 requires from an internal audit, who can run it, a seven-step method, and…
Read More
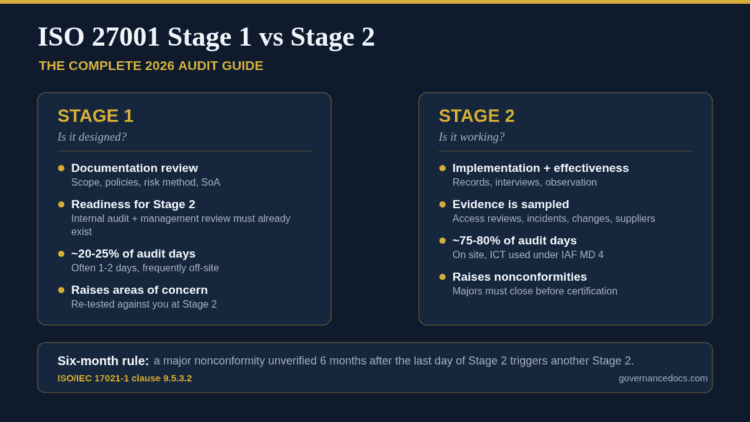
ISO 27001 Stage 1 vs Stage 2 audit comparison infographic

ISO 27001 Stage 1 vs Stage 2: The Complete 2026 Audit Guide

Governance Docs10th August 2026

ISO 27001 Stage 1 vs Stage 2 explained by clause: what each audit checks, how audit days are…
Read More
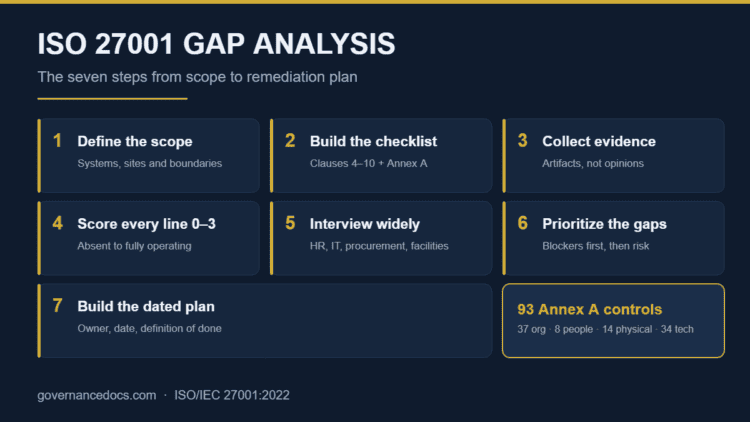
ISO 27001 gap analysis chart for governance documentation and compliance.

ISO 27001 Gap Analysis: The Complete 2026 Step-by-Step Guide

Governance Docs09th August 2026

An ISO 27001 gap analysis compares what you actually do against clauses 4-10 and the 93 Annex A…
Read More
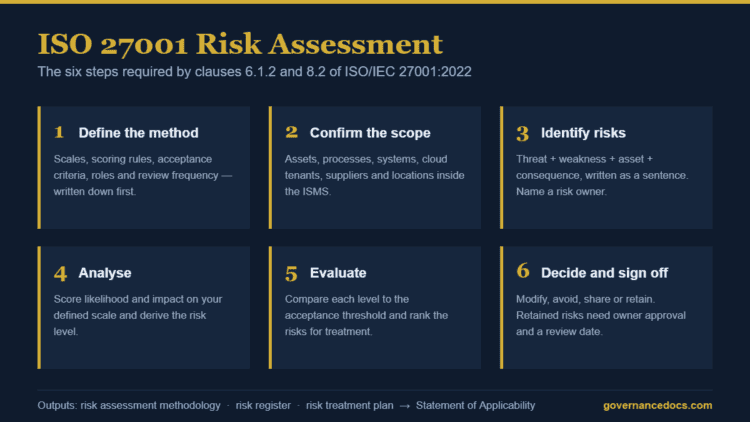
ISO 27001 risk assessment process showing the six steps from criteria to treatment decision

ISO 27001 Risk Assessment: The Complete 2026 Method

Governance Docs07th August 2026

How to run an ISO 27001 risk assessment that survives an audit: what clause 6.1.2 actually requires, the…
Read More
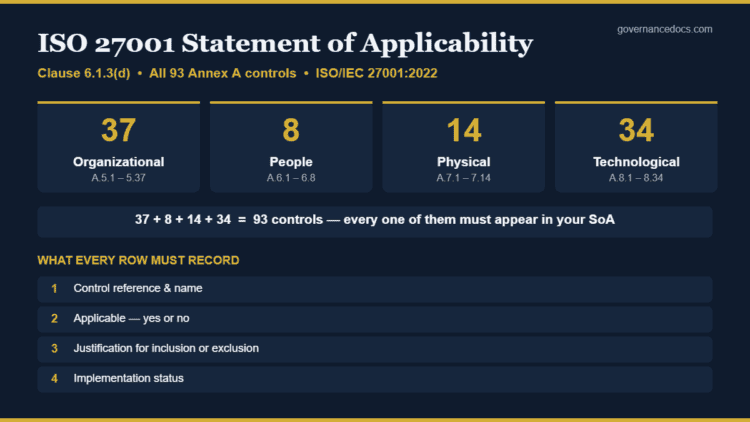
ISO 27001 Statement of Applicability infographic showing all 93 Annex A controls across four themes

ISO 27001 Statement of Applicability: The Complete 2026 Guide

Governance Docs06th August 2026

The ISO 27001 Statement of Applicability is mandatory under clause 6.1.3(d). What it must contain for all 93…
Read More
    ←
  • 1
  • …
  • 91
  • 92
  • 93
  • 94
  • 95
  • …
  • 99
  • →

Recent Posts

ISO 27001 configuration management requirements under Annex A 8.9 - established, documented, implemented, monitored, reviewed
ISO 27001 Configuration Management: Complete 2026 Guide

October 11, 2026

internal audit findings rating scale — Internal Audit Findings Rating Scale: Examples and Template
Internal Audit Findings Rating Scale: Examples and Template

October 11, 2026

third party topical requirement — Third Party Topical Requirement: The 2026 Audit Guide
Third Party Topical Requirement: The 2026 Audit Guide

October 11, 2026

cybersecurity topical requirement — Cybersecurity Topical Requirement: How to Audit It in 2026
Cybersecurity Topical Requirement: How to Audit It in 2026

October 11, 2026

quality assurance and improvement program — Quality Assurance and Improvement Program (QAIP): 2026 Guide
Quality Assurance and Improvement Program (QAIP): 2026 Guide

October 11, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA