About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

ISO 15189 explained — medical laboratory accreditation

ISO 15189: Patients, Pre-examination and Where Medical Laboratories Lose Findings

Governance Docs13th August 2026

What ISO 15189:2022 requires, what the fourth edition changed, and the four areas where medical laboratories most often…
Read More
Proficiency testing for laboratory accreditation

Proficiency Testing: Coverage, Scores and What Follows a Bad Result

Governance Docs12th August 2026

Internal controls tell a laboratory it is consistent. Only comparison with others tells it whether it is right.…
Read More
Decision rules and statements of conformity under ISO 17025

Decision Rules and Statements of Conformity Under ISO 17025

Governance Docs12th August 2026

You measure 9.8 against a maximum of 10.0, with an uncertainty of 0.4. Does it pass? It depends…
Read More
Measurement uncertainty budget for testing and calibration laboratories

Measurement Uncertainty: How to Build a Budget That Holds Up

Governance Docs12th August 2026

A budget built from repeatability alone can understate uncertainty fourfold. How contributions are identified, converted and combined, with…
Read More
ISO 17025 accreditation for testing and calibration laboratories

ISO 17025: Accreditation, Scope and Where Laboratories Lose Findings

Governance Docs12th August 2026

Laboratories are accredited, not certified — and only for a defined scope. What ISO 17025 requires, how Option…
Read More
ISO 27017 and ISO 27018 cloud security controls

ISO 27017: Cloud Security Controls and What the 2026 Edition Changes

Governance Docs12th August 2026

ISO 27017 is not a certification. Here is what the standard actually contains, how it differs from ISO…
Read More
Aerospace quality management: the AS9100, AS9110 and AS9120 standards and the NQA-1 nuclear parallel

Aerospace Quality Management: 3 Essential AS9100 Standards

Governance Docs12th August 2026

In most industries a quality escape costs money. In aerospace and nuclear it can cost lives, and the quality regimes reflect that. Aerospace quality management under the AS9100 family, and
Read More
Supply chain security compared: ISO 28000 for goods and TISAX for automotive information security

Supply Chain Security: 2 Essential Assurance Routes

Governance Docs12th August 2026

Ask two companies how they prove supply chain security and you will get two unrelated answers. One will describe physical controls over goods in transit; the other will describe how
Read More
ISO 55001 asset management, ISO 41001 facility management and ISO 50001 energy management compared

ISO 55001 vs ISO 41001 vs ISO 50001: Which One Do You Need?

Governance Docs12th August 2026

ISO 55001, ISO 41001 and ISO 50001 manage different things about the same estate. What each one actually…
Read More
IT governance framework layers compared: COBIT 2019 for governance, ISO 31000 for risk, CIS Controls for implementation

IT Governance Framework: 3 Essential Layers Explained

Governance Docs12th August 2026

Teams adopting COBIT, ISO 31000 and the CIS Controls often assume they are choosing between them. They are not. Each occupies a different layer of the same problem, and an
Read More
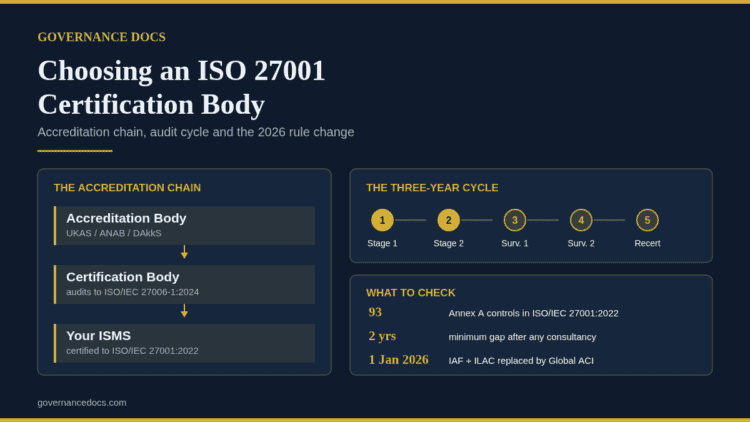
ISO 27001 certification body accreditation chain and three-year audit cycle

How to Choose an ISO 27001 Certification Body: The Complete 2026 Guide

Governance Docs12th August 2026

A practical 2026 guide to choosing an accredited ISO 27001 certification body: what changed on 1 January 2026,…
Read More
SWIFT CSP attestation: the five steps from architecture type to KYC-SA submission

SWIFT CSP Attestation: 5 Essential Steps to Comply

Governance Docs12th August 2026

If your institution is on the SWIFT network, security is not a matter of internal policy. SWIFT CSP attestation is an annual obligation: every member must attest against the Customer

Read More
    ←
  • 1
  • …
  • 90
  • 91
  • 92
  • 93
  • 94
  • …
  • 99
  • →

Recent Posts

ISO 27001 configuration management requirements under Annex A 8.9 - established, documented, implemented, monitored, reviewed
ISO 27001 Configuration Management: Complete 2026 Guide

October 11, 2026

internal audit findings rating scale — Internal Audit Findings Rating Scale: Examples and Template
Internal Audit Findings Rating Scale: Examples and Template

October 11, 2026

third party topical requirement — Third Party Topical Requirement: The 2026 Audit Guide
Third Party Topical Requirement: The 2026 Audit Guide

October 11, 2026

cybersecurity topical requirement — Cybersecurity Topical Requirement: How to Audit It in 2026
Cybersecurity Topical Requirement: How to Audit It in 2026

October 11, 2026

quality assurance and improvement program — Quality Assurance and Improvement Program (QAIP): 2026 Guide
Quality Assurance and Improvement Program (QAIP): 2026 Guide

October 11, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA