About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

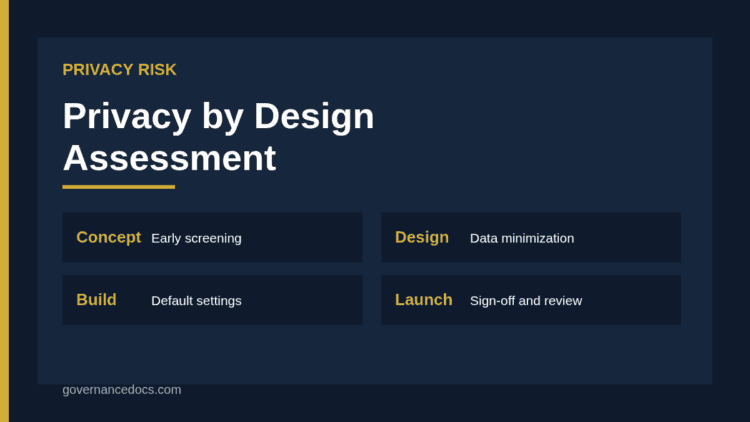
Privacy by design risk assessment mapped across product stages from concept to launch and review

Privacy by Design Risk Assessment Guide 2026

Governance Docs30th September 2026

How to run a privacy by design risk assessment: Article 25 duties, when to assess in the product…
Read More
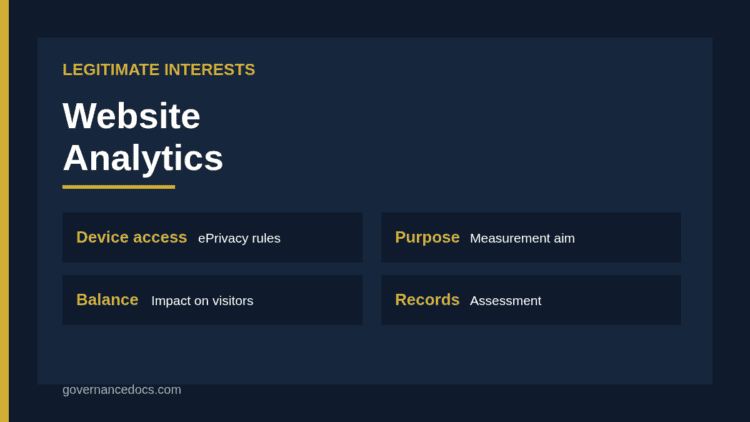
Legitimate interests for website analytics decision path from data type to cookie rules and balancing test

Legitimate Interests for Website Analytics Guide 2026

Governance Docs30th September 2026

When legitimate interests for website analytics can be used: GDPR test, ePrivacy consent rules for cookies, server-side and…
Read More
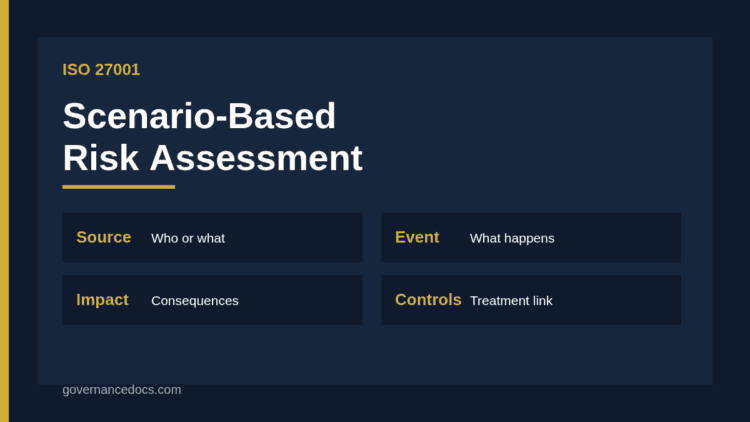
ISO 27001 scenario-based risk assessment flow from threat source and event to consequence and control

ISO 27001 Scenario-Based Risk Assessment Guide 2026

Governance Docs30th September 2026

How an ISO 27001 scenario-based risk assessment works: what a scenario contains, how to build a library, rate…
Read More
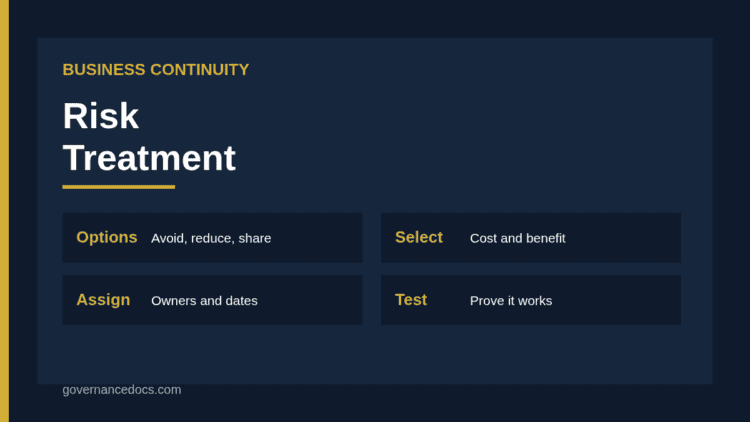
Business continuity risk treatment options linking assessed risks to prevention, protection and recovery measures

Business Continuity Risk Treatment Guide 2026

Governance Docs30th September 2026

How business continuity risk treatment works: options to avoid, reduce, transfer or accept, choosing strategies, costing, ownership, plans…
Read More
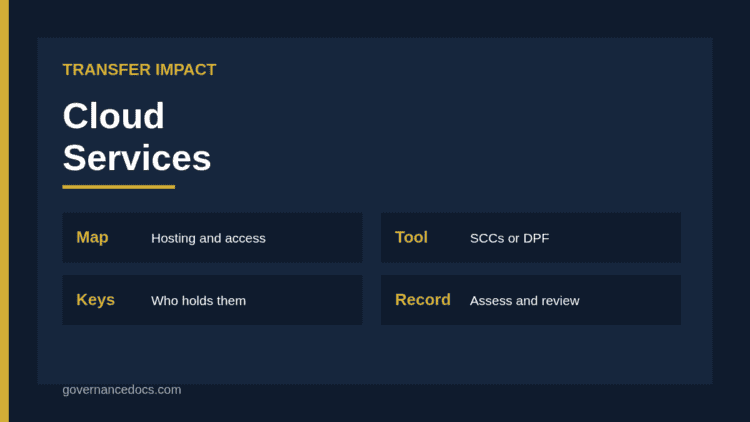
Transfer impact assessment for cloud services showing hosting region, support access, encryption keys and legal review

Transfer Impact Assessment for Cloud Services Guide 2026

Governance Docs30th September 2026

How to run a transfer impact assessment for cloud services: mapping hosting and support access, transfer tool, encryption…
Read More
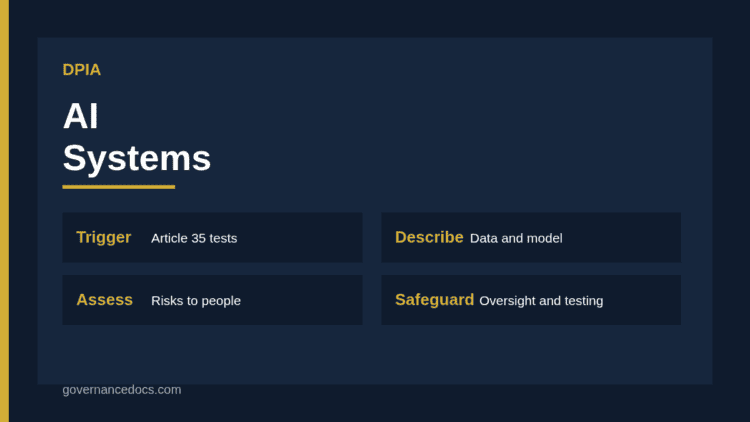
DPIA for AI showing model description, data flows, risks to individuals, safeguards and sign-off

DPIA for AI Systems Guide 2026

Governance Docs30th September 2026

When and how to complete a DPIA for AI: triggers under Article 35, describing models and data, necessity,…
Read More
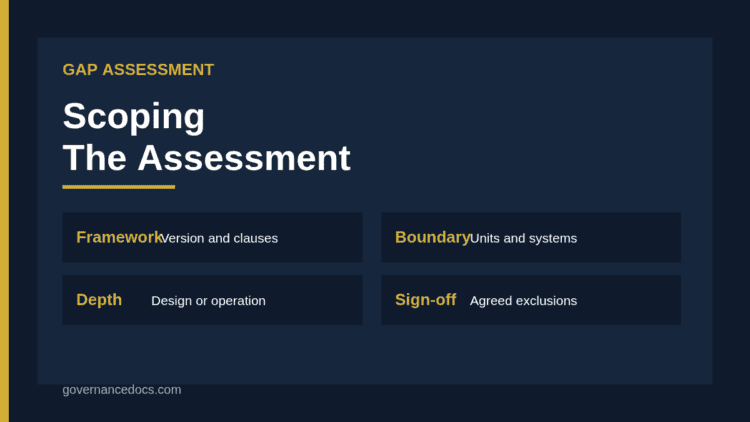
Gap assessment scoping diagram showing framework, organizational boundary, systems, sites and exclusions

Gap Assessment Scoping Guide 2026

Governance Docs30th September 2026

How to scope a gap assessment: choosing the framework and version, setting organizational and system boundaries, applicability, depth,…
Read More
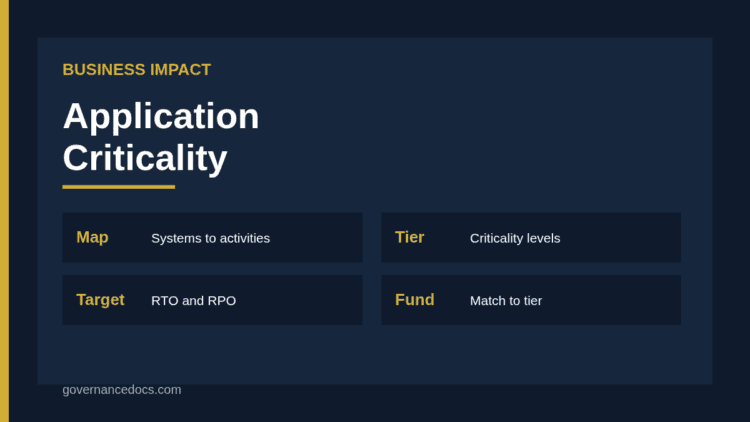
Application criticality tiers derived from business impact analysis with recovery time targets per tier

Application Criticality from a BIA Guide 2026

Governance Docs30th September 2026

How to rate application criticality from a business impact analysis: mapping systems to activities, deriving tiers, setting recovery…
Read More
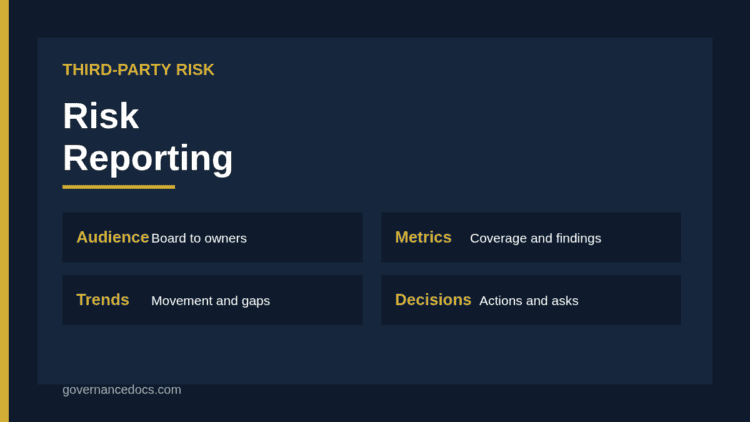
Third-party risk reporting dashboard with vendor tiers, open findings, overdue assessments and concentration

Third-Party Risk Reporting Guide 2026

Governance Docs30th September 2026

How to design third-party risk reporting: audiences, key metrics, tiering views, concentration, findings, exceptions and how to present…
Read More
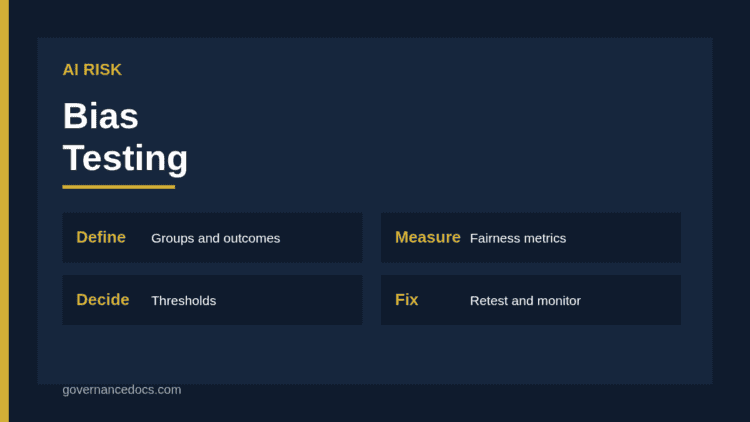
AI bias testing workflow from defining groups to metrics, thresholds, remediation and monitoring

AI Bias Testing Guide 2026: Methods and Records

Governance Docs30th September 2026

How to run AI bias testing: define groups and outcomes, choose metrics, build test data, set thresholds, investigate…
Read More
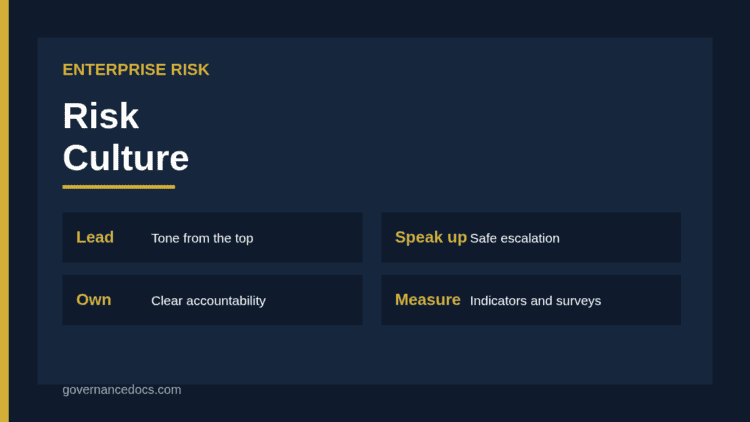
Risk culture assessment showing leadership, communication, accountability and incentives around a risk management program

Risk Culture Guide 2026: Assess and Improve It

Governance Docs30th September 2026

What risk culture is, why it decides whether enterprise risk management works, how to assess it with surveys…
Read More
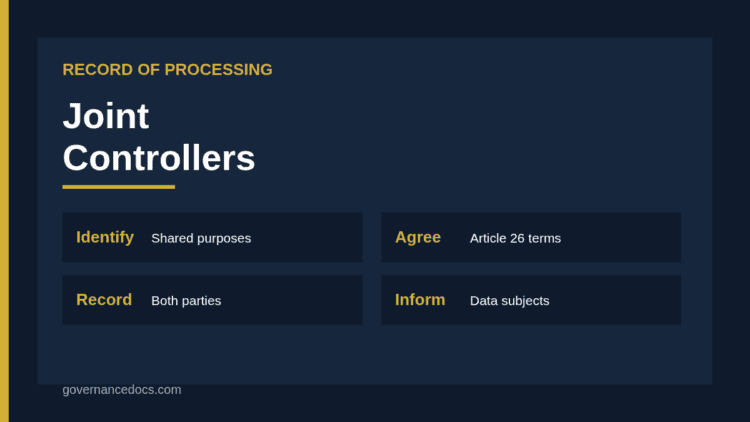
RoPA joint controllers diagram of two organizations sharing purposes and means with an Article 26 arrangement

RoPA and Joint Controllers Guide 2026

Governance Docs30th September 2026

How to handle RoPA joint controllers: when controllership is joint, what Article 26 requires, what to record in…
Read More

    ←
  • 1
  • …
  • 16
  • 17
  • 18
  • 19
  • 20
  • …
  • 100
  • →

Recent Posts

ISO 27001 remote working Annex A 6.7 diagram showing the four evidence sets: authorisation, provisioning, enforcement and attestation
ISO 27001 Remote Working: Complete A.6.7 Guide 2026

October 12, 2026

ISO 27001 configuration management requirements under Annex A 8.9 - established, documented, implemented, monitored, reviewed
ISO 27001 Configuration Management: Complete 2026 Guide

October 11, 2026

internal audit findings rating scale — Internal Audit Findings Rating Scale: Examples and Template
Internal Audit Findings Rating Scale: Examples and Template

October 11, 2026

third party topical requirement — Third Party Topical Requirement: The 2026 Audit Guide
Third Party Topical Requirement: The 2026 Audit Guide

October 11, 2026

cybersecurity topical requirement — Cybersecurity Topical Requirement: How to Audit It in 2026
Cybersecurity Topical Requirement: How to Audit It in 2026

October 11, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA