

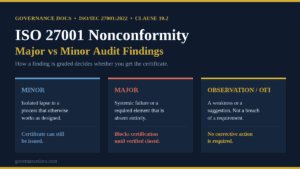
ISO 27001 Nonconformity: The Complete 2026 Guide to Major vs Minor Findings
How ISO 27001 nonconformity findings are classified as major or minor, the deadlines that follow, the six most…
CART
How ISO 27001 nonconformity findings are classified as major or minor, the deadlines that follow, the six most…
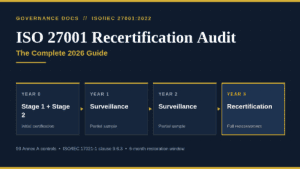
What happens at the year-three ISO 27001 recertification audit: the ISO/IEC 17021-1 timing rules, what auditors sample, typical…
Phishing-resistant MFA under NIST SP 800-63B-4: which methods qualify, what AAL2 and AAL3 each require, and why synced…
Cybersecurity governance after NIS2: what boards must approve, why NIST CSF 2.0 added a 6th function, and the…
A clean desk policy that passes an ISO 27001 audit: what Annex A 7.7 requires, the 9 rules…
A BYOD policy that survives an ISO 27001 audit: the 7 Annex A controls it satisfies, the 9…
PCI DSS documentation a QSA actually asks for: the 12 requirement areas, the 51 future-dated controls effective 31…
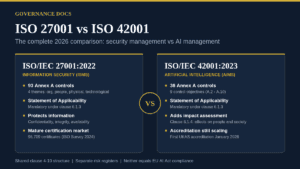
ISO 27001 vs ISO 42001 compared for 2026: 93 security controls versus 38 AI controls, the shared clause…
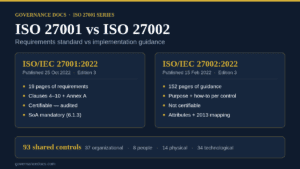
ISO 27001 vs ISO 27002 explained: one is a 19-page certifiable requirements standard, the other 152 pages of…
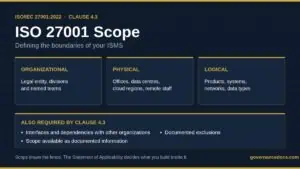
Your ISO 27001 scope decides your audit days, your workload and what your certificate says. Clause 4.3 rules,…
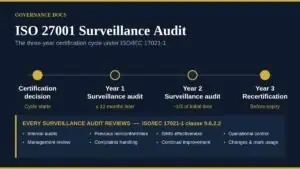
What an ISO 27001 surveillance audit covers, when it is due, what it costs in 2026, and how…
Clause 8.2 carries everything built on top of it, and 8.5 cannot be closed on paper. How to…
October 23, 2026
October 23, 2026

October 22, 2026

October 22, 2026
October 22, 2026