About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: October 12, 2026

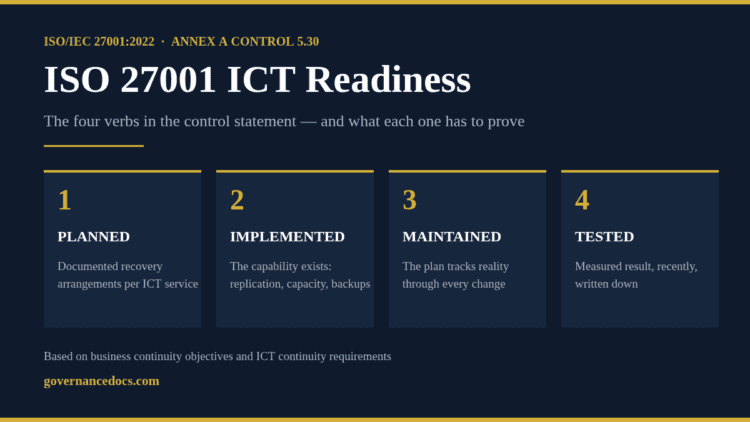
ISO 27001 ICT readiness (Annex A 5.30): the four verbs in the control statement — planned, implemented, maintained and tested

ISO 27001 ICT Readiness: Complete A.5.30 Guide 2026

Governance Docs12th October 2026

ISO 27001 ICT readiness (Annex A 5.30) explained: why the control demands a tested capability, and why a…
Read More
iso 30301 — ISO 30301 vs ISO 15489: Which Records Standard Do You Need?

ISO 30301 vs ISO 15489: Which Records Standard Do You Need?

Governance Docs12th October 2026

ISO 30301 vs ISO 15489: the certifiable management system for records versus the guidance standard, and how one…
Read More
legal hold — Legal Hold: How to Suspend Records Destruction Properly (2026)

Legal Hold: How to Suspend Records Destruction Properly (2026)

Governance Docs12th October 2026

How a legal hold works on the records side: triggers, the hold notice, suspending deletion and migrations, monitoring,…
Read More
records retention schedule — Records Retention Schedule: How to Build One in 2026

Records Retention Schedule: How to Build One in 2026

Governance Docs12th October 2026

How to build a records retention schedule: function-based classes, trigger events, disposition actions, approval and review, aligned with…
Read More
iso 15489 — ISO 15489 Explained: The Records Management Standard in 2026

ISO 15489 Explained: The Records Management Standard in 2026

Governance Docs12th October 2026

ISO 15489 explained: what ISO 15489-1:2016 covers clause by clause, why it cannot be certified, and how to…
Read More
records management metadata — Records Management Metadata: What to Capture and Why (2026)

Records Management Metadata: What to Capture and Why (2026)

Governance Docs12th October 2026

Records management metadata explained: point-of-capture and process metadata, entities and classes, schemas and why metadata makes records evidence.
Read More
records appraisal — Records Appraisal: A Step-by-Step Method for 2026

Records Appraisal: A Step-by-Step Method for 2026

Governance Docs12th October 2026

Records appraisal under ISO 15489-1 clause 7: scoping, functional analysis, risk, records requirements, decisions and authorisation, step by…
Read More
business classification scheme — Business Classification Scheme: A Practical 2026 Guide

Business Classification Scheme: A Practical 2026 Guide

Governance Docs12th October 2026

How to build a business classification scheme: functions, activities and transactions, file plans, and linking classes to access…
Read More
records management policy — Records Management Policy: What It Must Contain (2026 Guide)

Records Management Policy: What It Must Contain (2026 Guide)

Governance Docs12th October 2026

What a records management policy should contain under ISO 15489-1 clause 6.2: scope, mandates, responsibilities, approval, review and…
Read More
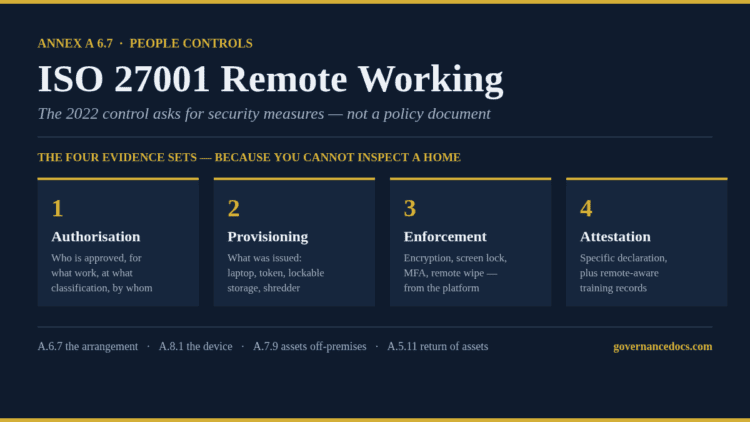
ISO 27001 remote working Annex A 6.7 diagram showing the four evidence sets: authorisation, provisioning, enforcement and attestation

ISO 27001 Remote Working: Complete A.6.7 Guide 2026

Governance Docs12th October 2026

ISO 27001 remote working (Annex A 6.7) explained: why the 2022 control no longer names a policy, plus…
Read More

Recent Posts

ISO 27001 toolkit contents shown as three layers: clause 4 to 10 records, 93 Annex A controls and supporting registers
ISO 27001 Toolkit: What a Complete One Contains (2026)

November 2, 2026

ISO 9001 recertification audit three-year cycle showing surveillance in years 1 and 2 and recertification in year 3
ISO 9001 Recertification Audit: The Complete 2026 Guide

November 1, 2026

ISO 9001 surveillance audit: eight required review areas, the 12-month window and the 2029 transition deadline
ISO 9001 Surveillance Audit: The Complete 2026 Guide

October 31, 2026

ISO 27001 software installation under Annex A 8.19: production systems and end-user endpoints
ISO 27001 Software Installation: Essential A.8.19 Guide 2026

October 31, 2026

ISO 27001 employment contracts and Annex A 6.2 terms and conditions of employment among the people controls
ISO 27001 Employment Contracts: The Essential 2026 Guide

October 30, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Request a custom toolkit
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA