About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentGap AssessmentsBusiness Impact AnalysisISO 27001 Risk AssessmentContinuity Risk AssessmentEnterprise Risk AssessmentAI Risk AssessmentAI Impact AssessmentThird-Party Risk AssessmentAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 30, 2026

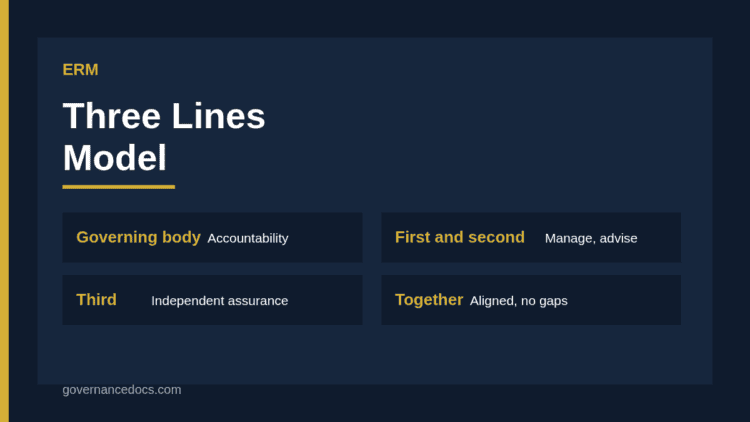
Three lines model diagram showing governing body, management first and second line roles, internal audit and external assurance

Three Lines Model for Enterprise Risk Management: 2026

Governance Docs30th September 2026

How the three lines model works in enterprise risk management: roles of the governing body, management, risk and…
Read More
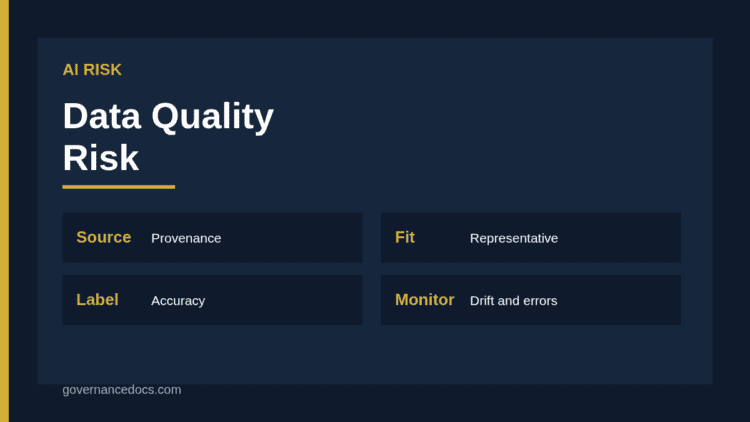
AI data quality risk checks for representativeness, labelling, provenance, completeness and drift in training and input data

AI Data Quality Risk: A Practical 2026 Guide

Governance Docs30th September 2026

How to manage AI data quality risk: assessing representativeness, labelling, provenance, bias and drift in training and input…
Read More
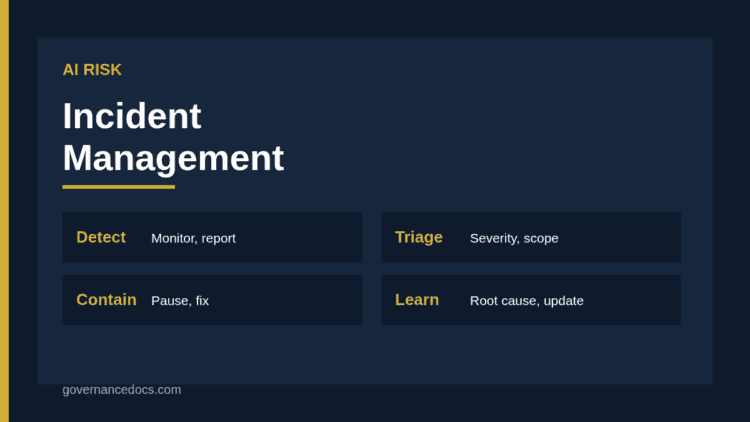
AI incident management lifecycle from detection and triage to containment, reporting and lessons learned

AI Incident Management: A Practical 2026 Guide

Governance Docs30th September 2026

How to build AI incident management: defining AI incidents, detection, triage, containment, reporting duties, root cause analysis and…
Read More
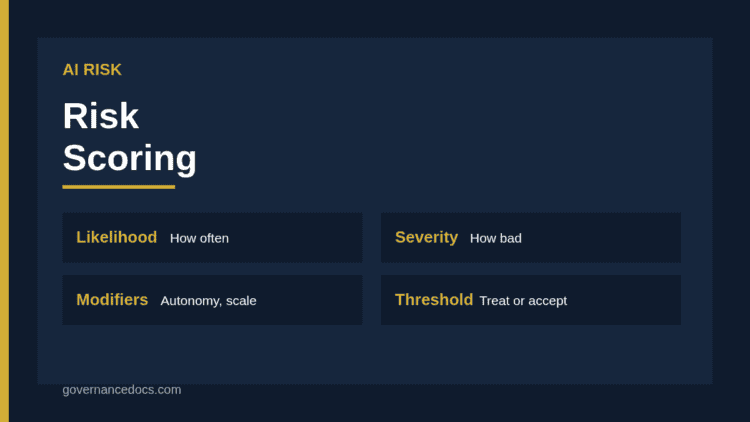
AI risk scoring matrix combining likelihood, severity, autonomy and scale into low, medium, high and critical ratings

AI Risk Scoring: A Practical 2026 Guide

Governance Docs30th September 2026

How to approach AI risk scoring: rating likelihood and severity of harm, adjusting for autonomy and scale, setting…
Read More
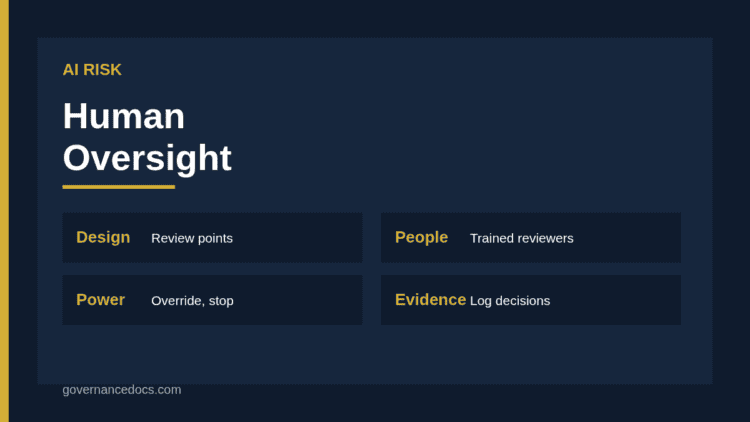
Human oversight of AI model showing review points, reviewer training, override powers and monitoring evidence

Human Oversight of AI Systems: A Practical 2026 Guide

Governance Docs30th September 2026

How to design human oversight of AI: meaningful review points, reviewer competence, automation bias, intervention rights and evidence…
Read More
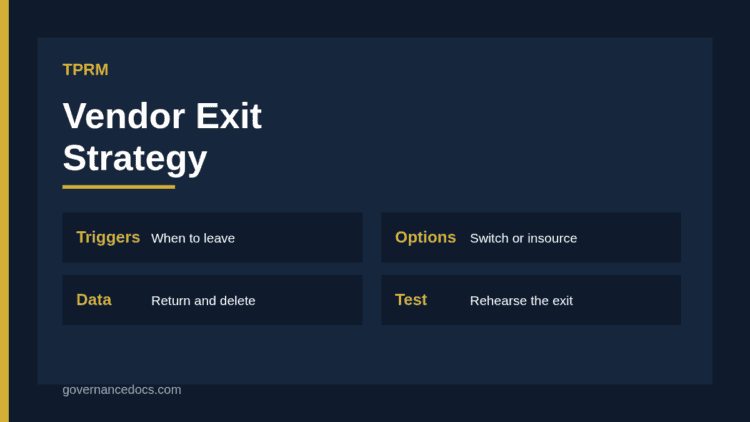
Vendor exit strategy showing triggers, exit options, data return, transition and testing steps

Vendor Exit Strategy: How to Plan One in 2026

Governance Docs30th September 2026

How to build a vendor exit strategy: triggers, stressed and planned exit options, data return, transition steps, contract…
Read More
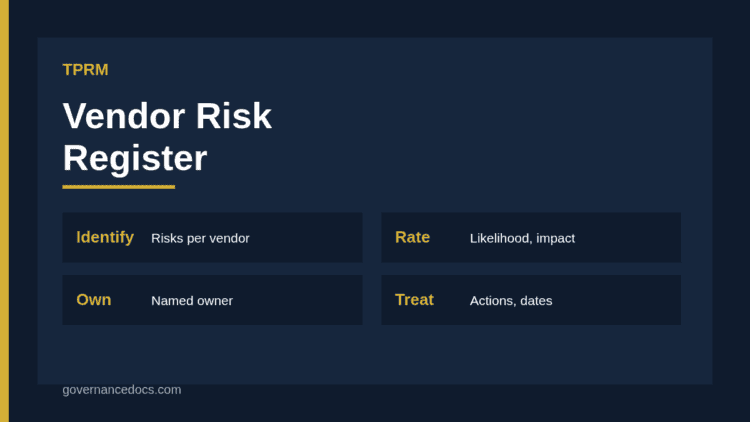
Vendor risk register table with vendor, risk description, rating, owner, treatment and review date columns

Vendor Risk Register: How to Build One in 2026

Governance Docs30th September 2026

How to build a vendor risk register: the fields to include, how to score risks, assign owners, link…
Read More
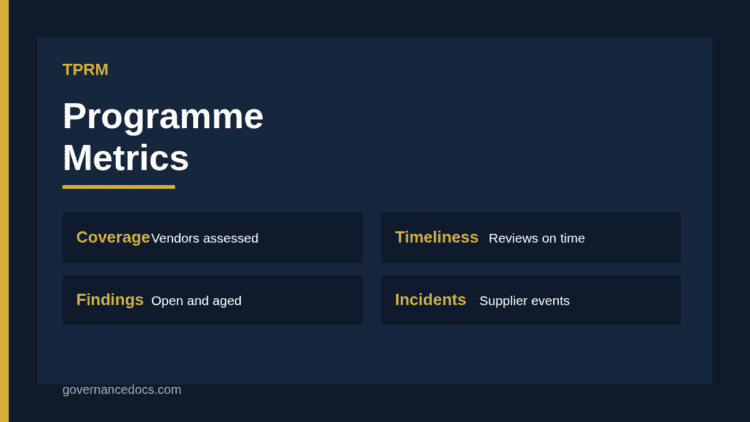
TPRM metrics dashboard showing coverage, assessment timeliness, open findings, incidents and concentration

TPRM Metrics and KPIs: A Practical 2026 Guide

Governance Docs30th September 2026

Which TPRM metrics matter: coverage, timeliness, findings, incidents and concentration, how to set thresholds and how to report…
Read More
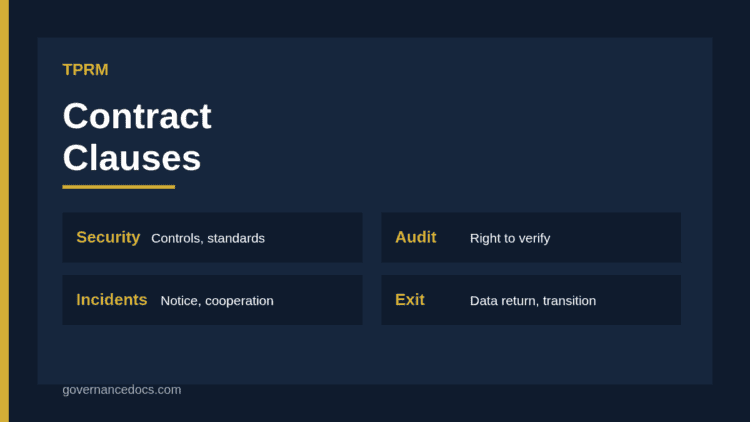
Third-party contract clauses grouped into security, data, audit, incident, subcontractor and exit protections

Third-Party Contract Clauses for Risk Management: 2026

Governance Docs30th September 2026

The third-party contract clauses that matter for risk management: security, data protection, audit rights, incident notification, subcontractors, resilience…
Read More
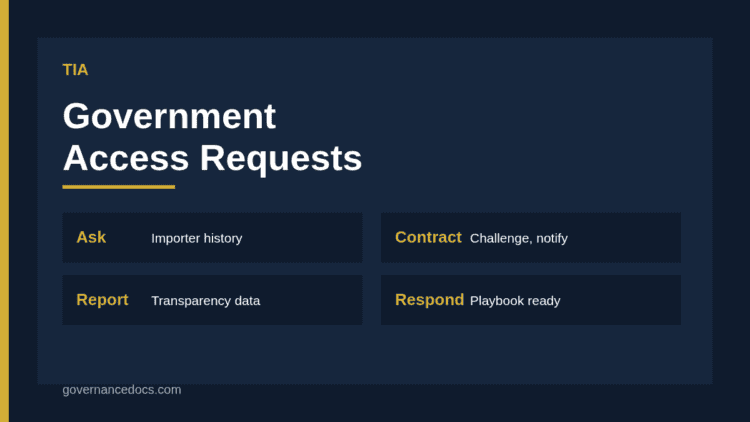
Government access requests in a TIA showing assessment, contract clauses, transparency reports and response steps

Government Access Requests in a TIA: 2026 Guide

Governance Docs30th September 2026

How to handle government access requests in a TIA: assessing importer track record, contract commitments, transparency reports and…
Read More
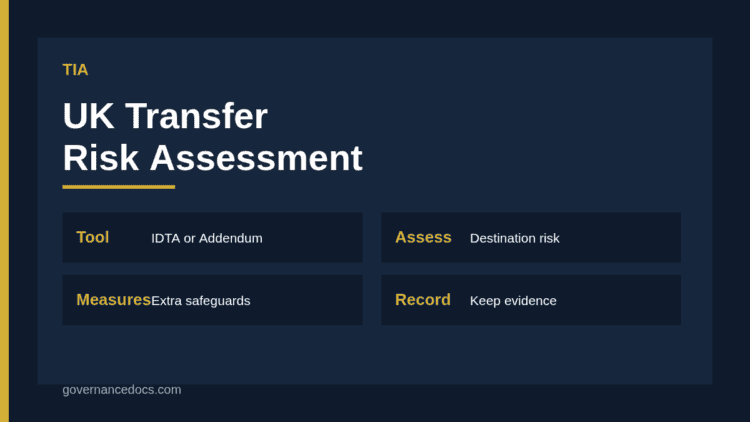
UK transfer risk assessment steps covering transfer description, tool, destination laws, risk rating and safeguards

UK Transfer Risk Assessment: A Practical 2026 Guide

Governance Docs30th September 2026

How to do a UK transfer risk assessment: when the IDTA or UK Addendum needs one, the ICO…
Read More
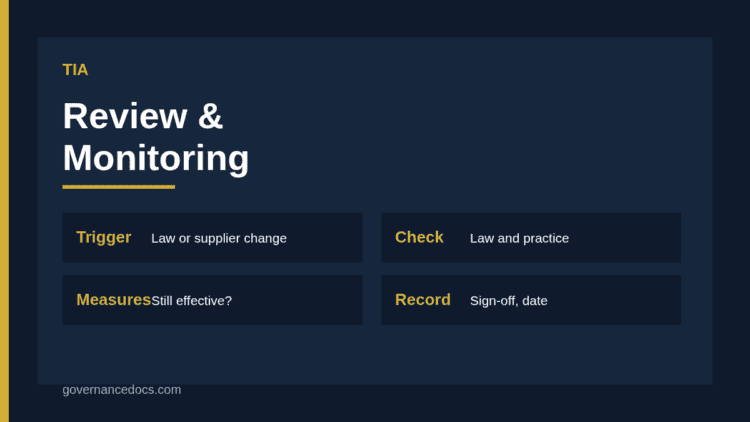
TIA review and monitoring cycle showing triggers, legal check, supplier check, measures review and sign-off

TIA Review and Monitoring: A Practical 2026 Guide

Governance Docs30th September 2026

How to run TIA review and monitoring: review triggers, schedules, what to check about laws and suppliers, ownership…
Read More

    ←
  • 1
  • 2
  • 3
  • 4
  • 5
  • …
  • 9
  • →

Recent Posts

Gap assessment reassessment progress comparison diagram
Gap Assessment Reassessment: The Essential 2026 Guide to Measuring Progress

September 30, 2026

Business continuity supply chain risk map diagram
Business Continuity Supply Chain Risk: The Essential 2026 Guide to Resilient Suppliers

September 30, 2026

Business continuity risk appetite statement diagram
Business Continuity Risk Appetite: The Essential 2026 Guide to Setting Tolerance for Disruption

September 30, 2026

Business continuity risk monitoring indicators diagram
Business Continuity Risk Monitoring: The Essential 2026 Guide to Indicators and Reviews

September 30, 2026

Business continuity scenario planning steps diagram
Business Continuity Scenario Planning: The Essential 2026 Guide to Testing Your Plans

September 30, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA