
About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account
CART

No products in the cart.

ISO 27001

Interagency Guidance — The Interagency Guidance on Third-Party Relationships: A Complete 2026 Guide

The Interagency Guidance on Third-Party Relationships: A Complete 2026 Guide

Governance Docs13th September 2026

The 2023 Interagency Guidance on Third-Party Relationships explained: what it rescinded, its lifecycle, the 14 due diligence factors and 17 contract considerations.
Read More
TPRM — What Is TPRM? Third-Party Risk Management Explained (2026 Guide)

What Is TPRM? Third-Party Risk Management Explained (2026 Guide)

Governance Docs13th September 2026

TPRM, third-party risk management, explained: the five-stage lifecycle regulators use, the twelve regimes that require it, and what a documented programme holds.
Read More
NIST CSF to 800-53 mapping — NIST CSF to 800-53 Mapping: A Clear Guide to All 106

NIST CSF to 800-53 Mapping: A Clear Guide to All 106

Governance Docs06th September 2026

NIST maps all 106 CSF 2.0 outcomes to SP 800-53 Rev 5 with 740 control references. How to use the mapping properly, and why it is not proof of coverage.
Read More
NIST CSF 2.0 vs 1.1 — NIST CSF 2.0 vs 1.1: The 79 Subcategories That Changed

NIST CSF 2.0 vs 1.1: The 79 Subcategories That Changed

Governance Docs06th September 2026

CSF 2.0 withdrew 79 Subcategories and removed 12 Categories. The full mapping, the 16 outcomes with no predecessor, and the traps in re-mapping them.
Read More
NIST CSF GOVERN function — The NIST CSF GOVERN Function: All 31 Outcomes Explained

The NIST CSF GOVERN Function: All 31 Outcomes Explained

Governance Docs06th September 2026

The GOVERN function is 31 of the 106 CSF 2.0 outcomes across six Categories, ten of them supply chain. What it asks for, and where programmes fall short.
Read More
SWIFT architecture types explained

SWIFT Architecture Types: A Clear Guide to All 5 Types

Governance Docs02nd September 2026

SWIFT architecture types A1 to B decide how much of the CSCF applies to you. What sets your type, what changed in v2026, and the misclassification that costs.
Read More
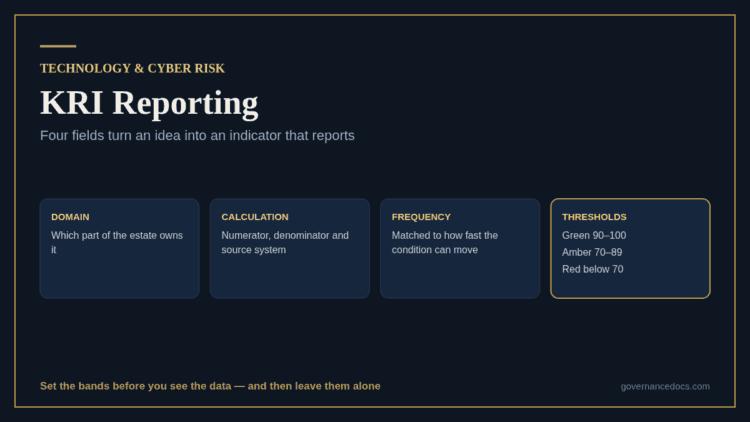
KRI reporting: the four fields every key risk indicator needs before it can report

KRI Reporting: A Clear Guide to the 4 Core Fields

Governance Docs31st August 2026

KRI reporting fails when indicators are picked for easy data. The 4 fields every KRI needs, RAG thresholds that hold, and how to structure the pack.
Read More
IEC 62443 Toolkit – 117 IACS cybersecurity templates

IEC 62443 Toolkit – 117 IACS Cybersecurity Templates

The IEC 62443 Toolkit delivers 117 ready-to-use Microsoft Office templates for industrial automation and control system asset owners — 82 Word documents and 35 Excel workbooks covering every one of...
Read More
VDA ISA2027 for TISAX assessments

VDA ISA2027: What Changed and What It Means for Your TISAX Assessment

Governance Docs14th August 2026

VDA ISA2027 replaces ISA 6 for every TISAX assessment ordered from 1 January 2027. What changed in the catalogue, the rewritten Prototype Protection module, and the dates.
Read More
Data Governance Toolkit for management and compliance.

Comprehensive Data Governance Toolkit – 91 DMBOK-Aligned Templates

Data Governance Toolkit delivers 91 ready-to-use Microsoft Office templates covering data governance, data architecture, data modelling and design, data storage and operations, data security, data integration and interoperability, document and...
Read More
    ←
  • 1
  • …
  • 30
  • 31
  • 32
  • 33
  • →

Recent Posts

ISO 9001 certification timeline 2026: six stages from gap analysis to certificate, with the ISO 9001:2026 transition dates
ISO 9001 Certification Timeline: The Complete 2026 Guide

September 21, 2026

ISO 13485 certification timeline infographic: 6–18 months from kickoff to certificate, phase by phase
ISO 13485 Certification Timeline: The Complete 2026 Guide

September 20, 2026

ISO 27001 vs HIPAA infographic comparing the voluntary ISO/IEC 27001:2022 standard with the HIPAA federal law on scope, controls, proof and consequences
ISO 27001 vs HIPAA: 7 Essential Differences Explained (2026)

September 20, 2026

HITRUST vs ISO 27001 comparison: issuer, controls, scoring, validity and recognition side by side
HITRUST vs ISO 27001: 7 Essential Differences Explained (2026)

September 19, 2026

compliance consultant certifications explained
Compliance Consultant Certifications: 6 Essential Credentials

September 19, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA