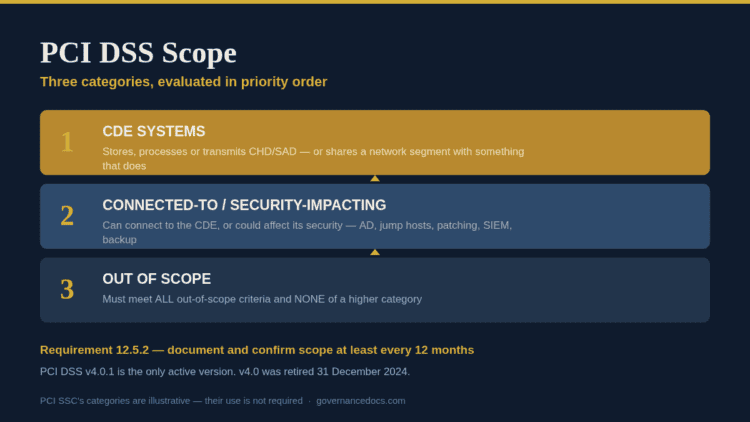
How PCI DSS scope is decided: the 3 system categories in priority order, the annual confirmation under Requirement 12.5.2, and how to reduce scope legitimately.
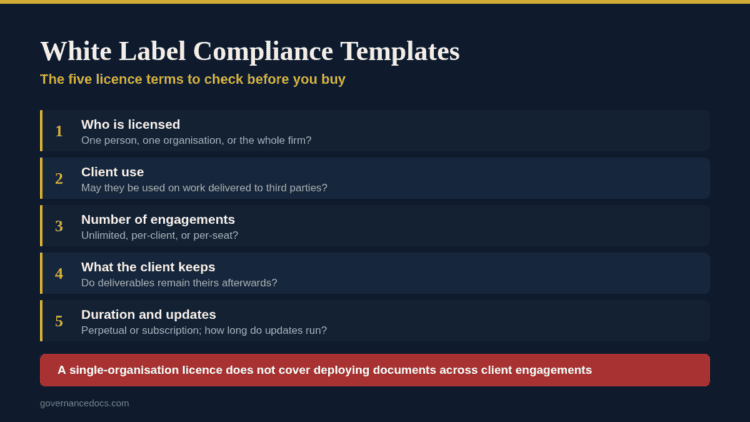
Can you use white label compliance templates on client work? The 5 licence terms to check, how to tailor properly, and the metadata step consultants miss.
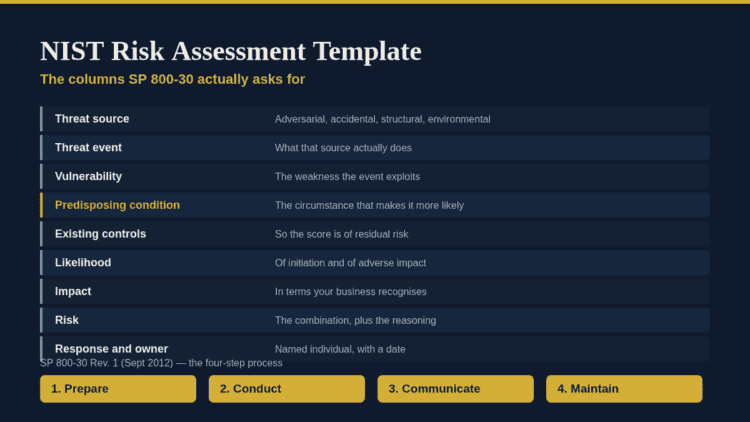
What a NIST risk assessment template must contain, the 4 steps of SP 800-30, and how it differs from a risk register and a CSF 2.0 maturity assessment.