Cyber Essentials requirements v3.3: the 5 controls with numbers — 14-day patching, MFA on cloud, 12-character passwords, 10-attempt lockout — and what changed.
Board cybersecurity reporting built on 6 indicators — exposure, control coverage, detection and response speed, incident impact, third-party risk, delivery.
NIS2 incident reporting under Article 23: 24-hour early warning, 72-hour notification, one-month final report, and the thresholds in Regulation 2024/2690.
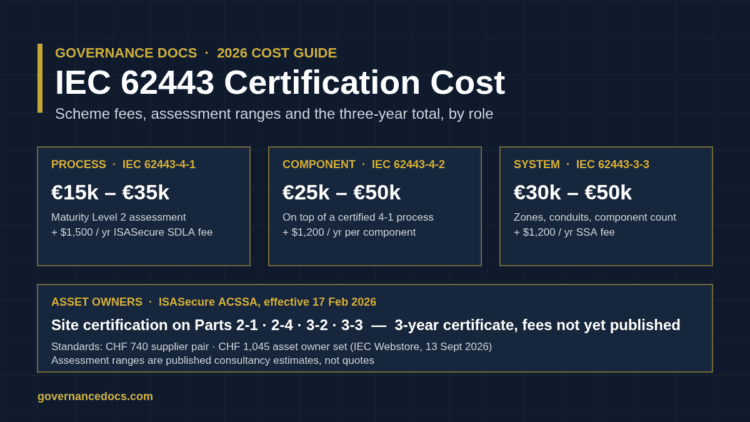
IEC 62443 certification cost in 2026: ISASecure fees from $1,200 a year, assessment ranges of €15,000–€50,000 by role, and the new ACSSA asset owner scheme.
SOC 1 Toolkit: 87 editable SOC 1 / ISAE 3402 templates built on AT-C section 320 — management's system description in every required section, 19 control objectives with 76 risks...
The TPRM lifecycle stage by stage: planning, due diligence, contracting, monitoring and exit, with the entry and exit criteria and the record each stage must leave.
TPRM Toolkit: 86 editable third-party risk management templates on the lifecycle every regulator uses — planning, due diligence, contracting, monitoring and exit — mapped to 188 requirements across 12 regimes...