Anyone comparing ISO 31000 vs ISO 27005 has usually been handed a risk register and told to “align it with the standard” — without being told which standard. The two are not rivals. ISO 31000 is the generic risk management guideline for the whole organization. ISO/IEC 27005 is the information security specialization that sits inside it. Pick the wrong one as your starting point and you will either build something too abstract to use or something too narrow to satisfy your board.
Here is what each one actually covers in 2026, and how to decide which belongs at the centre of your programme. The short version of ISO 31000 vs ISO 27005: one sets the rules of the game, the other plays one position on the field.
ISO 31000 vs ISO 27005 at a glance
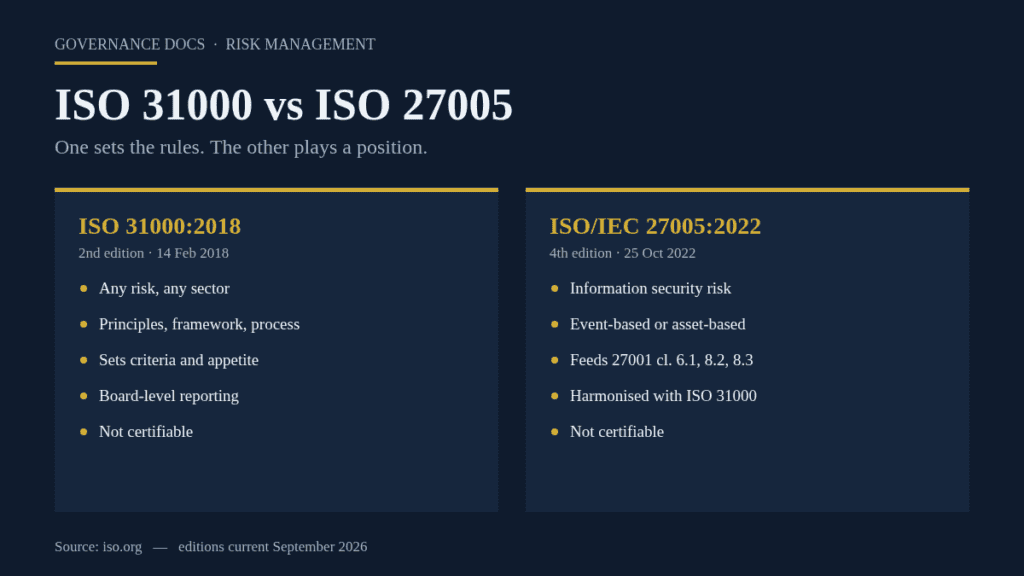
ISO 31000:2018
ISO/IEC 27005:2022
Full title
Risk management — Guidelines
Information security, cybersecurity and privacy protection — Guidance on managing information security risks
Edition
Second edition, 14 February 2018
Fourth edition, 25 October 2022
Scope
Any risk, any organization, any sector
Information security risk only
Certifiable?
No — guidance
No — guidance
Structure
Principles, framework, process
Process detail, with worked approaches and annexes
Audience
The board, ERM, whoever owns risk across the business
The ISMS owner, security and privacy teams
Feeds
Enterprise risk management
ISO/IEC 27001 clauses 6.1, 8.2 and 8.3
Typical output
A risk policy, criteria and an organization-wide register
Risk scenarios, a treatment plan and a Statement of Applicability input
What ISO 31000 gives you
ISO 31000:2018 is the second edition, published on 14 February 2018, and it is deliberately short. It sets out eight principles, a framework built around leadership and commitment, and a process: scope and context, risk identification, analysis, evaluation, treatment, then monitoring, recording and reporting throughout.
What it does not do is tell you how. There are no threat catalogues, no likelihood tables, no worked examples. That is the point — it has to work for a hospital, a shipping line and a software company at once.
Two things follow from that. First, ISO 31000 is where your risk criteria, your risk appetite and your escalation thresholds belong, because those are organization-wide decisions and should not be reinvented per domain. Second, ISO 31000 is not certifiable. It is a guidance document, not a requirements document, so nobody can audit you against it and issue a certificate. Any vendor offering “ISO 31000 certification” for your organization is selling something the standard does not support.
If ISO 31000 is the constitution, this is the statute. Most of the confusion in an ISO 31000 vs ISO 27005 debate disappears once you have read the first page of each.
ISO/IEC 27005:2022 is the fourth edition, published on 25 October 2022, and it is the opposite in character: specific, practical and full of the detail ISO 31000 leaves out.
The 2022 edition made two changes that matter. Its terminology was harmonized with ISO 31000, so the two now describe the same process using the same words. And its content was realigned to ISO/IEC 27001:2022, so it maps directly onto clause 6.1 (actions to address risks and opportunities), clause 8.2 (risk assessment) and clause 8.3 (risk treatment).
It also describes two ways to identify risk, and choosing between them is the most consequential decision in the whole exercise:
The event-based approach — a high-level assessment that builds strategic scenarios from risk sources and how they affect interested parties. Faster, better for getting a board-level picture, weaker on operational specifics.
The asset-based approach — an in-depth assessment that builds operational scenarios from assets, threats and vulnerabilities. Slower, heavier to maintain, and far more useful when you need to justify a specific control.
Mature programmes usually run event-based at the top for the board and asset-based underneath for the systems that carry real exposure. Like ISO 31000, ISO 27005 is guidance and cannot be certified against. What gets certified is ISO/IEC 27001, and 27005 is how you satisfy its risk clauses convincingly.
ISO 31000 vs ISO 27005: the differences that change your work
Breadth. ISO 31000 covers every risk your organization carries — financial, legal, safety, strategic, environmental. ISO 27005 covers one category. If your risk register only holds cyber risks, you do not have an enterprise risk register; you have a security one.
Depth. ISO 27005 will tell you how to build a risk scenario. ISO 31000 will not. The ISO 31000 vs ISO 27005 gap here is not a disagreement — it is a difference in altitude.
Who reads the output. ISO 31000 output goes to a board or risk committee that needs consistency across domains. ISO 27005 output goes to an ISMS, an auditor, and increasingly a customer’s security questionnaire.
What an auditor does with it. Neither is auditable on its own. But an ISO 27001 auditor will look at your risk process and ask whether it is defensible and repeatable. A process built on ISO 27005 answers that question in the auditor’s own vocabulary.
How often it changes. ISO 31000 has been stable since 2018. ISO 27005 moved in 2022 to follow ISO/IEC 27001:2022, and will move again when 27001 does.
Which one you should start with
The ISO 31000 vs ISO 27005 decision is mostly a question of what already exists.
You have no risk framework at all and you need one for the business. Start with ISO 31000. Set the criteria, the appetite and the reporting lines once, then let each domain work inside them.
You are implementing or maintaining ISO 27001. Start with ISO 27005. It is written for exactly that job, and it will produce the evidence your certification auditor expects.
You already have an enterprise risk function and you are adding security. Use ISO 27005 for the method and inherit your criteria and thresholds from the existing ISO 31000-shaped framework. Do not create a second risk appetite.
You are a regulated financial or critical-infrastructure entity. You will usually need both, because your regulator expects enterprise-wide risk governance and your security obligations are assessed separately.
The failure mode worth naming: running ISO 27005 with no ISO 31000 layer above it, so the security team invents its own impact scale. Six months later the board cannot compare a cyber risk to a credit risk, and the security register gets quietly ignored. Setting a single scale first is cheap. Retrofitting one is not.
Running ISO 31000 vs ISO 27005 together
In practice most organizations do not choose. They run both, at different altitudes, and the ISO 31000 vs ISO 27005 question becomes a question of sequencing instead.
A workable order looks like this:
Set the criteria once, at ISO 31000 level. One impact scale, one likelihood scale, one appetite statement, one escalation threshold. Every domain inherits them.
Define the security scope. Which systems, which data, which third parties. This is also your ISMS scope, so do it once.
Identify with ISO 27005. Event-based for the strategic picture, asset-based where exposure is concentrated.
Analyse and evaluate against the inherited criteria — not against a scale the security team invented.
Treat, and record the decision. Accept, reduce, share or avoid, with a named owner and a date. This is what feeds your Statement of Applicability.
Report on the organization-wide cycle. If security risk is reported on a different rhythm to everything else, it will drift out of the conversation.
The test of whether you have done it properly is simple: can your board put a cyber risk and an operational risk side by side and say which is worse? If not, the two layers are not actually connected, whatever the documentation claims.
Documenting either one
Whichever way the ISO 31000 vs ISO 27005 question lands for you, the documents are the deliverable. A risk management policy, the criteria and appetite statement, the assessment methodology, the register itself, the treatment plan, and a reporting cycle that actually happens.
If you want a picture of where you stand before writing anything, our free ISO 31000 gap assessment scores you clause by clause across the principles, the framework and the process, and returns a prioritized list of what is missing. For the security side, our guide to building a cybersecurity risk register covers the fields that survive an audit.
When the gaps are documentation rather than practice, the ISO 31000 Toolkit supplies the policy, criteria, methodology, register and reporting templates already structured to the 2018 clause order.
Frequently asked questions
Is the ISO 31000 vs ISO 27005 comparison even the right question?
Often not. They operate at different levels, so the useful question is which one you start with and how the other inherits from it — not which one wins.
Can you be certified to ISO 31000 or ISO 27005?
Neither. Both are guidance standards rather than requirements standards, so there is nothing for a certification body to audit you against. Individuals can hold training certificates in both; organizations cannot be certified to either. ISO/IEC 27001 is the certifiable one.
Does ISO 27005 replace ISO 31000?
No. ISO 27005 is harmonized with ISO 31000 and specializes it for information security. Using 27005 does not remove the need for an organization-wide view of risk.
Which edition of each is current?
ISO 31000:2018 is the second edition, published 14 February 2018. ISO/IEC 27005:2022 is the fourth edition, published 25 October 2022. Documentation referencing ISO/IEC 27005:2018 is now two editions behind the alignment with ISO/IEC 27001:2022.
Do I need ISO 27005 to pass an ISO 27001 audit?
No. ISO 27001 requires a defined, repeatable risk process but does not mandate a particular method. ISO 27005 is the path of least resistance because it was written to fit, not because it is compulsory.
Event-based or asset-based — which should I use?
Event-based if you need a board-level picture quickly or your environment changes faster than you can inventory it. Asset-based when you have to justify individual controls or defend a Statement of Applicability. Running both at different altitudes is common and entirely legitimate.