CART
GovRAMP cost is one of the few compliance budgets that can be built from a published tariff. GovRAMP’s fee schedule, effective 1 January 2025 and approved by its board on 1 November 2024, sets two annual charges by revenue tier: membership dues paid to StateRAMP Inc. dba GovRAMP, and Program Management Office fees paid to RAMPQuest for each stage of the Security Program. A provider with under $1 million in revenue pays $1,500 a year for a Single Security Snapshot and $5,000 a year for Authorized status before assessor fees; a provider over $5 million pays $4,000 and $21,000 for the same.
What the schedule does not include is the third-party assessment organisation — required for Ready and Authorized — and the implementation work behind 60, 80 or 300-plus NIST SP 800-53 Rev. 5 controls, which is where most of the money goes. This guide sets out the GovRAMP cost line by line from the schedule, adds the 3PAO and implementation ranges the schedule leaves out, explains how Fast Track and Core change the total, and works three example budgets.
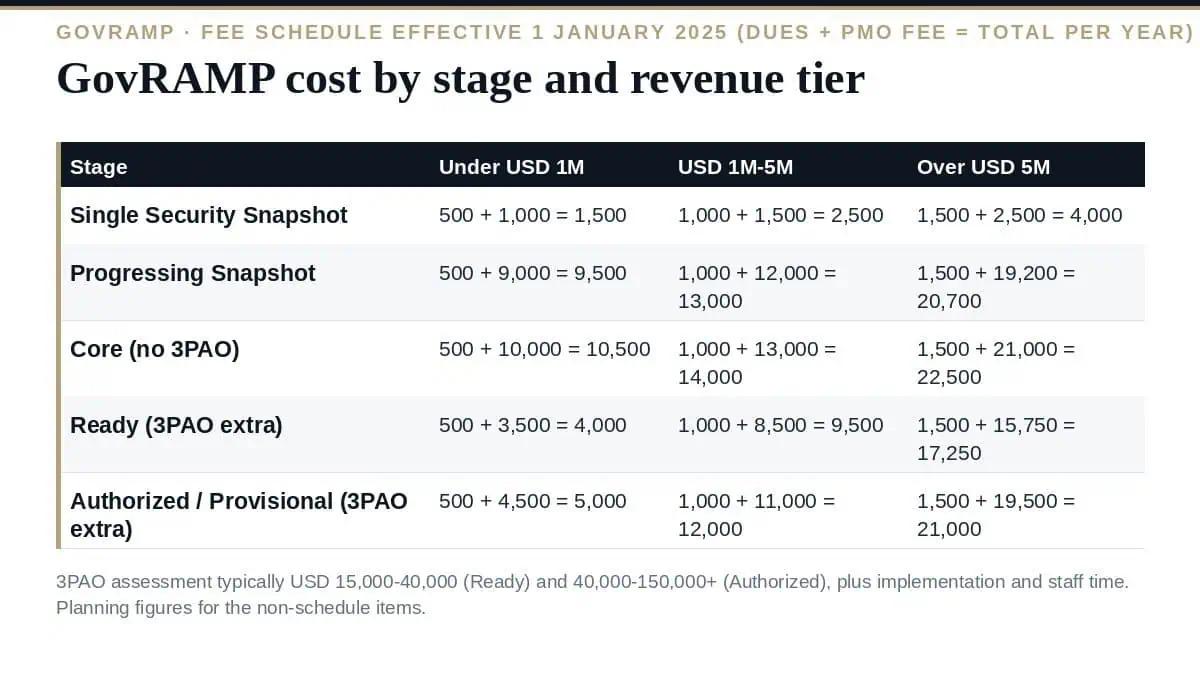
GovRAMP separates who you pay. Membership dues go to GovRAMP itself, are due annually on 1 June, and fund the programme; every service provider must be an active private-sector member before participating in any stage. Security-programme fees go to RAMPQuest, the contracted PMO that runs intake, documentation review and continuous monitoring. Both are set by revenue tier — under $1 million, $1 million to $5 million, and over $5 million — and the schedule notes that PMO fees may rise annually by no more than the Bureau of Labor Statistics rate published each June. Our guide to the GovRAMP status levels covers what each stage means; this guide covers what each costs.
| Programme stage | Under $1M: dues + PMO = total | $1M–$5M: dues + PMO = total | Over $5M: dues + PMO = total | 3PAO required? |
|---|---|---|---|---|
| Single Security Snapshot (40 controls, one-time score) | $500 + $1,000 = $1,500 | $1,000 + $1,500 = $2,500 | $1,500 + $2,500 = $4,000 | No |
| Progressing Security Snapshot (quarterly rescoring, monthly advisory) | $500 + $9,000 = $9,500 | $1,000 + $12,000 = $13,000 | $1,500 + $19,200 = $20,700 | No |
| Core (60 controls, PMO-validated, quarterly ConMon) | $500 + $10,000 = $10,500 | $1,000 + $13,000 = $14,000 | $1,500 + $21,000 = $22,500 | No |
| Ready (80 controls, monthly ConMon, annual assessment) | $500 + $3,500 = $4,000 | $1,000 + $8,500 = $9,500 | $1,500 + $15,750 = $17,250 | Yes |
| Authorized / Provisional (300+ controls, monthly ConMon, annual assessment) | $500 + $4,500 = $5,000 | $1,000 + $11,000 = $12,000 | $1,500 + $19,500 = $21,000 | Yes |
Two things in the table surprise first-time readers. Core’s PMO fee is higher than Ready’s or Authorized’s in every tier, because at Core the PMO does the validation work a 3PAO would otherwise do; the 3PAO invoice is what makes Ready and Authorized more expensive overall. And the Progressing Snapshot is priced monthly on its own page — $750, $1,000 or $1,600 a month by tier, three months paid up front — which is where the $9,000, $12,000 and $19,200 annual figures come from. The schedule states that pricing “reflects the lowest available membership tier”; higher membership levels with more benefits cost more.
| Cost | Typical range (2026, USD) | Notes |
|---|---|---|
| 3PAO assessment — Ready | $15,000 to $40,000 | 80 controls; scope and boundary size drive days; not included in PMO fees |
| 3PAO assessment — Authorized | $40,000 to $150,000+ | 300+ controls at Moderate; penetration testing usually included or added; annual reassessment recurs |
| Implementation and remediation | $20,000 to $250,000+ | The widest item: MFA, logging, vulnerability management, encryption, boundary work; far lower for a provider already at FedRAMP Moderate |
| Documentation: SSP, policies, procedures, POA&M, ConMon pack | $99 to $40,000 | Template pack against consultant-written; GovRAMP’s own templates are free to members |
| Internal staff time | $30,000 to $150,000 equivalent | Control implementation, evidence, monthly ConMon submissions |
| Sponsor engagement | Staff time | A government CIO sponsor or the Approvals Committee; no fee, but a relationship to build |
These are planning figures from published 3PAO practice and project experience, not quotes. The assessor row is the one to get in writing early: 3PAO capacity is finite and the Ready and Authorized statuses cannot be awarded without one.
| Provider | Path | Year-one GovRAMP cost (planning figure) | Recurring |
|---|---|---|---|
| SaaS start-up, under $1M revenue, no prior framework | Single Snapshot, then Progressing, then Core | $1,500 Snapshot; $9,500 Progressing; $10,500 Core — plus $20,000 to $60,000 remediation | $10,500 a year at Core plus ConMon effort |
| Mid-size provider, $1M–$5M, SOC 2 in place | Ready | $9,500 fees + $15,000 to $40,000 3PAO + $20,000 to $80,000 implementation | $9,500 fees + annual 3PAO reassessment |
| Established provider, over $5M, FedRAMP Moderate held | Fast Track to Authorized | $21,000 fees + a reduced 3PAO alignment engagement, since the federal SAR, RAR and ConMon data are reused; fees are the same as the standard process | $21,000 fees + monthly ConMon + annual assessment |
The third row is why the Fast Track matters: GovRAMP states the fees are identical to the standard process, so the saving is entirely in assessment and documentation effort, not in what GovRAMP charges.
How much does GovRAMP cost?
From the published schedule: membership of $500, $1,000 or $1,500 a year by revenue tier, plus PMO fees per stage — a Single Snapshot from $1,000, Core from $10,000, Ready from $3,500 and Authorized from $4,500 a year in the smallest tier, rising to $2,500, $21,000, $15,750 and $19,500 in the largest. Ready and Authorized add 3PAO assessment fees, typically $15,000 to $40,000 and $40,000 to $150,000 or more.
Why is Core more expensive than Ready in PMO fees?
Because the PMO validates Core itself; Ready and Authorized are assessed by a 3PAO, whose separate invoice makes them more expensive in total.
Is the Fast Track cheaper?
GovRAMP states the fees are the same as the standard process; the saving is in reusing federal SARs, RARs and continuous monitoring data instead of producing new assessment evidence.
Are the fees fixed?
The schedule has applied since 1 January 2025; PMO fees may increase annually by no more than the BLS rate published each June, with notice to the board by 1 September of the preceding year.
When are membership dues payable?
Annually on 1 June, to GovRAMP; programme fees are paid to RAMPQuest as the PMO.
Build the GovRAMP cost in three layers: the published dues and PMO fees for your tier and target stage, the 3PAO assessment if the target is Ready or Authorized, and the implementation and staff time that dwarf both. Choose the stage from the solicitations, not from ambition, draw the boundary tightly, and reuse every control already evidenced for FedRAMP, SOC 2 or ISO 27001.
The Pursuit Strategy, the Service Boundary and FIPS 199 Categorization documents, the System Security Plan, the Plan of Action and Milestones and the Monthly ConMon Pack are in the GovRAMP (StateRAMP) TX-RAMP Compliance Toolkit, or start with the free templates.


September 20, 2026

September 19, 2026

September 19, 2026

September 19, 2026

September 19, 2026

