CART
The ISAE 3402 vs ISO 27001 question almost never arrives as a free choice. It arrives as a line in a customer’s procurement pack, or as an email from their external auditor asking for “your service organization report” — and the organization that receives it already holds the other one. A certificate on the wall does not answer an auditor who needs an opinion on controls, and an auditor’s opinion does not answer a procurement team that wants a certificate to file.
This guide sets out the seven differences in ISAE 3402 vs ISO 27001 that change what you have to produce, how to tell from the request which one is wanted, and how much of an ISO 27001 management system a service auditor can reuse.
Free gap assessment
Where do you actually stand against ISO 27001?
Score every management system clause and all 93 Annex A controls, free, and get a prioritised gap list back.
Run the free ISO 27001 gap assessment → or View premium report sample
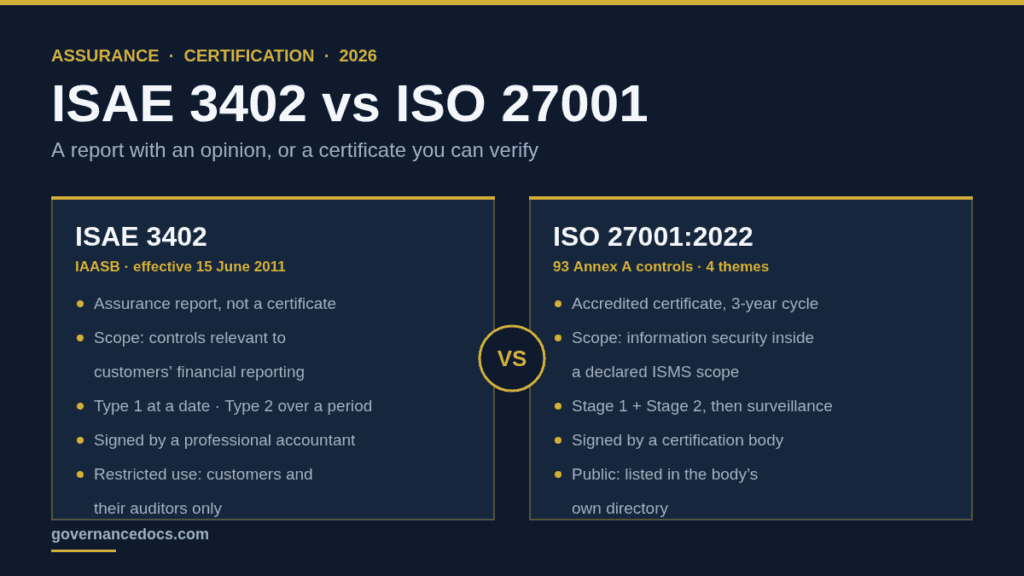
ISAE 3402, Assurance Reports on Controls at a Service Organization, is an assurance standard issued by the International Auditing and Assurance Standards Board. The IAASB announced it on 18 December 2009, and it is effective for service auditors’ reports covering periods ending on or after 15 June 2011. It has never been rewritten; the changes since have been conforming amendments, most recently in 2022.
It sits under ISAE 3000 (Revised), the framework standard for assurance engagements other than audits of historical financial information. Its scope is narrow and specific: controls at a service organization likely to be relevant to its customers’ internal control as it relates to financial reporting. That phrase is the whole boundary, and it is the first thing that separates ISAE 3402 vs ISO 27001. Payroll processing, claims administration, transfer agency, hosted accounting platforms — these are the engagements ISAE 3402 was written for.
The output is not a certificate. It is a report containing management’s description of the system, management’s written assertion, and a practitioner’s opinion. A type 1 report covers the description and the suitability of design as at a date. A type 2 report also covers operating effectiveness throughout a stated period, and includes the tests performed and their results. ISAE 3402 is the international counterpart of the American SOC 1; our ISAE 3402 guide covers that pairing in detail, and the SOC 1 report guide explains the document itself.
ISO/IEC 27001:2022 is a requirements standard for an information security management system. It is certifiable: an accredited certification body audits your management system in two stages, issues a three-year certificate, and returns for annual surveillance audits and a recertification audit in year three.
Its content is a management system — context, leadership, planning, support, operation, performance evaluation, improvement — plus Annex A, a reference set of 93 controls in four themes: 37 organizational, 8 people, 14 physical and 34 technological. Clause 6.1.3 makes the Statement of Applicability mandatory, which is where you record which of the 93 you apply and why you excluded any. The 2013 to 2022 transition period closed on 31 October 2025, so every valid certificate now cites the 2022 edition. Amendment 1:2024 added climate-change wording to clauses 4.1 and 4.2 and is published free of charge.
Free ISO 27001 risk assessment
Which of your risks sit above your appetite line?
Set your own risk criteria, pick from 61 information security risk scenarios, rate likelihood and impact, and decide how to treat each one. You get a heat map, a process score and the findings an auditor would raise, free.
Run the free risk assessment → or View premium report sample
Nothing in ISO 27001 asks whether a control matters to a customer’s financial statements — it asks whether risks to confidentiality, integrity and availability inside your declared scope are identified, treated and monitored. That is the second structural split in ISAE 3402 vs ISO 27001. Our complete ISO 27001 guide walks through the full requirement set.
Set side by side, ISAE 3402 vs ISO 27001 is not two versions of one thing. They answer different questions, for different readers, under different rules.
| Topic | ISAE 3402 | ISO 27001 |
|---|---|---|
| What it is | An assurance engagement producing a practitioner’s opinion | A management system standard producing a certificate |
| Subject matter | Controls relevant to customers’ internal control over financial reporting | Information security within a declared ISMS scope |
| Who sets the controls | Management defines the control objectives and controls; there is no fixed list | Annex A supplies 93 reference controls; the Statement of Applicability records your selection |
| Who signs it | A professional accountant, bound by the IESBA Code and firm-level quality management | An auditor employed by a certification body accredited to ISO/IEC 17021-1 |
| Time dimension | Type 1 as at a date; type 2 across a stated period, commonly six or twelve months | A point-in-time audit of a system that must be demonstrably running, on a three-year cycle |
| What you hand over | A full report: system description, management assertion, opinion, tests and results | A one-page certificate, usually supported by the scope statement and Statement of Applicability |
| Who may read it | Restricted use — intended for customers and their auditors only | Public; certificates are listed in the certification body’s directory |
The restricted-use point is the one that catches people out. An ISAE 3402 report cannot be posted on a trust page or handed to a prospect who is not yet a customer. If your goal is to shorten sales cycles with something publicly verifiable, the ISAE 3402 vs ISO 27001 decision resolves toward the certificate every time.
In practice the ISAE 3402 vs ISO 27001 answer is in the request itself — who sent it, and which words they used.
It is ISAE 3402 if the request came from or mentions the customer’s external auditor; if it uses the words “service auditor”, “user entity”, “type 2”, “control objectives” or “period covered”; if the customer is audited outside the United States; or if your service touches their transactions — anything that ends up as a number in their financial statements. Their auditor needs evidence they can rely on under their own auditing standards, and a certificate is not that evidence.
It is ISO 27001 if the request came from procurement, legal or a security team; if it arrived as a questionnaire row reading “ISO 27001 certified: Y/N”; if it mentions Annex A controls, a Statement of Applicability or your ISMS scope; or if it is a condition of a tender. Here the customer wants a verifiable third-party credential they can file, and they want it to cover information security broadly rather than financial-reporting relevance.
If the request names a SOC report instead, the comparison you want is ISO 27001 vs SOC 2 for security and availability, or SOC 1 for financial reporting. The ISAE 3402 vs ISO 27001 pairing specifically covers the case where an international customer’s auditor is involved.
The honest answer to “we already have ISO 27001, does that help?” is: substantially, for one layer of the report, and not at all for the rest. Almost every ISAE 3402 engagement contains IT general controls — logical access, change management, backup and recovery, job scheduling, monitoring. That layer maps closely onto Annex A, and an ISMS that genuinely runs already produces the evidence a service auditor tests.
| ISAE 3402 control area | ISO 27001 Annex A support | Carries over? |
|---|---|---|
| Logical access and user provisioning | A.5.15–A.5.18, A.8.2–A.8.5 | Yes — access reviews and joiner/mover/leaver records are the same evidence |
| Change management | A.8.31–A.8.32 | Yes, if change records show test and approval per change |
| Backup, recovery and availability | A.5.29–A.5.30, A.8.13–A.8.14 | Yes, with restore testing evidence |
| Monitoring and incident handling | A.5.24–A.5.28, A.8.15–A.8.16 | Yes |
| Transaction completeness and accuracy | None | No — application and process controls over transaction flow are outside the ISMS |
| Authorization of transactions | None | No |
| Management’s system description and assertion | None | No — a new document with no ISO 27001 equivalent |
Two more items have no ISO 27001 analogue and are frequently underestimated. The first is complementary user entity controls — the things your customers must do for your controls to work, which must be identified and stated. The second is subservice organizations: every provider you depend on has to be carved out or included, and carving out means telling the reader which of your control objectives they are relying on someone else for.
Organizations that end up holding both usually do it in this order, and the order matters.
Get the management system first. ISO 27001 forces you to define scope, own risk, approve policy, and run internal audit and management review. A service auditor arriving into that finds control owners who know what they own and a document set with version control and approval dates. The reverse — a type 2 examination at an organization with no management system — makes the examination do the governance work, at audit rates.
Then align the periods. A type 2 report covers a stated period; the ISO 27001 surveillance audit lands annually. Ending the type 2 period shortly before that audit lets one evidence-collection effort serve both, instead of pulling the same access reviews twice in a quarter.
Finally, write the control matrix once. Build a single register in which each row carries the control description, the owner, the Annex A reference and the ISAE 3402 control objective it supports. That register, not two separate ones, is what keeps the ISAE 3402 vs ISO 27001 overlap from turning into two parallel compliance programs.
Our ISO 27001 Toolkit gives you that document layer as a starting point — 165 templates covering the management system clauses and all 93 Annex A controls, in editable Microsoft Office format, for $99. It is the ISO 27001 half of the work, and the half an ISAE 3402 examination will lean on.
On both sides of ISAE 3402 vs ISO 27001 the figures depend on scope, headcount and how much already exists, so treat any number you read as a band rather than a price.
For ISO 27001, the certification body’s fee is driven by audit days, calculated from the number of people in scope. Our ISO 27001 certification cost breakdown sets out the typical ranges. Expect implementation to run longer than the audit: a first certification is typically months, not weeks.
For an ISAE 3402 examination, the fee sits in the same band as a SOC 1 engagement of equivalent scope, since it is the same work under a different standard — our SOC 1 audit cost breakdown is the closest usable guide. One timeline constraint has no ISO 27001 equivalent: a type 2 report cannot be issued until its period has elapsed. Asked in January for a report covering the calendar year, the answer is next year, with a type 1 report as the stopgap.
No. In ISAE 3402 vs ISO 27001 these are different instruments, and a customer’s auditor cannot substitute one for the other. ISO 27001 says a management system meets a standard’s requirements; ISAE 3402 gives an opinion on specified controls across a period, with the tests disclosed. If the request came from an auditor, only a report closes it.
Its scope is controls likely to be relevant to customers’ internal control as it relates to financial reporting. In practice that pulls in a substantial security and IT layer, because access, change and backup controls underpin the integrity of the data being processed. But a control with no financial-reporting relevance does not belong in an ISAE 3402 report, which is exactly why the ISAE 3402 vs ISO 27001 scopes cannot be treated as interchangeable.
ISO 27001, in most cases. It is the credential procurement teams recognize, it is publicly verifiable, and it builds the governance an examination later depends on. Add ISAE 3402 when a customer’s auditor asks — and they will ask, if your service touches their transactions.
Yes. Dual-standard reporting is routine where customers are audited on both sides of the Atlantic, and one system description can serve both. ISO 27001 cannot be bundled in; it remains a separate certification audit by an accredited body.
Not in the way a certificate does, but it goes stale. A type 2 report covers a defined period and provides no assurance after it. Customers expect a fresh report each year, and a bridge letter to cover the gap between the period end and their own year end.
Treat the ISAE 3402 vs ISO 27001 choice as a question about the reader, not about which standard is stronger. An auditor who must rely on your controls needs a report with an opinion and disclosed tests. A procurement team that must tick a box needs a certificate they can verify. Service organizations whose customers include both end up producing both, and the ones who do it cheaply are the ones who built the management system first and wrote the control register once.
For the ISO 27001 side, the ISO 27001 Toolkit covers the full document set — 165 templates, $99 — so the policies, the risk assessment and the Statement of Applicability are drafted before either auditor arrives. Full details of the standard itself are on the ISO 27001 page at iso.org.

October 24, 2026
October 23, 2026
October 23, 2026

October 22, 2026

October 22, 2026

