About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentGap AssessmentsBusiness Impact AnalysisISO 27001 Risk AssessmentContinuity Risk AssessmentEnterprise Risk AssessmentAI Risk AssessmentAI Impact AssessmentThird-Party Risk AssessmentAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 30, 2026

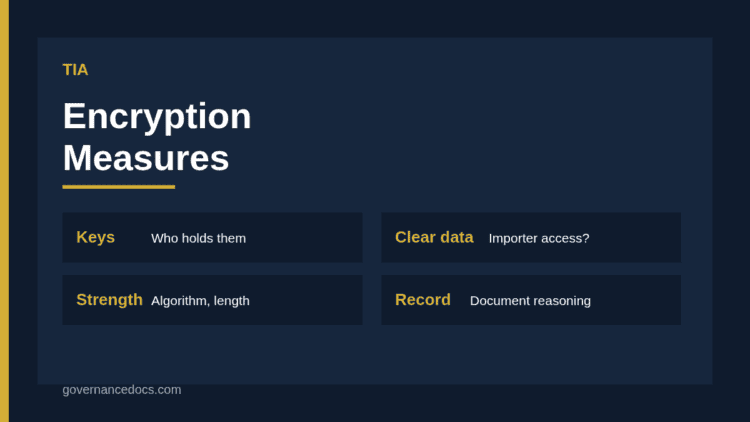
Encryption in a TIA decision flow showing key control, data in the clear and residual risk for a transfer

Encryption as a Supplementary Measure in a TIA: 2026

Governance Docs30th September 2026

How to assess encryption in a TIA: when it works as a supplementary measure, who must hold the…
Read More
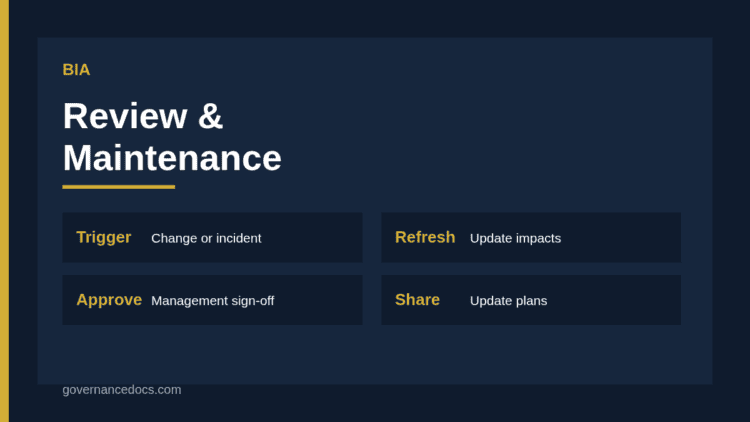
BIA review and maintenance cycle showing triggers, refresh, approval and communication of updated recovery priorities

BIA Review and Maintenance: A 2026 Guide

Governance Docs30th September 2026

How to handle BIA review and maintenance: refresh cycles, review triggers, ownership, what to check and how to…
Read More
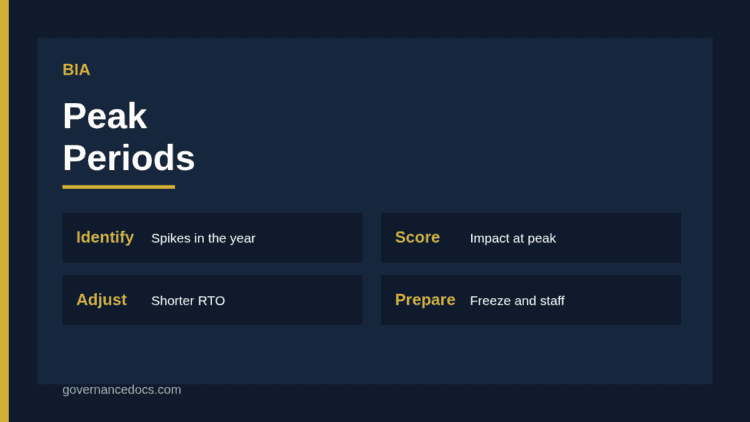
BIA peak periods calendar showing month-end, seasonal and event-driven spikes that raise disruption impact

BIA Peak Periods and Seasonality: 2026 Guide

Governance Docs30th September 2026

How to handle BIA peak periods: capturing seasonal, month-end and event-driven spikes, adjusting recovery targets and planning for…
Read More
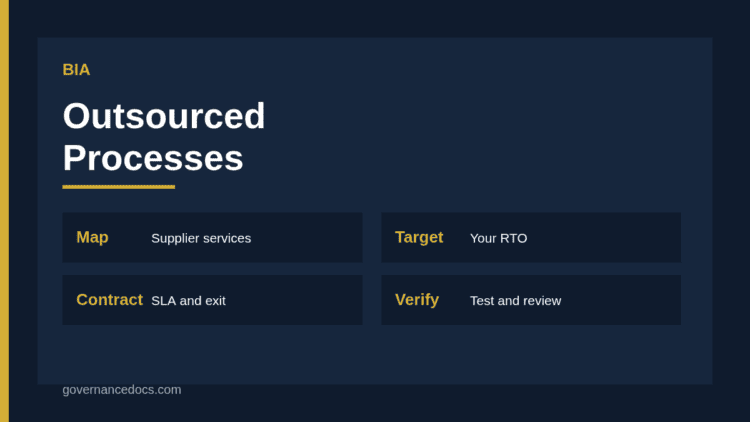
BIA for outsourced processes linking internal activities to supplier services, contract terms and recovery targets

BIA for Outsourced Processes: A 2026 Guide

Governance Docs30th September 2026

How to run a BIA for outsourced processes: mapping supplier-run activities, setting recovery expectations, reviewing contracts and verifying…
Read More
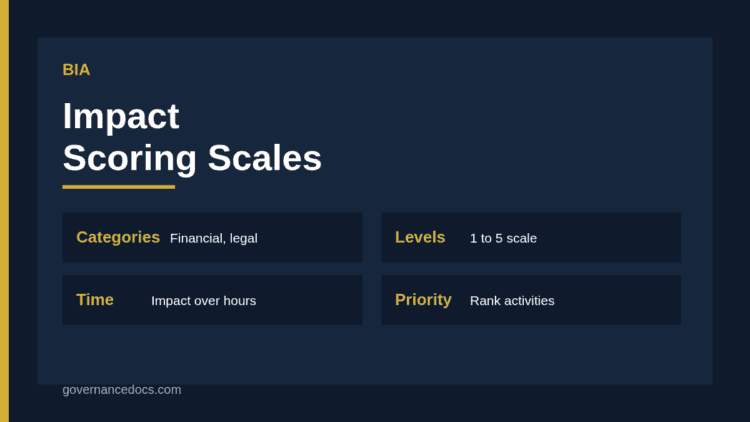
BIA impact scoring scales matrix showing impact categories and severity levels over time

BIA Impact Scoring Scales: A Practical 2026 Guide

Governance Docs30th September 2026

How to build BIA impact scoring scales: choosing impact categories, defining thresholds over time, calibrating ratings and linking…
Read More
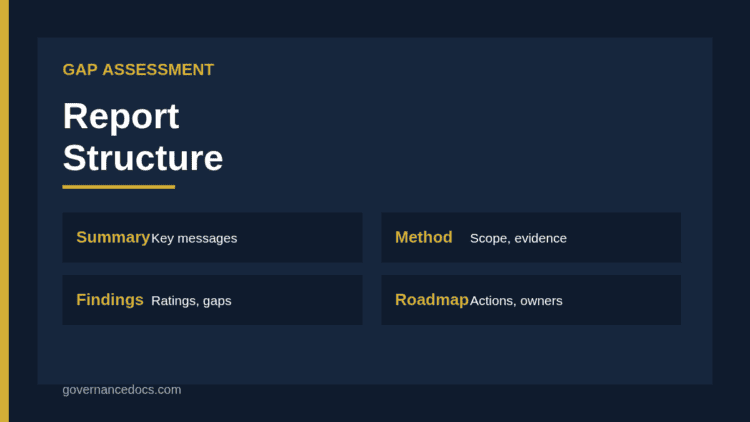
Gap assessment report structure showing executive summary, scope, method, findings, roadmap and appendices

Gap Assessment Report Structure: A 2026 Guide

Governance Docs30th September 2026

A practical gap assessment report structure: executive summary, scope, method, findings, ratings, roadmap and appendices that help leaders…
Read More
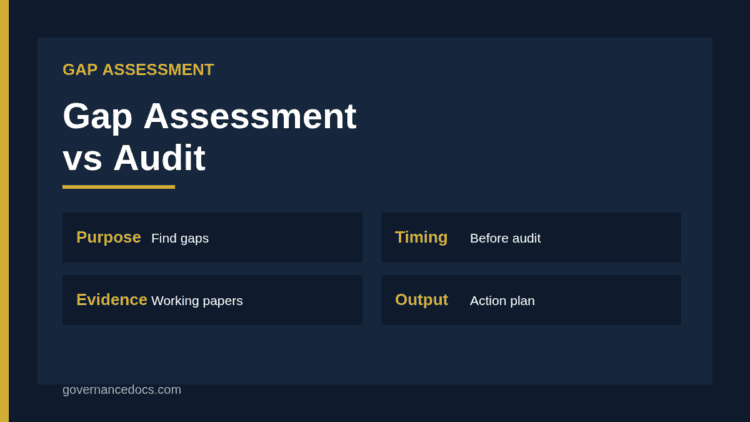
Gap assessment vs audit comparison of purpose, timing, independence and outputs

Gap Assessment vs Audit: Key Differences in 2026

Governance Docs30th September 2026

Gap assessment vs audit compared: purpose, timing, evidence, independence and outputs, and how to use both together when…
Read More
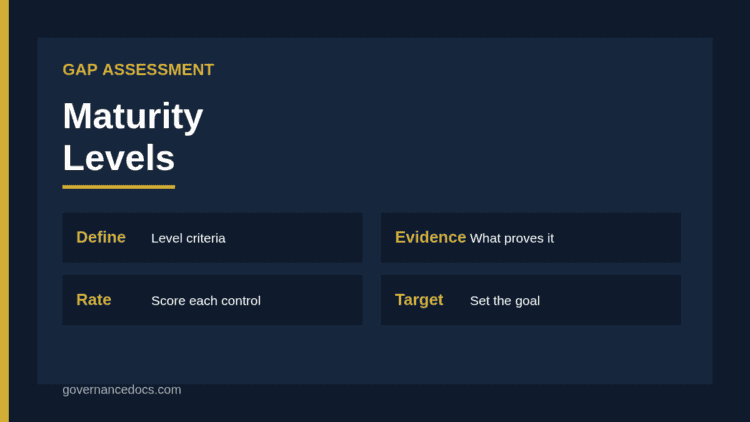
Gap assessment maturity levels scale from initial and repeatable to defined, managed and optimised with evidence examples

Gap Assessment Maturity Levels: A 2026 Guide

Governance Docs30th September 2026

How to use gap assessment maturity levels: building a five-level scale, defining each level with evidence, rating controls…
Read More
Legitimate interests and debt recovery process from account review to contact, tracing limits and safeguards

Legitimate Interests and Debt Recovery: 2026 Guide

Governance Docs30th September 2026

How to apply legitimate interests to debt recovery: the three-part test, data limits, tracing, collection agencies, transparency and…
Read More
Legitimate interests for intra-group data sharing between group companies with purpose, necessity and safeguards

Legitimate Interests for Intra-Group Data Sharing: 2026

Governance Docs30th September 2026

How to use legitimate interests for intra-group data sharing: what Recital 48 says, the three-part test, transparency, international…
Read More
Legitimate interests for B2C marketing decision flow from channel, consent rules and balancing test to opt-out

Legitimate Interests for B2C Marketing: 2026 Guide

Governance Docs30th September 2026

How to use legitimate interests for B2C marketing: the three-part test, ePrivacy limits on email and SMS, transparency,…
Read More
Legitimate interests for CCTV three-part test covering purpose, necessity and balancing against individual privacy

Legitimate Interests for CCTV: A 2026 Guide

Governance Docs30th September 2026

How to rely on legitimate interests for CCTV: the three-part test, weighing security against privacy, signage, retention and…
Read More

    ←
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • …
  • 9
  • →

Recent Posts

Gap assessment reassessment progress comparison diagram
Gap Assessment Reassessment: The Essential 2026 Guide to Measuring Progress

September 30, 2026

Business continuity supply chain risk map diagram
Business Continuity Supply Chain Risk: The Essential 2026 Guide to Resilient Suppliers

September 30, 2026

Business continuity risk appetite statement diagram
Business Continuity Risk Appetite: The Essential 2026 Guide to Setting Tolerance for Disruption

September 30, 2026

Business continuity risk monitoring indicators diagram
Business Continuity Risk Monitoring: The Essential 2026 Guide to Indicators and Reviews

September 30, 2026

Business continuity scenario planning steps diagram
Business Continuity Scenario Planning: The Essential 2026 Guide to Testing Your Plans

September 30, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA