About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: September 30, 2026

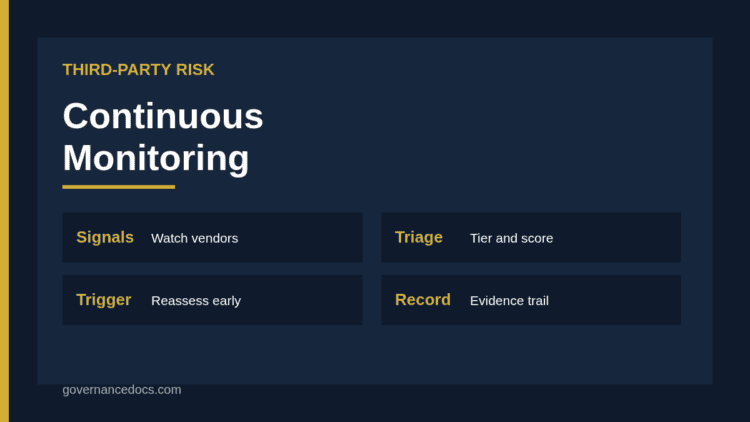
Third-party continuous monitoring dashboard showing vendor risk signals, triggers and reassessment actions

Third-Party Continuous Monitoring Guide 2026

Governance Docs30th September 2026

How to set up third-party continuous monitoring: which signals to watch, how to tier vendors, when to trigger…
Read More
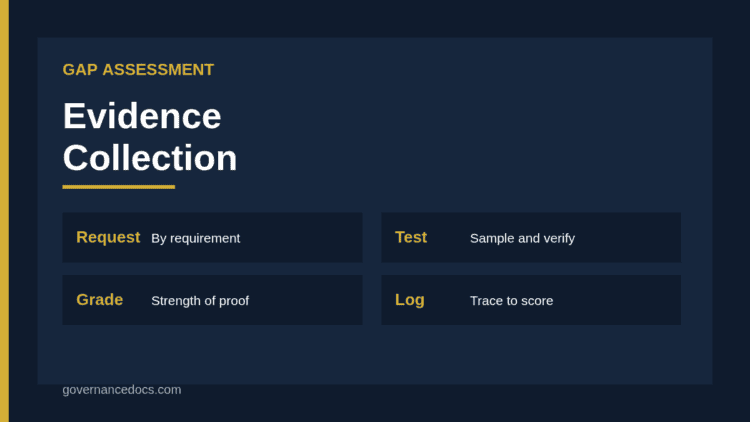
Gap assessment evidence log linking requirements to documents interviews and system samples

Gap Assessment Evidence Guide 2026: What to Collect

Governance Docs30th September 2026

What gap assessment evidence to collect, how to test it, how to grade its strength and how to…
Read More
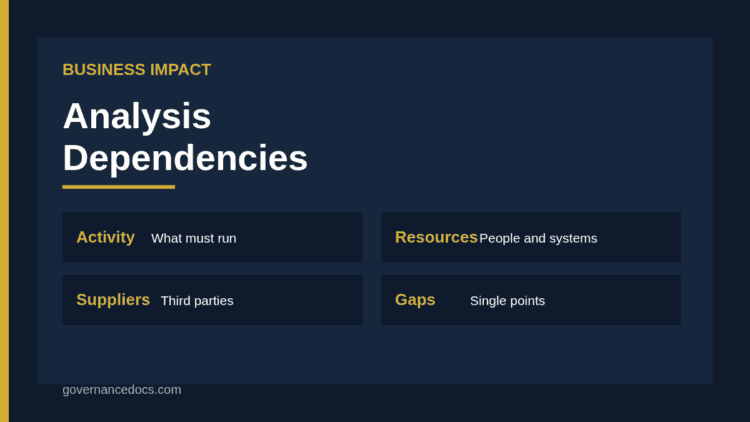
Business impact analysis dependencies map linking a critical activity to people systems suppliers and sites

Business Impact Analysis Dependencies Guide 2026

Governance Docs30th September 2026

How to identify and map business impact analysis dependencies: people, technology, suppliers, data and facilities, with a worked…
Read More
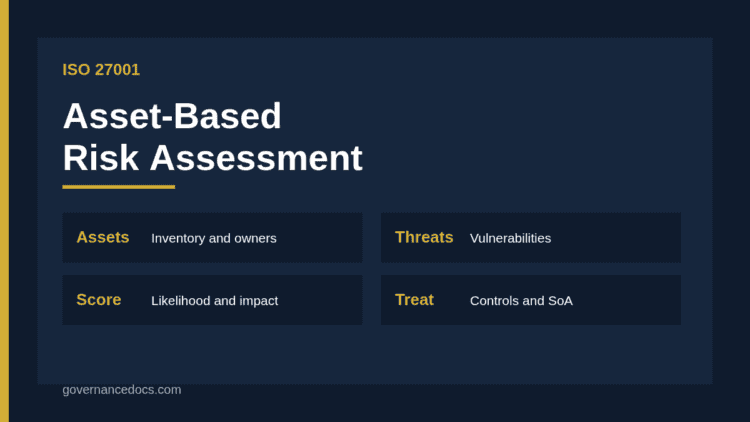
ISO 27001 asset-based risk assessment showing assets, threats and vulnerabilities feeding a risk score

ISO 27001 Asset-Based Risk Assessment Guide 2026

Governance Docs30th September 2026

How to run an ISO 27001 asset-based risk assessment: asset inventory, owners, threats, vulnerabilities, scoring, treatment and audit…
Read More
Privacy risk assessment methodology flow from data flows to scored risks and treatment

Privacy Risk Assessment Methodology Guide 2026

Governance Docs30th September 2026

How to build a privacy risk assessment methodology: scope, harm categories, likelihood and impact scales, scoring, treatment and…
Read More
Business continuity threat assessment matrix of natural technological and human threats

Business Continuity Threat Assessment Guide 2026

Governance Docs30th September 2026

How to run a business continuity threat assessment: threat categories, sources, likelihood and impact rating, scenario selection and…
Read More
Emerging risk identification funnel from horizon scanning to risk register

Emerging Risk Identification: A Practical Process 2026

Governance Docs30th September 2026

How to run emerging risk identification: horizon scanning, sources, triage criteria, scenario analysis, ownership and how to report…
Read More
AI model drift risk chart showing performance decaying over time against thresholds

AI Model Drift Risk: Monitoring and Response 2026

Governance Docs30th September 2026

How to assess and manage AI model drift risk: data drift, concept drift and performance decay, monitoring metrics,…
Read More
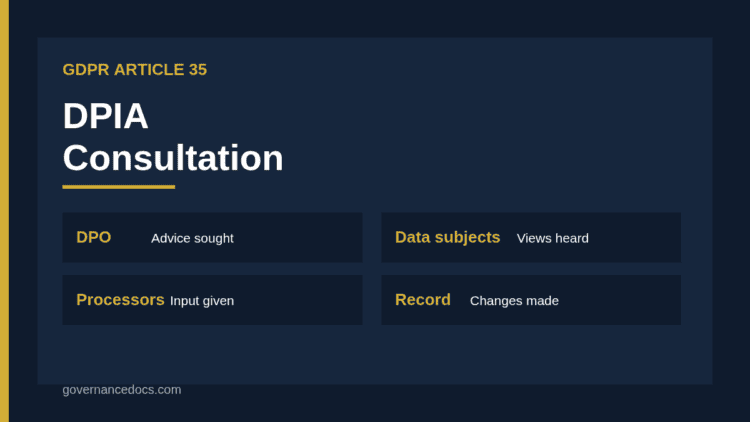
DPIA consultation with DPO data subjects and processors

DPIA Consultation: DPO Advice and Data Subject Views 2026

Governance Docs30th September 2026

How to run a DPIA consultation: seeking DPO advice, asking data subjects for their views, involving processors and…
Read More
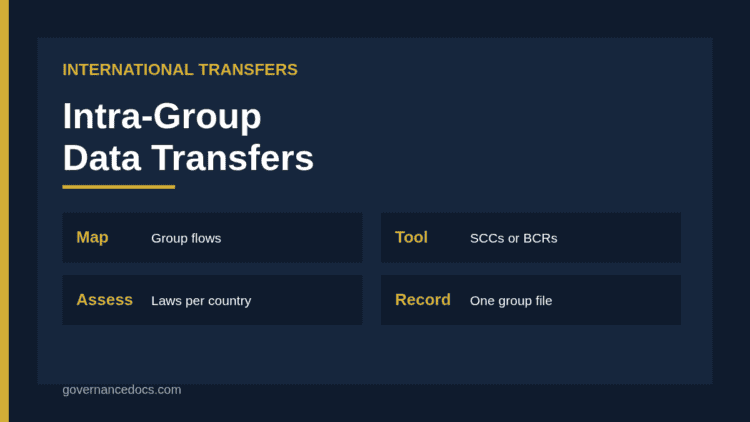
Intra-group data transfers between group companies with transfer mechanism and assessment

Intra-Group Transfers: Transfer Impact Assessment 2026

Governance Docs30th September 2026

Why intra-group data transfers need a transfer mechanism and a transfer impact assessment, how SCCs and BCRs work,…
Read More
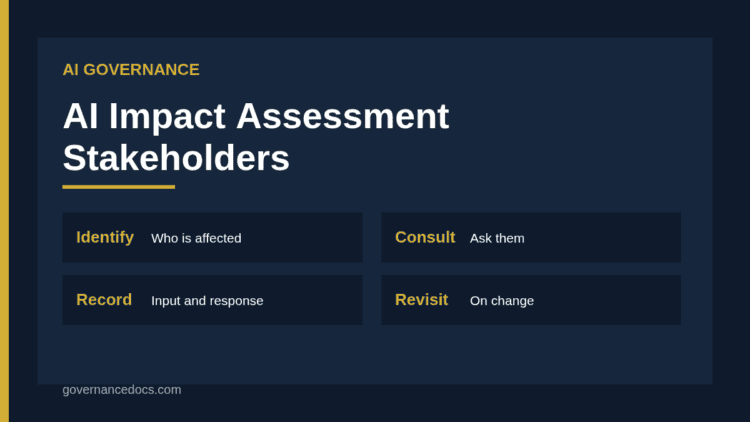
AI impact assessment stakeholders map of affected groups and internal owners

AI Impact Assessment Stakeholders: Who to Involve 2026

Governance Docs30th September 2026

How to identify and involve AI impact assessment stakeholders: affected groups, internal owners, external experts, consultation methods and…
Read More
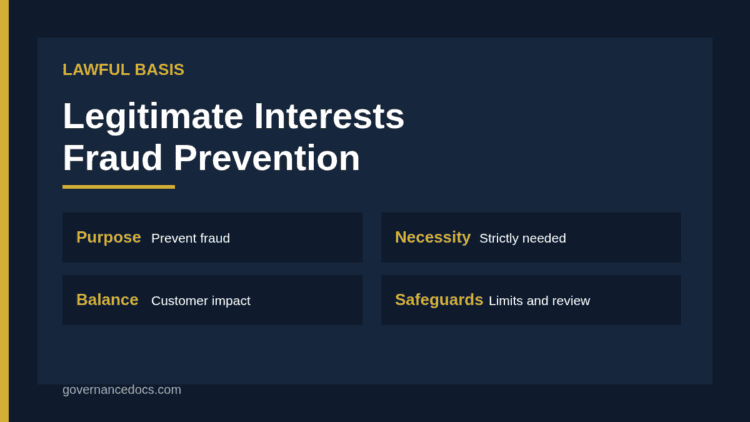
Legitimate interests fraud prevention assessment covering purpose necessity and balance

Legitimate Interests for Fraud Prevention 2026

Governance Docs30th September 2026

When legitimate interests supports fraud prevention: Recital 47, the three-part test, data sharing, profiling and automated decisions, safeguards…
Read More

    ←
  • 1
  • …
  • 9
  • 10
  • 11
  • 12
  • →

Recent Posts

ISO 27001 password policy requirements under Annex A 5.17 and A.8.5, with NIST, PCI DSS and Cyber Essentials length baselines compared
ISO 27001 Password Policy: Complete 2026 Requirements Guide

October 20, 2026

ISO 27001 intellectual property rights: the six categories in Annex A control 5.32
ISO 27001 Intellectual Property Rights: Complete 2026 Guide

October 20, 2026

ISO 27001 independent review under Annex A 5.35 compared with the clause 9.2 internal audit and clause 9.3 management review
ISO 27001 Independent Review: Complete A.5.35 Guide 2026

October 19, 2026

ISO 27001 acceptable use policy requirements under Annex A control A.5.10
ISO 27001 Acceptable Use Policy: Complete 2026 Guide

October 19, 2026

ISO 27001 network security controls A.8.20, A.8.21 and A.8.22 compared
ISO 27001 Network Security: Complete A.8.20–8.22 Guide 2026

October 18, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA