About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesGap AssessmentsBusiness Impact AnalysisAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Tag: Topic: Information Security

Derived from the related-toolkit resolver (WPCode 12925). Used to scope MailPoet post-notification digests. Archives noindexed.

NIST CSF audit checklist — NIST CSF Audit Checklist: 6 Fields Every Line Needs

NIST CSF Audit Checklist: 6 Fields Every Line Needs

Governance Docs06th September 2026

There is no CSF certification audit. What an internal NIST CSF audit checklist is for, the six fields…
Read More
NIST CSF maturity levels — NIST CSF Maturity Levels: A Clear 5-Point Scale That Works

NIST CSF Maturity Levels: A Clear 5-Point Scale That Works

Governance Docs06th September 2026

CSF 2.0 has no maturity model. Here is a defensible 5-point scale for scoring all 106 outcomes, why…
Read More
NIST CSF policy templates — NIST CSF Policy Templates: What All 106 Outcomes Need

NIST CSF Policy Templates: What All 106 Outcomes Need

Governance Docs06th September 2026

What NIST CSF policy templates must cover across the six Functions, the documents most programmes are missing, and…
Read More
NIST CSF to 800-53 mapping — NIST CSF to 800-53 Mapping: A Clear Guide to All 106

NIST CSF to 800-53 Mapping: A Clear Guide to All 106

Governance Docs06th September 2026

NIST maps all 106 CSF 2.0 outcomes to SP 800-53 Rev 5 with 740 control references. How to…
Read More
NIST CSF 2.0 vs 1.1 — NIST CSF 2.0 vs 1.1: The 79 Subcategories That Changed

NIST CSF 2.0 vs 1.1: The 79 Subcategories That Changed

Governance Docs06th September 2026

CSF 2.0 withdrew 79 Subcategories and removed 12 Categories. The full mapping, the 16 outcomes with no predecessor,…
Read More
NIST CSF GOVERN function — The NIST CSF GOVERN Function: All 31 Outcomes Explained

The NIST CSF GOVERN Function: All 31 Outcomes Explained

Governance Docs06th September 2026

The GOVERN function is 31 of the 106 CSF 2.0 outcomes across six Categories, ten of them supply…
Read More
NIST CSF Tiers — NIST CSF Tiers: A Clear Guide to the 4 Implementation Tiers

NIST CSF Tiers: A Clear Guide to the 4 Implementation Tiers

Governance Docs06th September 2026

The 4 NIST CSF Tiers explained, including the two axes CSWP 29 scores them on and why Tier…
Read More
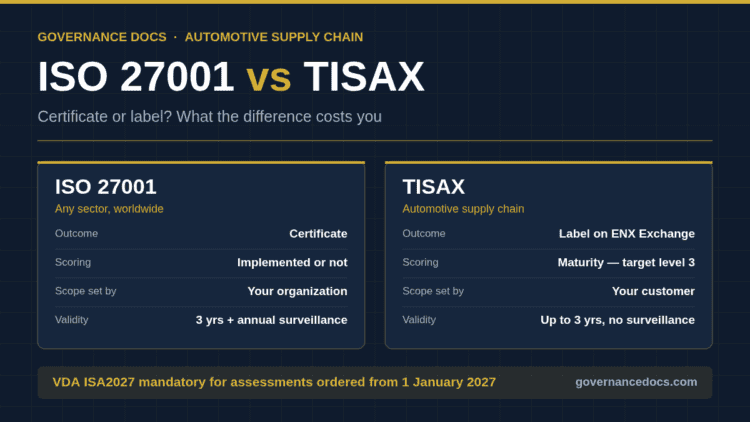
ISO 27001 vs TISAX comparison showing certificate versus ENX label, scoring and validity

ISO 27001 vs TISAX: The Complete 2026 Supplier Guide

Governance Docs06th September 2026

ISO 27001 vs TISAX compared for automotive suppliers: certificate versus ENX label, maturity level 3 scoring, AL2 vs…
Read More
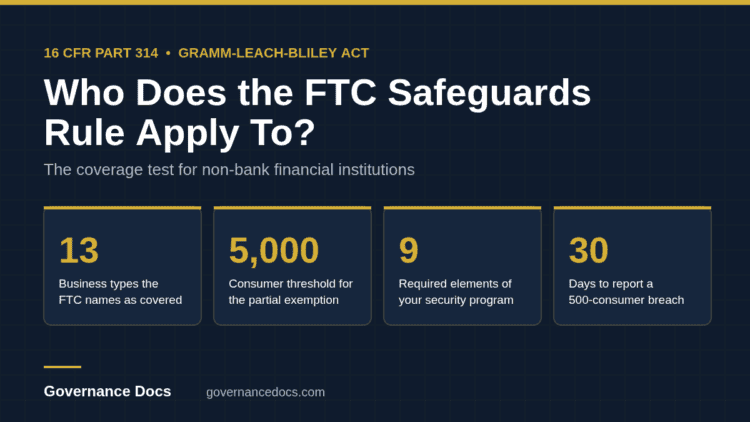
Infographic explaining who does the FTC Safeguards Rule apply to under 16 CFR Part 314

Who Does the FTC Safeguards Rule Apply To? The Complete 2026 Guide

Governance Docs05th September 2026

The FTC Safeguards Rule covers 13 types of non-bank financial institution, not just banks. Here is the two-part…
Read More
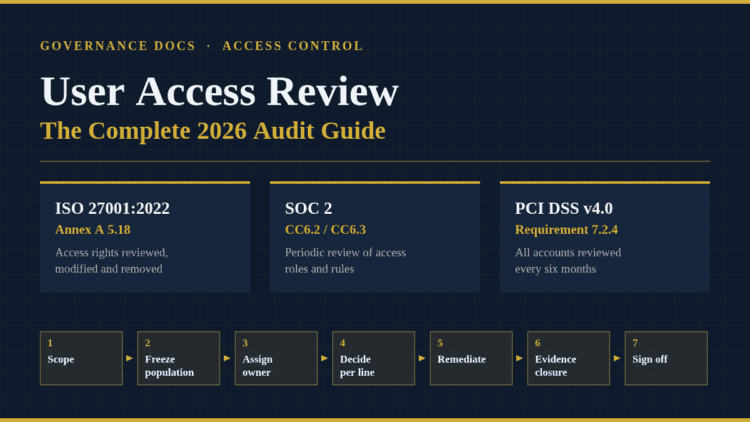
User access review process mapped to ISO 27001 Annex A 5.18, SOC 2 CC6.3 and PCI DSS 7.2.4

User Access Review: A Complete 2026 Guide for ISO 27001 and SOC 2

Governance Docs04th September 2026

A user access review is the control auditors test hardest. Here is the seven-step process, the ISO 27001…
Read More
wisp for sole practitioner

WISP for Sole Practitioners: 4 Elements You Can Safely Skip

Governance Docs03rd September 2026

A WISP for sole practitioners is smaller, but not for the reason most assume. What 16 CFR 314.6…
Read More
wisp for sole practitioner

FTC Safeguards Rule for Tax Preparers: The 10 Requirements

Governance Docs03rd September 2026

The FTC Safeguards Rule for tax preparers sets ten obligations at 16 CFR 314.4. What each requires, what…
Read More

    ←
  • 1
  • …
  • 4
  • 5
  • 6
  • 7
  • 8
  • …
  • 19
  • →

Recent Posts

Business Impact Analysis questionnaire with 30 essential questions for governance and risk.
Business Impact Analysis Questionnaire: 30 Essential Questions (2026)

September 26, 2026

Comparison of BIA and Risk Assessment for governance and business continuity planning.
BIA vs Risk Assessment: The Definitive 2026 Comparison

September 25, 2026

Business Impact Analysis example from Governance Docs website.
Business Impact Analysis Example: A Complete Worked BIA (2026)

September 25, 2026

Infographic answering is ISO 13485 worth it in 2026 with audit days, QMSR date and MDSAP regulators
Is ISO 13485 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Is ISO 42001 worth it in 2026 — audit days, first-year cost and Annex A controls at a glance
Is ISO 42001 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Gap assessments
  • Business impact analysis
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA