About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesGap AssessmentsBusiness Impact AnalysisAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Tag: Topic: Information Security

Derived from the related-toolkit resolver (WPCode 12925). Used to scope MailPoet post-notification digests. Archives noindexed.

Cyber Essentials renewal explained

Cyber Essentials Renewal: The Complete 12-Month Cycle (2026)

Governance Docs18th September 2026

Cyber Essentials renewal: 12-month validity, a full reassessment each year at £320–600, the April question-set change, Plus timing,…
Read More
Cyber Essentials vs ISO 27001 explained

Cyber Essentials vs ISO 27001: 10 Clear Differences (2026)

Governance Docs18th September 2026

Cyber Essentials vs ISO 27001 on 10 points: 5 prescribed controls vs a risk-based ISMS, cost, validity, who…
Read More
TISAX prototype protection explained

TISAX Prototype Protection: 20 ISA2027 Controls Explained (2026)

Governance Docs17th September 2026

TISAX prototype protection under ISA2027: the 20 controls in 8.1 and 8.2, the 4 objectives that trigger them,…
Read More
TISAX labels explained

TISAX Labels: All 12 Assessment Objectives Explained (2026 Guide)

Governance Docs17th September 2026

TISAX labels explained: the 12 assessment objectives, the info-security label hierarchy, the prototype and data protection objectives, and…
Read More
TISAX self-assessment explained

TISAX Self-Assessment: 6 Proven Steps to a Clean Audit (2026)

Governance Docs17th September 2026

How to run a TISAX self-assessment: the 6 ISA maturity levels 0–5, the target level 3, how the…
Read More
TISAX assessment levels explained

TISAX Assessment Levels: AL 1, 2 and 3 Explained (2026 Guide)

Governance Docs17th September 2026

TISAX assessment levels explained: what AL 1, AL 2, AL 2.5 and AL 3 involve, which of the…
Read More
ISO 20000 vs ISO 27001 explained

ISO 20000 vs ISO 27001: 5 Clear Differences Explained (2026)

Governance Docs17th September 2026

ISO 20000 vs ISO 27001 on 5 differences: purpose, what the audit tests, who asks, overlap, and which…
Read More
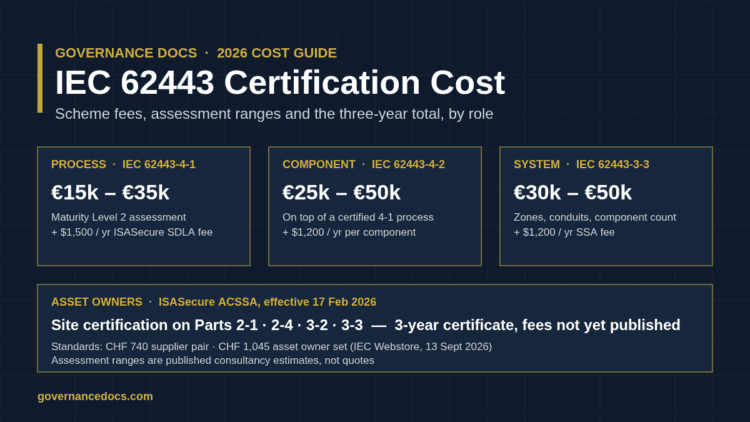
IEC 62443 certification cost infographic: process, component and system assessment ranges, ISASecure scheme fees and the ACSSA asset owner scheme

IEC 62443 Certification Cost in 2026: The Complete Guide

Governance Docs13th September 2026

IEC 62443 certification cost in 2026: ISASecure fees from $1,200 a year, assessment ranges of €15,000–€50,000 by role,…
Read More
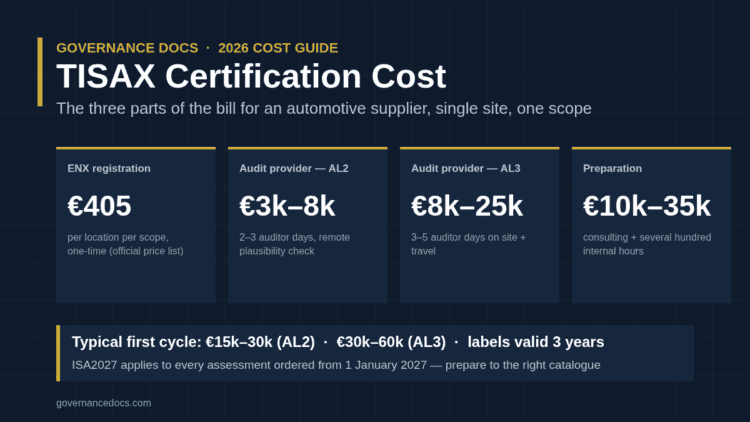
TISAX certification cost 2026 infographic: ENX fee €405, AL2 and AL3 audit provider ranges, preparation cost

TISAX Certification Cost in 2026: The Complete Breakdown

Governance Docs13th September 2026

TISAX certification cost in 2026: the €405 ENX fee, AL2 vs AL3 audit provider fees, preparation ranges, hidden…
Read More
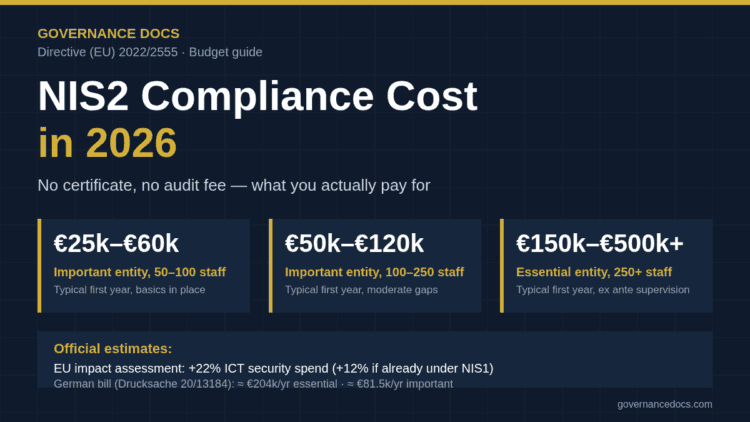
NIS2 compliance cost in 2026: typical first-year ranges for important and essential entities and the official EU and German estimates

NIS2 Compliance Cost in 2026: The Complete Breakdown

Governance Docs12th September 2026

NIS2 compliance cost in 2026 runs €25,000 to €120,000 in year one for most important entities, more for…
Read More
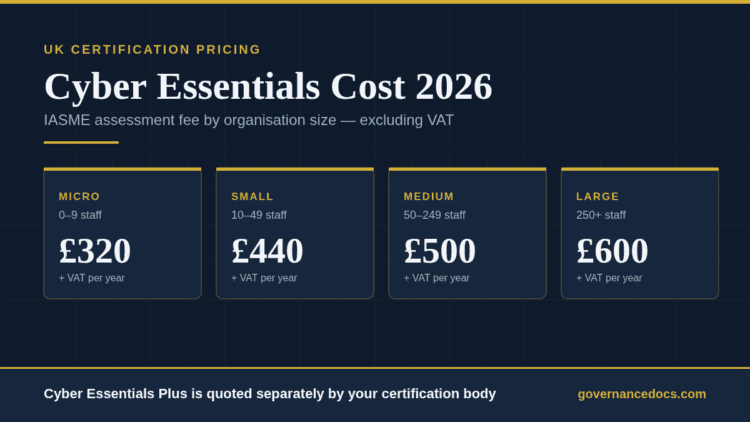
Cyber Essentials cost 2026 by organisation size: micro £320, small £440, medium £500, large £600 plus VAT

Cyber Essentials Cost 2026: The Complete UK Price Guide

Governance Docs10th September 2026

Cyber Essentials cost in 2026 runs £320 to £600 plus VAT by headcount, with Plus quoted separately from…
Read More
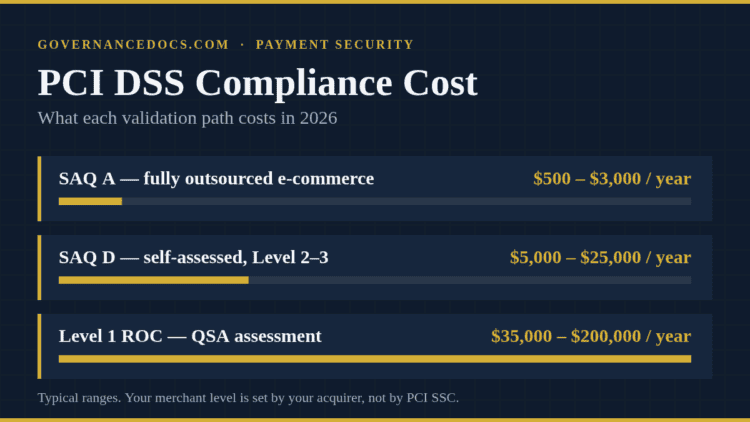
PCI DSS compliance cost by validation path in 2026, from SAQ A to a Level 1 ROC

PCI DSS Compliance Cost: A Clear 2026 Price Breakdown

Governance Docs10th September 2026

PCI DSS compliance cost in 2026 runs from about $500 a year on SAQ A to over $200,000…
Read More

    ←
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • …
  • 19
  • →

Recent Posts

Business Impact Analysis questionnaire with 30 essential questions for governance and risk.
Business Impact Analysis Questionnaire: 30 Essential Questions (2026)

September 26, 2026

Comparison of BIA and Risk Assessment for governance and business continuity planning.
BIA vs Risk Assessment: The Definitive 2026 Comparison

September 25, 2026

Business Impact Analysis example from Governance Docs website.
Business Impact Analysis Example: A Complete Worked BIA (2026)

September 25, 2026

Infographic answering is ISO 13485 worth it in 2026 with audit days, QMSR date and MDSAP regulators
Is ISO 13485 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Is ISO 42001 worth it in 2026 — audit days, first-year cost and Annex A controls at a glance
Is ISO 42001 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Gap assessments
  • Business impact analysis
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA