ISO 27001 vs ISO 27701: The Complete 2026 Decision Guide Governance Docs09th September 2026 ISO 27001 vs ISO 27701: since the 2025 edition a privacy system can be certified alone. Which you… Read More
ISO 27001 vs GDPR: The Complete 2026 Compliance Guide Governance Docs08th September 2026 ISO 27001 vs GDPR: certification proves you secure data, but GDPR asks whether you should hold it at… Read More
PCI PIN Remote Key Distribution: Normative Annex A Explained Governance Docs08th September 2026 Remote key distribution under PCI PIN Annex A: the two sub-annexes, the design assurance requirement, the three barrier… Read More
PCI PIN Key Injection Facility: Normative Annex B Explained Governance Docs08th September 2026 Key injection facility requirements under PCI PIN Annex B: the secure room, the clear-text injection dates and their… Read More
Qualified PIN Assessor: What a PCI PIN Assessment Involves Governance Docs08th September 2026 Qualified PIN Assessor explained: no self-assessment route, observation-led testing, the two-year listing clock that starts at signature, and… Read More
Dual Control and Split Knowledge: The Difference That Fails Audits Governance Docs08th September 2026 Dual control and split knowledge are two separate controls, not one. What each requires, the arrangements that look… Read More
PCI PIN Scope: Which of the 145 Requirements Apply to You Governance Docs08th September 2026 PCI PIN scope explained: the four requirement columns, why 96 + 85 + 105 + 94 does not… Read More
PCI PIN Key Blocks: The 3 Phases and What Phase 3 Did Not Require Governance Docs08th September 2026 PCI PIN key blocks explained: the three phases, why Phase 3 never required existing POI deployments to convert,… Read More
PCI PIN vs PCI DSS: Which One Applies to You in 2026 Governance Docs08th September 2026 PCI PIN vs PCI DSS explained: different assessors, no self-assessment route for PIN, a two-year cycle, and scope… Read More
PCI PIN Security Requirements: A Complete Guide to v3.1 in 2026 Governance Docs08th September 2026 PCI PIN Security Requirements v3.1 explained: 7 control objectives, 33 requirements, 145 sub-requirements, the four scope columns and… Read More
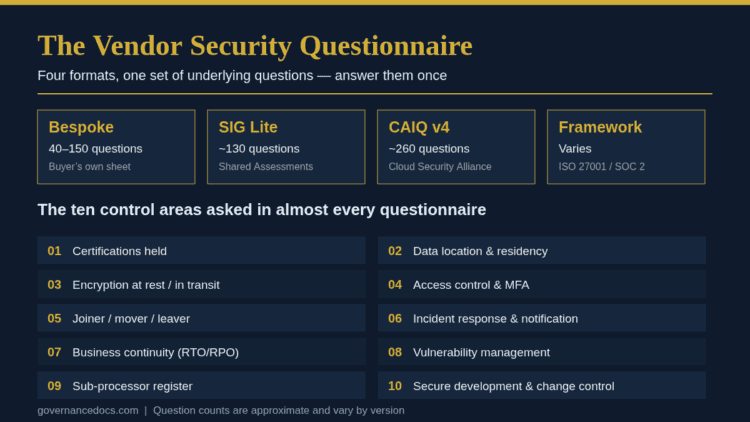
Vendor Security Questionnaire: The Complete 2026 Response Playbook Governance Docs07th September 2026 A vendor security questionnaire slows deals only when you improvise. Here are the four formats, the ten recurring… Read More
FedRAMP Compliance Checklist: The Best 8 Steps for 2027 Governance Docs06th September 2026 A FedRAMP compliance checklist for 2026: the 8 steps in order, the Rev5 and 20x paths, and the… Read More