About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesGap AssessmentsBusiness Impact AnalysisAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Tag: Topic: Information Security

Derived from the related-toolkit resolver (WPCode 12925). Used to scope MailPoet post-notification digests. Archives noindexed.

written information security plan template

Written Information Security Plan Template: The 10 Elements

Governance Docs03rd September 2026

A written information security plan template is only the shape. Here is what a WISP must contain under…
Read More
NERC CIP vs IEC 62443 — NERC CIP vs IEC 62443: The Complete 2026 Comparison

NERC CIP vs IEC 62443: A Clear 2026 Comparison

Governance Docs03rd September 2026

NERC CIP vs IEC 62443 compared: mandatory versus voluntary, impact ratings versus zones and conduits, and how to…
Read More
NERC CIP audit — NERC CIP Audit: The Complete 2026 Preparation Guide

NERC CIP Audit: The Complete 2026 Preparation Guide

Governance Docs03rd September 2026

NERC CIP audit preparation: writing the RSAW narrative, computing your own intervals, the three checks worth running first,…
Read More
CIP-015 — CIP-015: Internal Network Security Monitoring in 2026

CIP-015: Internal Network Security Monitoring in 2026

Governance Docs03rd September 2026

CIP-015 internal network security monitoring is not enforceable until 1 October 2028, not September 2025. What the standard…
Read More
CIP-014 physical security — CIP-014 Physical Security: The Complete 2026 Guide

CIP-014 Physical Security: The Complete 2026 Guide

Governance Docs03rd September 2026

CIP-014 physical security explained: the two separate unaffiliated third-party gates at R2 and R6, the six R5 functions,…
Read More
CIP-013 supply chain — CIP-013 Supply Chain: The Complete 2026 Guide

CIP-013 Supply Chain: The Complete 2026 Guide

Governance Docs03rd September 2026

CIP-013 supply chain risk management: the planning stage everyone skips, the six procurement elements, and what to do…
Read More
NERC CIP patch management — NERC CIP Patch Management: The Complete 2026 Guide

NERC CIP Patch Management: The Complete 2026 Guide

Governance Docs03rd September 2026

NERC CIP patch management under CIP-007 R2: the two separate 35-calendar-day clocks, named patch sources, and mitigation plans…
Read More
NERC CIP low impact — NERC CIP Low Impact: The Complete 2026 Guide

NERC CIP Low Impact: The Complete 2026 Guide

Governance Docs03rd September 2026

NERC CIP low impact explained: the seven CIP-003 Attachment 1 topics, the vendor remote access control added in…
Read More
BES Cyber System categorization — BES Cyber System Categorization: A Complete CIP-002 Guide

BES Cyber System Categorization: A Complete CIP-002 Guide

Governance Docs03rd September 2026

BES Cyber System categorization under CIP-002: the high, medium and low criteria, the process auditors test, and the…
Read More
NERC CIP compliance — NERC CIP Compliance: The Complete 2026 Guide

NERC CIP Compliance: The Complete 2026 Guide

Governance Docs03rd September 2026

NERC CIP compliance explained: how RSAW audits work, the three evidence rules, the compliance calendar, and where programmes…
Read More
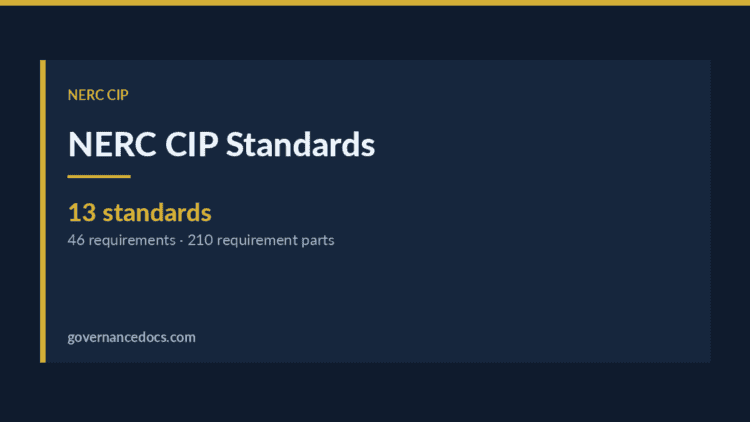
NERC CIP standards — NERC CIP Standards: The Complete 2026 Guide to All 13

NERC CIP Standards: The Complete 2026 Guide to All 13

Governance Docs03rd September 2026

NERC CIP standards explained: all 13 enforceable standards, 46 requirements, the 2028 cutover, and why CIP-015 is not…
Read More
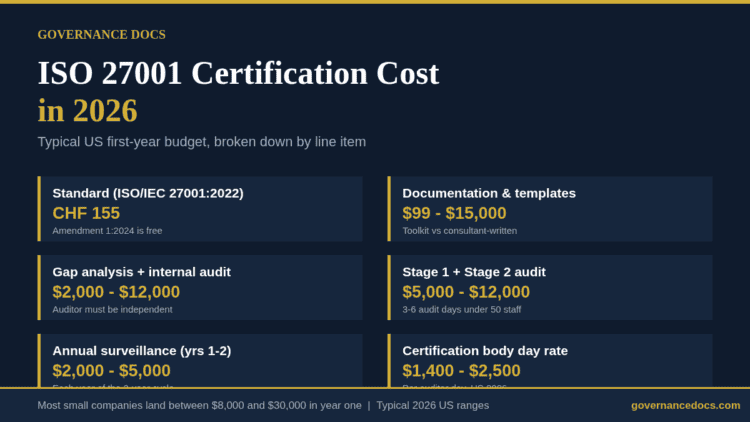
ISO 27001 certification cost breakdown for 2026 showing audit fees, day rates and surveillance costs

ISO 27001 Certification Cost in 2026: The Complete Breakdown

Governance Docs03rd September 2026

ISO 27001 certification cost in 2026 runs $8,000 to $30,000 for most small US companies. A full line-item…
Read More

    ←
  • 1
  • …
  • 5
  • 6
  • 7
  • 8
  • 9
  • …
  • 19
  • →

Recent Posts

Business Impact Analysis questionnaire with 30 essential questions for governance and risk.
Business Impact Analysis Questionnaire: 30 Essential Questions (2026)

September 26, 2026

Comparison of BIA and Risk Assessment for governance and business continuity planning.
BIA vs Risk Assessment: The Definitive 2026 Comparison

September 25, 2026

Business Impact Analysis example from Governance Docs website.
Business Impact Analysis Example: A Complete Worked BIA (2026)

September 25, 2026

Infographic answering is ISO 13485 worth it in 2026 with audit days, QMSR date and MDSAP regulators
Is ISO 13485 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Is ISO 42001 worth it in 2026 — audit days, first-year cost and Annex A controls at a glance
Is ISO 42001 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Gap assessments
  • Business impact analysis
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA