About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesGap AssessmentsBusiness Impact AnalysisAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Tag: Topic: Information Security

Derived from the related-toolkit resolver (WPCode 12925). Used to scope MailPoet post-notification digests. Archives noindexed.

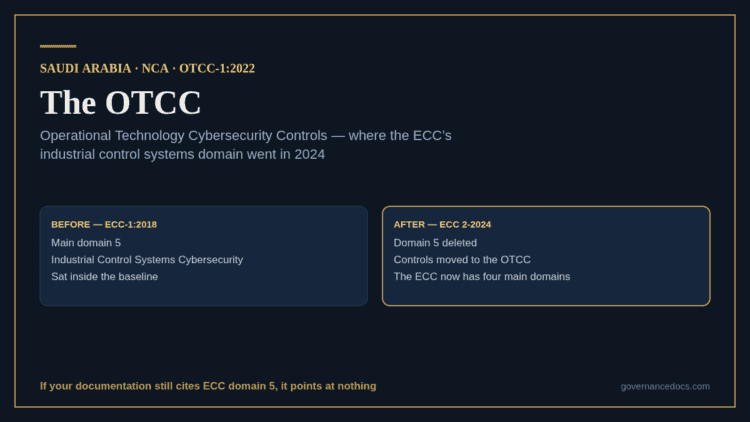
The OTCC absorbed the ECC main domain 5 for industrial control systems

OTCC: A Clear Guide to Saudi OT Cybersecurity in 2026

Governance Docs30th August 2026

The OTCC absorbed the ECC's industrial control systems domain in 2024. What it covers, how it differs from…
Read More
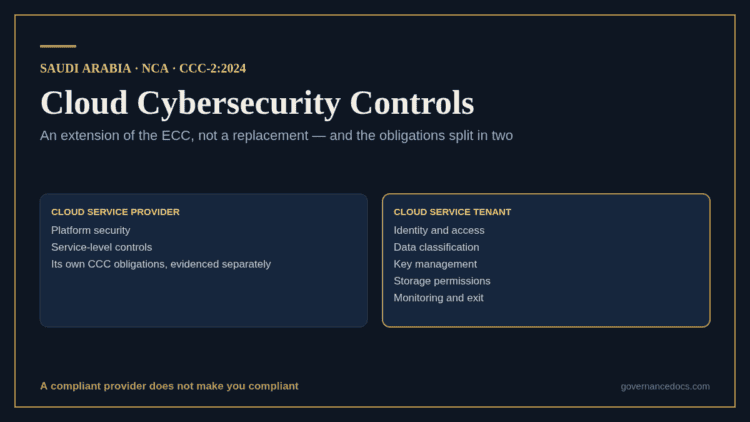
Cloud Cybersecurity Controls: how CCC-2:2024 splits obligations between provider and tenant

Cloud Cybersecurity Controls: A Clear CCC-2:2024 Guide

Governance Docs30th August 2026

The Cloud Cybersecurity Controls split obligations between provider and tenant. CCC-2:2024, the 6 responsibility areas, and what changed…
Read More
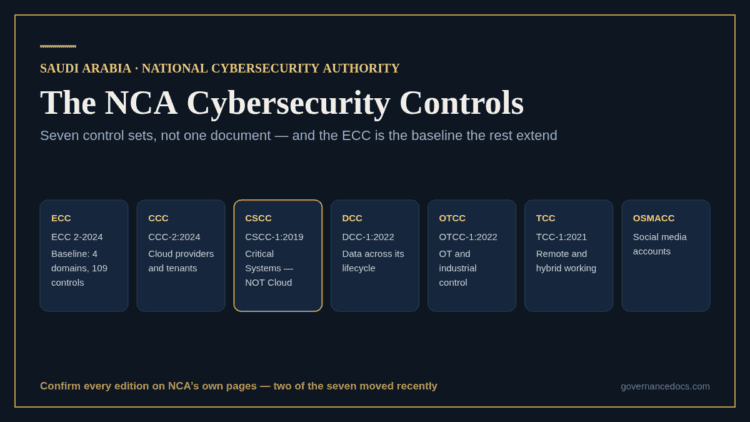
Overview of Saudi Arabia's NCA cybersecurity control sets and standards.

NCA Cybersecurity Controls: A Clear Guide to All 7 Sets

Governance Docs30th August 2026

The 7 NCA cybersecurity controls sets and their current editions, which apply to you, and why CSCC is…
Read More
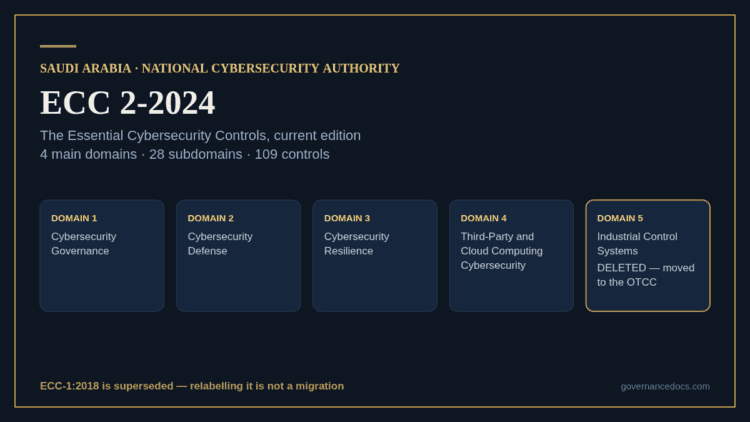
Saudi Arabia National Cybersecurity Authority ECC 2-2024 document overview.

ECC 2-2024: A Clear Guide to All 4 Domains

Governance Docs30th August 2026

ECC 2-2024 replaced ECC-1:2018 and deleted a whole domain. The 4 domains, 109 controls, where the ICS controls…
Read More
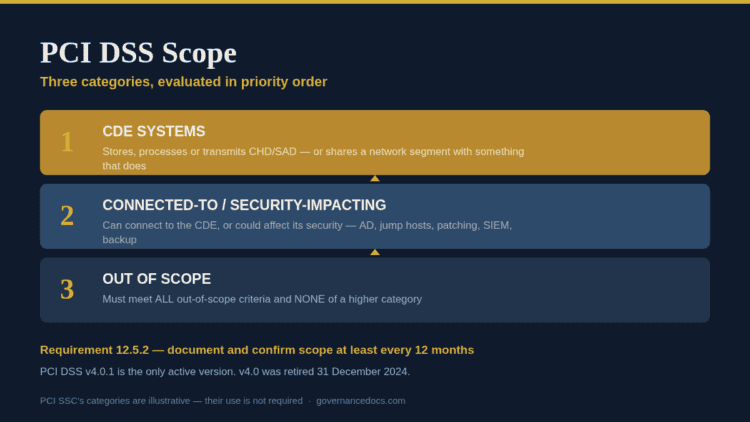
Diagram showing PCI DSS scope categories and their importance in security.

PCI DSS Scope: A Clear Guide to All 3 Categories

Governance Docs30th August 2026

How PCI DSS scope is decided: the 3 system categories in priority order, the annual confirmation under Requirement…
Read More
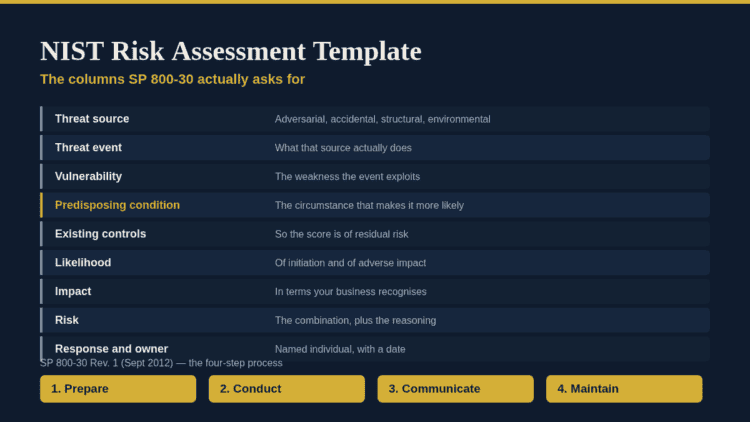
NIST Risk Assessment Template showing threat source, event, vulnerability, and controls.

NIST Risk Assessment Template: A Clear Guide to 4 Steps

Governance Docs30th August 2026

What a NIST risk assessment template must contain, the 4 steps of SP 800-30, and how it differs…
Read More
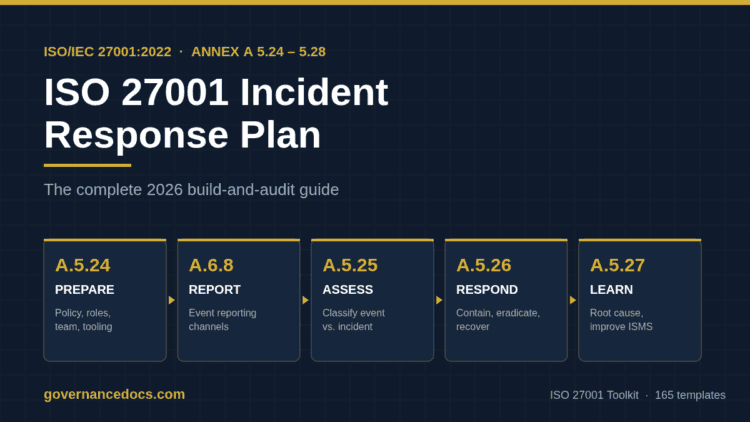
ISO 27001 incident response plan lifecycle across Annex A controls 5.24 to 5.27

ISO 27001 Incident Response Plan: The Complete 2026 Guide

Governance Docs30th August 2026

What an ISO 27001 incident response plan must contain, the Annex A 5.24 to 5.28 controls behind it,…
Read More
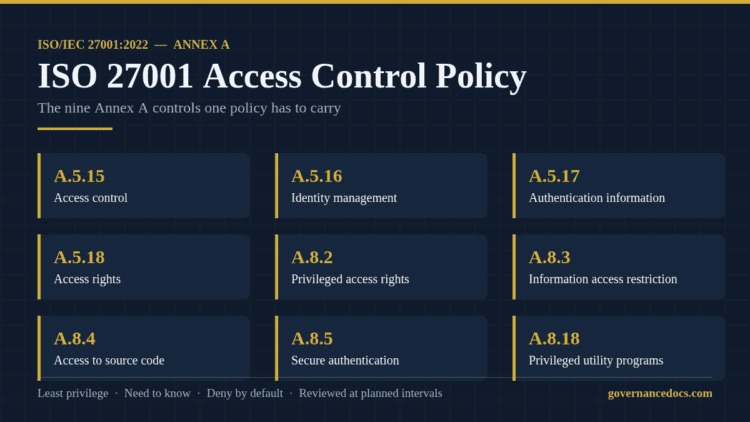
Diagram of ISO 27001 access control policy and annexes.

ISO 27001 Access Control Policy: The Complete 2026 Guide

Governance Docs29th August 2026

What an ISO 27001 access control policy must contain in 2026 — the nine Annex A controls it…
Read More
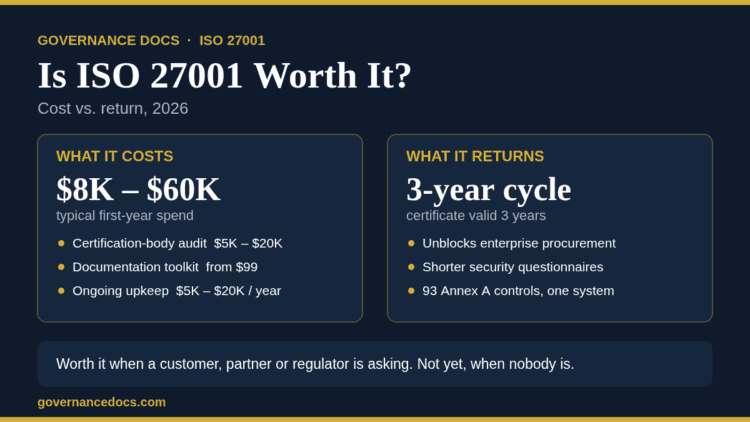
Is ISO 27001 worth it: 2026 cost versus return comparison

Is ISO 27001 Worth It? The Complete 2026 ROI Breakdown

Governance Docs28th August 2026

Is ISO 27001 worth it in 2026? A straight cost-versus-return breakdown: typical $8,000-$60,000 first-year spend, what certification actually…
Read More
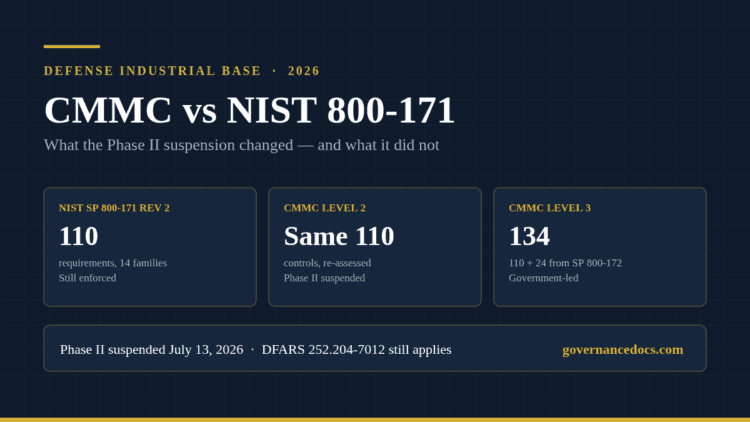
Comparison of CMMC and NIST 800-171 security standards for defense industrial base.

CMMC vs NIST 800-171: The Complete 2026 Guide for Defense Contractors

Governance Docs27th August 2026

CMMC vs NIST 800-171 explained for 2026. The Department of War suspended CMMC Phase II on July 13,…
Read More
NIS2 IEC 62443 mapping chart for cybersecurity governance.

NIS2 IEC 62443 Mapping: The Complete 2026 Guide

Governance Docs26th August 2026

A NIS2 IEC 62443 mapping of all ten Article 21(2) measures, plus the Article 23 reporting clock and…
Read More
Secure remote access with no direct path for governance and compliance.

OT Secure Remote Access: The Complete 2026 IEC 62443 Guide

Governance Docs26th August 2026

OT secure remote access under IEC 62443: jump host architecture, individual identities and MFA, vendor access rules, session…
Read More

    ←
  • 1
  • …
  • 9
  • 10
  • 11
  • 12
  • 13
  • …
  • 19
  • →

Recent Posts

Business Impact Analysis questionnaire with 30 essential questions for governance and risk.
Business Impact Analysis Questionnaire: 30 Essential Questions (2026)

September 26, 2026

Comparison of BIA and Risk Assessment for governance and business continuity planning.
BIA vs Risk Assessment: The Definitive 2026 Comparison

September 25, 2026

Business Impact Analysis example from Governance Docs website.
Business Impact Analysis Example: A Complete Worked BIA (2026)

September 25, 2026

Infographic answering is ISO 13485 worth it in 2026 with audit days, QMSR date and MDSAP regulators
Is ISO 13485 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Is ISO 42001 worth it in 2026 — audit days, first-year cost and Annex A controls at a glance
Is ISO 42001 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Gap assessments
  • Business impact analysis
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA