BSI C5 Attestation: A Clear Guide to Type 1 and Type 2 Governance Docs02nd September 2026 A BSI C5 attestation is an assurance report, not a certificate. Type 1 vs type 2, what the… Read More
Cyber Essentials Plus: A Clear Guide to the 2026 Audit Governance Docs02nd September 2026 Cyber Essentials Plus tests the same 5 controls independently. What the 2026 Danzell update changed, the new auto-fail… Read More
Cybersecurity Metrics: A Clear Guide to the 4 Types That Matter Governance Docs02nd September 2026 Cybersecurity metrics that survive scrutiny: the 4 measure types in NIST SP 800-55, the 10 fields that document… Read More
NIST CSF Organizational Profile: A Clear Guide to the 5 Steps Governance Docs02nd September 2026 A NIST CSF organizational profile in 5 steps from NIST SP 1301: scope, gather, create, analyze gaps, implement… Read More
FedRAMP SSP: A Clear Guide to the 2 Documents That Replaced It Governance Docs02nd September 2026 The FedRAMP SSP was retired in 2026. What replaced it: the Certification Package Overview and the Security Decision… Read More
FedRAMP ATO: A Clear Guide to the 5 Agency Steps in 2026 Governance Docs02nd September 2026 A FedRAMP ATO is the agency's risk decision, not FedRAMP's. The 5 steps of initial agency authorization in… Read More
TISAX Audit Checklist: A Clear Guide to the 7 ISA 2027 Steps Governance Docs02nd September 2026 A TISAX audit checklist for ISA 2027: which catalogue applies from 1 January 2027, the 7 preparation steps,… Read More
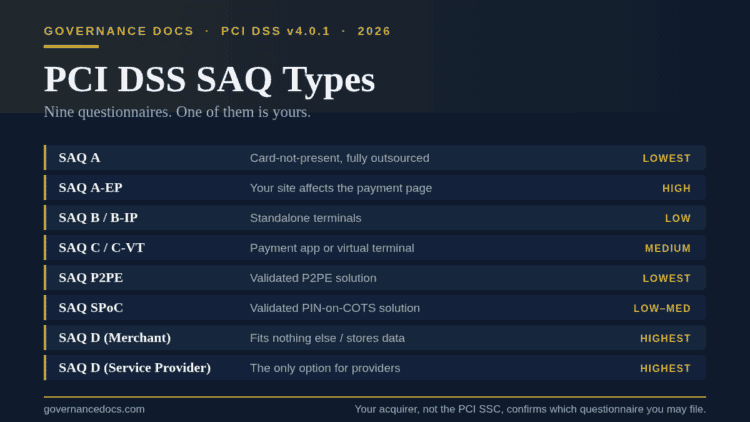
PCI DSS SAQ Types: The Complete 2026 Guide to Choosing Yours Governance Docs02nd September 2026 There are nine PCI DSS SAQ types in v4.0.1. This 2026 guide compares all of them, explains the… Read More
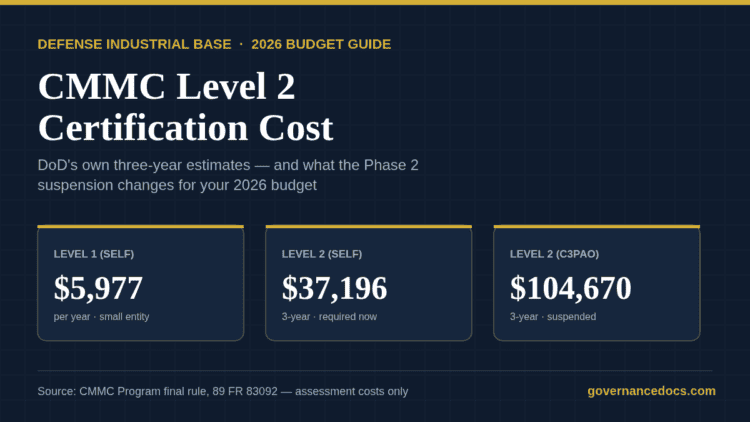
CMMC Level 2 Certification Cost: The Complete 2026 Breakdown Governance Docs01st September 2026 CMMC Level 2 certification cost runs about $104,670 over three years in DoD's own rule. Here's what to… Read More
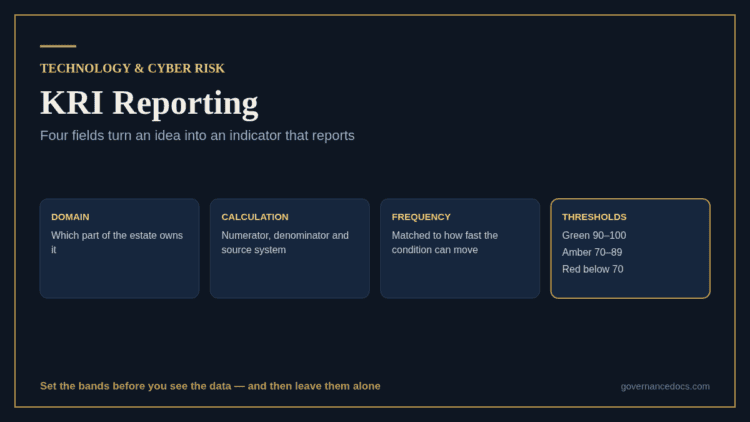
KRI Reporting: A Clear Guide to the 4 Core Fields Governance Docs31st August 2026 KRI reporting fails when indicators are picked for easy data. The 4 fields every KRI needs, RAG thresholds… Read More
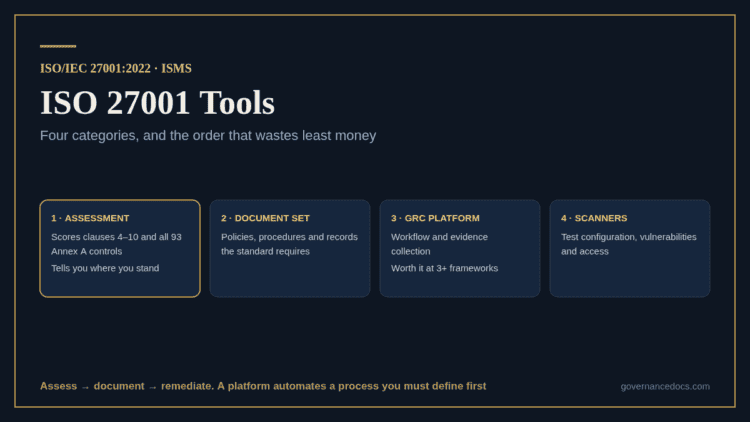
ISO 27001 Tools: Complete Guide to the 4 Categories Governance Docs31st August 2026 ISO 27001 tools range from a spreadsheet to a GRC platform. The 4 categories, what an assessment tool… Read More
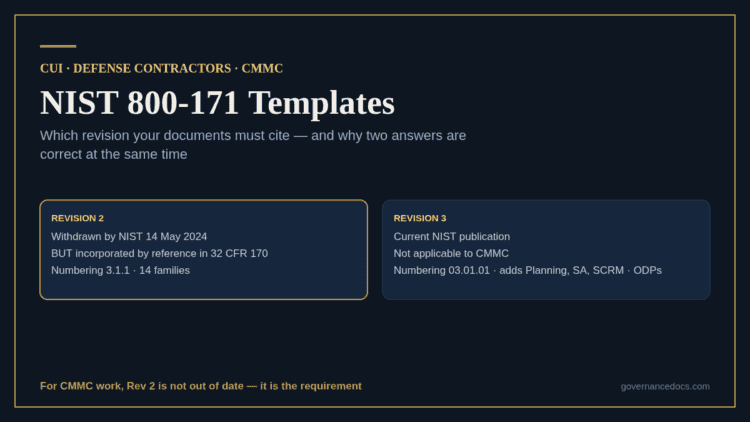
NIST 800-171 Templates: Complete Rev 2 Document Set Guide Governance Docs31st August 2026 NIST 800-171 templates must cite the right revision. Why CMMC still requires Rev 2 though NIST withdrew it,… Read More