About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesGap AssessmentsBusiness Impact AnalysisAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Tag: Topic: Information Security

Derived from the related-toolkit resolver (WPCode 12925). Used to scope MailPoet post-notification digests. Archives noindexed.

OT Patch Management process diagram for governance and security.

OT Patch Management: The Complete 2026 Guide for IEC 62443

Governance Docs26th August 2026

OT patch management under IEC 62443: verify authenticity, test for compatibility, set urgency from real exposure, and record…
Read More
Diagram of The Purdue Model in 2026 for industrial cybersecurity.

The Purdue Model in 2026: A Complete OT Security Guide

Governance Docs26th August 2026

The Purdue model explained for OT security: all 7 levels, why a level is not a zone, 7…
Read More
IEC 62443 certification badge for governance and cybersecurity standards.

IEC 62443 Certification: The Complete 2026 Guide

Governance Docs26th August 2026

IEC 62443 certification explained: what is certified by role, how assessment requirements are selected, and what 4 things…
Read More
IEC 62443 maturity levels chart for cybersecurity standards.

IEC 62443 Maturity Levels: The Complete 2026 Guide

Governance Docs26th August 2026

IEC 62443 maturity levels explained: ML 1 to ML 4, why clause 4.2 makes documentation the substance of…
Read More
Illustration of IEC 62443 parts and roles for cybersecurity governance.

IEC 62443 Parts Explained: The Complete 2026 Guide

Governance Docs26th August 2026

Which IEC 62443 parts do you actually need? 2-1, 3-2, 3-3, 4-1, 4-2 and 2-4 sorted by role,…
Read More
Comparison of IEC 62443 and ISO 27001 cybersecurity standards.

IEC 62443 vs ISO 27001: The Complete 2026 Comparison

Governance Docs26th August 2026

IEC 62443 vs ISO 27001 compared: what Edition 2.0 changed in 2024, which requirements your ISMS already covers,…
Read More
IEC 62443 security levels diagram for industrial automation.

IEC 62443 Security Levels: The Complete 2026 Guide

Governance Docs26th August 2026

IEC 62443 security levels explained: SL-T vs SL-C vs SL-A, how to assign a target level from risk,…
Read More
IEC 62443 Zones and Conduits diagram for cybersecurity.

IEC 62443 Zones and Conduits: The Complete 2026 Guide

Governance Docs26th August 2026

How to define IEC 62443 zones and conduits: the 8-step sequence, the 3 mandatory separations, and 8 questions…
Read More
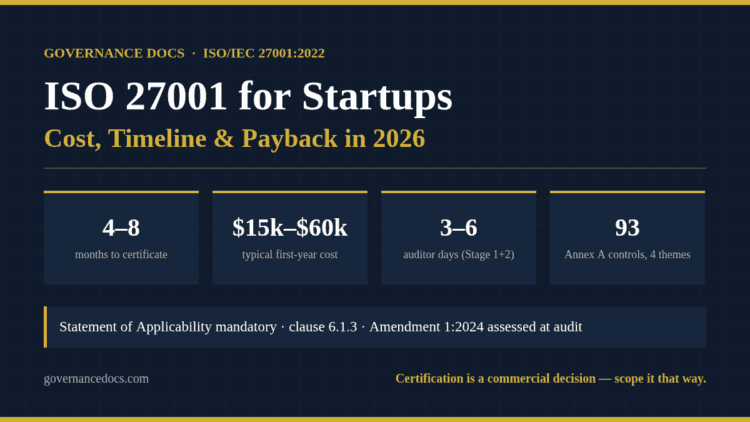
ISO 27001 for startups: 2026 cost, timeline and Annex A control summary

ISO 27001 for Startups: The Complete 2026 Guide to Cost, Timeline and Payback

Governance Docs26th August 2026

What ISO 27001 certification really costs a startup in 2026, how long it takes, the documents you must…
Read More
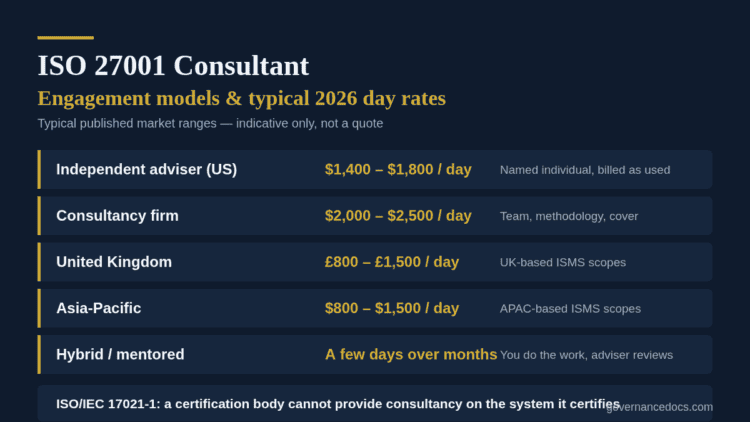
ISO 27001 consultant engagement models and typical 2026 day rates

ISO 27001 Consultant Costs in 2026: The Complete Decision Guide

Governance Docs25th August 2026

What an ISO 27001 consultant does, what day rates look like in 2026, the impartiality rule that stops…
Read More
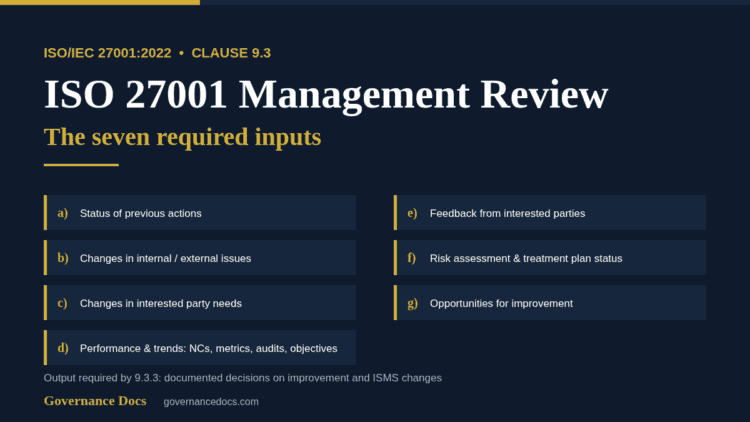
ISO 27001 management review inputs required by clause 9.3.2, listed a to g

ISO 27001 Management Review: The Complete 2026 Guide

Governance Docs24th August 2026

What ISO 27001 clause 9.3 requires: the seven management review inputs, how often to meet, what to minute,…
Read More
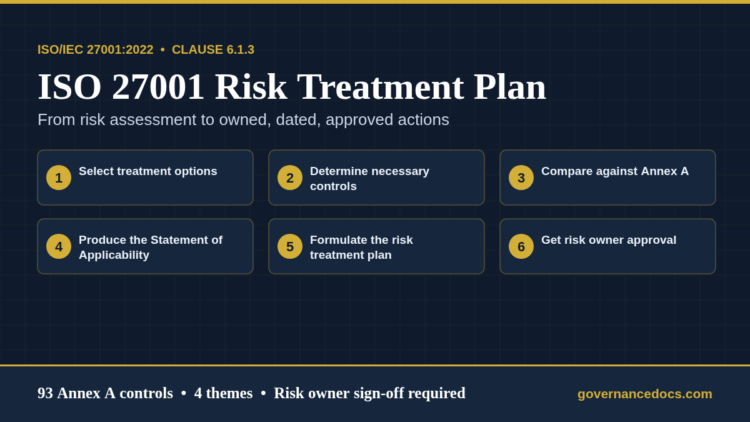
ISO 27001 risk treatment plan diagram showing the six steps of clause 6.1.3

ISO 27001 Risk Treatment Plan: The Complete 2026 Guide

Governance Docs23rd August 2026

An ISO 27001 risk treatment plan is required by clause 6.1.3. Here are the fields it needs, the…
Read More

    ←
  • 1
  • …
  • 10
  • 11
  • 12
  • 13
  • 14
  • …
  • 19
  • →

Recent Posts

Business Impact Analysis questionnaire with 30 essential questions for governance and risk.
Business Impact Analysis Questionnaire: 30 Essential Questions (2026)

September 26, 2026

Comparison of BIA and Risk Assessment for governance and business continuity planning.
BIA vs Risk Assessment: The Definitive 2026 Comparison

September 25, 2026

Business Impact Analysis example from Governance Docs website.
Business Impact Analysis Example: A Complete Worked BIA (2026)

September 25, 2026

Infographic answering is ISO 13485 worth it in 2026 with audit days, QMSR date and MDSAP regulators
Is ISO 13485 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Is ISO 42001 worth it in 2026 — audit days, first-year cost and Annex A controls at a glance
Is ISO 42001 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Gap assessments
  • Business impact analysis
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA