An ISO 42001 checklist covering both halves: the 7 mandatory clauses and the 38 Annex A controls, plus the Statement of Applicability mistake to avoid.
Annex SL is the harmonized structure behind ISO 9001, 14001, 27001 and 45001. The 10 clauses explained, the 2021 rename, and which standards are not on it.
NERC CIP vs IEC 62443 compared: mandatory versus voluntary, impact ratings versus zones and conduits, and how to run both without two disconnected programmes.
ISO 27018 applies in one narrow case: public cloud, personal data, acting as processor. The 6 obligations that carry commercial weight, and why no certificate.
The ISO 22301 risk assessment is the half of clause 8.2 that gets skipped. What it covers, how it differs from the BIA, and how it drives continuity strategy.
Risk criteria under ISO 31000: the 6 decisions to make before assessing anything, how they differ from risk appetite, and how to write a scale people can apply.
The ISO 27701 controls now sit in one Annex A with 3 tables - controller, processor and shared security controls. What each covers and how to map them.
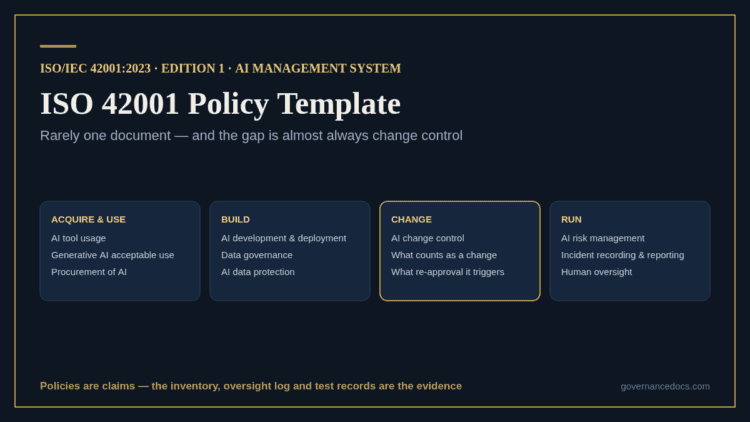
An ISO 42001 policy template is rarely one document. The 7 policies an AI management system needs, the change-control gap, and the registers behind them.