GovRAMP continuous monitoring is the set of reporting, remediation and assessment duties that start the day a cloud provider earns a verified status, and it is where many first-time providers stumble. Getting verified is a project. Staying verified is an operating routine, with monthly or quarterly uploads, fixed remediation windows and an escalation ladder that can end in suspension.
This guide summarises what the programme’s own guide requires, what to submit and when, how vulnerabilities and changes are handled, and how escalation works. GovRAMP was previously known as StateRAMP, as explained in our note on StateRAMP becoming GovRAMP. Confirm current details in the programme’s documents, since they are updated.
Free gap assessment
Are you working to the 2026 FedRAMP rules or the old ones?
Score the Key Security Indicators and the CR26 obligations, free, including the Security Decision Record that replaced the SSP.
According to the programme’s Continuous Monitoring Guide and Escalation Process, continuous monitoring begins once a service achieves a verified status. The FAQ summarises the obligations as submitting monthly and quarterly security reports to the programme management office, conducting annual assessments with an approved third-party assessment organisation, and remediating plan of action and milestones items within set timelines. Our guide to the GovRAMP status levels explains the statuses that these duties attach to.
Duty
What the guide describes
Reporting cadence
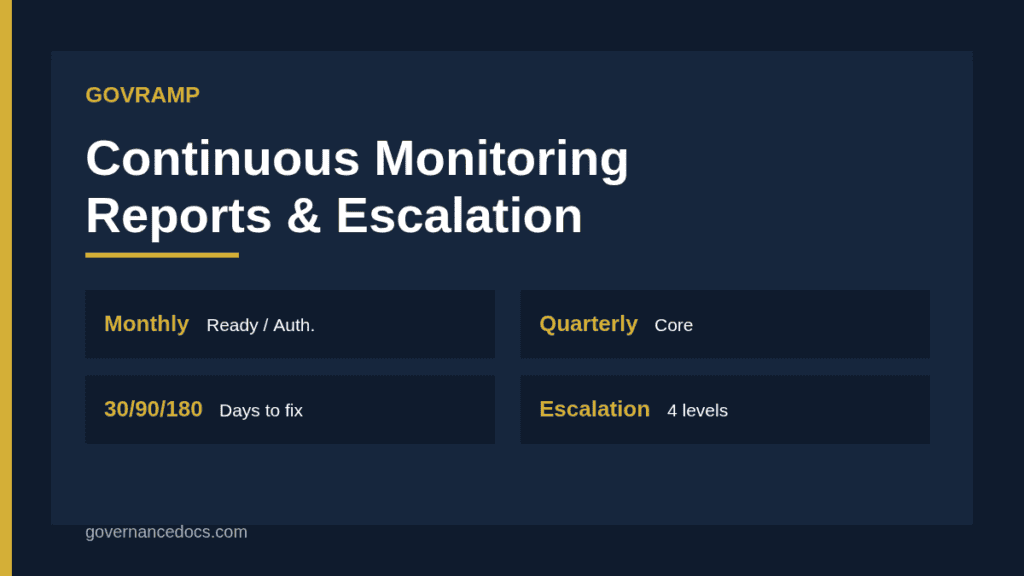
Quarterly for Core status, and monthly for Ready, Provisionally Authorized or Authorized status
Annual assessment
Third-party assessment of roughly one third of controls each year, with a full review over three years
Penetration testing
Annually for Provisionally Authorized and Authorized status
Significant change
Notify at least 30 days before, or within 5 days for emergency changes
Incidents
Report under the programme’s incident communications procedure
Some secondary sources describe the cadence differently, so use the guide for the version that applies to your status and check it at least once a year.
What to upload each cycle
For providers with a Low or Moderate categorisation, the guide lists the items to upload with each monthly or quarterly submission.
Plans of action and milestones. The current POA&M, with overdue items explained and remediation evidence.
Inventory workbook. An updated list of system components.
Vulnerability scans. Operating system, database and web application scans.
Adjustments. Documentation for risk adjustments, operational requirements and false positives.
Executive summary. A short report of the month’s or quarter’s position.
Treat the submission as a routine with an owner, a checklist and a date a week before the deadline. Late or incomplete packages are among the automatic triggers for escalation. Our comparison in GovRAMP vs FedRAMP and the guide to FedRAMP continuous monitoring show how the two programmes’ routines differ.
Remediation timelines under GovRAMP continuous monitoring
Discovered vulnerabilities must be fixed inside fixed windows by risk level: a maximum of 30 days for high risk, 90 days for moderate and 180 days for low. The POA&M must account for any item that runs past its window, with evidence of the remediation effort. Escalation begins when high-impact vulnerabilities stay open beyond 30 to 60 days or moderate ones beyond 90 to 180 days, according to the guide.
Build your patching process backwards from these windows. Run scans on a schedule that leaves enough time, triage results within days, assign owners and track exceptions with documented risk adjustments. If a fix depends on a vendor, record the vendor’s timeline and your compensating controls, so that the item is evidence of management and not neglect.
Annual activities
Each year, providers review and update security policies and procedures, undergo an assessment by an approved assessor covering about a third of the controls, carry out annual vulnerability and compliance scans, update plans such as configuration management, contingency and supply chain risk management, and test the incident response plan. Providers with the higher statuses also undergo penetration testing. Plan the year around this cycle: schedule the assessor early, and prepare evidence during the year and not in the final month. The GovRAMP cost guide covers how these recurring activities affect budget.
Significant changes and incidents
Significant changes, such as new components, changed architecture or new subservice providers, require notification to the programme at least 30 days before implementation, and emergency changes need notice within 5 days afterwards. Failing to notify counts as a deficiency. Build the notice into your change management process with a flag for changes that meet the significance criteria, and keep the request form and approvals with the change record. Incidents follow the programme’s incident communications procedure, and late notification or recurring types of incident can lead to a corrective action plan.
The escalation ladder
The guide describes four levels of escalation. Understanding them helps you judge how serious a deficiency is.
Detailed finding review. The initial response to minor deficiencies, where you address the issue within an agreed timeframe.
Corrective action plan. A request from the programme director for a root-cause analysis and a formal remediation plan. Failure to resolve the matter within the agreed time can lead to suspension or revocation.
Suspension. Temporary removal of status until deficiencies are resolved, with notice to sponsoring bodies for authorised and provisionally authorised products.
Revocation. Permanent removal from the authorised product list, with resubmission and assessor attestation needed to regain status.
The guide lists automatic triggers. They include a 20 percent rise in vulnerabilities from baseline, or ten or more, overdue high-impact vulnerabilities, annual assessment packages that arrive more than 30 days late, missing emergency change notices and unpaid obligations. Track these as internal indicators so you can act before the programme does.
A hypothetical example of GovRAMP continuous monitoring
A software provider holds a Moderate authorised status. Its compliance analyst compiles the monthly package on the 20th of each month, following a checklist: POA&M, inventory, scans, adjustments and summary. In one month, a scan finds a high-risk vulnerability in a web framework. The engineering team patches within three weeks and records the evidence. In the same quarter, the company plans a migration to a new database service. The change manager identifies it as significant, submits the request 45 days ahead and attaches the architecture change. The annual assessment is booked six months in advance and covers the controls scheduled for that year. No escalations occur. The example is illustrative only.
Common mistakes with GovRAMP continuous monitoring
Last-minute packages. Uploads are assembled on the due date, and errors follow.
Scans too late. Findings appear after the remediation window has begun to close.
Unlogged changes. Significant changes are made without notice.
Weak POA&M evidence. Overdue items lack proof of effort.
Assessor booked late. The annual assessment is squeezed into a short window.
Ignoring triggers. The vulnerability trend is not monitored against the escalation thresholds.
Roles and tooling for GovRAMP continuous monitoring
GovRAMP continuous monitoring runs best when one named person owns the monthly or quarterly cycle and a second person can cover for them. Typical roles are a security lead who signs the deliverables, an infrastructure owner who supplies scan results and inventory, and a compliance coordinator who tracks the plan of action and milestones. Write these roles into your procedure so the cycle does not depend on one individual’s calendar.
Tooling matters less than consistency. Whatever scanner, ticketing system and evidence store you use, GovRAMP continuous monitoring needs the same output each period: a current inventory, scan results that match it, and a remediation tracker that shows opening and closing dates. Automate the exports where you can, and keep a short checklist so a new team member can produce the package without guesswork.
Planning the annual assessment around GovRAMP continuous monitoring
The annual assessment by a third-party assessor should not be a surprise. Build a calendar at the start of the year that shows which controls are due for testing, when sample evidence will be collected and when the assessor needs access. Because GovRAMP continuous monitoring already produces regular evidence, many of the artifacts an assessor asks for should exist before the engagement begins. Gaps usually appear where evidence was collected informally, so store it in one place with dates.
Budget for the assessment and for remediation of its findings together. A finding raised in the assessment enters the same remediation clock as any other, so leave time in the schedule to fix issues rather than discover them close to a deadline. Confirm the current assessment scope and timing rules against the official guide before you fix your plan.
Templates and next steps
A practical set of documents includes a continuous monitoring procedure, a monthly package checklist, a POA&M tracker, a significant change form, an incident communications procedure and an annual activity calendar. The StateRAMP and GovRAMP Toolkit includes templates for these, which you can adapt to your service. The primary source is the programme’s Continuous Monitoring Guide and Escalation Process. If you sell in Texas, see also our guide to TX-RAMP certification.
GovRAMP continuous monitoring FAQ
How often do I submit continuous monitoring reports?
According to the programme’s guide, quarterly for Core status and monthly for Ready, Provisionally Authorized and Authorized statuses.
How fast must vulnerabilities be fixed?
Within 30 days for high risk, 90 days for moderate and 180 days for low, with overdue items accounted for in the POA&M.
Do I need to tell GovRAMP about changes?
Yes. Significant changes need at least 30 days’ notice, and emergency changes need notice within 5 days of implementation.
What happens if I fall behind?
The programme escalates through a detailed finding review, a corrective action plan, suspension and, ultimately, revocation of status.