About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Category: Articles

HACCP: 7 Must-Have Principles for Best Food Safety Practices.

HACCP: The 7 Principles of Food Safety

Governance Docs22nd May 2026

Mastering the 7 must-have HACCP principles is key to ensuring food safety from farm to table, helping prevent…
Read More
NIS2 directive explained - scope, security requirements, incident reporting and penalties

NIS2 Directive Explained: A Complete Compliance Guide

Governance Docs20th May 2026

The NIS2 Directive is the EU's most far-reaching cybersecurity law. A complete guide to its scope, security requirements,…
Read More
Data Protection Strategy: Must-Have Tips for Scalable Success.

Building a Scalable Data Protection Strategy

Governance Docs18th May 2026

Building a strong data protection strategy is essential for businesses aiming to safeguard sensitive information while growing confidently.…
Read More
NIST Framework: Must-Have Guide for Best Cybersecurity Investments.

NIST Cybersecurity Framework: A Guide to Getting Started

Governance Docs16th May 2026

The NIST cybersecurity framework is your go-to roadmap for making smart, effective cybersecurity investments that protect your business…
Read More
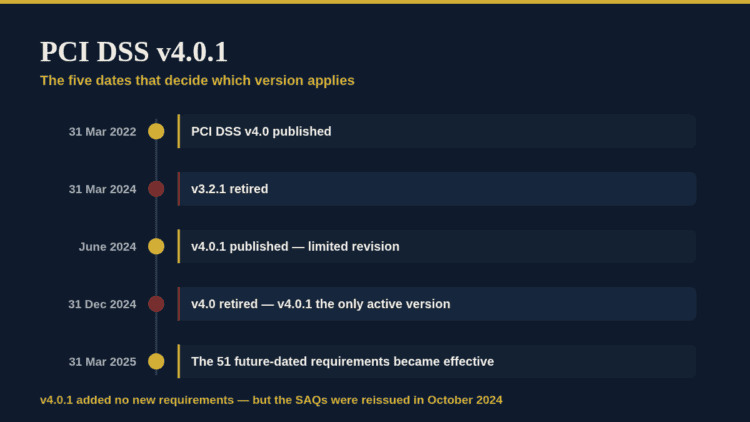
Timeline of PCI DSS v4.0.1 release and updates for governance and security.

PCI DSS v4.0.1: A Clear Guide to the 2026 Version

Governance Docs14th May 2026

PCI DSS v4.0.1 is the only active version since v4.0 retired. The 5 dates that matter, what the…
Read More
ISO 20000: Must-Have Guide for Affordable IT-Business Alignment.

ISO 20000: Aligning IT Service Management with the Business

Governance Docs12th May 2026

Discover how ISO 20000 alignment can transform your IT services into a powerful driver of business success—affordably and…
Read More
ISO 14001: Exclusive Guide to Effortless Environmental Compliance.

ISO 14001: A Guide to Environmental Management

Governance Docs10th May 2026

Discover how ISO 14001 compliance can simplify your journey to sustainable business practices, helping you meet environmental regulations…
Read More
ISO 45001: Must-Have Guide for Best Workplace Safety Practices.

ISO 45001: A Guide to Occupational Health & Safety

Governance Docs08th May 2026

Discover how ISO 45001 workplace safety standards can transform your organization by creating a proactive, safer work environment…
Read More
ISO 9001 explained - the quality management system, seven principles and clause structure

ISO 9001 Explained: The Complete Quality Management Guide

Governance Docs06th May 2026

ISO 9001 is the world's most-used quality management standard. A complete guide to the QMS, the seven principles,…
Read More
ISO 22301: Must-Have Guide for Building Strong Organizational Resilience.

ISO 22301: A Guide to Business Continuity Management

Governance Docs04th May 2026

Discover how ISO 22301 organizational resilience can transform your business by helping you proactively manage risks and ensure…
Read More
Unified Management System: The Ultimate Guide to Quality & Safety.

Unified Management Systems: Aligning Quality & Safety

Governance Docs02nd May 2026

A Unified Management System brings all your quality and safety processes together under one roof, making it easier…
Read More
Structured Project Management: Must-Have Tips for Best Risk Reduction.

Structured Project Management: Reducing Delivery Risk

Governance Docs30th April 2026

Discover how structured project management can transform your approach to handling risks by providing a clear, methodical framework…
Read More

    ←
  • 1
  • …
  • 96
  • 97
  • 98
  • 99
  • →

Recent Posts

ISO 27001 configuration management requirements under Annex A 8.9 - established, documented, implemented, monitored, reviewed
ISO 27001 Configuration Management: Complete 2026 Guide

October 11, 2026

internal audit findings rating scale — Internal Audit Findings Rating Scale: Examples and Template
Internal Audit Findings Rating Scale: Examples and Template

October 11, 2026

third party topical requirement — Third Party Topical Requirement: The 2026 Audit Guide
Third Party Topical Requirement: The 2026 Audit Guide

October 11, 2026

cybersecurity topical requirement — Cybersecurity Topical Requirement: How to Audit It in 2026
Cybersecurity Topical Requirement: How to Audit It in 2026

October 11, 2026

quality assurance and improvement program — Quality Assurance and Improvement Program (QAIP): 2026 Guide
Quality Assurance and Improvement Program (QAIP): 2026 Guide

October 11, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA