About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesGap AssessmentsBusiness Impact AnalysisAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Author: Governance Docs

Governance Docs LLC

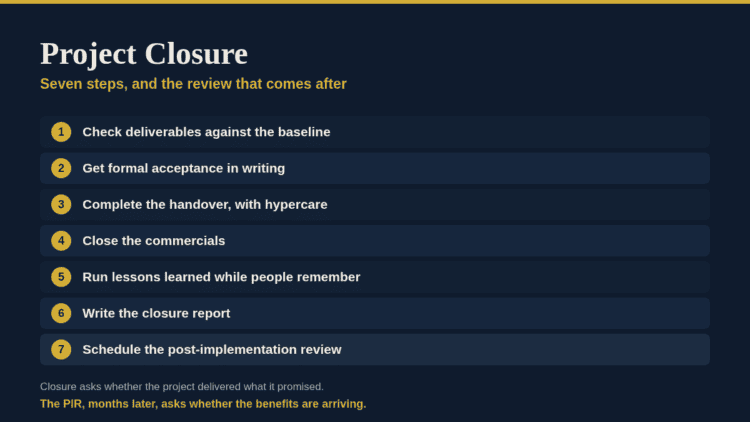
Step-by-step project closure process from Governance Docs website.

Project Closure: A Clear Guide to 7 Essential Steps

Governance Docs30th August 2026

Project closure in 7 steps: confirming delivery, formal acceptance, handover and hypercare, commercial closure, lessons learned and booking…
Read More
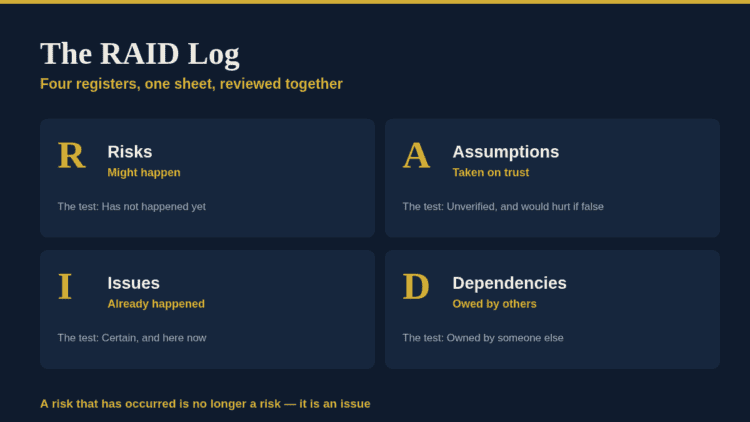
RAID Log for governance with risks, issues, assumptions, dependencies.

RAID Log: A Clear Guide to All 4 Elements

Governance Docs30th August 2026

A RAID log covers risks, assumptions, issues and dependencies in one sheet. What each means, how to score…
Read More
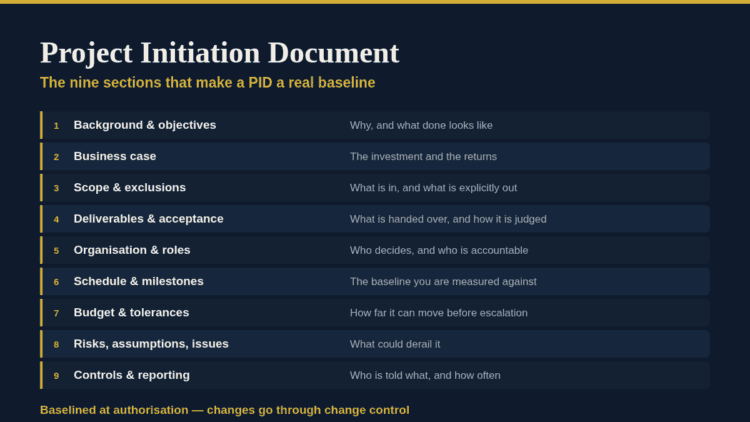
Governance Docs project initiation document with nine key sections for governance planning.

Project Initiation Document: A Clear PID Guide for 2026

Governance Docs30th August 2026

What goes in a project initiation document, how the PID differs from a project charter and business case,…
Read More
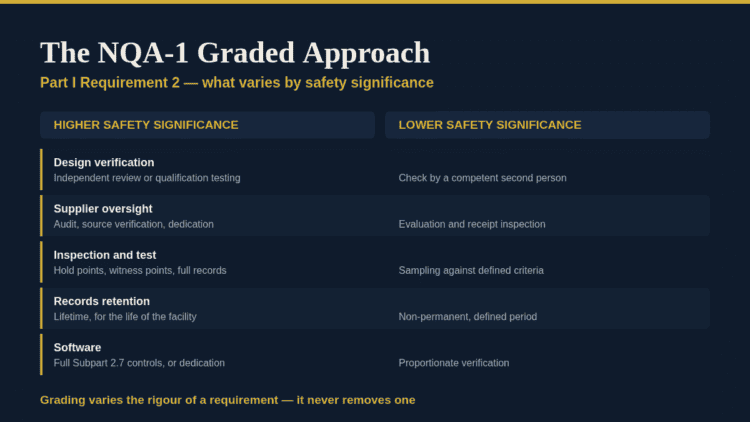
Diagram illustrating the NQA-1 graded approach for safety standards.

NQA-1 Graded Approach: A Clear Guide to Quality Levels in 2026

Governance Docs30th August 2026

The NQA-1 graded approach sits in Part I Requirement 2: defining quality levels, what varies by level, and…
Read More
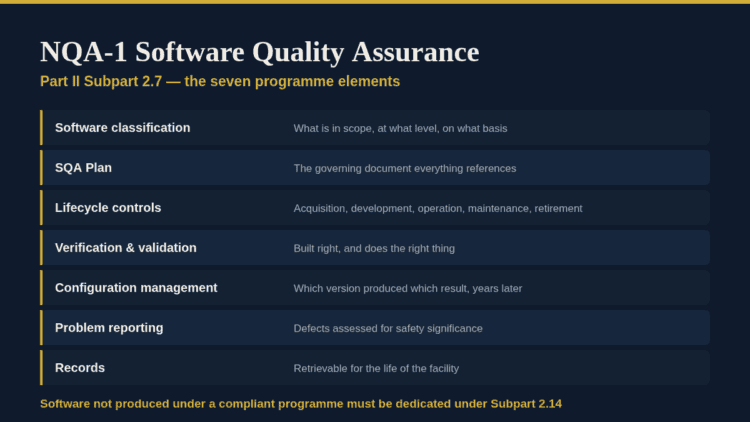
Governance Docs software quality assurance process overview.

NQA-1 Software Quality Assurance: A Clear Subpart 2.7 Guide

Governance Docs30th August 2026

NQA-1 software quality assurance under Subpart 2.7: what counts as software, the 7 programme elements, and why bought…
Read More
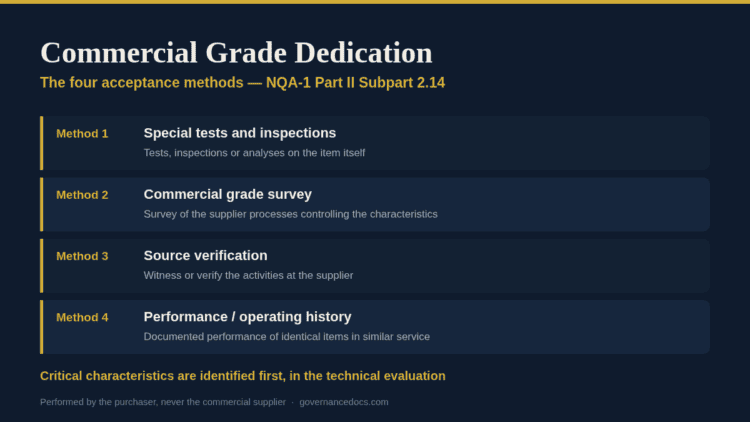
Detailed chart of commercial grade dedication methods for governance.

Commercial Grade Dedication: A Clear Guide to 4 Methods

Governance Docs30th August 2026

Commercial grade dedication under NQA-1 Subpart 2.14: the 4 acceptance methods, identifying critical characteristics, and the 5 findings…
Read More
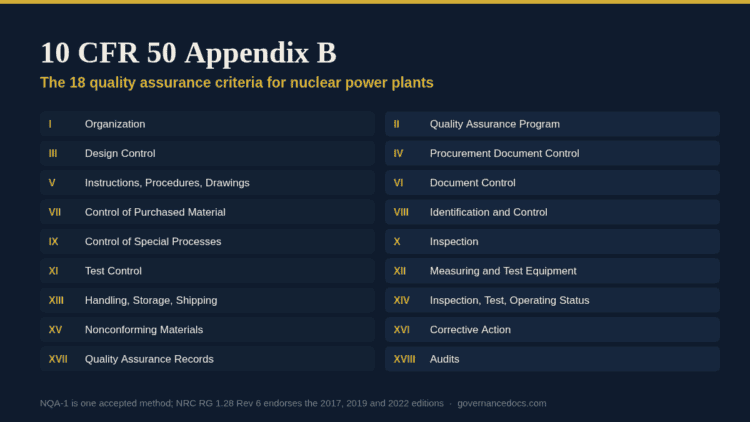
Diagram of 10 CFR 50 Appendix B quality assurance criteria for nuclear plants.

10 CFR 50 Appendix B: A Clear Guide to the 18 Criteria

Governance Docs30th August 2026

10 CFR 50 Appendix B sets 18 QA criteria for nuclear facilities. How NQA-1 satisfies them, which editions…
Read More
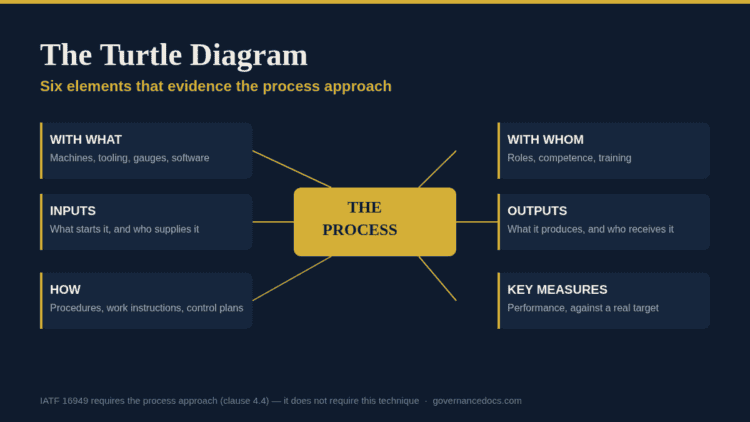
Visual of The Turtle Diagram illustrating governance process elements and relationships.

Turtle Diagram: A Clear Guide to All 6 Elements

Governance Docs30th August 2026

A turtle diagram has 6 elements and is not required by IATF 16949 - the process approach is.…
Read More
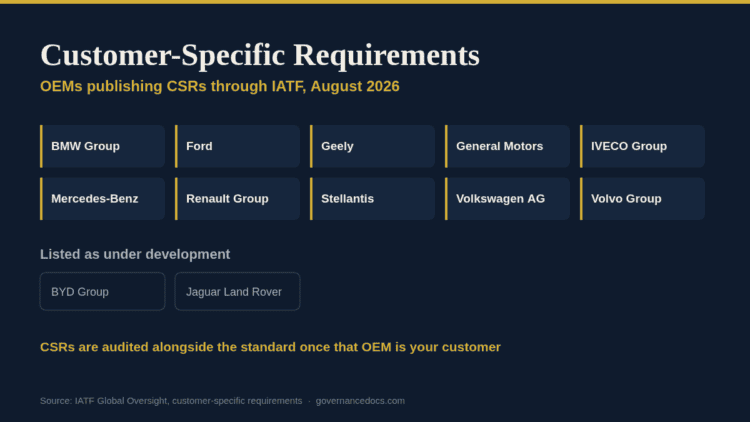
Customer-specific requirements document for OEMs from Governance Docs.

Customer-Specific Requirements: A Clear Guide for 10 OEMs

Governance Docs30th August 2026

10 OEMs publish customer-specific requirements via IATF. The matrix that makes CSRs auditable, handling conflicts, and what 2027…
Read More
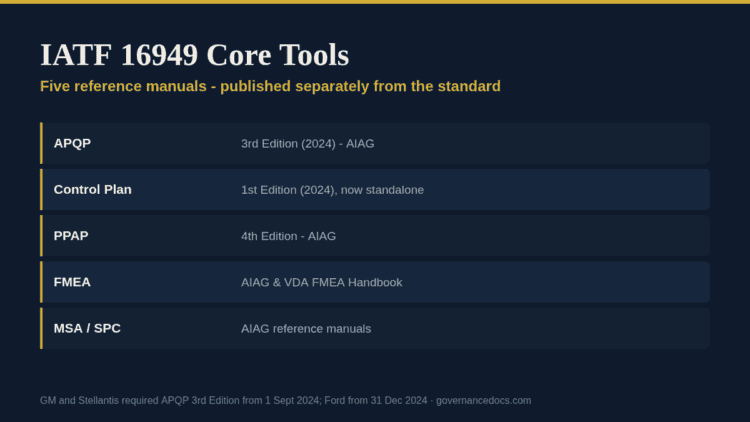
IATF 16949 core tools: the five AIAG reference manuals and their current editions

IATF 16949 Core Tools: A Clear Guide to All 5 Manuals

Governance Docs30th August 2026

The 5 IATF 16949 core tools explained: APQP, Control Plan, PPAP, FMEA, MSA and SPC - the 2024…
Read More
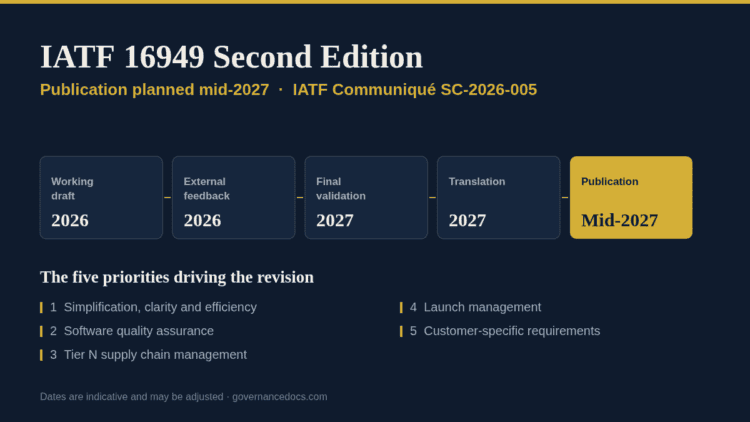
IATF 16949 second edition timeline to mid-2027 and the five revision priorities

IATF 16949 Second Edition: 5 Priorities and a Clear 2027 Timeline

Governance Docs30th August 2026

The IATF 16949 second edition is planned for mid-2027. The 5 priorities, the transition tied to ISO 9001,…
Read More
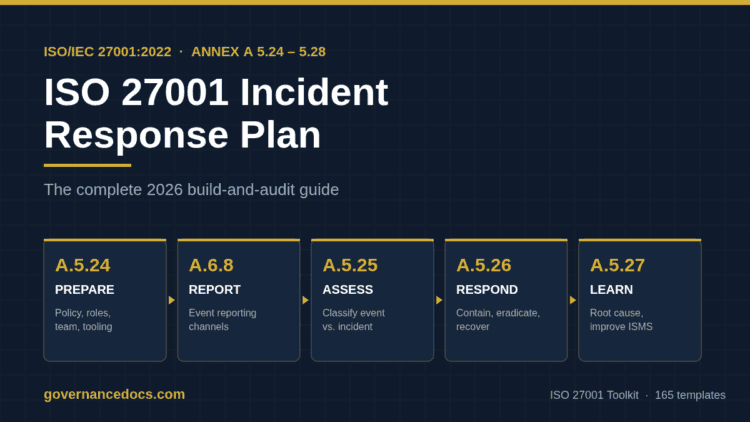
ISO 27001 incident response plan lifecycle across Annex A controls 5.24 to 5.27

ISO 27001 Incident Response Plan: The Complete 2026 Guide

Governance Docs30th August 2026

What an ISO 27001 incident response plan must contain, the Annex A 5.24 to 5.28 controls behind it,…
Read More

    ←
  • 1
  • …
  • 42
  • 43
  • 44
  • 45
  • 46
  • …
  • 68
  • →

Recent Posts

Infographic answering is ISO 13485 worth it in 2026 with audit days, QMSR date and MDSAP regulators
Is ISO 13485 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Is ISO 42001 worth it in 2026 — audit days, first-year cost and Annex A controls at a glance
Is ISO 42001 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Is SOC 2 worth it in 2026 — typical first-year cost, annual report cycle and attestation status
Is SOC 2 Worth It? The Complete 2026 Cost-Benefit Case

September 24, 2026

ISO 21502 vs PMBOK 8 comparison: the 2020 project management guidance against PMI six principles, five Focus Areas and seven Performance Domains
ISO 21502 vs PMBOK 8: The Complete 2026 Guide for Project Governance

September 24, 2026

ISO 31000 vs ISO 27005 comparison: 2018 risk management guidelines against the 2022 information security risk guidance
ISO 31000 vs ISO 27005: The Definitive 2026 Guide

September 24, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Gap assessments
  • Business impact analysis
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA