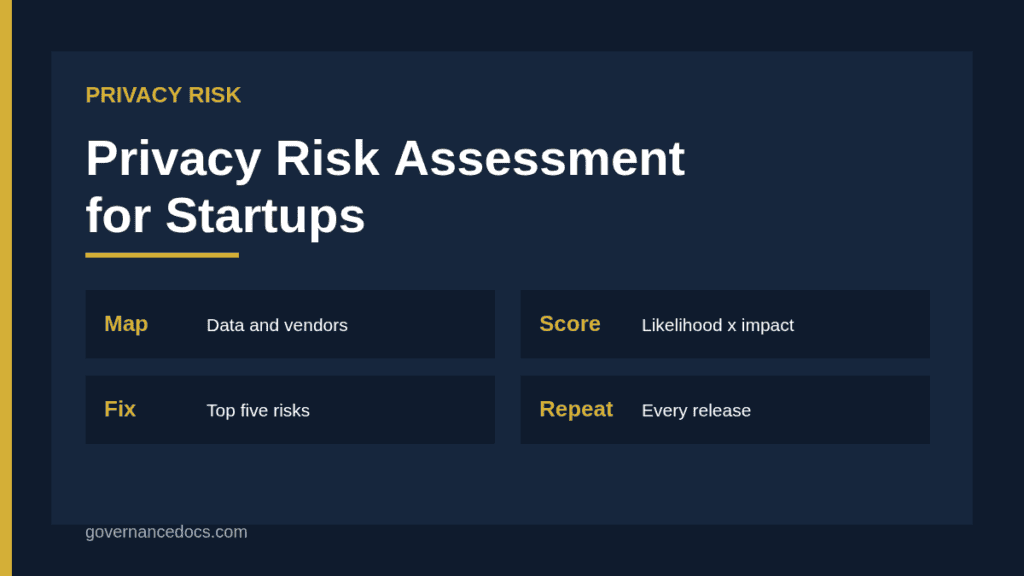
A privacy risk assessment for startups is a short, structured exercise that finds where your product collects or shares personal data in ways that could harm people, scores those risks, and assigns an owner to fix the worst ones. It is not a 60-page legal memo. For a team of five to fifty, it is usually a two-to-four-week piece of work that a founder and one technical lead can run.
Startups tend to delay it until a customer questionnaire or a security review forces the issue. That is the expensive moment to start, because you are rebuilding under deadline. Doing a lean assessment earlier costs less and gives you answers ready for procurement teams, investors and regulators.
This guide shows what to include, how to score, and what to skip. Every number in the examples is illustrative, so replace them with your own data.
Free gap assessment
Could you demonstrate GDPR compliance today?
Score yourself against what a supervisory authority actually asks for, free — the records, not the policy.
Why a privacy risk assessment for startups matters early
Early-stage products are built fast, and the data decisions made in the first year tend to stick. A login system, an analytics script and a customer support tool can quietly create a large personal data footprint before anyone writes a policy.
Three pressures make the assessment worth doing sooner. Enterprise buyers send security and privacy questionnaires that ask how you identify and treat privacy risks. Investors run diligence that checks for unresolved data exposure. Regulators, where GDPR applies, expect accountability under Article 24 and data protection by design under Article 25, regardless of company size.
The business case is simple: a short assessment now is cheaper than a retrofit later, and it gives your sales team a credible answer to the question every buyer asks.
Start with a data map, not a policy
You cannot assess what you have not listed. Begin with a one-page inventory of the personal data you handle: what you collect, why, where it is stored, who can access it, which vendors receive it and how long you keep it.
Keep it practical. Walk through the signup flow, the billing flow and the support flow, and write down each field and each system it touches. Include the obvious and the forgotten: server logs, backups, product analytics, error trackers, email tools and spreadsheets exported by the sales team.
Mark anything sensitive, such as health, children’s data, precise location, biometrics or financial details. These categories raise the impact score later and may trigger extra legal duties. The inventory feeds directly into the privacy risk assessment methodology you will follow in the next steps.
Free privacy risk assessment
Which privacy risks would hurt the people whose data you hold?
List your personal data and processing, pick from 38 privacy risk scenarios, rate them for the people concerned and for you, and plan treatment with ISO 27701 controls. You get a heat map, a process score and the findings an auditor would raise, free.
A privacy risk is not the same as a security risk. Security asks whether your systems can be breached. Privacy asks whether people could be harmed by how data is collected, used, shared or kept, even without a breach.
For each data flow, ask what could go wrong for the individual. They might be surprised by a secondary use, profiled unfairly, unable to delete their data, tracked without a real choice, or exposed when a vendor fails. A privacy harms taxonomy gives you a ready list of harm types so you do not rely on memory.
Write each risk as a plain sentence: cause, event, consequence. For example, “Because support staff have full database access, a curious employee could view customer messages, exposing private details.” Aim for 15 to 30 risks for a typical early product, not 200.
Score privacy risk for startups without false precision
Use a simple five-by-five matrix: likelihood from 1 to 5, impact from 1 to 5, multiplied into a score from 1 to 25. Define each level in one line so two people score the same risk the same way.
Impact should reflect harm to individuals first, then legal and commercial consequences. A risk that could expose health data scores higher than one that could reveal a newsletter preference, even if the breach probability is equal. See privacy risk scoring for worked scales you can copy.
Do not chase decimal precision. The point is to rank risks so the top five get attention. If two risks tie, prefer the one that affects more people or involves sensitive data.
Build a lean risk register and treatment plan
Put every scored risk into one table: ID, description, score, owner, chosen response, due date and status. This is your privacy risk register, and it is the single document buyers and auditors ask to see.
For each of the top risks, choose one response: reduce, avoid, transfer or accept. Most startup fixes are small engineering or process changes: restrict access by role, turn off unneeded analytics fields, add a deletion job, sign a data processing agreement, or shorten retention. Record them in your privacy risk treatment plan with an owner and a date.
Accepting a risk is legitimate, but it should be a named person making the decision with a reason written down, not silence.
When a DPIA is required in a startup
A data protection impact assessment is a more formal version of a privacy risk assessment, required under GDPR Article 35 where processing is likely to result in a high risk to individuals. Typical triggers include large-scale profiling, large-scale processing of sensitive data and systematic monitoring of public areas.
If your product uses automated scoring that affects people, processes health or biometric data at scale, or tracks behavior across services, plan for a full DPIA. The regulator-facing record needs to describe the processing, its necessity, the risks and the measures. You can read the legal text in GDPR Article 35 text.
Your lean assessment is not wasted in that case. It becomes the starting point, so the DPIA builds on the same inventory and register rather than starting cold.
Build privacy into the product cycle
The most efficient time to assess is before you ship. Add a short privacy check to your product requirements or pull request template: does this feature collect new data, share data with a new vendor, or change how long data is kept? If yes, flag it for review.
This is the practical meaning of privacy by design risk assessment. It turns the assessment from an annual project into a habit, and it keeps the register current without a separate exercise.
Pair it with a simple privacy review process: a named reviewer, a 48-hour response target and a record of the decision. Startups that do this rarely face painful rework at audit time.
A practical privacy risk assessment for startups timeline
A realistic schedule keeps the work from stalling. In week one, run the data map with one engineer and one product owner, and list every vendor that touches personal data. In week two, identify and score risks in a single working session, then challenge the top ten with a second person. In week three, agree treatment actions, assign owners and book the fixes into the normal sprint plan. Week four is for evidence: save screenshots, contract references and decisions so the privacy risk assessment for startups can be shown to a buyer without rework.
Budget for this honestly. The main cost is staff time, not software. A template-driven approach, such as the Privacy Risk Assessment Report, reduces drafting effort because the scales, register columns and report structure already exist, leaving your team to supply the facts.
Keep a short log of what you decided not to fix and why. That log is often the most persuasive part of a questionnaire answer, because it shows judgment rather than box-ticking.
What buyers ask about startup privacy risk
Enterprise questionnaires usually ask five things. Do you keep a data inventory? Do you assess privacy risk before launching new processing? Who owns privacy risk? How do you handle subprocessors? How quickly can you delete a customer’s data? A current register answers four of these directly, and the fifth is covered by your retention and deletion controls.
When you reply, link the answer to evidence rather than adjectives. Say that a privacy risk assessment for startups like yours was completed on a named date, that the register holds a stated number of open risks, and that the highest ones have owners and due dates. Buyers trust specifics, and a dated record is hard to fake.
Also be ready for the breach question. Under GDPR Article 33, a controller must notify the supervisory authority within 72 hours of becoming aware of a reportable personal data breach, so your response plan should name who decides and who calls the regulator.
Keeping startup privacy risk current after launch
After the first assessment, the goal is to stay light. Add a column to your roadmap for new data, new vendors and new purposes. Reopen the register when any of them appear, rescore only the affected rows, and record the change. Monitor a small set of indicators, such as open high risks, overdue actions and deletion requests closed on time, using the approach in privacy risk monitoring.
Finally, set a risk appetite so the team knows what needs escalation. A one-line rule, such as no open risk above 15 without founder approval, is enough, and privacy risk appetite shows how larger firms formalize it. Treat privacy risk assessment for startups as a living habit rather than a document.
Common mistakes in a privacy risk assessment for startups
The first mistake is copying a large-company template and filling it with generic answers. The result looks thorough but does not reflect your actual data flows, and a buyer will spot that within minutes.
The second is treating the assessment as a one-time document. Product changes, new vendors and new markets all change the risk picture, so set a review trigger rather than relying on the calendar alone.
The third is skipping vendors. Many startup privacy incidents begin at a processor, so check each vendor contract, location and security posture. Finally, avoid a register with no owners. A risk nobody owns will not be fixed.
Privacy risk assessment for startups FAQ
Do startups need a privacy risk assessment?
If you process personal data of people in the EU or UK, accountability duties apply regardless of size, and buyers will expect evidence. A lean assessment is the practical way to show it.
How long does it take?
For a small product, two to four weeks of part-time effort is typical. The data map takes the most time; scoring and planning are quicker once it exists.
Is a privacy risk assessment the same as a DPIA?
No. A DPIA is a formal assessment required in high-risk cases under GDPR Article 35. A lean assessment is broader and lighter, and it feeds into a DPIA when one is needed.
Who should own it?
A founder or product lead should own it, with engineering input. Legal counsel can review the output, but the people who build the product know the data flows.
How often should we update it?
Review it whenever you launch a major feature, add a significant vendor or enter a new market, and at least once a year as a fallback.