About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesSample ReportsFind the Right AssessmentRecords of Processing (ROPA)Data Privacy Impact AssessmentLegitimate Interests AssessmentTransfer Impact AssessmentPrivacy Risk AssessmentGDPR Gap AssessmentUK GDPR Gap AssessmentCCPA/CPRA Gap AssessmentISO 27701 Gap AssessmentHIPAA Gap AssessmentISO 27001 Risk AssessmentThird-Party Risk AssessmentSoA GeneratorISO 27001 Assessment Tool (Excel)ISO 27001 Gap AssessmentSOC 2 Gap AssessmentNIST CSF 2.0 Gap AssessmentNIST SP 800-53 Gap AssessmentNIST RMF Gap AssessmentCIS Controls Gap AssessmentPCI DSS 4.0 Gap AssessmentNIS2 Gap AssessmentCMMC 2.0 Gap AssessmentNIST SP 800-171 Gap AssessmentFedRAMP Gap AssessmentBSI C5 Gap AssessmentIEC 62443 Gap AssessmentSAMA CSF Gap AssessmentNCA ECC Gap AssessmentISO 20000 Gap AssessmentAI Risk AssessmentAI Impact AssessmentISO 42001 Gap AssessmentEU AI Act Gap AssessmentBusiness Impact AnalysisContinuity Risk AssessmentISO 22301 Assessment Tool (Excel)ISO 22301 Gap AssessmentDORA Gap AssessmentISO 9001 Gap AssessmentISO 13485 Gap AssessmentIATF 16949 Gap AssessmentISO 14001 Gap AssessmentISO 45001 Gap AssessmentISO 45001 Assessment Tool (Excel)HACCP Gap AssessmentEnterprise Risk AssessmentISO 31000 Gap AssessmentData Governance Gap AssessmentProject Management Gap AssessmentAll Gap AssessmentsISO 27001 Internal AuditISO 42001 Internal AuditAboutBlogContactMy AccountCart
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Day: October 1, 2026

Cyber Resilience Act open source infographic

Cyber Resilience Act Open Source: The Essential 2026 Guide to Stewards and Manufacturers

Governance Docs01st October 2026

How the Cyber Resilience Act treats open source: when software is in scope, steward obligations, manufacturer duties and…
Read More
AS9100 internal audit checklist infographic

AS9100 Internal Audit Checklist: The Essential 2026 Guide for Aerospace Suppliers

Governance Docs01st October 2026

Use this AS9100 internal audit checklist to test your aerospace QMS: process approach, performance, product safety, configuration and…
Read More
BSI C5:2026 transition infographic

BSI C5:2026 Transition: The Essential Guide for Cloud Service Providers

Governance Docs01st October 2026

Plan your BSI C5:2026 transition: what changed from C5:2020, new criteria types, reported deadlines and an attestation roadmap.
Read More
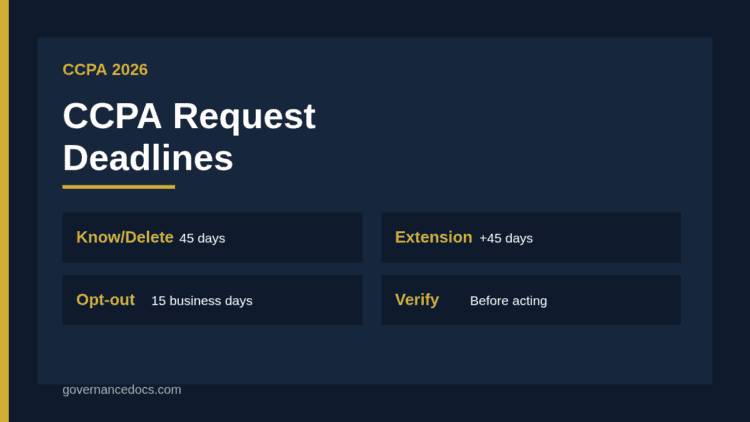
CCPA consumer request deadlines infographic

CCPA Consumer Request Deadlines: The Essential 2026 Response Guide

Governance Docs01st October 2026

CCPA consumer request deadlines: response times for know, delete, correct and opt-out requests, plus a workflow and evidence…
Read More
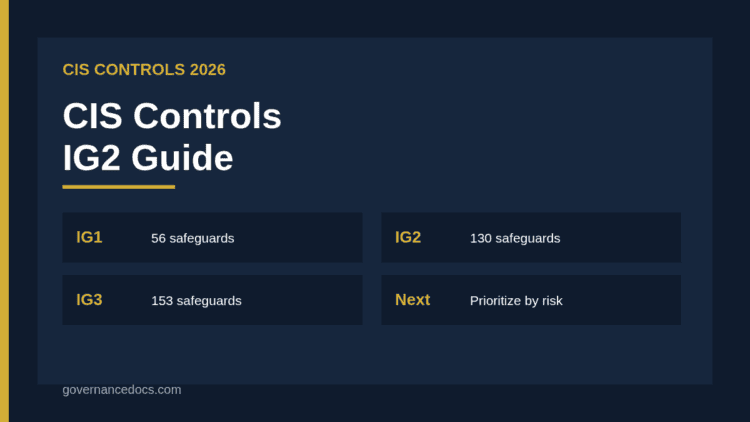
CIS Controls IG2 infographic

CIS Controls IG2: The Essential 2026 Guide to Moving Beyond IG1

Governance Docs01st October 2026

CIS Controls IG2 guide: which organizations need Implementation Group 2, what it adds beyond IG1, and how to…
Read More
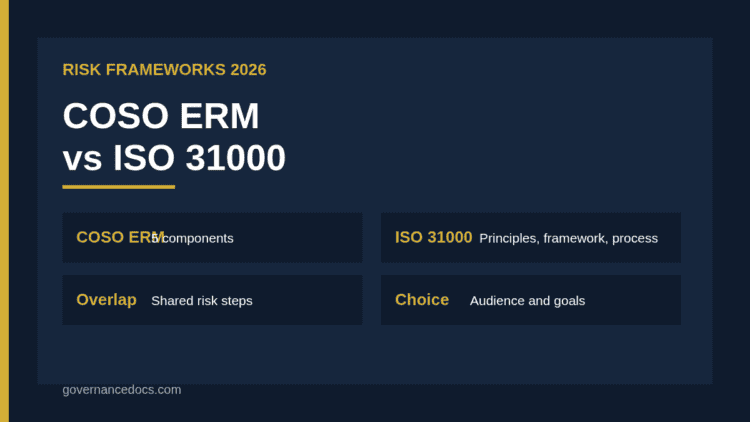
COSO ERM vs ISO 31000 comparison infographic

COSO ERM vs ISO 31000: The Essential 2026 Guide to Choosing a Risk Framework

Governance Docs01st October 2026

COSO ERM vs ISO 31000 compared side by side: components, principles, process, use cases and how to combine…
Read More
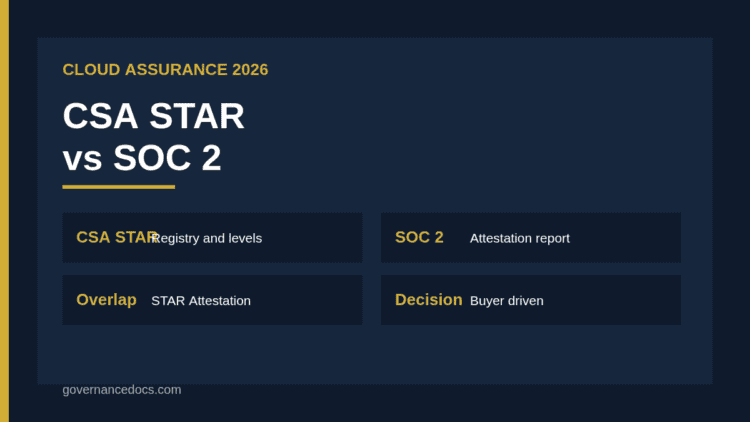
CSA STAR vs SOC 2 comparison infographic

CSA STAR vs SOC 2: The Essential 2026 Guide for Cloud Providers

Governance Docs01st October 2026

CSA STAR vs SOC 2 for cloud providers: how they relate, where they differ, and how to choose…
Read More
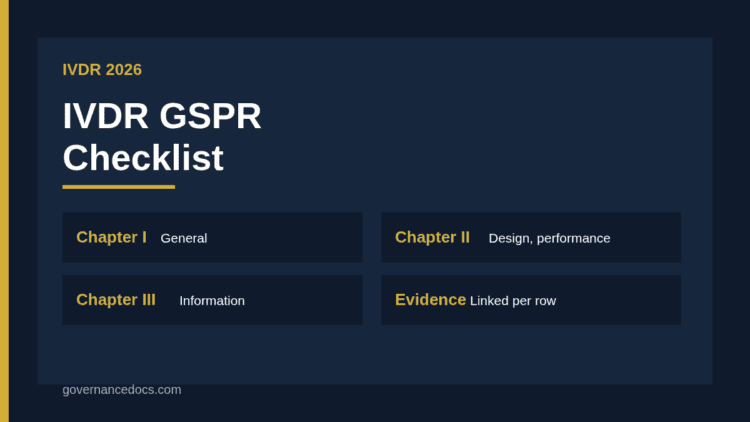
IVDR GSPR checklist infographic

IVDR GSPR Checklist: The Essential 2026 Guide to Annex I Compliance

Governance Docs01st October 2026

Build an IVDR GSPR checklist for Annex I: structure, applicability, evidence links and common mistakes for IVD manufacturers.
Read More
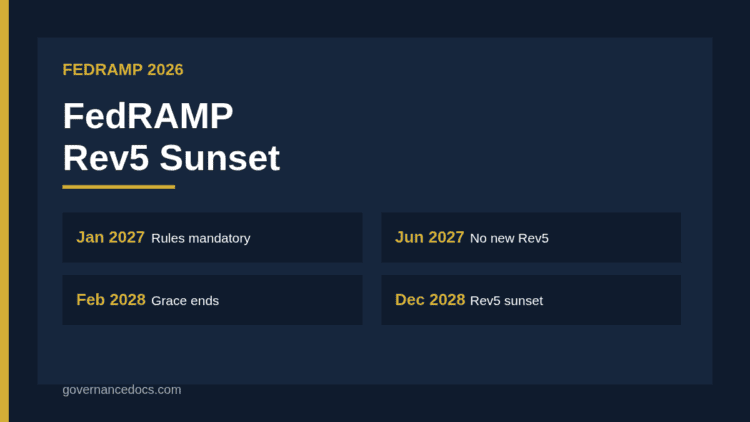
FedRAMP Rev5 sunset timeline infographic

FedRAMP Rev5 Sunset: The Essential 2026 Timeline for Cloud Providers

Governance Docs01st October 2026

The FedRAMP Rev5 sunset timeline: Consolidated Rules 2026, key dates through 2028 and what cloud providers should do…
Read More
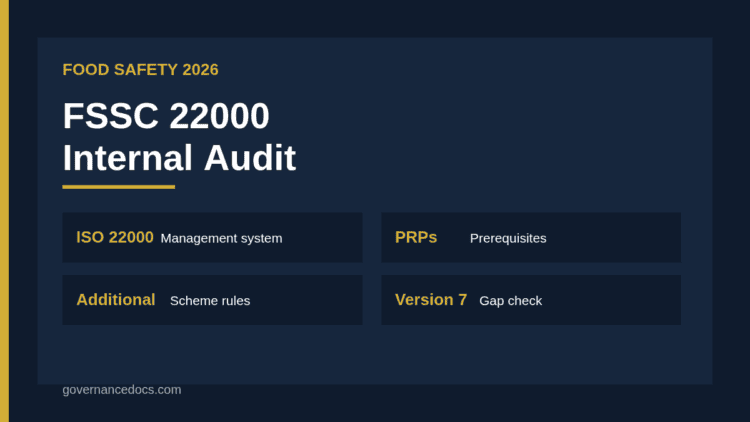
FSSC 22000 internal audit checklist infographic

FSSC 22000 Internal Audit Checklist: The Essential 2026 Guide for Food Manufacturers

Governance Docs01st October 2026

Use this FSSC 22000 internal audit checklist to test your food safety system against ISO 22000, prerequisite programs…
Read More
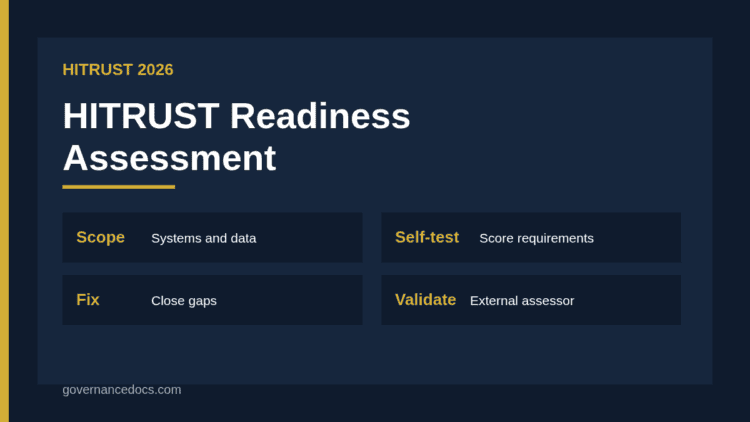
HITRUST readiness assessment infographic

HITRUST Readiness Assessment: The Essential 2026 Guide Before You Validate

Governance Docs01st October 2026

Learn how a HITRUST readiness assessment works, how to scope it, what to fix first and when to…
Read More
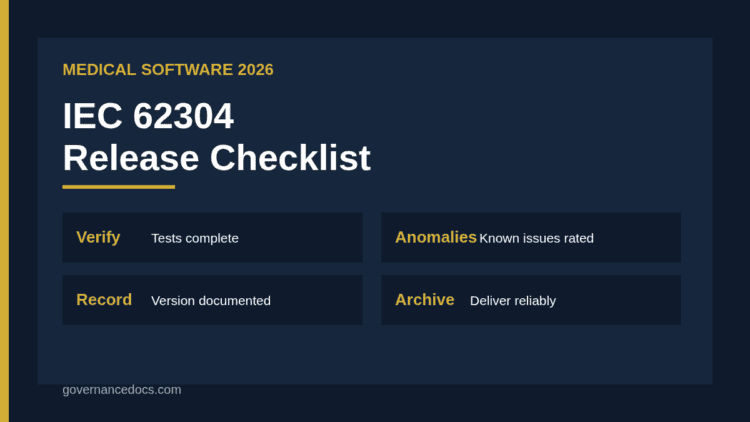
IEC 62304 software release checklist infographic

IEC 62304 Software Release Checklist: The Essential 2026 Guide to Clause 5.8

Governance Docs01st October 2026

An IEC 62304 software release checklist covering clause 5.8: verification, known anomalies, release records, archiving and delivery.
Read More
    ←
  • 1
  • 2
  • 3
  • →

Recent Posts

ISO 22301 surveillance audit cycle: stage 1 and 2, two annual surveillance audits, recertification, and what BCMS auditors test
ISO 22301 Surveillance Audit: The Complete 2026 Guide

November 11, 2026

ISO 42001 recertification audit: full-system review, major nonconformities closed before expiry, 6-month restore window and ISO/IEC 42006
ISO 42001 Recertification Audit: The Complete 2026 Guide

November 10, 2026

ISO 45001 toolkit: what a complete one contains, mapped to clauses 4 to 10
ISO 45001 Toolkit: What a Complete One Contains (2026)

November 9, 2026

ISO 13485 recertification audit 2026: audit time, expiry rules and MDSAP re-audit
ISO 13485 Recertification Audit: The Complete 2026 Guide

November 8, 2026

ISO 13485 surveillance audit infographic: first audit within 12 months of the certification decision, about one third of initial days, 8 plus 1 review areas, Global ACI-TECH-3-007
ISO 13485 Surveillance Audit: The Complete 2026 Guide

November 7, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
[email protected]
+1 505 289 2455

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Request a custom toolkit
  • Free templates
  • SoA generator
  • Assessments
  • Sample reports
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA