CART
CCPA vs GDPR is the comparison every company with Californian customers and European ones has to make, and the mistake in it runs both ways: treating GDPR compliance as automatically covering California, or building a Californian programme and assuming it satisfies Europe. The General Data Protection Regulation is a comprehensive law that applies to any organisation processing EU residents’ data, requires a lawful basis before processing starts, and fines up to €20 million or 4% of global turnover.
The California Consumer Privacy Act, as amended by the CPRA and now surrounded by the Privacy Protection Agency’s 2026 regulations, applies to for-profit businesses over defined thresholds, lets processing proceed by default subject to opt-out rights, and fines per violation — $2,663, or $7,988 for intentional violations and those involving children under 16, since the 2025 inflation adjustment. This guide sets out the eight differences that decide what a programme built for one has to add for the other, where the two have converged since 2023, and how to run a single privacy programme across both.
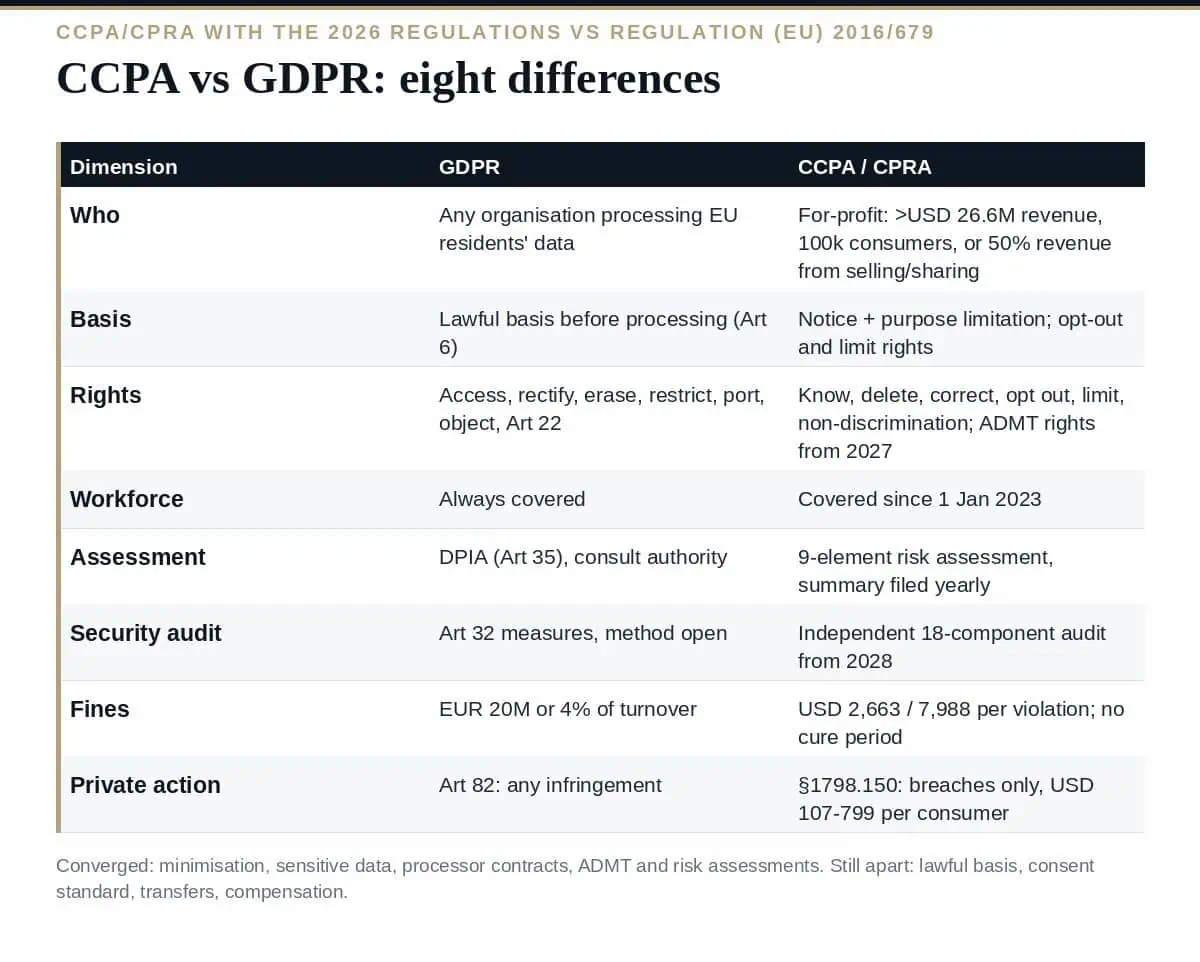
| Dimension | GDPR (Regulation (EU) 2016/679) | CCPA as amended by the CPRA, with the 2026 regulations |
|---|---|---|
| Who is covered | Any controller or processor established in the EU, or offering goods or services to or monitoring people in the EU, whatever its size or sector | For-profit businesses doing business in California that exceed $26,625,000 in annual revenue, or buy, sell or share the personal information of 100,000 or more consumers or households, or derive 50% or more of revenue from selling or sharing; plus their service providers, contractors and third parties |
| Whose data | Data subjects in the EU | California residents as consumers — including employees, contractors, job applicants and B2B contacts since 1 January 2023 |
| Basis for processing | A lawful basis under Article 6 before processing — consent, contract, legal obligation, vital interests, public task or legitimate interests | No prior basis; processing is lawful by default subject to notice at collection, purpose limitation, data minimisation and the consumer’s rights to opt out and limit |
| Consumer rights | Access, rectification, erasure, restriction, portability, objection, and rights about automated decisions (Articles 15–22) | Know, delete, correct, opt out of sale or sharing, limit use of sensitive personal information, non-discrimination, and — from 1 January 2027 — notice, opt-out and access rights for automated decision-making technology |
| Sensitive data | Special categories under Article 9, prohibited unless an exception applies | Sensitive personal information: a right to limit use to what is necessary, plus a risk assessment before processing |
| Risk assessment | A data protection impact assessment under Article 35 for high-risk processing, with prior consultation where residual risk is high | A risk assessment under Article 10 of the regulations before selling or sharing, processing sensitive data, using ADMT for significant decisions or training it — with a summary filed with the Agency each year |
| Fines | Up to €10 million or 2% of worldwide turnover, or €20 million or 4% for the more serious infringements (Article 83) | Administrative fines up to $2,663 per violation, or $7,988 for intentional violations and violations involving consumers known to be under 16; no cure period since 2023 |
| Private action | Article 82: compensation for material or non-material damage for any infringement | Section 1798.150 only: $107 to $799 per consumer per incident, or actual damages, for data breaches caused by a failure to maintain reasonable security |
The GDPR has no size threshold; a two-person consultancy processing EU customer data is a controller. The CCPA has three, and meeting any one is enough — revenue above $26,625,000 (adjusted every two years), personal information of 100,000 or more consumers or households, or half of revenue from selling or sharing. The third catches data brokers and ad-tech regardless of size; the first two exclude most small businesses entirely. The CCPA vs GDPR scope question therefore has opposite answers for a small company: probably in scope of the GDPR, probably out of scope of the CCPA.
This is the structural difference the rest follow from. Under the GDPR nothing may be processed without one of the Article 6 bases, and consent must be freely given, specific, informed and unambiguous.
Under the CCPA a business may collect and use personal information once it has given notice at collection, provided the use is compatible with the disclosed purposes and reasonably necessary and proportionate; the consumer’s protection is the right to opt out of sale and sharing and to limit the use of sensitive personal information, which the business must honour — including through opt-out preference signals such as Global Privacy Control. Consent appears in the CCPA only at the edges: children under 16, financial incentives, and re-entering a consumer into sale after an opt-out.
The lists overlap heavily — access, deletion, correction, portability in both — but California’s are held by a wider population. Since 1 January 2023 employees, job applicants, contractors and business-contact individuals are consumers with full rights, and the Agency’s first seven-figure enforcement decision, against Tractor Supply in September 2025, turned partly on the privacy rights of job applicants. The GDPR has always covered employees; the CCPA’s late arrival there is why HR data is the most common gap in a US programme extended from marketing.
The CCPA vs GDPR gap on assessments narrowed in 2026 but did not close. The GDPR’s DPIA under Article 35 is required for processing likely to result in a high risk, with the supervisory authority consulted if residual risk stays high. California’s risk assessment is required for a fixed list of activities regardless of a high-risk judgement, must contain nine specified elements including named contributors and an executive approver, must be updated within 45 days of a material change, and is reported to the Agency in summary each year under penalty of perjury.
Section 7156 of the regulations lets a DPIA count only if it contains everything the California rule requires; in practice a DPIA needs the minimum-data statement, the vendor list with purposes and the decision record added. Our guide to the CCPA risk assessment covers the nine elements.
The GDPR’s controller–processor model rests on Article 28: a written contract with prescribed terms, sub-processor authorisation, assistance duties, and a processor that is itself directly liable for some obligations. The CCPA’s service provider and contractor roles rest on the contract too — prohibitions on selling or sharing, on use outside the business purpose, on combining data, and a right to audit — but the consequence of a missing term is different: the vendor becomes a third party and the transfer becomes a sale or share, which triggers opt-out rights and a risk assessment. Our guide to CCPA service providers vs contractors covers the terms.
The GDPR requires appropriate technical and organisational measures under Article 32 and leaves the method to the controller. California’s 2026 regulations require businesses above defined processing thresholds to complete an annual cybersecurity audit by an independent auditor against 18 named components, with the first reports due from 1 April 2028 and a certification filed with the Agency each year. Nothing in the GDPR mandates an audit of that shape. Our guide to the CCPA cybersecurity audit covers it.
The GDPR is enforced by national supervisory authorities with turnover-based fines and a one-stop-shop for cross-border cases. The CCPA is enforced by the California Privacy Protection Agency through administrative decisions and by the Attorney General through civil actions, with per-violation amounts that scale with the number of consumers affected: Honda paid $632,500 in March 2025, Todd Snyder $345,178 in May 2025 and Tractor Supply $1.35 million in September 2025, while data brokers have been fined for registration failures under the Delete Act through 2026. The headline numbers are smaller than Europe’s; the per-consumer arithmetic on a large breach or a broken opt-out is not. Our guide to CCPA penalties covers the amounts.
Article 82 of the GDPR gives any data subject a right to compensation for any infringement, and European courts have awarded damages for non-material harm. The CCPA’s private right of action is confined to section 1798.150: a data breach of unencrypted, unredacted personal information caused by a failure to implement reasonable security, with statutory damages of $107 to $799 per consumer per incident. Every other CCPA violation is for the regulators alone — but the breach action, multiplied across a large consumer base, is the largest single exposure in the statute.
What is the main difference between CCPA vs GDPR?
The GDPR requires a lawful basis before any processing and applies to organisations of any size handling EU residents’ data, with fines up to 4% of turnover; the CCPA applies to for-profit businesses over revenue or volume thresholds, allows processing by default subject to notice and opt-out rights, and fines per violation — $2,663 or $7,988 since 2025 — with a private right of action limited to data breaches.
Does GDPR compliance cover the CCPA?
Mostly, but not entirely: California adds opt-out preference signals, the workforce as consumers, service-provider contract terms with different consequences, a nine-element risk assessment reported to the Agency, and from 2028 an independent cybersecurity audit.
Does CCPA compliance cover the GDPR?
No. A California programme lacks the lawful-basis requirement, consent standards, restriction and objection rights, the DPIA consultation route, international transfer rules and a general right to compensation.
Which has bigger fines?
The GDPR’s ceiling — €20 million or 4% of worldwide turnover — is far larger; the CCPA’s per-violation amounts multiply by affected consumers, and the largest CPPA decision to date is Tractor Supply’s $1.35 million in September 2025.
Are employees covered by the CCPA?
Yes, since 1 January 2023: employees, applicants, contractors and business contacts hold full consumer rights.
Treat CCPA vs GDPR as two regimes with one inventory: the GDPR’s lawful basis and consent standard as the floor for everyone, California’s opt-out mechanics, workforce coverage, risk-assessment reporting and cybersecurity audit as the additions, and one assessment template that satisfies both. The convergence since 2023 is real; the differences that remain are exactly the ones a programme built for the other side will miss.
The Privacy Program Framework, the Data Processing Inventory and Record of Processing Activities, the Cross-Border Data Transfer Policy, the Consumer Rights Policy and the Right to Opt-Out of Sale/Sharing Procedure are in the CCPA-CPRA Compliance Toolkit, or start with the free templates.


September 20, 2026

September 19, 2026

September 19, 2026

September 19, 2026

September 19, 2026

