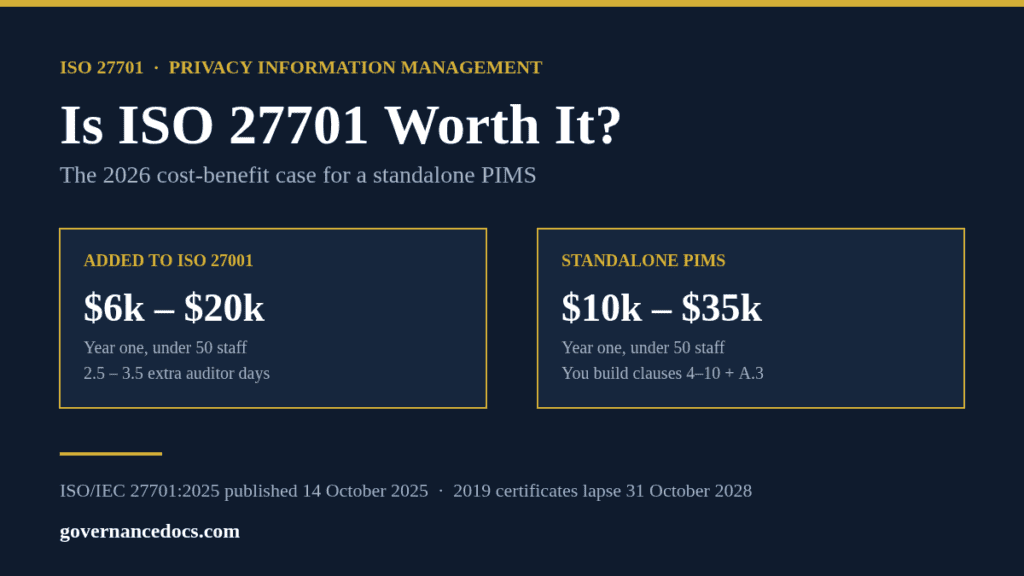
Is ISO 27701 worth it? For a processor whose customers already ask for privacy assurance, yes — added to an existing ISO 27001 certificate it typically costs $6,000 to $20,000 in year one.
The standalone route, new since October 2025, typically runs $10,000 to $35,000 in year one, because you build the management system and the Annex A.3 security controls yourself instead of inheriting them.
ISO 27701 is not a GDPR Article 42 approved certification, so it buys commercial credibility and a working privacy program, not a legal presumption of compliance.
Is ISO 27701 worth it in 2026? The honest answer is that it depends on one thing most budget conversations skip: whether anybody is actually asking you for it. Privacy certification does not create demand the way a SOC 2 report or an ISO 27001 certificate does. It answers a question that a specific kind of buyer asks, and if that buyer is not in your pipeline, the money is better spent elsewhere.
What changed is the price of entry. Until 14 October 2025 a Privacy Information Management System (PIMS) could only be certified alongside a valid ISO 27001 certificate, because ISO 27701 was an extension to it. ISO/IEC 27701:2025 is a standalone management system standard, which means the certificate is now available to organizations that were previously priced out of it — and unavailable as a cheap add-on to nothing.
This guide sets out the real cost on both routes, the returns that show up in practice, the one that does not, and a break-even test you can run in an afternoon.
Is ISO 27701 worth it? The short answer
Three situations, three answers.
Your situation
Is ISO 27701 worth it?
Why
You hold ISO 27001 and process personal data for customers
Usually yes
Marginal cost is 2.5 to 3.5 extra auditor days; it closes the privacy section of every vendor questionnaire you already answer
You are a pure processor (SaaS, BPO, payroll, managed service) with no ISO 27001
Often yes, now
Standalone certification did not exist before October 2025; privacy is the thing your customers are actually asking about
You are a controller whose obligations come from law alone, with no customer asking
Usually no
A certificate is not a defense under the GDPR; spend the budget on records of processing, retention and rights handling instead
The pattern is simple. Whether is ISO 27701 worth it comes down to one question: is a third party deciding whether to trust you with personal data? It pays back there, and it does not pay back as a compliance insurance policy.
Free privacy risk assessment
Which privacy risks would hurt the people whose data you hold?
List your personal data and processing, pick from 38 privacy risk scenarios, rate them for the people concerned and for you, and plan treatment with ISO 27701 controls. You get a heat map, a process score and the findings an auditor would raise, free.
You cannot answer is ISO 27701 worth it without the whole number, so split the spend into three buckets: building the PIMS, paying the certification body, and keeping the certificate alive. Most quotes only cover the middle one, which is rarely the largest.
Line item
Typical 2026 US range
Notes
The standard itself
CHF 225 (about $275)
Edition 2, dated 2025-10; the 2019 edition is withdrawn
Gap analysis against Annex A
$0 – $8,000
Free if run internally
PIMS documentation set
$99 – $15,000
Template toolkit versus consultant-written
Records of processing and PII inventory
$0 – $10,000
Scales with processing activities, not headcount
Control remediation
$0 – $20,000
Highest for controllers with consumer-facing products
Certification audit, added to ISO 27001
$3,500 – $9,000
2.5 to 3.5 extra auditor days for most firms under 65 staff
Certification audit, standalone PIMS
$5,000 – $14,000
Full Stage 1 and Stage 2 on its own
Internal staff time
150 – 400 hours
Privacy lead plus process owners; almost never budgeted
Year one, under 50 staff, added to ISO 27001
$6,000 – $20,000
Controls largely already in place
Year one, under 50 staff, standalone
$10,000 – $35,000
You also build clauses 4 to 10 and the A.3 security controls
These are planning bands aggregated from published 2026 guidance by accredited certification bodies and consultancies, not a survey. Get three quotes before you commit to any of them. Our ISO 27701 certification cost breakdown walks through how a certification body arrives at the audit days on each route.
One figure people forget is the surveillance cycle. Budget roughly a third of the certification audit fee for each of years two and three, plus a recertification audit in year three. Over a three-year certificate that is usually the initial audit fee again.
Is ISO 27701 worth it if you already hold ISO 27001?
This is where the arithmetic is easiest. You already have the scope statement, the risk process, the internal audit program, the management review and most of the security controls. What you add is the privacy layer: lawful basis records, a data map, consent and withdrawal mechanics, rights handling with a clock on it, retention schedules, processor and sub-processor agreements, and transfer records.
So is ISO 27701 worth it in that position? Three tests:
Do your vendor questionnaires have a privacy section you answer by hand every time? If yes, a certificate replaces a dozen free-text answers with one PDF. That is the clearest payback on this list.
Do your contracts contain privacy audit rights your customers actually exercise? Certification does not remove those clauses, but it reliably shortens the conversation.
Is your ISMS scope already the same as your processing scope? If it is, the delta is small. If not, the two scopes drifting apart is the single most common finding when both certificates are held.
If two of the three are yes, the bolt-on is cheap insurance against sales friction. Our guide to ISO 27001 vs ISO 27701 sets out what each certificate actually proves.
Is ISO 27701 worth it without an ISO 27001 certificate?
This is the group the 2025 revision was written for, and the answer changed in their favor. Before October 2025 a privacy-driven organization that had no interest in a security certificate had to implement and certify an entire ISMS first, then bolt the privacy extension on top. The total was often three times the cost of the thing they wanted.
Now the PIMS stands alone. The trade-off is that a standalone standard cannot assume controls it does not contain, so ISO/IEC 27701:2025 brings a set of information security controls inside itself as Annex A.3, alongside controller controls in A.1 and processor controls in A.2. You declare and evidence those security controls within the PIMS rather than inheriting them. That is why the standalone route costs more in year one despite covering less ground.
Published control counts differ between certification bodies, because subclauses can be tallied more than one way. Take the count from the copy of the standard you are certifying against — it is the list your Statement of Applicability has to answer. Our breakdown of ISO 27701:2025 vs 2019 covers what carries over and what you have to build.
One practical note on timing: certification bodies have been completing their own accreditation transitions to the 2025 edition through 2026. Ask a prospective body to confirm its accreditation scope for ISO/IEC 27701:2025 in writing before you sign.
The four returns that show up — and the one that does not
In practice the certificate returns value in four places:
Procurement throughput. Enterprise and public sector buyers run privacy due diligence separately from security due diligence. A certificate is the fastest way through the second gate.
Processor credibility. If you process on documented instructions, your customer carries the controller’s accountability for your work. Independent assurance is directly useful to them, which makes it directly useful to you.
Internal discipline. The records of processing and the retention schedule are the artifacts most privacy programs never finish. An audit date finishes them.
Multi-regime leverage. One PIMS answers the GDPR, the UK regime, CCPA and CPRA, and India’s DPDP Act from the same control set, because the standard is written around processing roles rather than one law.
The return that does not show up is legal protection. ISO 27701 certification is not an approved certification mechanism under Article 42 of the GDPR. The first scheme approved under that article was Europrivacy, endorsed by the European Data Protection Board in October 2022 as the European Data Protection Seal. A regulator will treat an ISO 27701 certificate as evidence that you took your obligations seriously. It is not a presumption of compliance, and anyone selling it to you as one is overselling.
When ISO 27701 is not worth the money
Four cases where the answer to is ISO 27701 worth it is no, or not yet:
Nobody has asked. If no customer, tender or contract has requested privacy assurance, you are buying a certificate to put on a page.
Your records of processing do not exist. Certification will force you to build them, but at audit-day rates. Build them first and the audit gets cheaper.
You are mid-way through the 2019 edition. Stop and re-baseline against the 2025 edition. Certificates issued to the 2019 edition remain valid until 31 October 2028 and then lapse, so certifying to a withdrawn edition now buys a short-dated asset.
You need a transfer mechanism. ISO 27701 is not one. Standard contractual clauses plus a transfer impact assessment are.
A break-even test you can run this week
Pull the last 20 deals that involved personal data and count three numbers: how many had a privacy questionnaire, how many stalled on a privacy question, and the average value of the ones that stalled. If one stalled deal in the year is worth more than $20,000 in margin, the bolt-on route pays for itself on a single save. For the standalone route, make it two saves.
Then check the opposite direction. If none of the 20 raised a privacy question, the certificate is not the constraint on your pipeline and you should say so out loud before the budget is approved.
If the answer comes out yes, the documentation is the part you can buy rather than write. Our ISO 27701 Toolkit ($99, 75+ templates) covers the PIMS documentation set — policies, records of processing, the Statement of Applicability and the controller and processor control evidence — so the spend goes on the audit rather than on drafting.
Frequently asked questions
Is ISO 27701 worth it for a small SaaS company?
If you process customer personal data and sell to businesses, usually yes — and the standalone route now makes it viable without an ISO 27001 certificate first. Under 50 staff, budget $10,000 to $35,000 in year one standalone, or $6,000 to $20,000 added to an existing ISO 27001 certificate.
Does ISO 27701 certification prove GDPR compliance?
No. It is not an Article 42 approved certification mechanism, so it carries no legal presumption. It is strong evidence of a managed privacy program, which is a different and more modest claim.
Can I certify ISO 27701 without ISO 27001?
Yes, since ISO/IEC 27701:2025 was published in October 2025. The standard is now a standalone management system standard with its own clauses 4 to 10, and it includes the information security controls it used to inherit.
How long does ISO 27701 certification take?
Plan six to nine months from a standing start for a standalone PIMS, or three to four months to add the privacy layer to a working ISO 27001 management system. The constraint is usually the records of processing, not the audit calendar.
Is ISO 27701 worth it if I already hold a SOC 2 report?
Often yes, because they answer different questions. SOC 2 reports on controls at a service organization against the trust services criteria; ISO 27701 certifies a privacy management system against a published standard. Buyers in regulated sectors increasingly ask for both.
The verdict
Is ISO 27701 worth it? Yes if a buyer is asking, and the bolt-on route makes it one of the cheapest certificates you can add to an existing ISO 27001 program. Yes if you are a processor who was previously locked out, because standalone certification finally prices it sensibly. No if you are buying it as protection from a regulator, because that is not what it does. Start with the guide to privacy information management, run the 20-deal test, and let the pipeline decide.