An ISO 27001 risk assessment template is only as useful as the method behind it, because the standard asks for a repeatable process, not a particular spreadsheet. A template that lets two assessors reach the same score for the same risk, and that records the evidence auditors ask for, is one that will survive certification.
This guide sets out what the template must contain to meet clause 6.1.2 and clause 6.1.3, which fields to include, how to keep scoring consistent and which mistakes to avoid. It links to the methodology, the risk register and the risk treatment plan.
Free gap assessment
Where do you actually stand against ISO 27001?
Score every management system clause and all 93 Annex A controls, free, and get a prioritised gap list back.
What the standard requires from an ISO 27001 risk assessment template
Clause 6.1.2 of ISO/IEC 27001:2022 requires you to define and apply an information security risk assessment process. It must establish risk acceptance criteria and criteria for performing assessments, produce consistent, valid and comparable results, identify risks and their owners, analyze likelihood and consequences and evaluate risks against your criteria.
Free ISO 27001 risk assessment
Which of your risks sit above your appetite line?
Set your own risk criteria, pick from 61 information security risk scenarios, rate likelihood and impact, and decide how to treat each one. You get a heat map, a process score and the findings an auditor would raise, free.
Clause 6.1.3 then requires a treatment process, a comparison of your chosen controls with Annex A, a Statement of Applicability, a treatment plan and owner approval of residual risk. You can confirm the wording in your licensed copy, listed at ISO/IEC 27001:2022 on iso.org. A good template makes each of those requirements visible.
Start with criteria, not with the spreadsheet
Before any risk is entered, define your scales. Decide how likelihood and impact are measured, what each level means in plain language, and which scores are acceptable, which need treatment and which need senior approval. Without this, the template is a blank grid and scores become opinions.
The guide to risk criteria explains how to write those scales and link them to your appetite, and they should sit on the first tab of the workbook so every assessor sees them.
Fields the ISO 27001 risk assessment template should include
Keep the layout compact but complete. Record a unique risk ID, the asset or process affected, the threat, the vulnerability, the consequence for confidentiality, integrity and availability, the inherent likelihood and impact, the inherent score, the treatment decision, the controls applied, the residual score, the owner and the review date.
Add columns only when someone will use the data. Each extra field is another thing to maintain, and unused columns are a common sign of a template copied from somewhere else.
Sample rows for an ISO 27001 risk assessment template
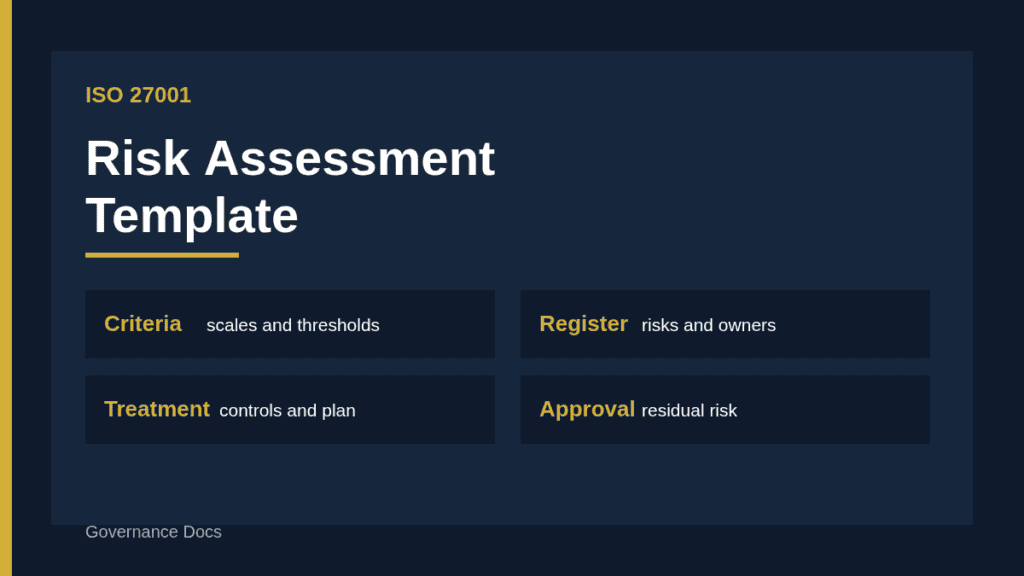
The table in this article shows the sections of a workable template. A good register row reads as a specific scenario, for example: customer records in the payment database could be disclosed through stolen administrator credentials because multi-factor authentication is not enforced; inherent score high; treatment modify through enforced multi-factor authentication and privileged access monitoring; residual score medium; owner head of IT.
Compare that with a vague row such as “data breach”, which cannot be scored consistently or linked to a control.
Template section
What it records
Standard link
Audit question it answers
Risk criteria
Scales, thresholds, appetite
Clause 6.1.2 a
How do you decide what is acceptable?
Risk register
Risks, owners, scores
Clause 6.1.2 c to e
Who owns each risk and how was it scored?
Treatment
Options, controls, actions
Clause 6.1.3
What are you doing about it?
Approval
Residual risk and sign-off
Clause 6.1.3 f
Who accepted what remains?
Choosing asset-based or scenario-based structure
The 2022 edition no longer requires you to start from assets, so either structure satisfies the standard. Asset-based templates list each asset with its threats and vulnerabilities, which suits organizations with a mature asset inventory. Scenario-based templates list events, which read more naturally to management.
Our guides to asset-based and scenario-based assessment compare the two. Whichever you choose, use it consistently in one register.
Linking the template to treatment and the Statement of Applicability
Every risk above threshold needs a treatment decision, and each chosen control should trace to Annex A and to the Statement of Applicability. Build that traceability into the template with a column for control references and a column for the treatment action, owner and due date.
Auditors often follow one risk from identification through control to evidence, so a clear trail saves time during the audit and shows the process works.
Recording residual risk and owner approval
The template must capture residual risk after treatment and the approval of the risk owner, because clause 6.1.3 requires owners to accept residual risks. Include approver name, role and date, and keep the approved score visible next to the inherent one so the effect of controls is clear.
The article on residual risk shows how to rescore consistently after treatment.
Send owners their own rows before each review, ask them to confirm or change the scores and record their reply. A simple confirmation email saved with the register is strong evidence that owners take part rather than receive a finished spreadsheet.
Assigning owners in the template
Every row needs a named individual with the authority to accept or treat the risk, not a department alias. Owners should confirm their scores at each review. The guide to the risk owner role sets out what ownership means in practice.
If an owner cannot be named, that is itself a finding, because nobody is accountable for the risk.
Testing an ISO 27001 risk assessment template before rollout
Pilot the template with two or three assessors on the same five risks, working separately. Compare the scores and discuss every difference larger than one level. Disagreements usually point to a scale definition that is too vague or a field that means different things to different people. Fix the template, then retest. This half-day exercise prevents months of inconsistent data and gives you a record showing that the process produces comparable results, which is what clause 6.1.2 asks for.
Also ask a risk owner from outside security to read a completed row. If they cannot follow it, simplify the wording.
Common mistakes with an ISO 27001 risk assessment template
Templates fail in predictable ways.
Copying an example register full of risks that do not match the business.
Scales without definitions, so scores differ between assessors.
No link from risks to treatment, controls or owners.
A residual score with no approval or date.
Never updating the template after a change in scope or method.
Version control for the ISO 27001 risk assessment template
Treat the template and completed assessments as documented information. Store them in one place, record version and date, restrict editing and keep previous versions so you can show how scores changed. Take a dated copy at each review as audit evidence.
Protect formulas and lock the scale definitions so nobody changes them without approval.
What auditors sample from the template
Auditors rarely read the whole register. They pick a few rows and trace each from the description to the scores, the treatment decision, the control and its evidence, and finally the owner approval and date. They also check that the scales in use match the documented criteria and that the assessment has been reviewed within the planned interval. Rehearse this trace yourself on five random rows before the audit. Any break in the chain, such as a control reference that does not exist or an approval older than the score, is worth fixing first.
Between formal reviews, keep a short change log of new risks, changed scores and closed actions, so the next review starts from a current picture and nothing depends on memory.
Reviewing and updating the assessment
Clause 6.1.2 requires assessments at planned intervals or when significant changes occur. Record the cycle in your procedure and capture triggers such as incidents, new suppliers and system changes. The guide to the risk review shows how to run each cycle.
Adapting the template to your size and sector
A small company can run the whole assessment on four tabs: criteria, register, treatment and approvals. A larger organization may add tabs for asset inventory, threat and vulnerability libraries and supplier risks. Regulated sectors sometimes add columns for regulatory references or data protection impact. Keep the core structure the same so results stay comparable, and document any additions in the procedure so auditors understand why they exist.
Using a finished structure
If you would rather not build the template yourself, the ISO 27001 Risk Assessment Report and Workbook provides a structured report and workbook with criteria, register, treatment and approval sections already laid out. Whatever you use, test it on a few real risks before rolling it out, and adjust fields that nobody fills in.
ISO 27001 risk assessment template FAQ
Does ISO 27001 require a specific risk assessment template?
No. The standard requires a defined, repeatable process and documented results, but it does not prescribe a format.
Can I use a simple spreadsheet?
Yes, provided it records criteria, risks, owners, scores, treatment and approvals and is kept under version control.
Do I still need an asset register?
The 2022 edition does not require an asset-based method, but many organizations keep one because it helps identify risks.
How many risks should the template hold?
Enough to cover your scope with specific scenarios. Quality matters more than volume.
Who should approve the completed assessment?
The risk owners approve treatment and residual risk, and senior management approves risks above your defined threshold.