Description
What the ISO 27001 risk assessment report contains
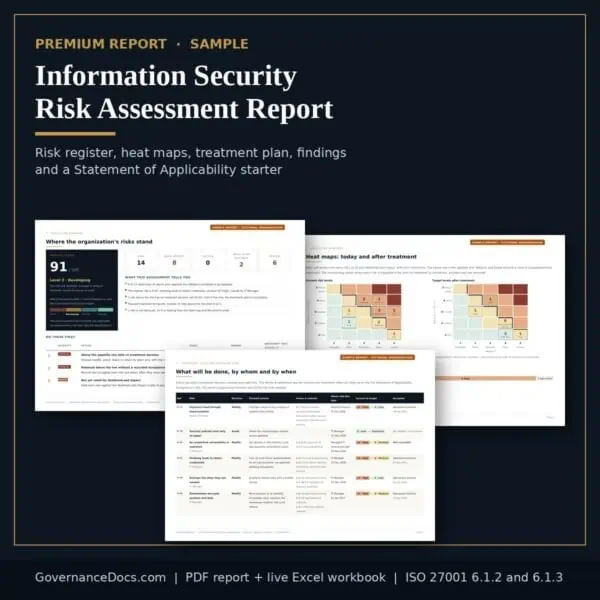
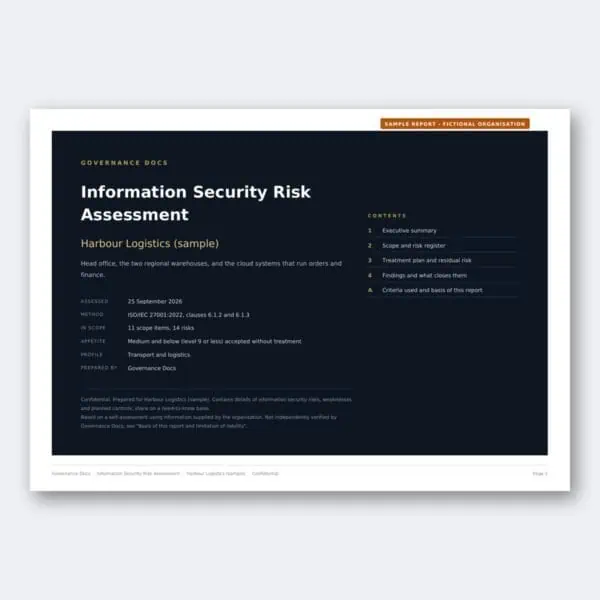
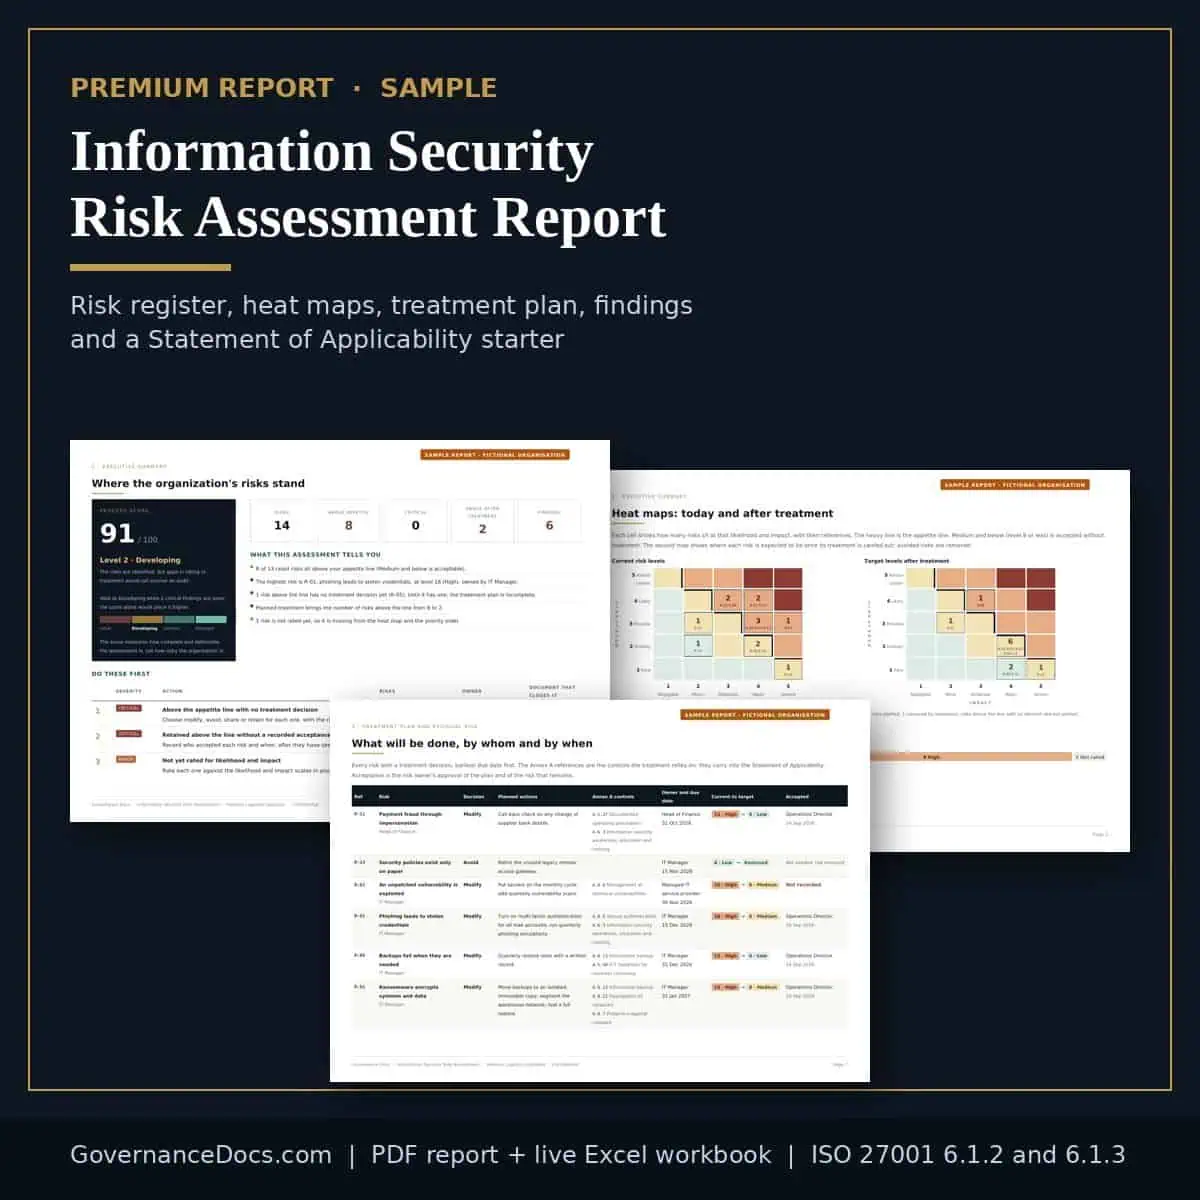
You already have your heat map, your top risks and your findings for free. This ISO 27001 risk assessment report is the full assessment behind them, written up as the record an auditor, a board or a risk committee expects to see.
- The complete risk register, highest level first. Every risk with its owner, the scope items it affects, the controls already in place, its likelihood, impact and level, and the rationale for the rating.
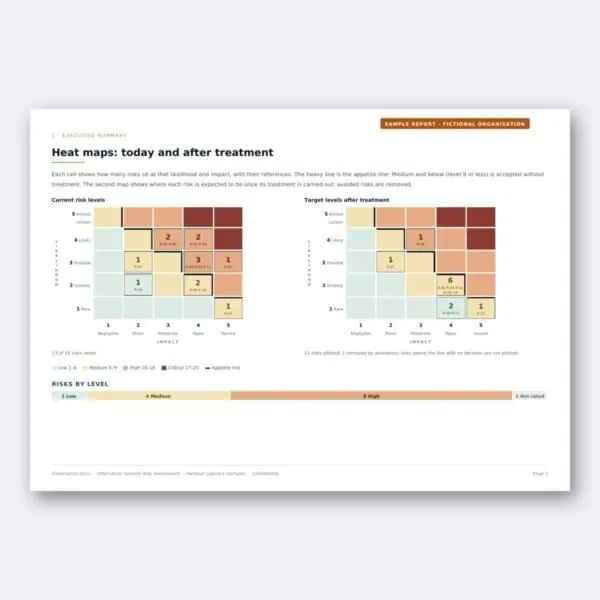
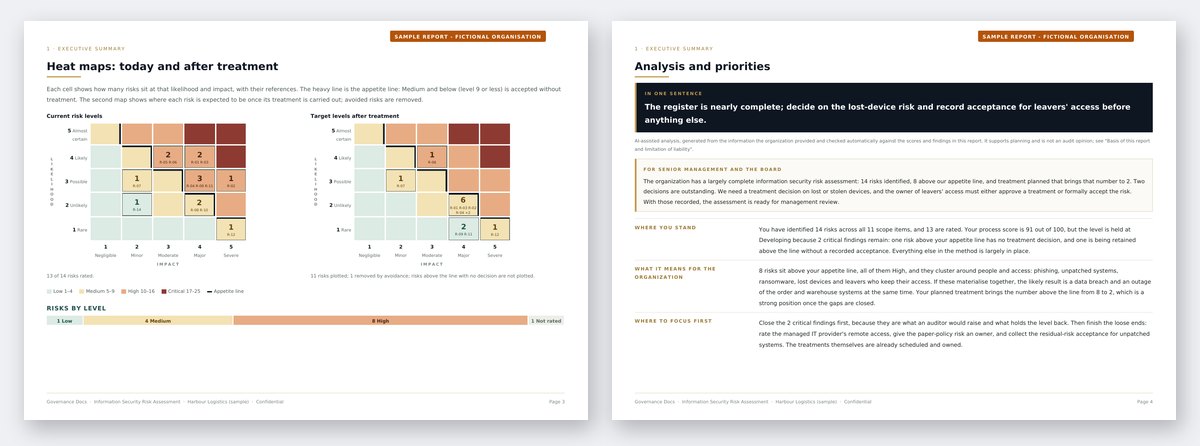
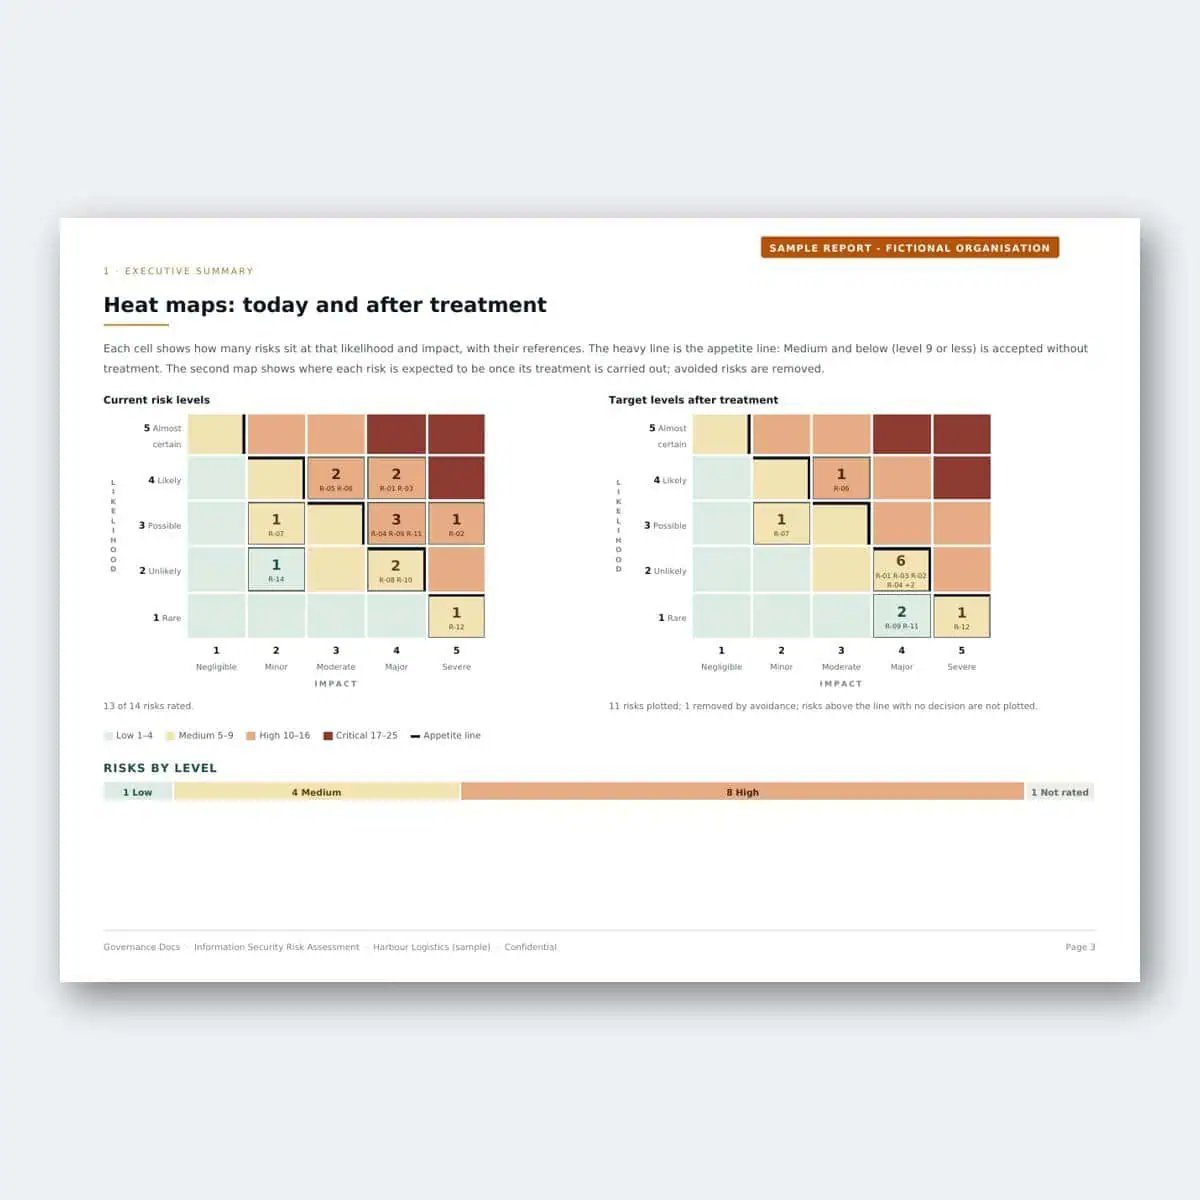
- Heat maps today and after treatment, side by side. Both drawn against your own appetite line, so anyone can see at a glance what the treatment plan achieves.
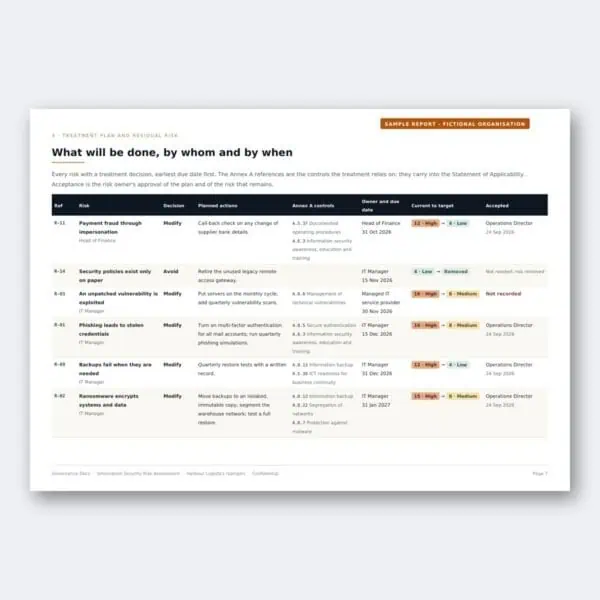
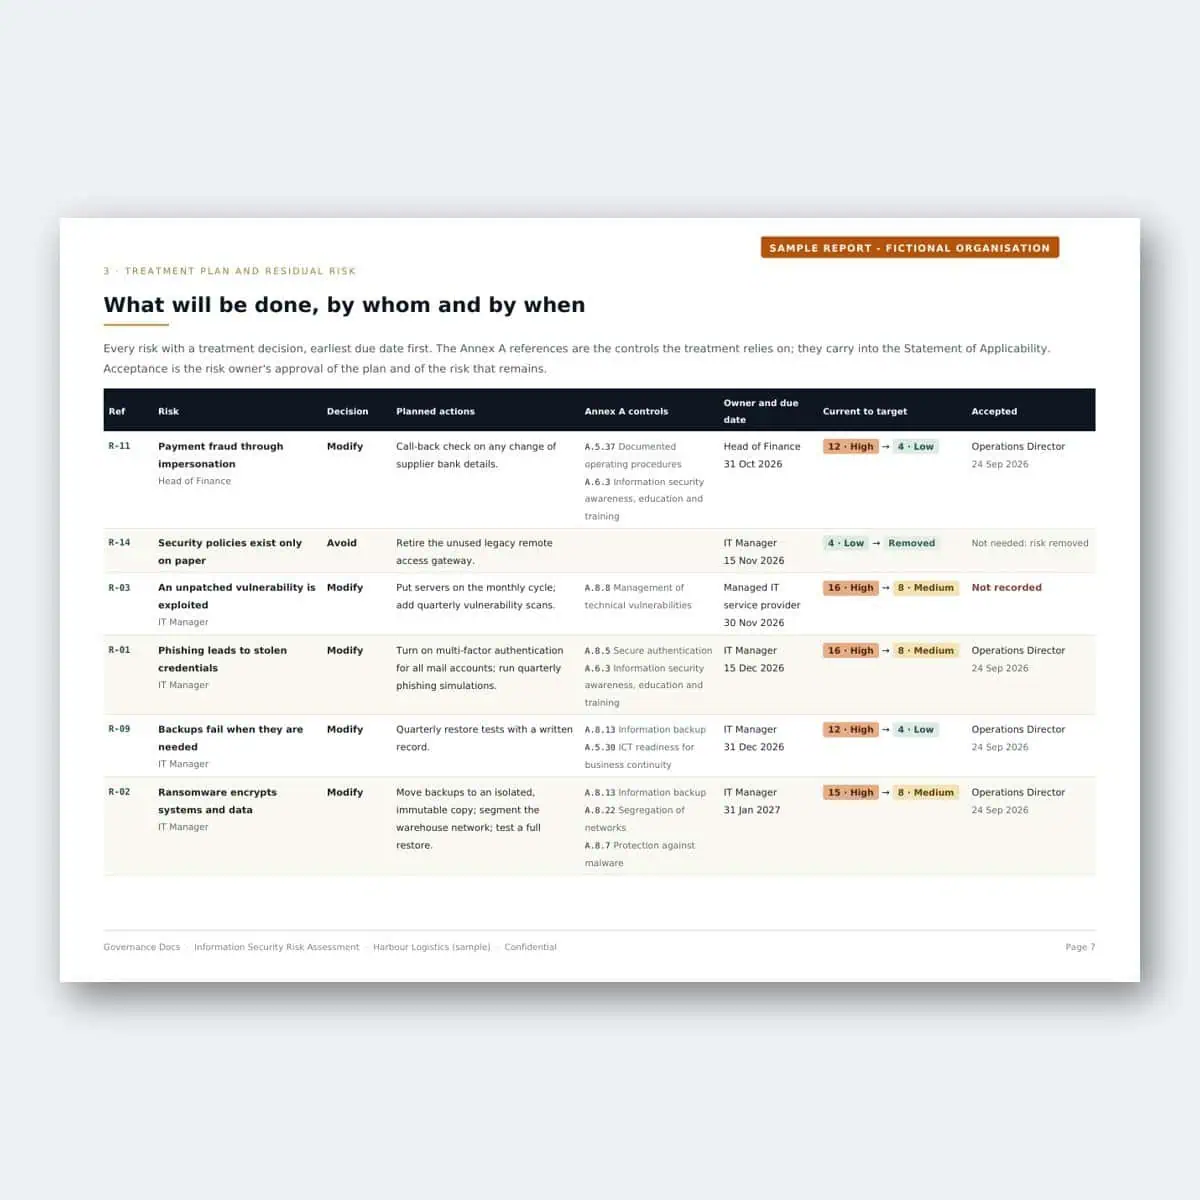
- The treatment plan by due date. For each risk: the decision (modify, avoid, share or retain), the planned actions, the Annex A controls it relies on, the treatment owner, the due date, the current and target level, and the risk owner’s acceptance.
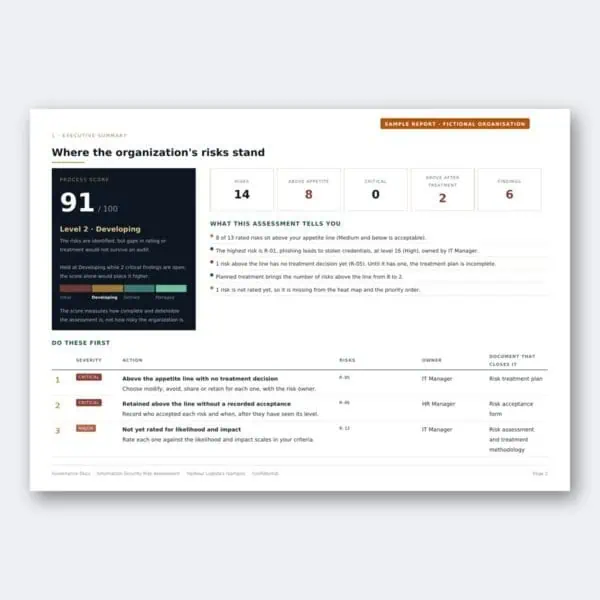
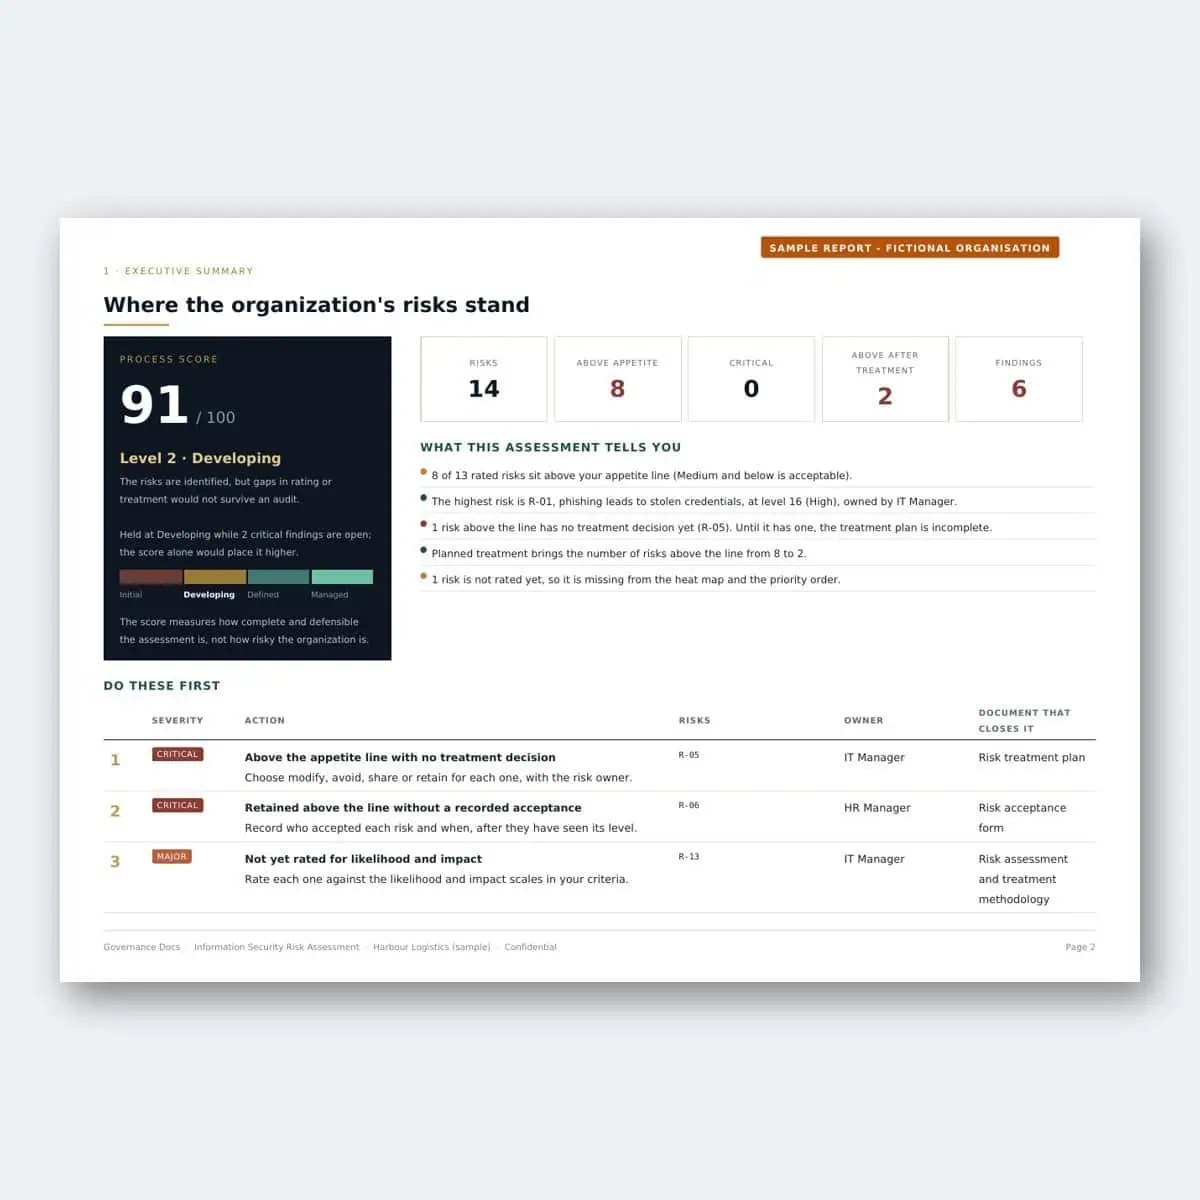
- Every finding, with what closes it. Each gap between your assessment and what ISO 27001 clauses 6.1.2 and 6.1.3 ask for, the risks it applies to, what to change, and the document that closes it.
- An AI-assisted analysis and 30/60/90-day roadmap. A one-sentence verdict, where you stand and what it means, a statement for your board, three to five priorities and a roadmap, written from your own ratings and checked automatically against them.
- Your process score in detail. Nine weighted dimensions, from criteria and ownership to treatment and residual risk acceptance, so you can see exactly where the assessment is thin.
- Your criteria, written up. Likelihood and impact definitions, the risk bands and the appetite line: the record of risk acceptance criteria clause 6.1.2 requires.
The live Excel workbook
A risk assessment is revisited every time something changes, so alongside the ISO 27001 risk assessment report you also get the register as a working file, not a static export:
- Dashboard: the process score, level and heat maps, recalculated as you edit.
- Criteria: your scales, band ceilings and appetite line, which drive every calculation.
- Scope and Risk register: change a likelihood or impact and the level, band and appetite check update.
- Treatment plan: decisions, actions, owners, due dates, targets and acceptance.
- Statement of Applicability starter: all 93 Annex A controls, with those your treatments rely on marked as selected and the risks they treat listed, ready for your justifications and implementation status.
How to get your ISO 27001 risk assessment report
- Run the free ISO 27001 risk assessment: set your criteria, list what is in scope, pick risks from the library, rate them and decide how to treat each one.
- Finish to see your free results, then choose Get the full report.
- Your ISO 27001 risk assessment report and the workbook are generated immediately and a link is emailed to you. They also appear under My assessments in your account. Each report is final: it shows your answers as they were when you bought it.
You cannot buy this product on its own, because there would be nothing to put in it. If you have arrived here directly, start the free assessment first.
Honest about the boundaries
The ISO 27001 risk assessment report is exactly as good as the information you enter. It is a structured self-assessment built on your own criteria and ratings; Governance Docs does not review or verify it, and it is not a certification, an audit opinion or a substitute for an independent risk assessment. What it does is show you, clause by clause, whether your assessment is complete, consistent and defensible, and what to fix where it is not.
For the policies, procedures and templates that close the gaps it finds, see the ISO 27001 Toolkit. The requirement itself is clause 6.1.2 of ISO/IEC 27001:2022.
Guides for the ISO 27001 Risk Assessment Report
Free articles that explain the requirements this toolkit covers.


Reviews
There are no reviews yet