CART
Compliance consulting rates are set by three things a client rarely sees: the consultant’s utilisation, the cost of the certifications and tools the work requires, and the risk the consultant carries when a certificate, an audit or a regulator is on the line. Nobody publishes a tariff, and the ranges that circulate — from a few hundred dollars a day for a documentation contractor to several thousand for a partner at a large firm — are so wide that they say nothing until they are broken down by service, seniority, market and pricing model.
This guide does that breakdown with labelled typical ranges for 2026: day and hour rates by seniority and market, fixed-fee ranges for the engagements clients most often buy — ISO 27001, ISO 9001, SOC 2 readiness, GDPR, a virtual CISO retainer — the arithmetic that turns a rate into an income, how clients compare quotes, and how to set and defend a rate as an independent or a small practice. The ranges are planning figures drawn from published proposals and our own engagements, not survey data; treat them as a starting point for a quote, not a benchmark to hold anyone to.
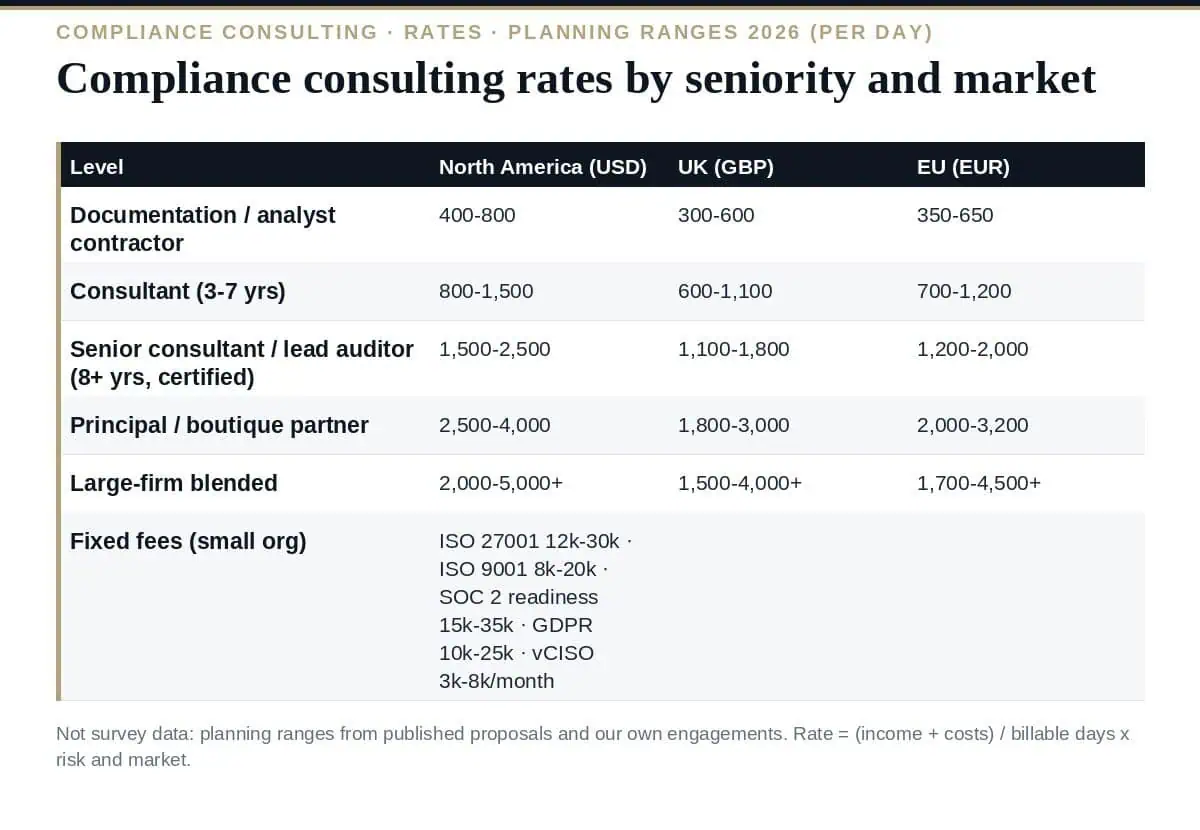
| Level | Typical work | North America (USD/day) | UK (GBP/day) | EU (EUR/day) | Middle East and Asia-Pacific (USD/day) |
|---|---|---|---|---|---|
| Documentation and analyst contractor | Drafting policies and procedures, evidence collection, register upkeep | $400 to $800 | £300 to £600 | €350 to €650 | $300 to $700 |
| Consultant (3–7 years) | Gap analysis, implementation, internal audit, audit preparation | $800 to $1,500 | £600 to £1,100 | €700 to €1,200 | $600 to $1,300 |
| Senior consultant / lead auditor (8+ years, certified) | Programme lead, multi-framework, regulator-facing work, expert witness | $1,500 to $2,500 | £1,100 to £1,800 | €1,200 to €2,000 | $1,200 to $2,200 |
| Principal / partner at a boutique | Strategy, board advisory, remediation after enforcement | $2,500 to $4,000 | £1,800 to £3,000 | €2,000 to €3,200 | $2,000 to $3,500 |
| Big Four and large-firm teams | Blended team rates; partners well above | $2,000 to $5,000+ blended | £1,500 to £4,000+ | €1,700 to €4,500+ | $1,800 to $4,500+ |
Hourly equivalents run at roughly the day rate divided by seven to eight, with a premium of 10–25% for hourly and short-notice work. Sector, framework scarcity and regulatory pressure move the figure inside each band: FedRAMP, DORA, PCI QSA-adjacent and medical-device (ISO 13485, MDR) work sits at the top; ISO 9001 and generic policy work at the bottom. Our guide to the compliance consulting practice covers the six decisions that put a consultant in one band rather than another.
| Engagement | Typical scope | Small organisation (≤50 staff) | Mid-size (50–500 staff) | Notes |
|---|---|---|---|---|
| ISO 27001 implementation to certification-ready | Gap analysis, risk assessment, SoA, policies, internal audit, management review, audit support | $12,000 to $30,000 | $30,000 to $80,000 | Excludes certification body fees; template-based delivery sits at the low end |
| ISO 9001 / 14001 / 45001 implementation | Same shape, lighter risk work | $8,000 to $20,000 | $20,000 to $50,000 | Integrated systems priced per additional standard at 30–50% of the first |
| SOC 2 readiness | Scoping, control design, evidence, readiness assessment | $15,000 to $35,000 | $35,000 to $90,000 | Excludes the CPA attestation |
| GDPR / privacy programme | Data mapping, RoPA, DPIAs, policies, DSAR process, DPO support | $10,000 to $25,000 | $25,000 to $70,000 | Ongoing DPO-as-a-service retainers separate |
| Gap analysis or readiness assessment (any framework) | Assessment and prioritised report | $3,000 to $8,000 | $8,000 to $25,000 | Often credited against a follow-on implementation |
| Internal audit (outsourced) | Programme, fieldwork, report | $2,000 to $6,000 per audit | $6,000 to $20,000 | Per standard, per cycle |
| Virtual CISO / compliance officer retainer | Defined days per month, board reporting, programme ownership | $3,000 to $8,000 per month | $8,000 to $20,000 per month | Our virtual CISO guide covers the service elements |
| Remediation after an audit failure or enforcement | Root cause, corrective action programme, regulator liaison | Time and materials | Time and materials | Rarely fixed-fee; risk too open |
| What the client compares | What it actually measures | How to present it |
|---|---|---|
| Day rate | Seniority and market position | State it with the deliverables per day; a high rate with fast delivery beats a low rate with slow |
| Fixed fee | Predictability | Scope, assumptions, exclusions and change triggers stated; see our fixed fee vs time and materials guide |
| Total cost to certificate | The real question | Include certification body fees, tools and the client’s own time in the proposal so the comparison is honest |
| Credentials | Risk reduction | Lead auditor, CISA, CISSP, CCEP, CIPP — and the audit outcomes they have produced |
| Guarantees | Confidence | Offer audit support and a re-work commitment rather than a ‘certification guarantee’ nobody can honestly give |
What are typical compliance consulting rates in 2026?
As planning ranges: $400 to $800 a day for documentation contractors, $800 to $1,500 for consultants, $1,500 to $2,500 for senior certified consultants and lead auditors, $2,500 to $4,000 for boutique principals, and $2,000 to $5,000-plus blended for large firms in North America; the UK, EU, Middle East and Asia-Pacific run 10–30% lower in local terms. These are not survey data.
How much does an ISO 27001 consultant cost?
Fixed fees of $12,000 to $30,000 for a small organisation and $30,000 to $80,000 for a mid-size one to reach certification-ready, excluding the certification body. Template-based delivery sits at the low end of each range.
Why do rates vary so much?
Seniority, market, framework scarcity, regulatory pressure and the risk carried. A FedRAMP or DORA specialist facing a regulator is priced differently from an ISO 9001 documentation contractor, and both are compliance consultants.
Should I charge a day rate or a fixed fee?
Fixed fee for bounded, repeatable engagements — implementations, audits, assessments; time and materials for open-ended work — remediation, regulator liaison. Most practices run both with a published rate card.
How do templates affect what I can charge?
They reduce hours per engagement, so a fixed fee carries a higher effective rate. The condition is a licence that allows client use — single-organisation packs cannot be reused on a second client.
Set compliance consulting rates from the arithmetic — income and costs over realistic billable days — adjust for risk and market, price bounded work as fixed fees and unbounded work on a rate card, and let templates and repeatable methods raise the effective rate rather than lower the price. Then present total cost to outcome, not the day rate, because that is the number the client is actually comparing.
The Consultant Package — every Governance Docs toolkit, 85 packs and 7,700+ editable documents, licensed for unlimited client engagements at $1,399 one-time — is the library that turns a day rate into a fixed fee, or start with the free templates.


September 20, 2026

September 19, 2026

September 19, 2026

September 19, 2026

September 19, 2026

