CART
A bribery risk assessment is the document ISO 37001:2025 builds everything else on. Clause 4.5 requires it; clause 1 says the extent to which the standard’s requirements apply “depends on the factors specified in 4.1, 4.2 and 4.5”; clause 8.2 triggers due diligence where it shows more than a low risk; and the standard’s organising principle — controls that are “reasonable and proportionate according to the bribery risks the organization faces” — has no meaning without it. An auditor who wants to know whether your gifts register, your agent screening or your financial approvals are proportionate reads the bribery risk assessment first, and a thin one undermines every control in the system however well the control itself is run. This guide sets out what clause 4.5 requires, the risk factors the standard’s own text names — size, locations, sectors, and “the nature, scale and complexity of the organization’s activities” — the method for identifying, analysing and evaluating bribery risks, the scoring criteria that make “low risk” a defensible label rather than a convenient one, how the assessment drives due diligence and controls, and the five findings auditors raise against it.
| Element | What ISO 37001:2025 expects | Evidence |
|---|---|---|
| Identify | The bribery risks the organisation could reasonably anticipate — bribery by it, its personnel and its business associates on its behalf, and bribery of them — direct and indirect | A register of risks by activity, geography, sector, transaction type and relationship |
| Analyse, assess and prioritise | Likelihood and consequence of each identified risk | Scores against defined scales |
| Evaluate existing controls | Whether the controls in place are suitable and effective against each risk | Control column with an effectiveness judgement |
| Criteria | The organisation’s own criteria for evaluating the level of bribery risk, consistent with its policy and objectives | Documented criteria, including what ‘low’ means |
| Review | Regularly, so changes and new information are reflected, and on significant change to structure or activities | Dated reviews; change triggers |
| Documented information | Retained as evidence of the assessment | The assessment file with versions |
The standard’s own risk vocabulary applies: risk is the “effect of uncertainty on objectives” (3.12), characterised by events, consequences and likelihood, and ISO 31000 is in the bibliography. The 2025 edition adds subclauses on climate change — a context factor under 4.1 — and on compliance culture, and addresses conflicts of interest expressly, which widens what the assessment has to consider. Our guide to ISO 37001:2025 covers the edition.
| Factor | What raises the risk | Where to look |
|---|---|---|
| Countries and locations | Operations, customers, agents or supply in jurisdictions with high perceived corruption; the bibliography points to Transparency International’s Corruption Perceptions Index and the World Bank’s governance indicators | Country list against the indices; where officials are met |
| Sectors | Extractives, construction and infrastructure, defence, pharmaceuticals and healthcare, telecoms, logistics and customs-heavy trade, public procurement generally | Sector exposure per business unit |
| Transactions and activities | Government contracts, licences and permits, customs clearance, inspections, tax matters, land, visas and work permits, regulatory approvals, charitable and political donations, sponsorships | The interactions with public officials (3.26) per process |
| Business associates | Agents, intermediaries, consultants, distributors, JV partners, lobbyists — especially on commission or success fees; the standard’s definition is deliberately broad | Associate register by type and role |
| Personnel | Roles that meet officials, approve payments, award contracts, or hold conflicts of interest (3.28) | Position-by-position exposure; declarations |
| Bribery of the organisation | Procurement, recruitment, contract award and approval roles that can be bribed by others — the standard’s scope covers bribery of the organisation and its personnel | Inbound exposure per role |
| Structure and history | Controlled organisations, minority holdings, new acquisitions, past incidents and concerns raised | Group map; incident and concerns log |
| Assessment output | Clause it drives | What proportionate looks like |
|---|---|---|
| Associates and personnel above low risk | 8.2 Due diligence | Enhanced checks on the exposed few; declarations for the rest; see our anti-bribery due diligence guide |
| Payment routes exposed to bribery | 8.3 Financial controls | Approval thresholds, dual authorisation, no cash, vendor master controls |
| Processes exposed — procurement, contract award, recruitment | 8.4 Non-financial controls | Separation of duties, tender panels, recruitment checks |
| Controlled organisations and high-risk associates | 8.5, 8.6 | Controls implemented in subsidiaries; commitments from associates |
| Gifts, hospitality, donations exposure | 8.7 | Thresholds and approvals scaled to the risk of the counterparty |
| Roles needing awareness | 7.2, 7.3 | Training by exposure, not one course for all |
| Residual risks accepted | 9.3 Management review | Reviewed by top management; reported to the governing body |
The proportionality argument runs one way: from the assessment to the control. Our guide to anti-bribery due diligence covers the first and largest consequence; our guide to gifts and hospitality covers the most visible.
What is a bribery risk assessment under ISO 37001?
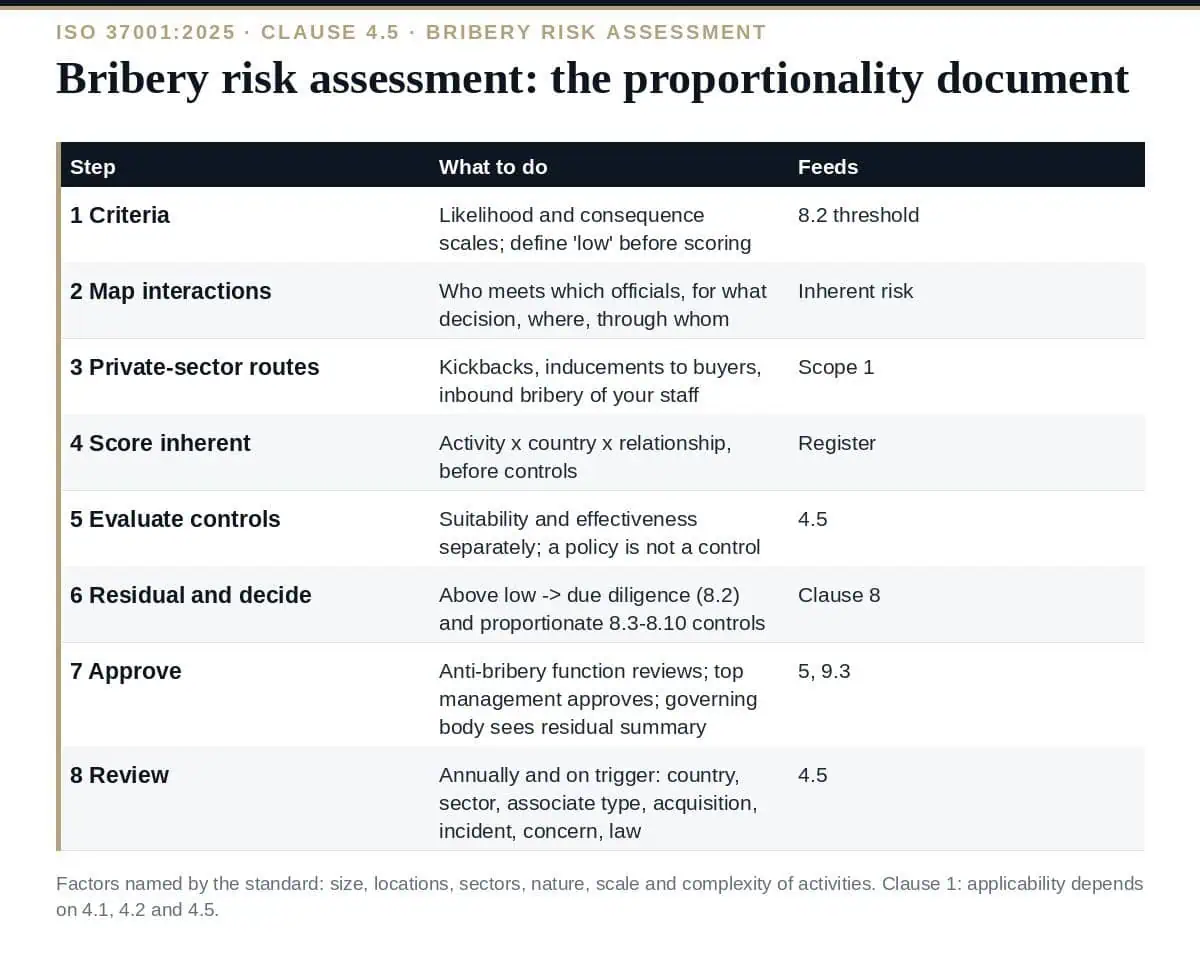
The clause 4.5 requirement to identify the bribery risks the organisation could reasonably anticipate, analyse and evaluate them against its own criteria, assess the suitability and effectiveness of existing controls, and review the assessment regularly. Clause 1 states that the extent to which the standard’s requirements apply depends on it.
How is it different from the enterprise risk register?
It is specific to bribery — by and of the organisation, its personnel and its business associates — and it is organised by activity, country, transaction and relationship rather than by strategic objective. ISO 31000 supplies the vocabulary; the content is anti-bribery.
What counts as low risk?
Whatever the organisation’s documented criteria say, set before scoring and consistent with the anti-bribery policy. Low is the threshold that determines whether due diligence under 8.2 applies, so it has to be defensible.
How often should it be reviewed?
Regularly — annually is the common cycle — and on significant change: a new country, sector, product, business associate type, an acquisition, an incident, a concern raised or a change in law.
Who should own it?
The anti-bribery function (3.8) runs it with input from sales, procurement, finance, HR and operations; top management approves it; the governing body sees the residual-risk summary.
Build the bribery risk assessment before any control: define the criteria and the meaning of low, map the interactions with officials and the private-sector routes, score inherent risk by activity, country and relationship, evaluate the controls honestly, and let the residual scores decide the due diligence, the financial and non-financial controls and the training. Then review it on every change, because under ISO 37001 the assessment is not a record of the system — it is the reason the system looks the way it does.
The Bribery Risk Assessment Methodology and Workbook — criteria, scales, the interaction map, inherent and residual scoring and the control-effectiveness column — and the registers it drives are in the ISO 37001 Anti-Bribery Toolkit, or start with the free templates.


September 20, 2026

September 19, 2026

September 19, 2026

September 19, 2026

September 19, 2026

