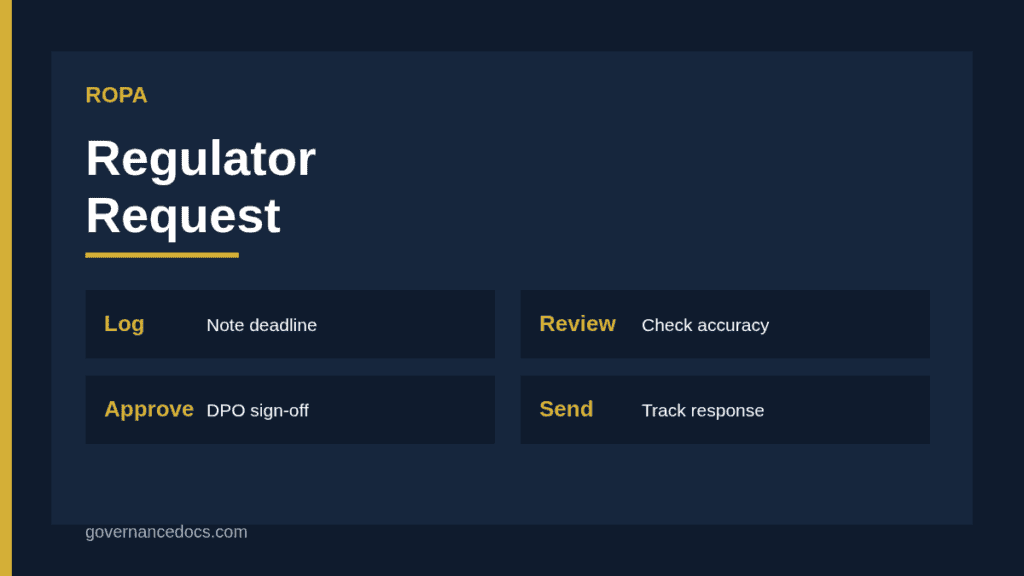
A ROPA regulator request is one of the few moments when your records of processing are read by someone who did not write them. Article 30(4) of the GDPR says the controller or processor must make the record available to the supervisory authority on request, and a ROPA regulator request often arrives at the start of an investigation, an audit or a complaint follow-up. The organizations that cope well are the ones whose records were already accurate before the letter landed.
This guide explains what a ROPA regulator request usually asks for, how to prepare your records before it happens, how to respond when it does and which mistakes turn a routine request into a wider inquiry. It is general information, not legal advice, so check the detail with your data protection officer or counsel.
What a ROPA regulator request is and why it happens
Under Article 30, most controllers and processors must keep written records of their processing activities, and those records must be available to the supervisory authority when asked. A ROPA regulator request is simply that ask. It might be a standalone letter, a questionnaire that arrives after a personal data breach, or a document request inside a wider investigation.
Regulators use records of processing as a map. They show what data you hold, why, who receives it and how long you keep it, so a regulator can decide where to look next. If you are new to the document itself, our guide to a worked ROPA example shows what a complete entry looks like.
The request does not mean you did something wrong. Many authorities ask for the record as a first step because it is the fastest way to understand an organization. Treat it as a routine but serious obligation, and answer it completely and on time.
What the regulator will look for in your records
Read your own record the way an outsider would. The regulator will check whether each entry covers the items Article 30 lists: the controller details, purposes, categories of data subjects and personal data, recipients, international transfers, retention periods where possible and a general description of security measures.
Completeness matters, but so does consistency. If your privacy notice says you keep customer data for six years and your record says indefinitely, the mismatch will be noticed. Our note on ROPA retention periods explains how to keep the two aligned, and international transfers in the ROPA covers the entries regulators often question.
Stage
What you do
Owner
Receive
Log the request, note the deadline and identify the sender
Privacy team
Scope
Confirm exactly which records or period are requested
DPO
Verify
Check each entry against reality with process owners
Process owners
Approve
Review and sign off the version to be sent
DPO or counsel
Submit
Send through the agreed channel and keep a copy
Privacy team
Free ROPA template and builder
Could you hand your records of processing to a regulator tomorrow?
Check whether Article 30 applies to you, add your processing activities from a library organized by department, complete every Article 30 content, and see which activities are missing a lawful basis, a transfer safeguard, a DPIA or an LIA. Free, with a record score and findings.
The best response starts months earlier. Keep the record current, give every entry an owner and date each review. A record that was last touched at launch is the most common weakness, and it is easy to avoid with a simple ROPA review process.
A few habits make a ROPA regulator request far easier to handle:
Name an owner. One person or team is responsible for the record and for receiving any request.
Review on a schedule. A quarterly or half-yearly review with sign-off from process owners keeps entries accurate.
Link to evidence. Each entry should point to the notice, contract or system that supports it.
Keep version history. You should be able to show what the record said at a given date.
Map the data first. A record built from real data flows is more reliable, so see GDPR data mapping if yours was written from memory.
How to respond to a ROPA regulator request step by step
Start by logging the request and its deadline. Confirm what is being asked for, because some requests cover the whole record and others only a period or business area. If anything is unclear, ask the authority rather than guess.
Next, verify before you send. Give each process owner their entries and ask them to confirm they are accurate today. Correct genuine errors, but do not quietly rewrite history: keep the earlier version and note the date of the correction, so you can explain the change if asked.
Then have the DPO or counsel approve the final version. Send it through the channel the authority specified, keep a copy of exactly what you sent and diarise any follow-up. A calm, complete and timely response is the goal. Rushed edits that make the record look tidier than the reality tend to backfire.
Special cases that complicate a response
Some situations need extra thought. If you act as a processor, your record covers the processing you do for each controller, and you may need to inform them. Our guide to controller and processor records explains the difference. Joint arrangements add another layer, covered in joint controller records.
If the record includes HR processing or special category data, check that the descriptions are accurate but not more detailed than needed. Security measures should be described in general terms, as our page on ROPA security measures explains, so the record does not become a blueprint for attackers.
The small-organization exemption is narrower than many people believe. It is worth checking the ROPA exemption before you assume you were never required to keep a record.
Mistakes that turn a request into a bigger problem
Most difficulties are avoidable. The record is missing entirely, or it exists but covers only marketing. Entries use vague purposes such as “business operations”. Recipients are listed as “third parties” with no names or categories. Retention is blank. Or the record was updated in a panic the day the letter arrived, leaving a history that does not match your practice.
Another frequent problem is inconsistency between documents. Your record, your privacy notice, your DPIAs and your contracts should tell the same story. When they do not, the regulator will ask which is true. Build a short consistency check into every review.
A short worked scenario
Imagine a mid-sized retailer receives a letter from its supervisory authority following a customer complaint. The letter asks for the record of processing and gives a deadline of four weeks. On day one the privacy lead logs the letter, confirms the scope with the DPO and sends each process owner a list of their entries with a five-day deadline to confirm or correct them.
Marketing finds that a loyalty-programme entry lists a data processor that was replaced last year. HR finds that retention for unsuccessful applicants has been shortened, but the record still shows the old period. Both corrections are made, dated and explained in a short change note. The DPO reviews the final version against the privacy notice, spots one further mismatch and fixes it before approval.
The package that goes to the authority contains the record, a short covering letter and a named contact. The retailer keeps an identical copy, the change note and the email trail. Nothing dramatic happened, but the organization could show that its record was maintained, reviewed and owned, which is exactly what the authority wanted to see.
A quick readiness checklist
Before any letter arrives, ask whether you can answer yes to each of these questions: is there a single current record, does every entry have an owner and a review date, can you show earlier versions, do the entries match your privacy notice and contracts, and does someone know who receives external requests? If any answer is no, fix that first. It takes far less time than repairing the record under a deadline.
Where to read the legal text
The obligation comes from Article 30 of the GDPR, which sets out the content of the record and the duty to make it available to the supervisory authority. Your national authority may publish its own template or guidance, so check its website for expectations that go beyond the regulation.
Getting a ready structure for the record
If you would rather start from a complete layout than a blank spreadsheet, the ROPA Report and Workbook provides a structured record with the Article 30 fields, guidance notes and a workbook you can maintain. Whichever format you choose, the test for a ROPA regulator request is whether an outsider could understand your processing from the record alone.
ROPA regulator request FAQ
How long do we have to respond to a ROPA regulator request?
The deadline is set by the authority in its letter, so read it carefully and diarise it on the day it arrives. If you need more time, ask early and explain why.
Do we have to send the whole record?
Send what is requested. If the request is broad, provide the full record. If it is limited to a business area or period, confirm the scope in writing and answer accordingly.
Can we fix errors before sending the record?
You can correct genuine inaccuracies, but keep the earlier version and record when and why the change was made. Never alter the record to hide past gaps.
Who should sign off the response?
The DPO or privacy lead should approve it, with legal counsel involved if there is any wider investigation. A named person should own the submission.
Does a ROPA regulator request mean we are under investigation?
Not necessarily. Requests are often routine, but the answer helps the authority decide whether to ask more, so accuracy and completeness are important.