-
×
 ISO 27001 Toolkit - 165 Comprehensive Templates
1 × $99.00
Subtotal: $99.00

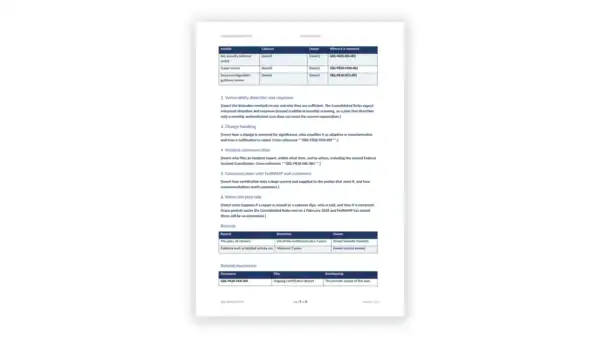
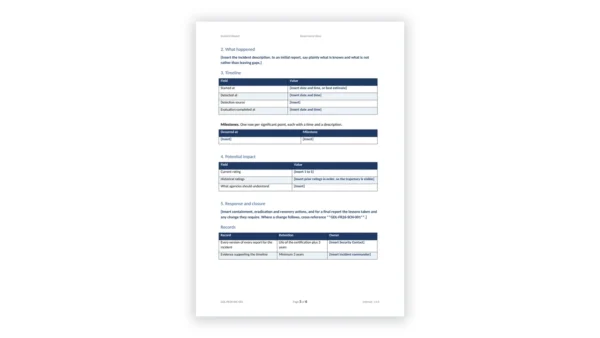
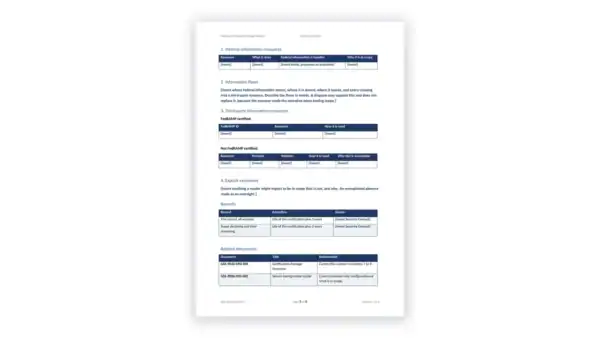
FedRAMP Toolkit: 52 editable templates rebuilt for the FedRAMP Consolidated Rules for 2026. Certification Package Overview, Security Decision Record, Accepted Weaknesses List, Ongoing Certification, 8 JSON companions on FedRAMP’s own schemas, and the full NIST SP 800-53 Rev 5 baseline set: 18 control-family policies, plans, assessment reports and workbooks. Rev5 and 20x. Instant download.
$99.00
✓ In stock — instant download after checkout
FedRAMP’s Consolidated Rules for 2026 took effect on 4 July 2026. They retired the System Security Plan in favour of a Certification Package Overview and a Security Decision Record, eliminated the Plan of Action and Milestones in favour of an Accepted Weaknesses List, turned Continuous Monitoring into Ongoing Certification, made the 20x path generally available, and require the core artifacts in JSON against FedRAMP’s published schemas as well as in a document a person can read.
New Rev5 applications must follow the rules from 1 January 2027; every grace period ends on 1 February 2028. A template pack built on the old package model answers questions FedRAMP has stopped asking.
The FedRAMP Toolkit was rebuilt in September 2026 for those rules. It is 52 editable templates, 47 Word documents and 5 Excel workbooks, in 11 folders, with 8 JSON companion files generated from FedRAMP’s schemas of 24 June 2026, and it serves both the Rev5 and the 20x certification paths, which now share the same rulesets and the same NIST SP 800-53 Rev 5 control baseline.
The 15 documents written for the 2026 rules in the FedRAMP Toolkit carry the FedRAMP rule identifiers they answer: 25 rule identifiers across 14 rulesets (AFC, CCM, CDS, CMU, CPO, FRC, IEC, IVV, MAS, SCG, SCN, SDR, VDR, VER). Each document states them in its control table and in a Rules basis panel that says what the rule requires.
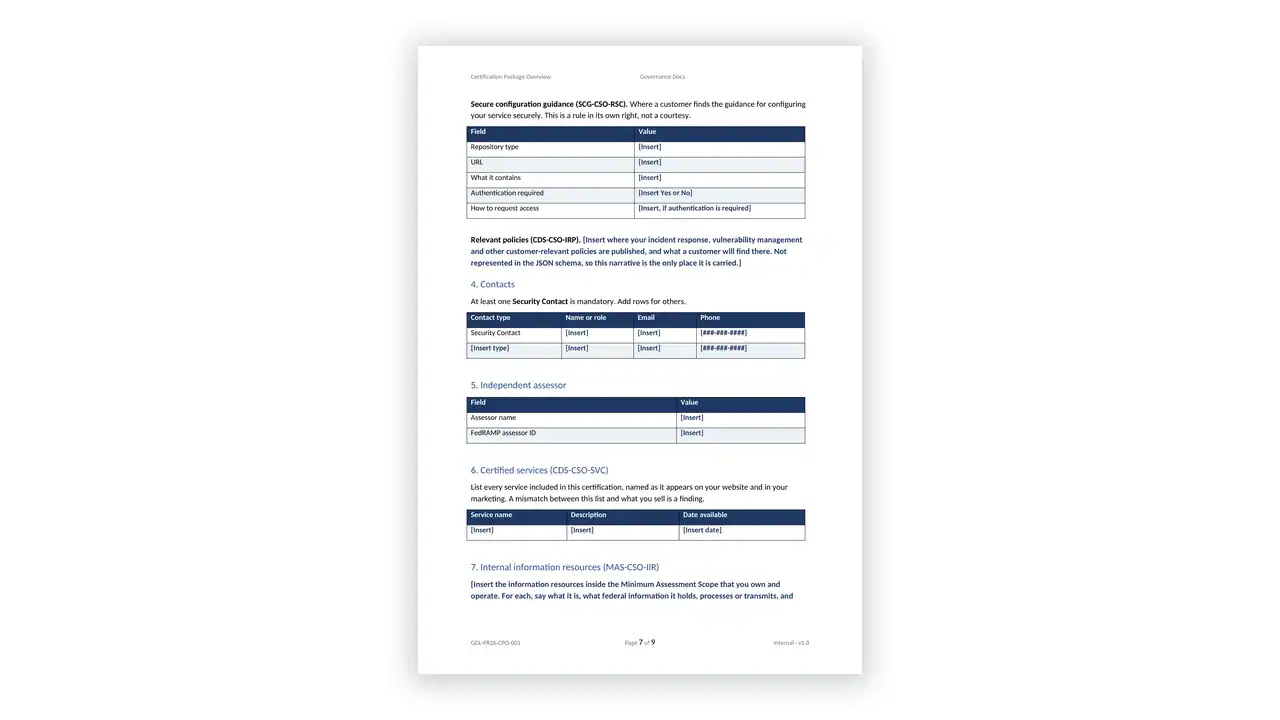
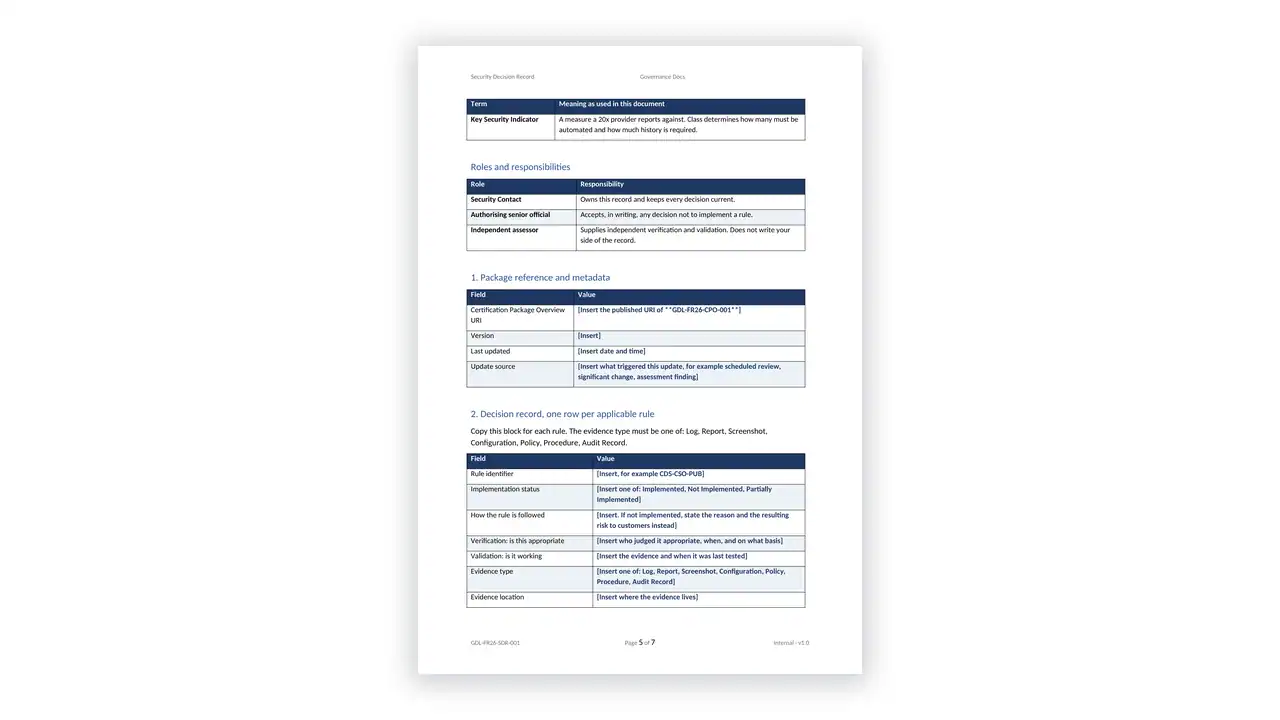
FedRAMP requires the Certification Package Overview and the Security Decision Record in human-readable form and in JSON, with OSCAL optional. Eight documents in the FedRAMP Toolkit ship with a JSON companion: a typed template generated from the published schema of the same name, every property present, enumerated fields seeded with a legal value, and dates and URIs given the right placeholder shape. Each was validated structurally against its schema (version 0.1.4, dated 24 June 2026). Fill the Word document, copy each value to the key of the same name, validate, publish.
The rules changed the package, not the control baseline. The FedRAMP Toolkit carries a full worked example of the NIST SP 800-53 Rev 5 Moderate baseline material for a fictional provider, Acme Cloud Services and its AcmeCloud Government Platform, updated for the 2026 terminology and pointed at the new artifacts rather than at an SSP.
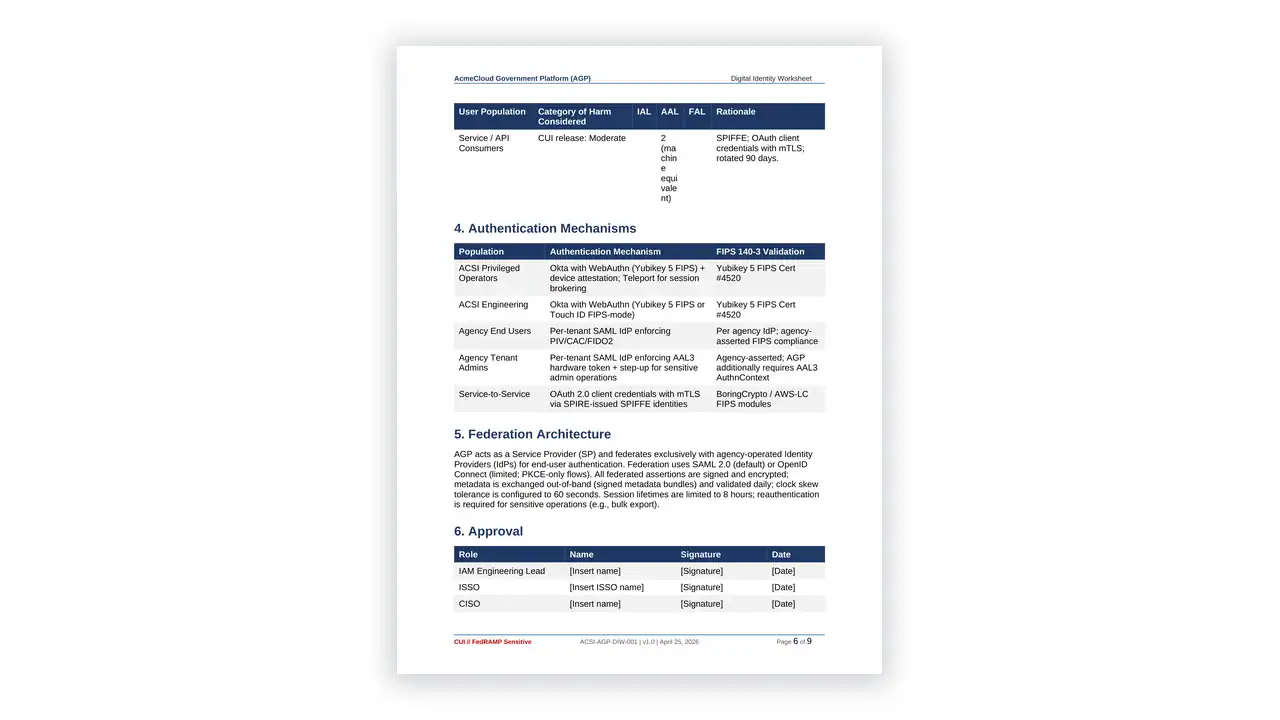
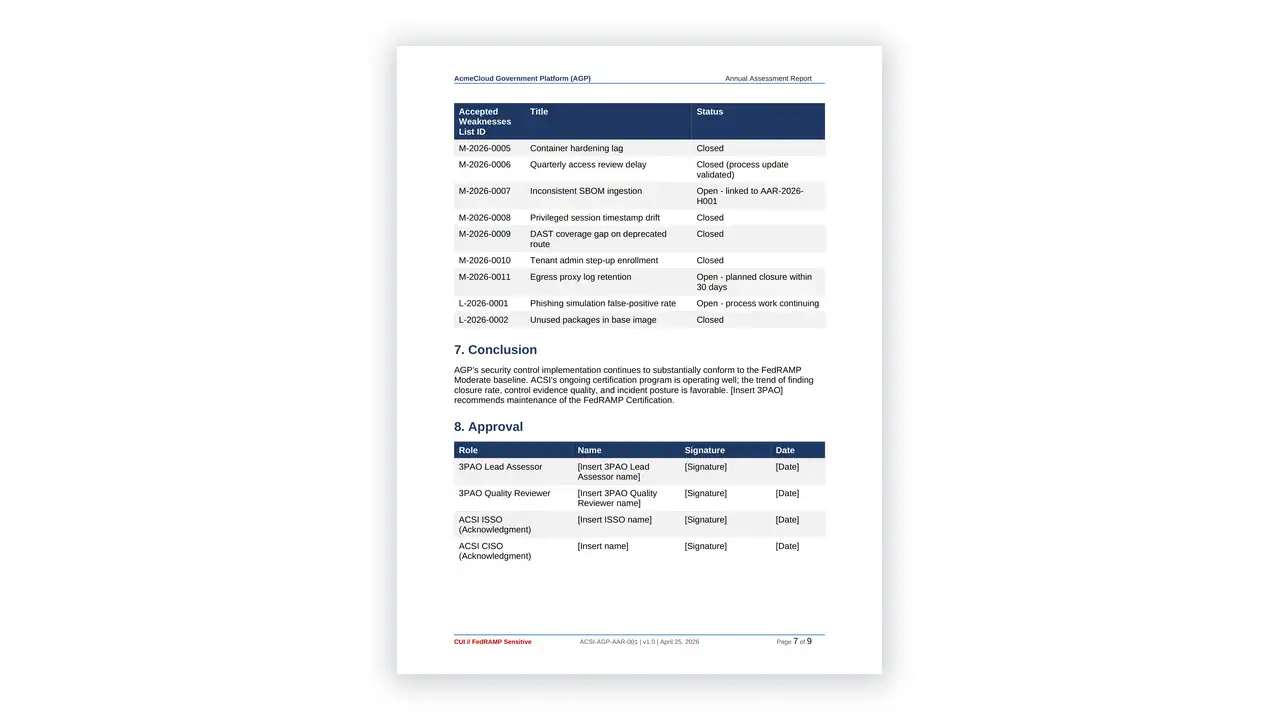
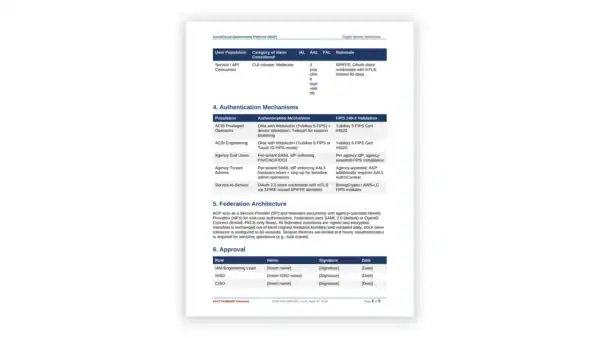
The FedRAMP Toolkit’s baseline half holds 18 control-family policies from Access Control to Supply Chain Risk Management; FIPS 199 categorization, the Privacy Threshold Analysis and Privacy Impact Assessment, the Digital Identity Worksheet, Rules of Behavior and User Guide; the Information System Contingency Plan, Incident Response Plan and Configuration Management Plan; the Security Assessment Plan and Report, the Readiness Assessment Report, and the Annual Assessment Plan and Report.
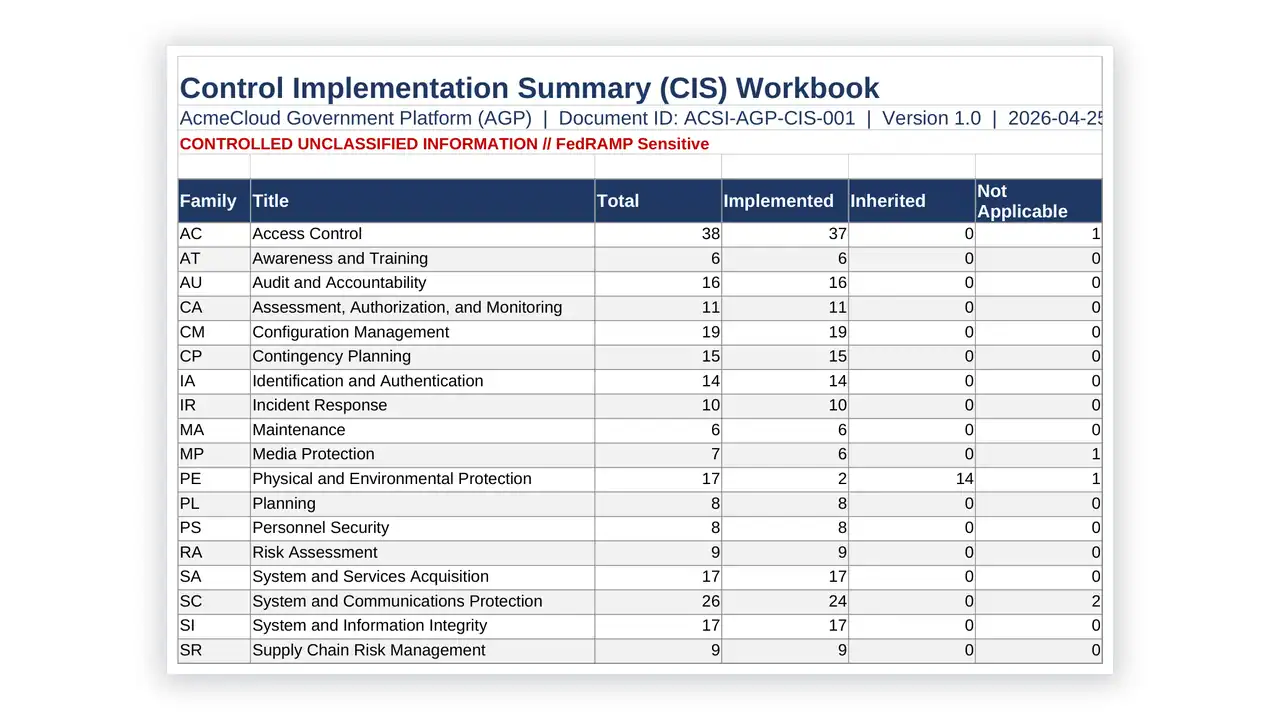
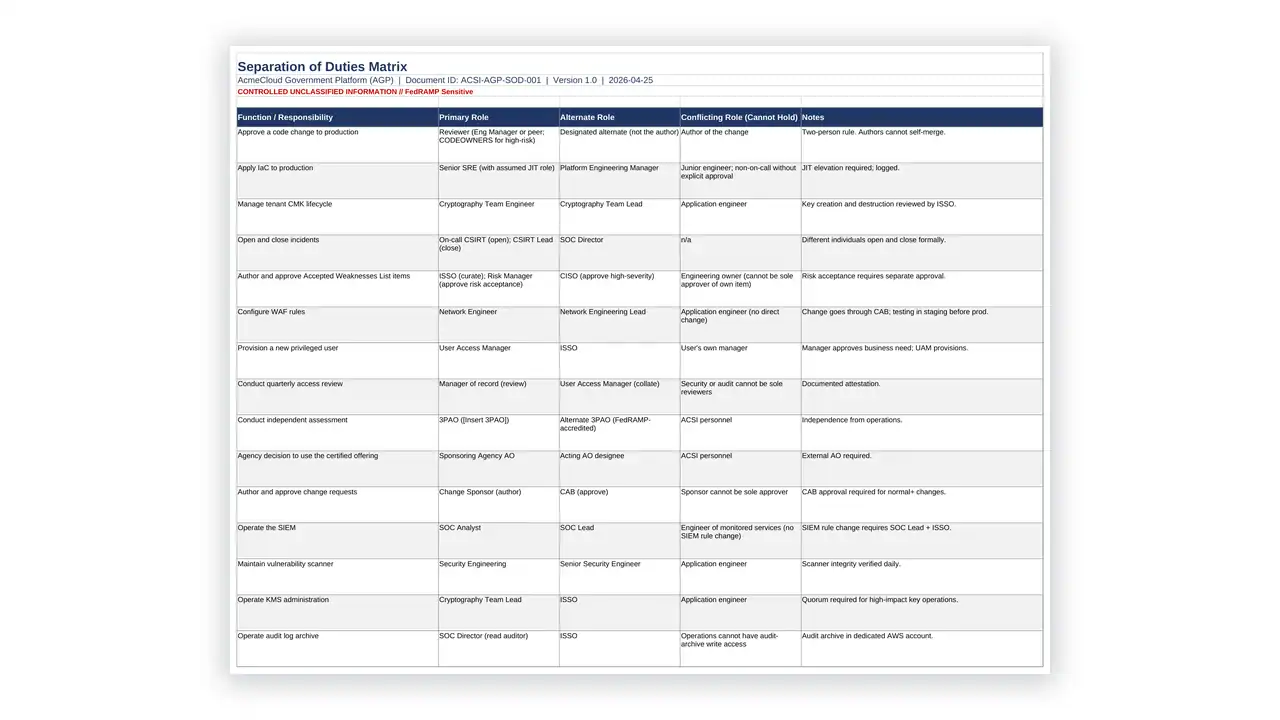
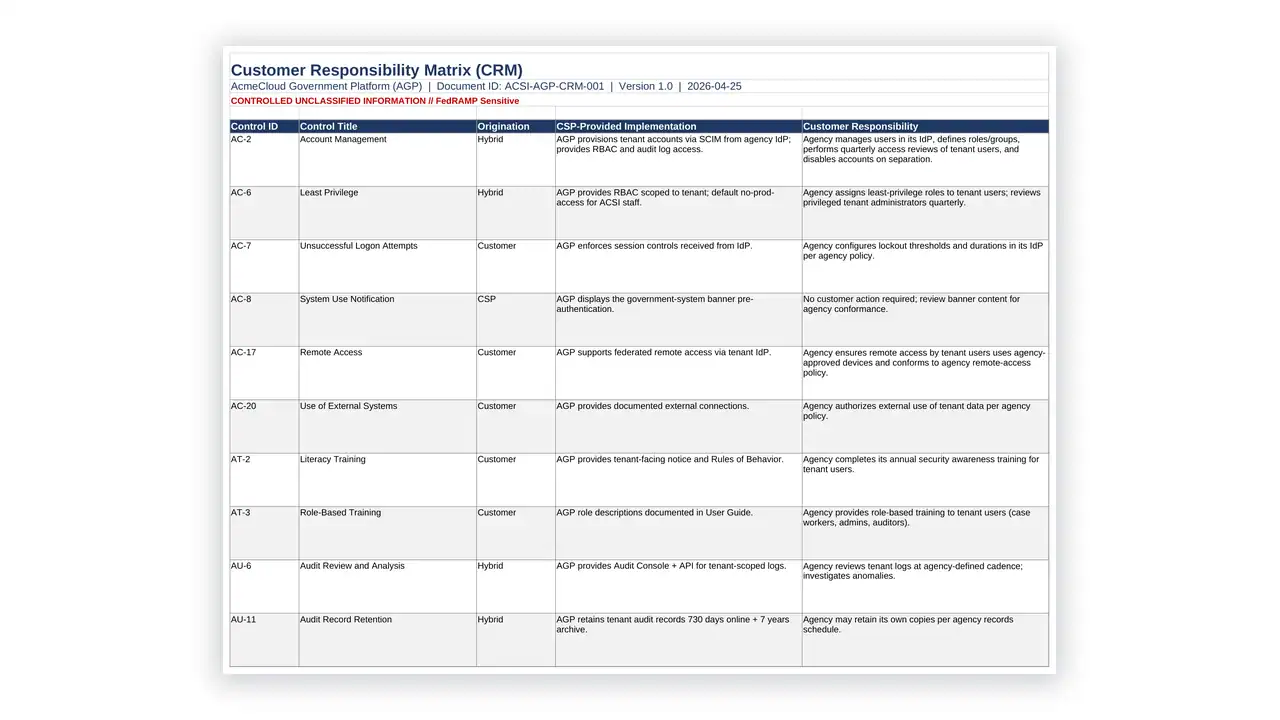
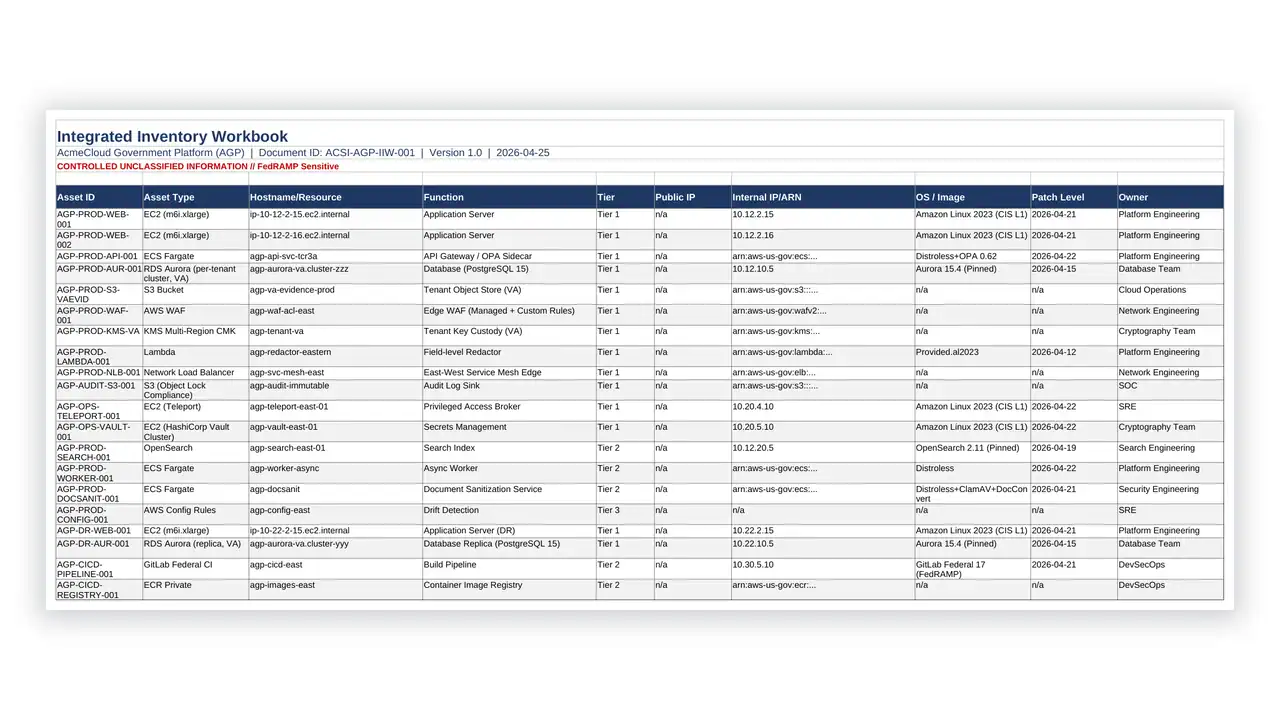
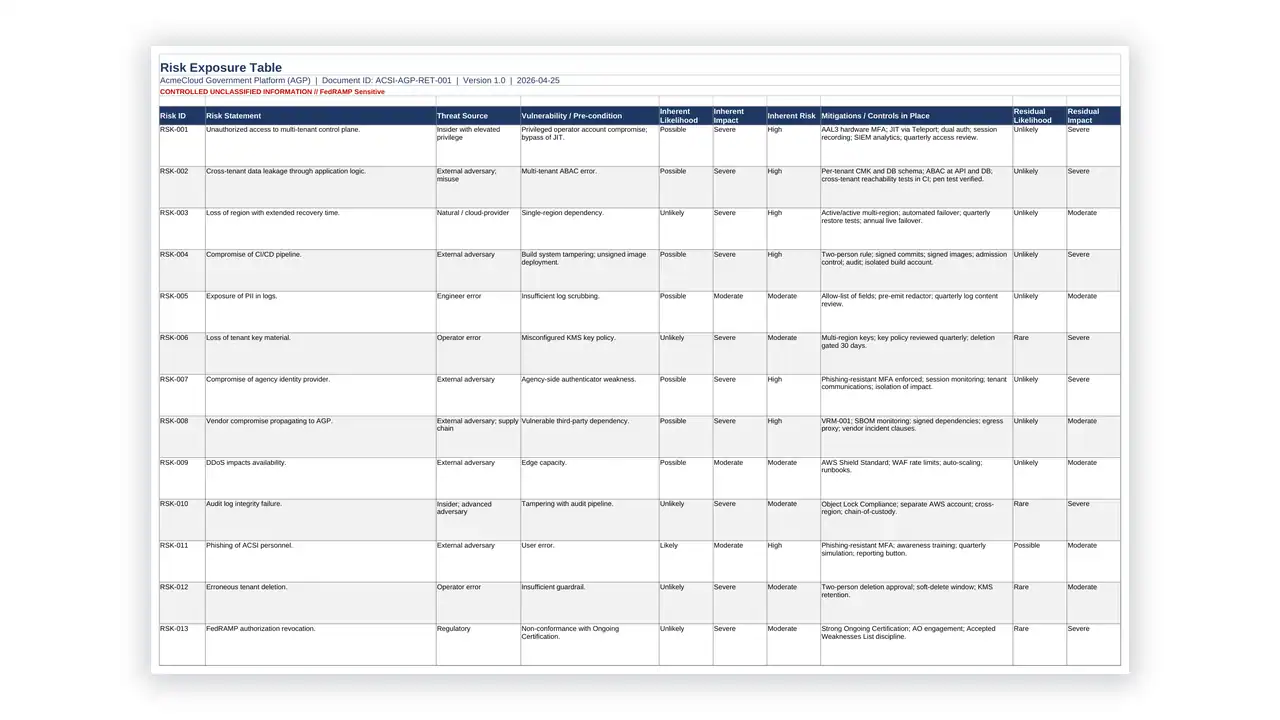
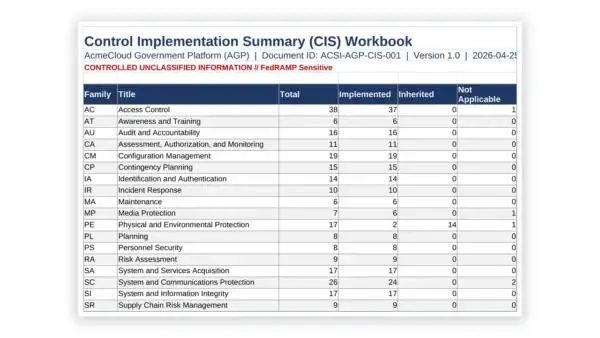
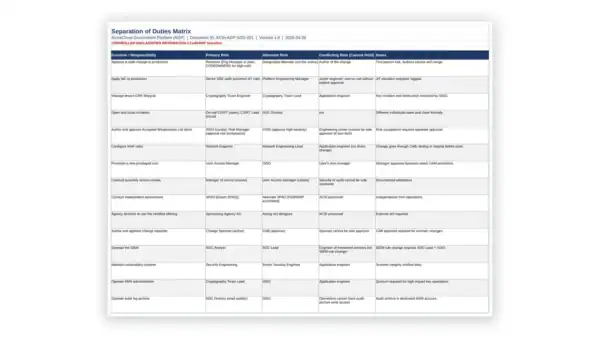
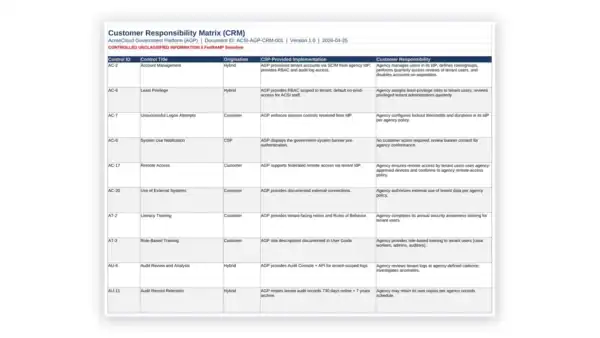
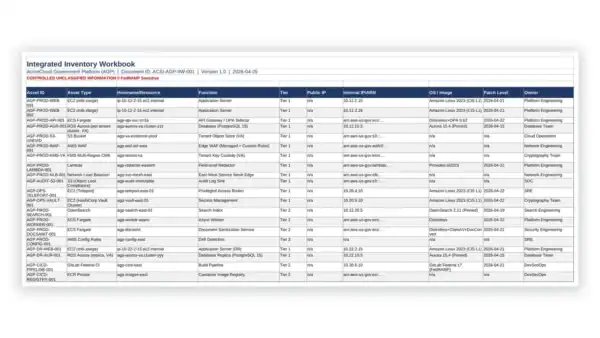
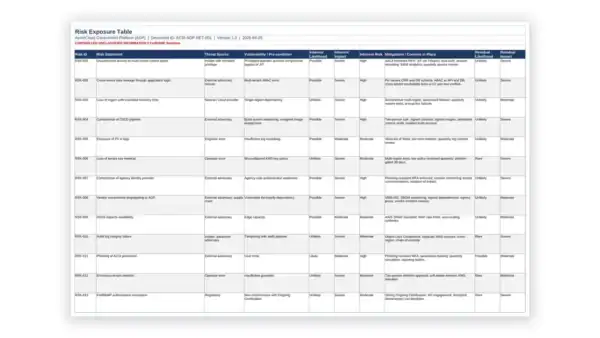
Five workbooks complete the FedRAMP Toolkit: the CIS Workbook, the Customer Responsibility Matrix, the Integrated Inventory Workbook, the Risk Exposure Table and the Separation of Duties Matrix. Every name, date and figure in the example is invented and marked for replacement.
Every rule identifier, artifact name, schema field and deadline in the FedRAMP Toolkit was read on fedramp.gov on 6 September 2026: the Consolidated Rules for 2026, the 11 published JSON schemas, and the deadlines page. The How to Use guide reproduces the deadline table and tells you to check the page before you commit to a date. Where the rules leave a choice to the provider, the pack says so rather than inventing a FedRAMP figure.
The NIST SP 800-53 Toolkit carries the control catalogue itself for organisations outside FedRAMP; the CMMC Toolkit serves defence contractors under NIST SP 800-171; the NIST CSF 2.0 Toolkit is the outcome-based framework many agencies ask for alongside. The FedRAMP Toolkit is the certification package layer for cloud service providers selling to the U.S. federal government.
Every file in the FedRAMP Toolkit, by folder. Word documents marked (+ JSON) ship with their schema companion.
| Folder | Files | What it holds |
|---|---|---|
| 00 Programme | 3 | Document index, How to Use guide, Toolkit FAQ |
| 01 Certification Package | 4 | Certification Package Overview and Security Decision Record, each with its JSON companion |
| 02 Organizational Requirements | 1 | The register of provider-set parameters |
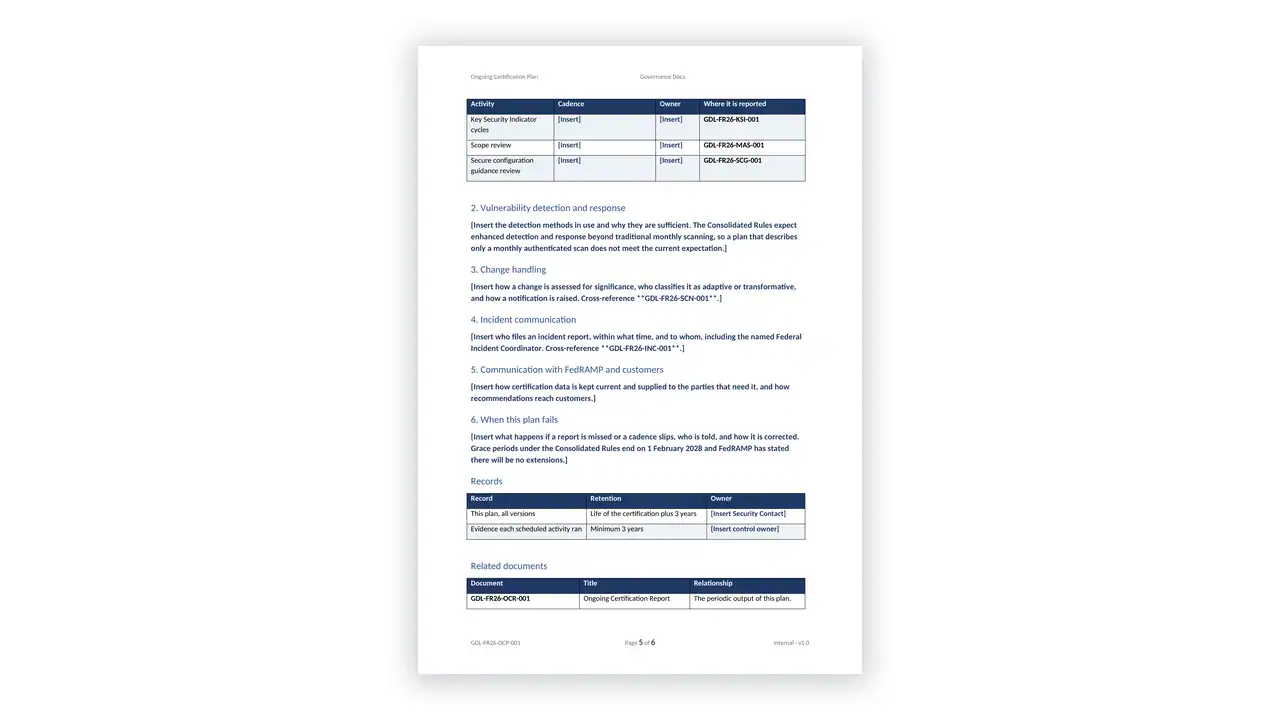
| 03 Ongoing Certification | 7 | Accepted Weaknesses List, Ongoing Certification Plan and Report, Significant Change Notification, with JSON companions |
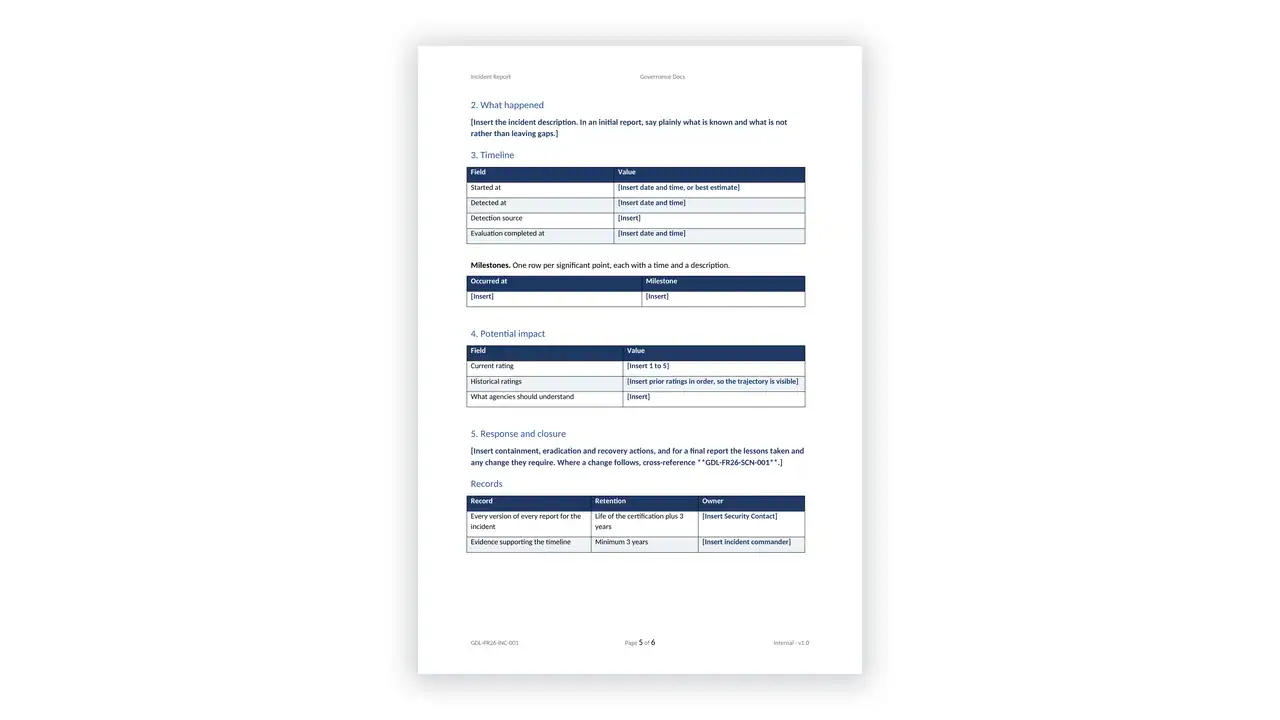
| 04 Vulnerability and Incident | 6 | Incident Report, Vulnerability Detail Report, Historical VER Activity Record, with JSON companions |
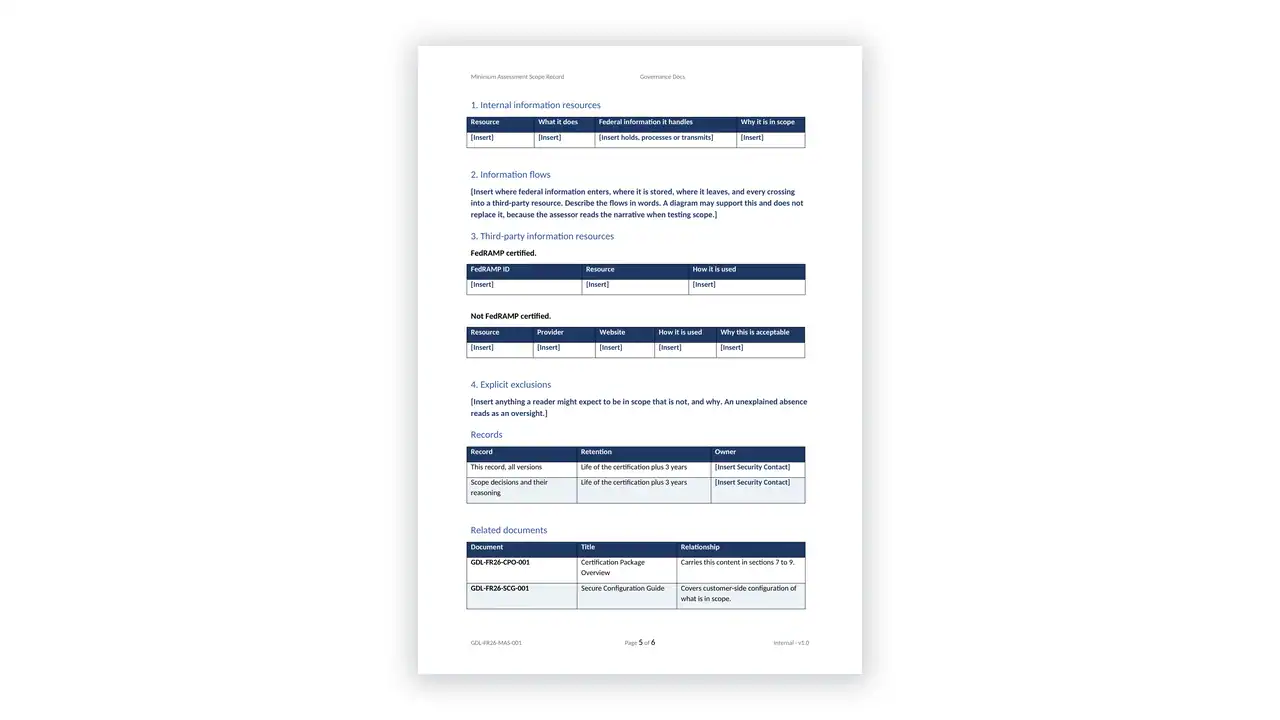
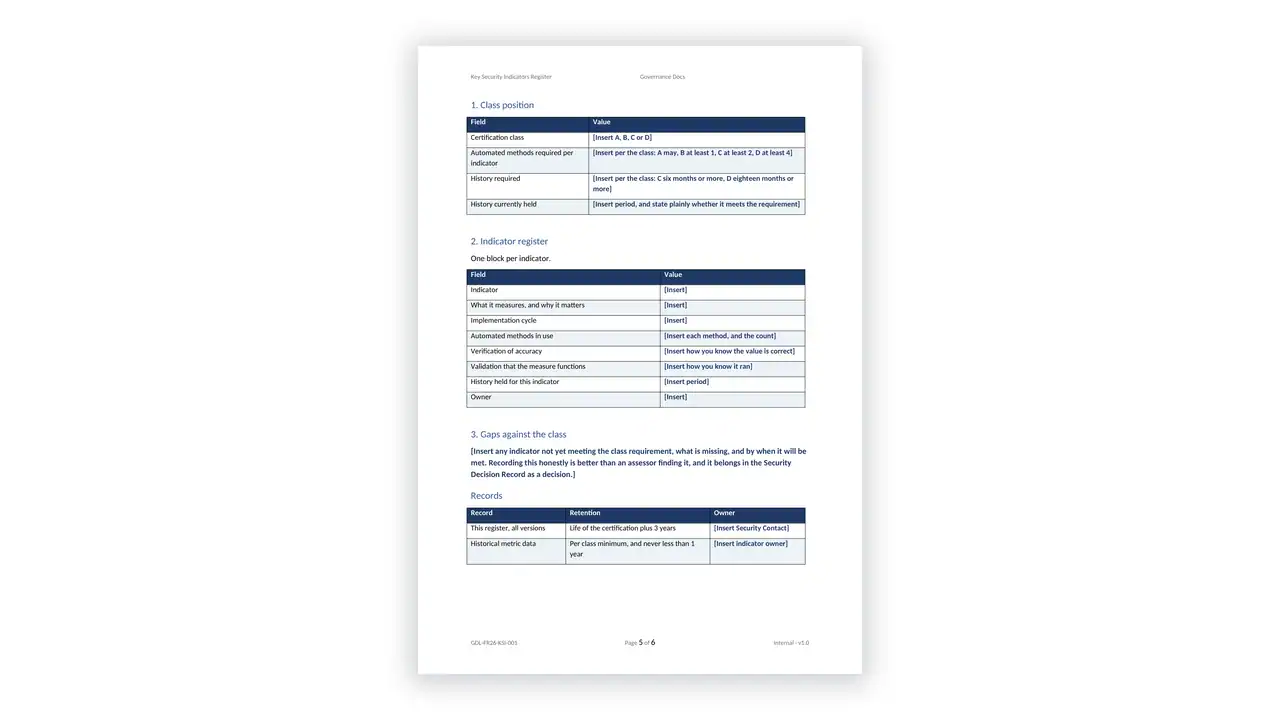
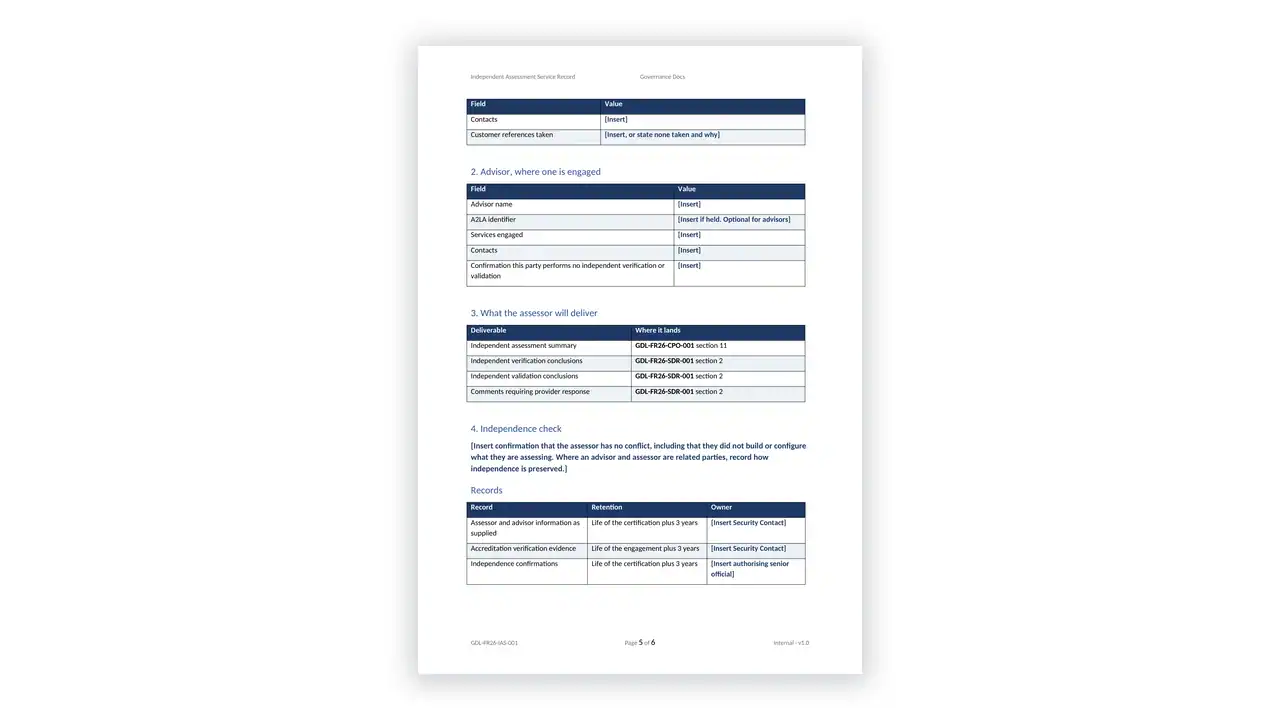
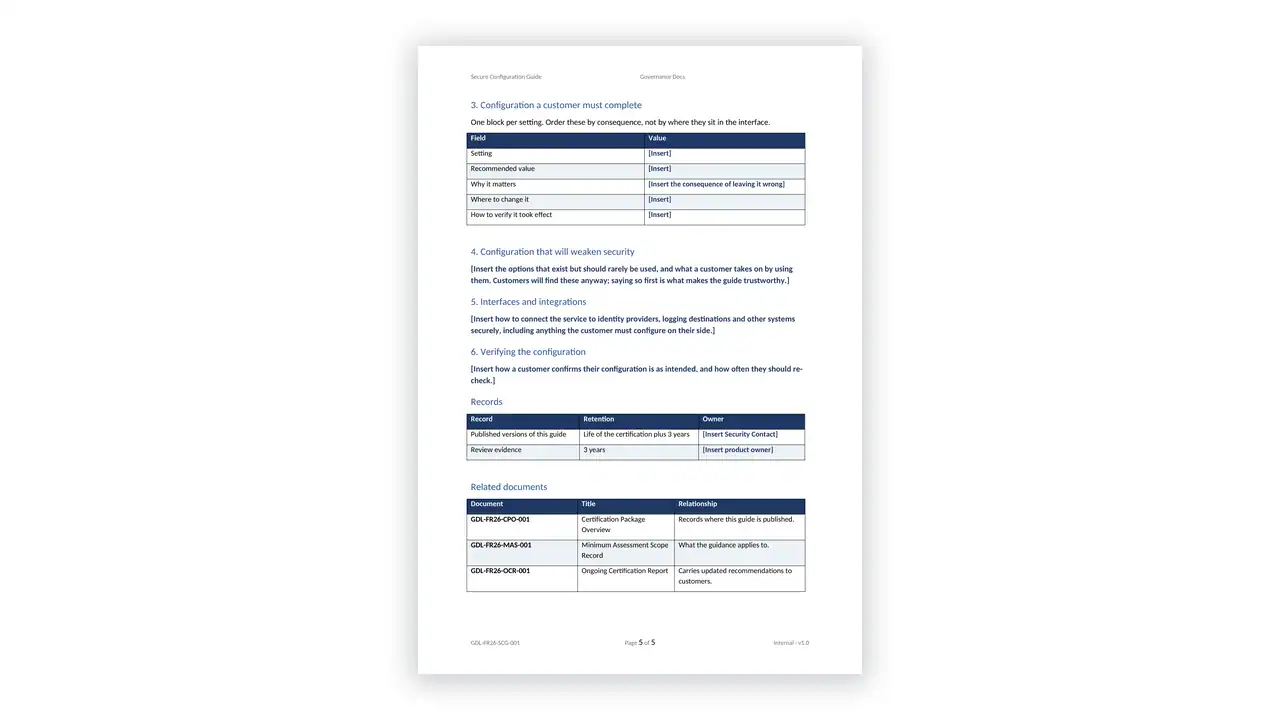
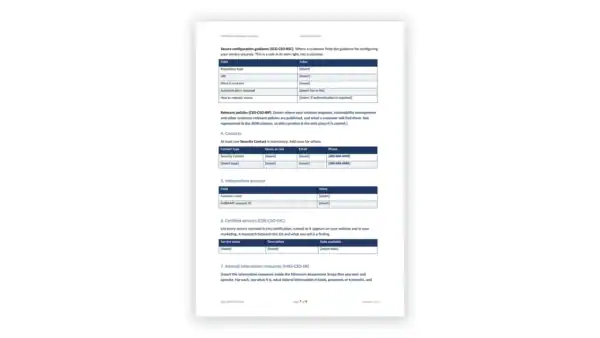
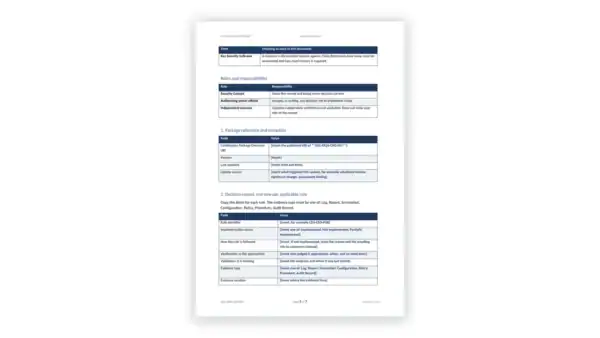
| 05 Scope and Assurance | 4 | Independent Assessment Service Record, Key Security Indicators Register, Minimum Assessment Scope Record, Secure Configuration Guide |
| 06 Categorization and Privacy | 6 | FIPS 199, PTA, PIA, Digital Identity Worksheet, Rules of Behavior, User Guide |
| 07 Operational Plans | 3 | Contingency, incident response and configuration management plans |
| 08 Assessment | 5 | Security Assessment Plan and Report, Readiness Assessment Report, Annual Assessment Plan and Report |
| 09 Workbooks | 5 | CIS Workbook, Customer Responsibility Matrix, Integrated Inventory Workbook, Risk Exposure Table, Separation of Duties Matrix |
| 10 Control Family Policies | 18 | Eighteen NIST SP 800-53 Rev 5 control-family policies, AC to SR |
00 Programme
01 Certification Package
02 Organizational Requirements
03 Ongoing Certification
04 Vulnerability and Incident
05 Scope and Assurance
06 Categorization and Privacy
07 Operational Plans
08 Assessment
09 Workbooks
10 Control Family Policies
Sorry, no reviews match your current selections
 FedRAMP Toolkit – 52 Templates for the FedRAMP Consolidated Rules 2026$99.00


This toolkit makes the authorization process much easier to navigate with clear and practical templates. It is a valuable resource for keeping compliance documentation organized and consistent.