CART
ISO 27017 certification cost is the price of extending an ISO 27001 certificate, not of buying a second one, and that changes every line of the budget. There is no ISO 27017 certificate: the cloud controls are added to the Statement of Applicability, audited as part of the ISO 27001 Stage 1, Stage 2 and surveillance audits, and named in the certificate’s scope statement. So the cost has two halves — the ISO 27001 certification you must already hold or obtain, and the increment the cloud extension adds to implementation, audit days and maintenance. For a small provider that already holds ISO 27001, the increment typically lands between $6,000 and $25,000 in the first year; for one starting from nothing, the ISO 27001 base of $8,000 to $30,000 comes first. This guide breaks the ISO 27017 certification cost into its components, explains how certification bodies price the extra audit time, what the 2026 edition adds to the remapping bill, what adding ISO 27018 alongside costs, and the four places these budgets overrun.
ISO/IEC 27001 is a management system standard with requirements, which is what accredited certification needs. ISO/IEC 27017:2026 is a guidance standard — implementation guidance on the ISO/IEC 27002:2022 controls for cloud services plus a few dedicated cloud controls — and guidance cannot be certified. A certification body therefore audits the cloud controls inside the ISO 27001 audit, where the organisation has declared them applicable in its Statement of Applicability, and records the extension in the scope statement on the ISO 27001 certificate. Any quote for “ISO 27017 certification” is a quote for additional ISO 27001 audit time plus a scope change. Our guide to ISO 27017 covers the standard and the July 2026 edition.
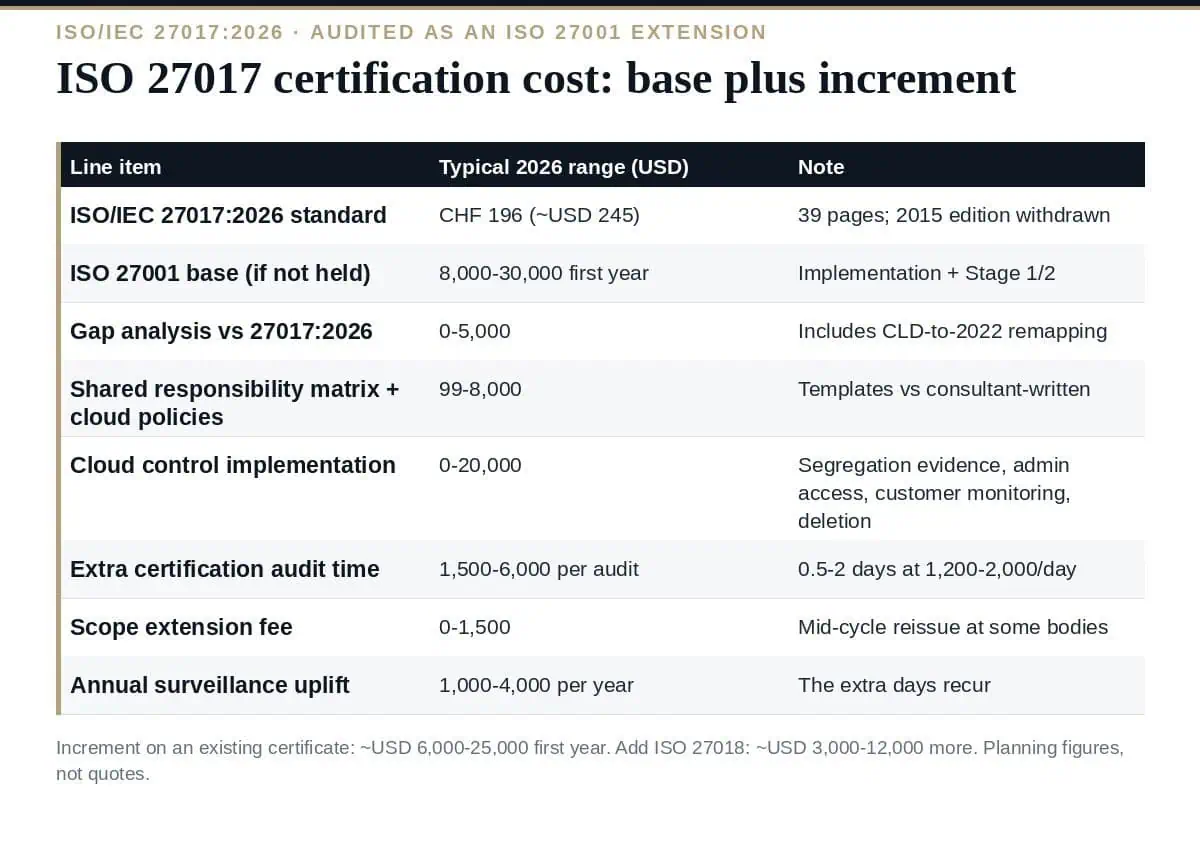
| Line item | Typical 2026 range (USD) | Notes |
|---|---|---|
| ISO/IEC 27017:2026 standard | CHF 196 (about $245) | Second edition, 39 pages, published July 2026; the 2015 edition is withdrawn |
| ISO 27001 base — if not already held | $8,000 to $30,000 first year | Implementation, Stage 1 + Stage 2 audit; see the ISO 27001 certification cost breakdown |
| Gap analysis against 27017:2026 | $0 to $5,000 | Internal, or a consultant day or two; includes the CLD-to-2022 remapping if you had the 2015 edition |
| Shared responsibility matrix and cloud policies | $99 to $8,000 | Template pack against consultant-written; the matrix is the document auditors read first |
| Cloud control implementation | $0 to $20,000 | Tenant segregation evidence, administrator access controls, customer-visible monitoring, asset removal at contract end — the widest item |
| Internal audit of the extension | $1,000 to $3,000 | Extra scope on the annual internal audit |
| Additional certification audit time | $1,500 to $6,000 per audit | Typically 0.5 to 2 extra audit days at $1,200 to $2,000 a day, at Stage 2 and at each surveillance |
| Scope extension fee (existing certificate) | $0 to $1,500 | Some bodies charge for a mid-cycle scope change and certificate reissue |
| Annual surveillance uplift | $1,000 to $4,000 per year | The extra days recur |
The ISO 27017 certification cost rows for audit are labelled typical ranges from certification-body practice; the implementation rows are planning figures, not quotes. Two rules shape them. First, the extra audit time is driven by the number of cloud services in scope and their deployment models, not by headcount — a provider with one SaaS product adds half a day; a provider with IaaS, PaaS and SaaS across three regions adds two. Second, the increment is cheapest when the extension is added at a recertification or at Stage 2 of an initial certification, because the auditor is already on site; a mid-cycle extension audit is a separate visit with its own minimum. Our guide to ISO 27001 certification cost gives the base figures the increment sits on.
ISO 27001 audit time is set from ISO/IEC 27006-1’s tables by the number of people in scope, adjusted for complexity; a sector-specific extension is one of the complexity factors that increases it. In practice bodies quote the extension as additional audit days, and the three questions that set the number are: how many cloud services and deployment models are in scope; whether the organisation is the provider, the customer or both; and how much of the ISO 27002 control set the cloud guidance touches — the 2015 edition supplied guidance on around 37 controls, and the 2026 edition’s guidance is spread across the 27002:2022 set. A provider that arrives with a completed shared responsibility matrix, a Statement of Applicability that already lists the cloud controls with justification, and evidence organised per control keeps the extra days at the bottom of the range.
The 2026 edition adds a line to the ISO 27017 certification cost for existing holders. ISO published the second edition in July 2026 and withdrew the 2015 edition. The CLD identifiers are gone, the structure follows ISO/IEC 27002:2022, and controls were merged, removed and added. For a provider already holding the extension, that is a remapping project: every policy and the SoA that cited CLD.6.3.1, CLD.9.5.1 and the rest has to be re-keyed to the 2022 numbering and the dedicated cloud controls, and the certification body will expect the new edition at the next audit. Budget one to three consultant days or the equivalent in staff time, and expect the auditor to sample the remapping. Because ISO 27017 is not certified in its own right there is no formal transition period; the date is whichever the certification body sets.
Providers that process customer personal data usually add ISO/IEC 27018:2025 in the same audit, and the marginal cost is smaller than the first extension: the same Stage 2 or surveillance visit, another half to one audit day, and the Annex A privacy controls — sub-processor register, disclosure-request log, breach notification, return and disposal, location of PII. Planning figure: $3,000 to $12,000 in the first year on top of the 27017 increment, most of it implementation. Our guide to ISO 27017 vs ISO 27018 covers when both are needed.
How much does ISO 27017 certification cost?
As an extension to an existing ISO 27001 certificate, typically $6,000 to $25,000 in the first year — gap analysis, cloud control implementation, the shared responsibility matrix, 0.5 to 2 extra audit days per audit, and a possible scope-change fee — then $1,000 to $4,000 a year in surveillance uplift. Without ISO 27001, add its $8,000 to $30,000 base first.
Is there a separate ISO 27017 certificate?
No. ISO 27017 is guidance, not a management system standard; certification bodies audit its controls inside the ISO 27001 audit and name the extension in the certificate’s scope statement.
How many extra audit days does it add?
Usually half a day to two days per audit, depending on how many cloud services and deployment models are in scope and whether you are provider, customer or both.
Does the 2026 edition cost more?
It costs a remapping project for existing holders — the CLD identifiers are gone and the structure follows ISO/IEC 27002:2022 — typically one to three consultant days or equivalent staff time; there is no formal transition period because the extension is not certified in its own right.
What does ISO 27018 add?
Another half to one audit day in the same visit plus the Annex A privacy controls; plan $3,000 to $12,000 in the first year on top of the 27017 increment.
Budget ISO 27017 certification cost as an increment on ISO 27001: the standard, a gap analysis against the 2026 edition, the shared responsibility matrix and cloud controls, half a day to two days of extra audit time at each visit, and a surveillance uplift every year — timed to a scheduled audit and scoped to the services you sell. The overruns are engineering, not paperwork: segregation evidence, customer-visible monitoring and deletion at contract end.
The Shared Responsibility Matrix Template, the Shared Roles and Responsibilities Policy, the Cloud Service Agreement Security Schedule and the cloud control procedures mapped to both the 2026 and 2015 editions are in the ISO 27017 & ISO 27018 Cloud Toolkit, or start with the free templates.


September 20, 2026

September 19, 2026

September 19, 2026

September 19, 2026

September 19, 2026

