CART
BSI C5 attestation cost is not published by anyone — not by the BSI, which takes no part in selecting auditors or checking reports, and not by the audit firms, which quote each engagement — so the honest way to price it is the way the engagement is actually built: assessor days, at the rates public accountancy firms charge for ISAE 3000 assurance work, multiplied by the scope the provider chooses. A C5:2026 examination covers 168 criteria under 17 objectives, in basic and optionally additional subcriteria, plus six general conditions and a system description, as a type 1 (design, point in time) or type 2 (operating effectiveness over a period).
Scope, type, the number of services and locations, and how much of the evidence already exists from an ISO 27001 ISMS or a SOC 2 programme decide the days. This guide gives our estimate — labelled as such throughout — for the audit fee by provider profile, the internal cost that exists whichever firm you hire, the readiness and remediation lines that most first-year budgets miss, a worked example, and the decisions that move the total.
| Driver | Effect | What you control |
|---|---|---|
| Type 1 or type 2 | Type 2 tests operating effectiveness across a period with sampling; roughly 1.5–2× the type 1 days | Type 1 first where operating history is short; type 2 when customers require it — and § 393 SGB V healthcare customers do, from 1 July 2025 |
| Basic only, or basic plus additional criteria | Each additional sharpening or complementing subcriterion in scope is tested; a full additional set adds a third or more to the days | A market decision, stated in the report |
| Number of cloud services and their complexity | Each service has its own system description and control mapping; shared platform controls are tested once | Scoping the services that need the report |
| Locations and subservice organisations | Data centres and subcontractors in scope add inspection and reliance work | Consolidation; carve-out or inclusive method for subservice organisations |
| Existing assurance | An ISO 27001-certified ISMS (required by OIS-01.01B) and a SOC 2 type 2 shorten the fieldwork; BSI recommends aligning the audits | Running C5 on the same evidence base and period |
| Evidence readiness | An auditor who has to find evidence bills the finding time | Subcriterion-level control mapping with evidence attached before fieldwork |
| Auditor | Big Four versus specialist assurance firms; German-market experience | Tender to two or three firms with C5 track records |
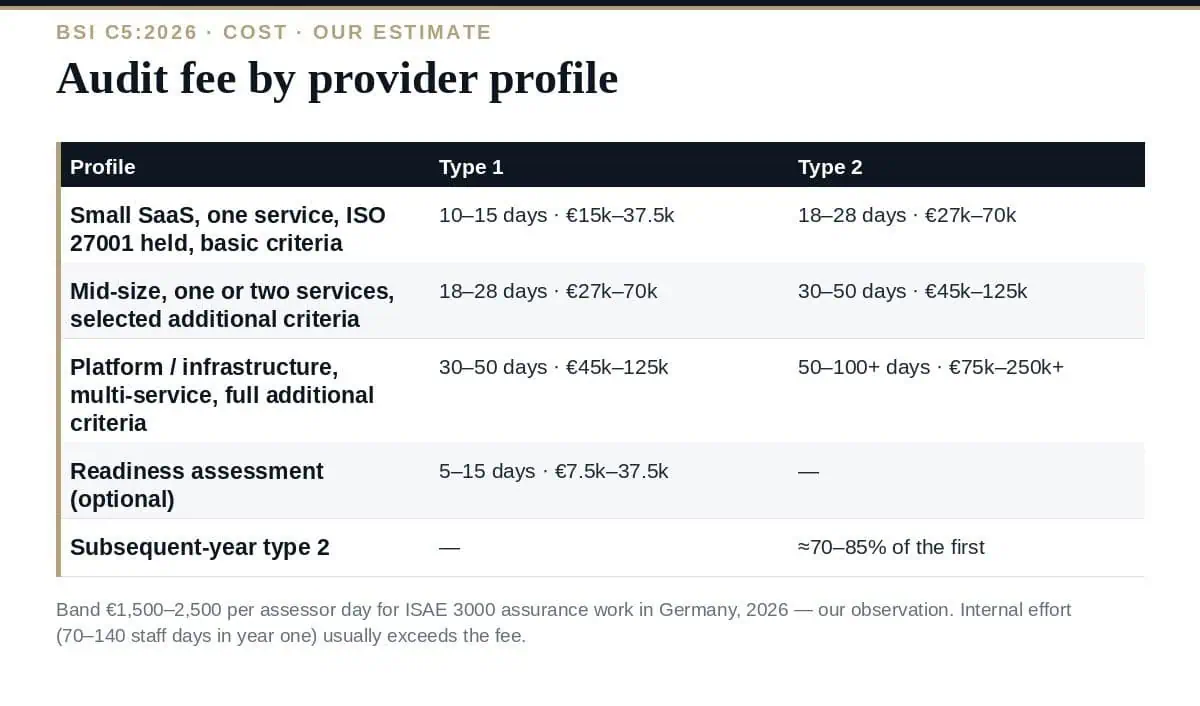
The band we use is €1,500 to €2,500 per assessor day for ISAE 3000-family assurance work by qualified public accountancy firms in Germany in 2026 — a market observation, not a published rate — with specialist firms at the lower end and Big Four at the upper. Days are our assumptions for a single cloud service with a competent evidence base.
| Provider profile | Type 1 days / fee | Type 2 days / fee | Notes |
|---|---|---|---|
| Small SaaS provider, one service, one region, ISO 27001 held, basic criteria | 10–15 days: €15,000 – €37,500 | 18–28 days: €27,000 – €70,000 | Most of OPS, IAM, CRY and DEV evidenced from the ISMS |
| Mid-size provider, one or two services, two regions, basic plus selected additional criteria | 18–28 days: €27,000 – €70,000 | 30–50 days: €45,000 – €125,000 | Additional criteria and a second region add sampling |
| Platform or infrastructure provider, multiple services, several data centres, full additional criteria | 30–50 days: €45,000 – €125,000 | 50–100+ days: €75,000 – €250,000+ | Subservice organisations and confidential computing or container criteria add specialist testing |
| Add: readiness assessment by the auditor or a consultant | 5–15 days: €7,500 – €37,500 | Same | Optional; it converts audit findings into pre-audit fixes |
| Add: bridge or subsequent-year type 2 | — | Typically 70–85% of the first type 2 | The system description and mapping exist; only the period changes |
A type 2 is usually not available in the first year: BSI’s FAQ notes that an initial examination may lack the operating history for effectiveness testing, in which case a type 1 is issued. Budget both — the type 1 now and the type 2 after six to twelve months of operation. Our guide to BSI C5 attestation covers the two types and the report contents.
| Activity | Who | Effort (our estimate, first year) |
|---|---|---|
| Import the C5:2026 catalogue and map every basic subcriterion in scope to a control | Security / compliance lead | 10–20 staff days |
| Decide the additional criteria and complementary customer criteria; write the six general conditions | Compliance, legal, product | 5–10 days |
| Write the system description | Compliance with engineering | 10–20 days |
| Build the per-subcriterion evidence pack; for type 2, evidence across the period | Security, operations, engineering | 30–60 days |
| Close gaps: OIS-01 ISMS scope, CRY key lifecycle, OPS logging and patching, PSS product security, INQ procedures | Engineering, operations, legal | Highly variable — from a policy to a platform change |
| Support fieldwork: interviews, walkthroughs, sample requests | All of the above | 10–25 days |
| Annual repeat | Compliance lead with owners | Half of the above, once the pack is maintained |
Seventy to a hundred and forty internal staff days in year one for a mid-size provider is the realistic range, and it exceeds the audit fee in most cases. Our guide to C5 criteria covers the mapping the first line produces.
A German SaaS provider, one service on a hyperscaler (carve-out method for the subservice organisation), ISO 27001 certified, selling to hospitals and health insurers under § 393 SGB V — which requires a current type 2 attestation from 1 July 2025 and implementation of the complementary customer criteria. Our estimate, illustrative only:
| Line | Basis | Estimate |
|---|---|---|
| Readiness assessment | 8 days at €1,800 | €14,400 |
| Type 1 examination (year one) | 14 days at €1,800 | €25,200 |
| Type 2 examination (year two, six-month period) | 24 days at €1,800 | €43,200 |
| Expenses | Two site visits | €2,000 – €4,000 |
| External subtotal over two years | €84,800 – €86,800 | |
| Internal effort | ≈90 staff days over two years | Internal cost — budget the days |
| Remediation | Key management lifecycle (CRY-07 to CRY-14), PSS vulnerability information process, INQ procedure | Variable; the key management work is the larger |
How much does a BSI C5 attestation cost?
No published figure exists — BSI does not set fees and audit firms quote per engagement. Our estimate for a single-service provider with an ISO 27001 ISMS is roughly €15,000–37,500 for a type 1 and €27,000–70,000 for a type 2 in audit fees, rising to six figures for multi-service platforms with additional criteria, plus internal effort that usually exceeds the fee.
Is type 2 more expensive than type 1?
Yes — roughly 1.5 to 2 times the days, because operating effectiveness is tested by sampling across a period. Most providers start with a type 1 and move to type 2 after six to twelve months of operation; healthcare customers under § 393 SGB V require the type 2.
Does the BSI charge anything?
No. BSI publishes the catalogue and takes no part in auditor selection, engagement or report review. The costs are the audit firm’s fee, your internal effort and remediation.
Does ISO 27001 or SOC 2 reduce the cost?
Substantially. OIS-01.01B requires an ISO 27001-compliant ISMS, so a certified one is both a requirement and an evidence base; a SOC 2 type 2 evidences most operational criteria. BSI recommends aligning the audits so records serve both reports.
Are these official prices?
No. Every figure is our estimate from assessor-day assumptions and a €1,500–2,500 per day assurance rate band observed in the German market in 2026. Get quotes from two or three firms with C5 experience.
Budget BSI C5 attestation cost as days times rate by scope and type — type 1 first, type 2 when the period exists — plus the internal mapping and evidence effort that no auditor can do for you, plus remediation. Scope the service, align with the assurance you already hold, decide the additional criteria on purpose, and map at subcriterion level before fieldwork; the ranges above shrink from the top in that order.
The subcriterion-level control mapping for all 17 objectives, the system description template, the general conditions disclosure and the evidence pack structure that take the discovery days out of the audit are in the BSI C5:2026 Cloud Toolkit, or start with the free templates.


September 21, 2026

September 20, 2026

September 20, 2026

September 19, 2026

September 19, 2026

