About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesGap AssessmentsBusiness Impact AnalysisAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Author: Governance Docs

Governance Docs LLC

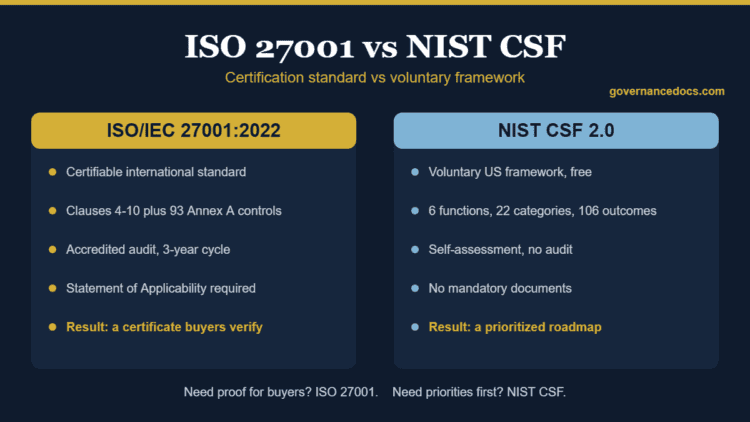
ISO 27001 vs NIST CSF comparison of certification, structure and controls

ISO 27001 vs NIST CSF: Which One Do You Need? (Complete 2026 Guide)

Governance Docs05th August 2026

ISO 27001 vs NIST CSF compared: certification versus self-assessment, 93 Annex A controls versus 106 CSF outcomes, and…
Read More
ISO 27001 timeline showing the phases from kickoff to certification

ISO 27001 Timeline: How Long Does Certification Take?

Governance Docs22nd July 2026

A realistic look at the ISO 27001 timeline: how long certification takes by company size, the seven phases…
Read More
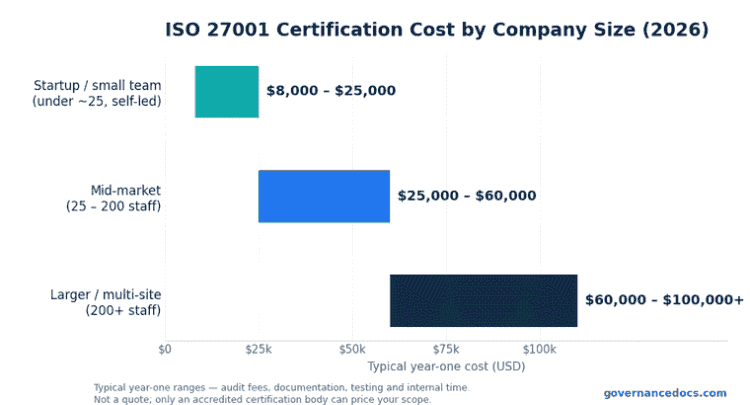
ISO 27001 certification cost by company size in 2026

How Much Does ISO 27001 Certification Cost? (Complete 2026 Breakdown)

Governance Docs22nd July 2026

A practical 2026 breakdown of what ISO 27001 certification actually costs, from certification-body audit fees to the internal…
Read More
ISO 9001 Certification Cost — guide from Governance Docs

ISO 9001 Certification Cost: A Complete 2026 Breakdown

Governance Docs17th July 2026

What ISO 9001 certification actually costs in 2026, broken down by company size, with a worked example, one-time…
Read More
ISO 9001 internal audit checklist covering clauses 4 to 10 of the quality management system

ISO 9001 Internal Audit: The Complete 2026 Checklist Guide

Governance Docs17th July 2026

ISO 9001 internal audit guide for the 2026 edition: what clause 9.2 requires, a 65-line checklist on the…
Read More
ISO 9001 clauses explained from context and leadership to operation and improvement

ISO 9001 Clauses Explained (Clauses 4-10)

Governance Docs17th July 2026

The ISO 9001 clauses hold every requirement. Here is a plain-language walkthrough of clauses 4 to 10, from…
Read More
ISO 9001 certification process step by step from building the QMS to the stage 2 audit

How to Get ISO 9001 Certified: A Step-by-Step Guide

Governance Docs17th July 2026

ISO 9001 certification is the world's most recognised quality credential. Here is the step-by-step process, how long it…
Read More
ISO 9001 mandatory documents and records including QMS scope, quality policy and objectives

ISO 9001 Mandatory Documents & Records List

Governance Docs17th July 2026

What documents does ISO 9001 require? A complete list of the mandatory ISO 9001:2015 documents and records -…
Read More
HIPAA BAA guide - what a business associate agreement is and its required provisions

HIPAA Business Associate Agreement (BAA): A Guide

Governance Docs17th July 2026

A HIPAA BAA is required whenever a vendor handles protected health information for you. Here is what a…
Read More
HIPAA compliance checklist covering Privacy Rule, Security Rule, breach notification and BAAs

HIPAA Compliance Checklist for Vendors & Small Practices

Governance Docs17th July 2026

A practical HIPAA compliance checklist, organised by the Privacy and Security Rules, breach notification, and business associates -…
Read More
HIPAA risk assessment steps from mapping ePHI to risk management and remediation

How to Conduct a HIPAA Risk Assessment

Governance Docs17th July 2026

The HIPAA risk assessment is the foundation of the Security Rule. Here is what it is, why it…
Read More
HIPAA Security Rule vs Privacy Rule - protecting electronic PHI versus governing use and disclosure

HIPAA Security Rule vs Privacy Rule Explained

Governance Docs17th July 2026

HIPAA Security Rule vs Privacy Rule: one protects electronic health data, the other governs its use and disclosure.…
Read More

    ←
  • 1
  • …
  • 60
  • 61
  • 62
  • 63
  • 64
  • …
  • 67
  • →

Recent Posts

Is ISO 42001 worth it in 2026 — audit days, first-year cost and Annex A controls at a glance
Is ISO 42001 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Is SOC 2 worth it in 2026 — typical first-year cost, annual report cycle and attestation status
Is SOC 2 Worth It? The Complete 2026 Cost-Benefit Case

September 24, 2026

ISO 21502 vs PMBOK 8 comparison: the 2020 project management guidance against PMI six principles, five Focus Areas and seven Performance Domains
ISO 21502 vs PMBOK 8: The Complete 2026 Guide for Project Governance

September 24, 2026

ISO 31000 vs ISO 27005 comparison: 2018 risk management guidelines against the 2022 information security risk guidance
ISO 31000 vs ISO 27005: The Definitive 2026 Guide

September 24, 2026

Comparison of NIST RMF and FedRAMP security frameworks for government.
NIST RMF vs FedRAMP: The Complete 2026 Guide to Which One You Need

September 24, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Gap assessments
  • Business impact analysis
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA