CIS Controls IG2 is where most growing organizations land after they finish the basics. Implementation Group 1 gives small teams a realistic starting point, but once you have dedicated IT staff, several sites, regulated data or customers who audit you, the question becomes what to add next.
This guide explains what IG2 is in CIS Controls v8.1, how many safeguards it includes, which controls gain the most from it, who should aim for it and how to sequence the work. It is written for IT and security managers who have completed or are close to completing IG1. Effort and cost figures are typical ranges, and the official CIS documents are the authority on safeguard wording.
Free gap assessment
Have you cleared Implementation Group 1?
Score all 18 Controls, free, with IG1 treated as the floor rather than the starting point, so you find out whether the basics are actually covered.
The CIS Controls are a prioritized set of security actions. Version 8.1 contains 18 controls and 153 safeguards, grouped into three Implementation Groups so that organizations can start where their resources and risk fit. IG1 is described by CIS as essential cyber hygiene. IG2 builds on IG1, and IG3 is the complete set.
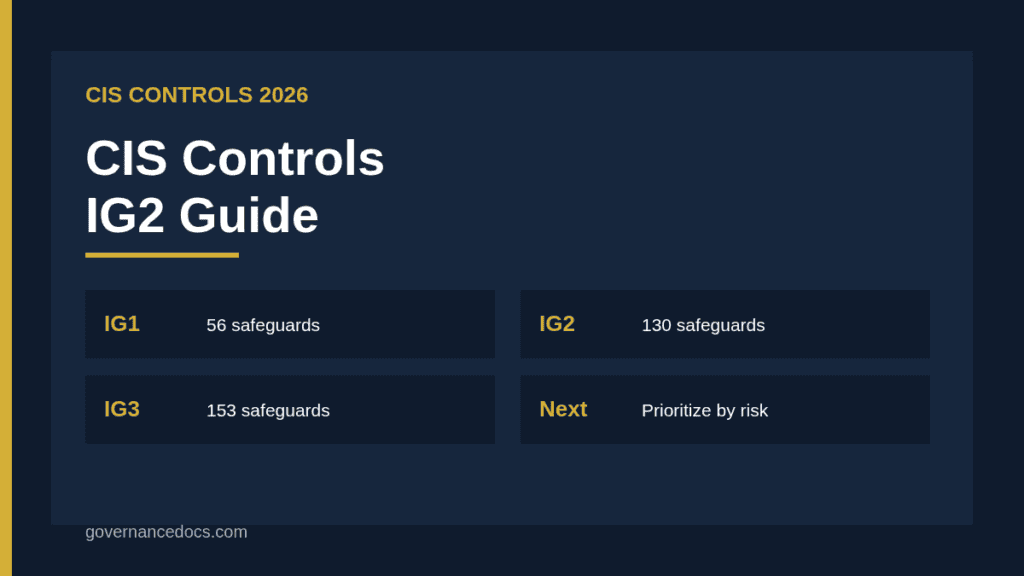
Published breakdowns count 56 safeguards in IG1, 130 in IG2 and all 153 in IG3. That means CIS Controls IG2 adds 74 safeguards beyond the basics. CIS describes IG2 as aimed at organizations with greater resources and a higher risk profile. Our overview of the CIS Controls explains the 18 controls; this article focuses on the step up.
Who should aim for IG2
Consider IG2 if any of the following apply: you have dedicated IT or security staff, you manage several departments or locations, you handle regulated or sensitive data such as health, payment or personal information, downtime would cause serious harm or customers require evidence of stronger controls in their contracts.
IG1 remains a fine target for very small organizations. The point of the groups is proportionality: do what fits your risk, and prove it. CIS Controls implementation is also commonly used to support legal defenses in some states; see CIS Controls safe harbor for that angle, and confirm requirements with counsel.
What IG2 adds beyond IG1
The extra safeguards fill in areas where IG1 is light, and they lean on process and tooling. Expect additions around asset and software management, data handling, configuration and account management, vulnerability management, logging and monitoring, email and web protections, service provider management and incident response.
Three controls are notable: network monitoring and defense, application software security and penetration testing contain no IG1 safeguards according to published breakdowns, because they need specialized expertise. IG2 is where some of them begin to appear, so you may need new skills or a managed provider. See our guide to IT asset inventory for the foundation that IG2 tooling depends on.
Group
Safeguards
Intended organization
Typical profile
IG1
56
Essential cyber hygiene
Small team, limited IT expertise, low data sensitivity
IG2
130 total, adds 74
More resources and higher risk
Dedicated IT staff, multiple departments, regulated or sensitive data
IG3
153 total, adds 23
Advanced security needs
Security specialists, high-value targets, heavy regulation
A practical roadmap for CIS Controls IG2
Do not try to do 74 safeguards at once. Use a phased plan, and adapt the durations to your team.
Phase 1: confirm IG1 is complete and evidenced, including inventories and access control
Phase 3: prioritize by risk, starting with vulnerability management, logging and incident response
Phase 4: implement tooling and write procedures
Phase 5: test, measure and report to management
Phase 6: decide whether IG3 safeguards are worth adding for specific systems
Prioritizing the IG2 safeguards
Rank the new safeguards by the risk they reduce and the effort they cost. Start with items that protect your most valuable data and most exposed systems. Continuous vulnerability management, centralized log collection with alerting and tested incident response usually deliver outsized value because they turn individual controls into a working detection and response capability.
Then consider dependencies. Logging is useless without accurate asset inventories. Vulnerability scanning needs defined scopes. Service provider management needs a list of providers. Fix the dependencies first so that later work does not stall.
Evidence and measurement
The value of an IG2 program shows in records. Keep dated inventories, scan reports with remediation times, log review samples, incident exercises, access reviews and training completions. Measure percentages covered, time to patch critical findings and time to detect and contain incidents.
Costs depend on your environment. Typical categories are endpoint and vulnerability tooling, log management or a managed detection service, staff time, training and external testing. See CIS Controls implementation cost for a breakdown. As a rough guide, a mid-sized organization may spend several months and a meaningful share of its security budget to move from IG1 to IG2, which is an illustrative figure, not a benchmark.
A managed service provider can cover specialist tasks such as monitoring or testing. If you outsource, keep oversight: you remain accountable for outcomes, and the contract should specify evidence you can retrieve.
Using templates for IG2 documentation
Most safeguards need a policy, a process or a record. The CIS Controls Toolkit provides editable templates for the main control areas, so your team can document what it does without writing every page from scratch. See CIS Benchmarks vs CIS Controls to avoid confusing configuration guidance with the control framework.
Example: a 200-person company moving to CIS Controls IG2
Picture a 200-person professional services firm with a three-person IT team, a cloud email and file platform, laptops for everyone and client data under contract confidentiality. It completed IG1 a year ago: inventories exist, multi-factor authentication is on, backups are tested and staff are trained. A client security review now asks about log monitoring, vulnerability remediation times and incident response testing. Those are IG2 territory.
The team starts by centralizing logs from identity, email and endpoint tools, defining a short list of alerts and assigning an on-call rota. Next it sets a vulnerability policy with target remediation times by severity and produces a monthly report. Then it writes an incident response plan, runs a half-day tabletop exercise and records the lessons. Finally it adds a service provider register and reviews its five most important vendors. The firm might need to buy a logging service and a scanner; the rest is process and discipline. Details in this example are illustrative.
Skills and staffing for IG2
IG2 typically requires more specialist capacity than IG1. A small team cannot watch every alert around the clock, so decide what will be handled internally, what will be outsourced and how the two will hand off. Cross-train at least two people on each critical task so that leave or turnover does not stop the program. Budget for training, and encourage certifications or courses that match the tooling you buy.
Governance and reporting
Give the program an executive sponsor and a steering meeting every quarter. Bring a one-page dashboard showing safeguards complete, in progress and planned, the most important risks still open and the metrics above. Record the decisions taken and the exceptions approved. When the program is governed this way, it survives changes in staff and budget, and it becomes easier to show customers, insurers and auditors that your controls are intentional and maintained.
Testing whether CIS Controls IG2 works
Safeguards on a spreadsheet prove little until they are tested. Run simple exercises: pick a laptop at random and confirm it appears in the asset inventory with the right owner; create a test alert and time how long it takes someone to notice; ask the vendor manager for the list of providers with access to sensitive data; and have the incident lead walk through the plan for a ransomware scenario. Record the results and fix what fails. Repeat each quarter with different samples. This habit keeps your CIS Controls IG2 program honest and gives you examples of controls operating that customers and assessors find convincing.
When to consider IG3
IG3 adds the final 23 safeguards and suits organizations with security specialists and high-value targets. You do not have to move all systems at once; some organizations apply IG3 safeguards to critical systems only while the rest stay at IG2. Decide with a risk assessment, not a desire to complete the set.
Free ISO 27001 risk assessment
Which of your risks sit above your appetite line?
Set your own risk criteria, pick from 61 information security risk scenarios, rate likelihood and impact, and decide how to treat each one. You get a heat map, a process score and the findings an auditor would raise, free.
The most common mistake is skipping IG1 gaps because IG2 looks more exciting. Another is buying tools without owners or processes. A third is measuring tool deployment instead of outcomes. Teams also forget to reassess annually, so the safeguard status drifts. Keep a single register of safeguards with status, owner, evidence and next review date, and update it whenever your environment changes.
CIS Controls IG2 FAQ
How many safeguards are in CIS Controls IG2?
Published breakdowns of version 8.1 count 130 safeguards in IG2, which includes the 56 in IG1 and adds 74.
Do I need IG2 or IG1?
Choose based on your resources and risk. Organizations with dedicated IT staff, sensitive data or customer requirements usually aim for IG2.
Is IG2 a certification?
No. The CIS Controls are a framework and not a certification. You self-assess or use an independent assessment to show progress.
Can I skip straight to IG2?
You can, but IG1 safeguards are foundations for many IG2 ones. Close IG1 gaps first.
How often should I reassess?
At least annually and after major changes, keeping evidence for each safeguard.