CART
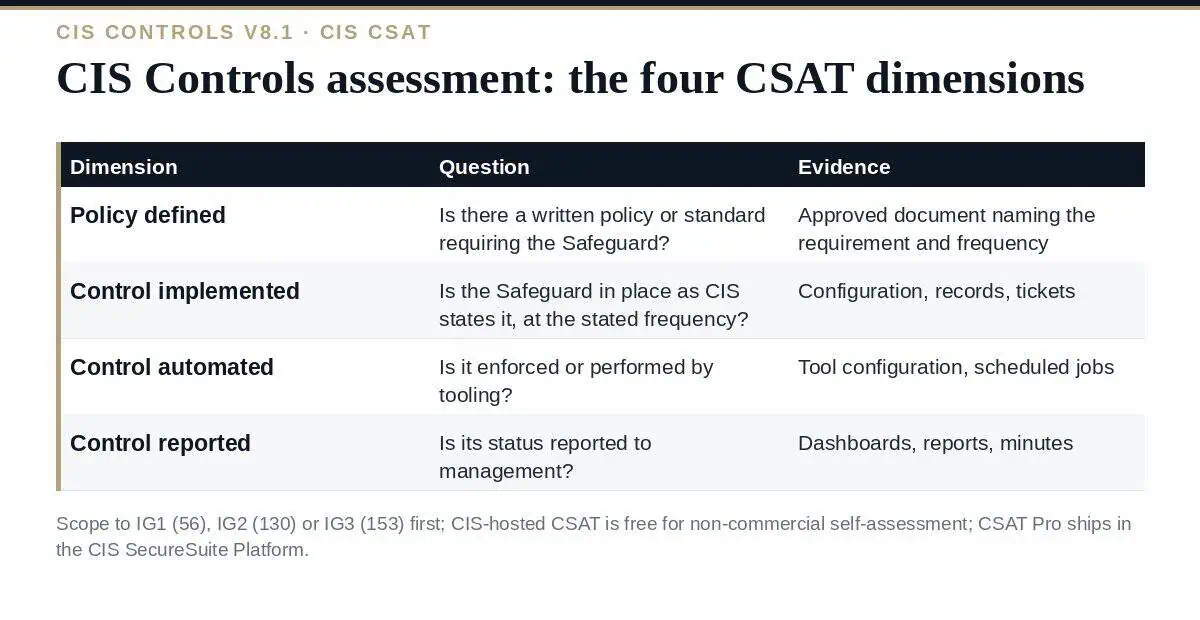
A CIS Controls assessment is how an organisation finds out which of the 153 Safeguards in CIS Controls v8.1 it has actually implemented — and, because there is no certification scheme behind the Controls, it is also the only result an insurer, a customer or a board will ever see. CIS provides the tool: the CIS Controls Self Assessment Tool, CSAT, which scores each Safeguard on four dimensions — whether a policy is defined, whether the control is implemented, whether it is automated and whether it is reported — and rolls the scores up by Control, by Implementation Group and for the enterprise.
The CIS-hosted CSAT is free for any organisation assessing its own implementation in a non-commercial capacity; CSAT Pro, now delivered inside the CIS SecureSuite Platform alongside the CIS-CAT Pro Dashboard, is the on-premises version for CIS SecureSuite members. This guide explains what a CIS Controls assessment measures, how CSAT scoring works, how to scope the assessment to an Implementation Group, what evidence each dimension needs, how to run the assessment in six steps, and how to turn the score into a plan rather than a number.
| Level | Unit | What is measured |
|---|---|---|
| Safeguard | One of 153 specific actions, e.g. 5.3 Disable dormant accounts after 45 days | Whether it is done as CIS states it, including the frequency |
| Control | One of 18 themes, e.g. 5 Account Management | The aggregate of its Safeguards’ scores |
| Implementation Group | IG1 (56 Safeguards), IG2 (130), IG3 (153) | The aggregate for the Safeguards in scope for the enterprise’s IG |
| Enterprise | The whole in-scope set | An overall score and the gap list |
The scope decision comes first. An organisation that assesses against IG3 when its risk profile is IG1 will score badly on 97 Safeguards it was never expected to implement; one that assesses against IG1 when it has security specialists and public-harm exposure will score well on an incomplete set. Our guide to the CIS Controls v8.1 covers how CIS defines the three groups.
| Dimension | Question | What full credit needs | Typical evidence |
|---|---|---|---|
| Policy defined | Is there a written policy or standard that requires the Safeguard? | An approved document that names the requirement and the frequency | Policy or standard, approval record |
| Control implemented | Is the Safeguard in place as described? | The action performed across the enterprise at the stated frequency | Configuration, records, screenshots, tickets |
| Control automated | Is the Safeguard enforced or performed by tooling rather than by hand? | Automation that performs or enforces the action without manual steps | Tool configuration, scheduled jobs, enforcement policies |
| Control reported | Is the Safeguard’s status reported to management? | Recurring reporting that management receives and acts on | Dashboards, reports, meeting records |
Each dimension is answered on a scale rather than yes/no, so a Safeguard implemented on most assets but not all, or automated for servers but manual for endpoints, scores partially. CSAT also records the assessment date, the assessor, and the validation status of the evidence, and it retains prior assessments so trend is visible. The four-dimension design is the useful part: a Safeguard that is implemented but has no policy and no reporting is a Safeguard that will decay, and the score says so.
| Step | What happens | Output |
|---|---|---|
| 1. Set up | Create the organisation in CSAT, select v8.1 and the Implementation Group, define the boundary, assign Safeguard owners | Assessment configured |
| 2. Collect | Owners answer the four questions per Safeguard and attach evidence | Draft scores with artefacts |
| 3. Validate | An independent reviewer checks evidence against the Safeguard wording and frequency; disputed answers are re-scored | Validated scores |
| 4. Analyse | Review by Control and by dimension: which Controls are weakest, which dimension (policy, implementation, automation, reporting) is systematically low | Gap analysis |
| 5. Plan | Prioritise gaps by Control order (lower-numbered Controls first) and by IG (IG1 gaps before IG2), assign owners and dates | Remediation plan |
| 6. Reassess | Repeat on a cycle — quarterly for the plan’s active Controls, annually in full — and track the trend | Trend report |
Our guide to CIS Controls implementation covers what the remediation plan looks like for IG1.
| Audience | What they want | How to present the assessment |
|---|---|---|
| Cyber insurer | Evidence of essential cyber hygiene | IG1 score with the Safeguards implemented, and the plan for the gaps |
| Customer or supplier questionnaire | A framework statement | IG level, overall score, date, assessor independence; CSF Profile if asked, via CIS’s mapping |
| Board | Trend and risk | Score by Control over time, the top gaps and their cost |
| ISO 27001 auditor | Annex A evidence | The Safeguard-to-Annex A mapping with CSAT evidence as control evidence |
Our guides to CIS Controls vs NIST CSF and the CIS Controls ISO 27001 mapping cover the two translations most often asked for.
What is a CIS Controls assessment?
A structured evaluation of which of the 153 CIS Controls v8.1 Safeguards an organisation has implemented, scoped to its Implementation Group, usually performed in CIS CSAT, which scores each Safeguard on policy defined, control implemented, control automated and control reported.
Is CIS CSAT free?
The CIS-hosted CSAT is free for any organisation to assess its own implementation of the CIS Controls in a non-commercial capacity. CSAT Pro, the on-premises version, is delivered through the CIS SecureSuite Platform to CIS SecureSuite members.
Is there a CIS Controls certification?
No. There is no accreditation scheme or certificate for the CIS Controls; a CSAT assessment, ideally with independent validation of the evidence, is the assurance available.
Which Implementation Group should we assess against?
The one that matches your risk profile and resources: IG1 (56 Safeguards) for organisations with limited IT and security expertise, IG2 (130) for those with dedicated IT staff, IG3 (all 153) for those with security specialists and significant public-harm exposure. CIS advises every enterprise to start with IG1.
How often should we reassess?
Annually in full, with quarterly updates on the Controls under active remediation; CSAT keeps prior assessments so the trend is visible.
Run the CIS Controls assessment as a scoped, evidenced, four-dimension exercise: pick the Implementation Group honestly, define the boundary, score every Safeguard on policy, implementation, automation and reporting with an artefact for each, validate independently, and turn the result into a plan ordered by Control and by IG — because the score is the only assurance the CIS Controls offer, and it is only worth what the evidence behind it proves.
The Safeguard-level assessment workbook with the four scoring dimensions, evidence fields and Implementation Group filter, the gap analysis and remediation plan templates and the 18 Control policies are in the CIS Controls v8.1 Toolkit, or start with the free templates.


September 21, 2026

September 20, 2026

September 20, 2026

September 19, 2026

September 19, 2026

