CART
The C5 criteria are the substance of Germany’s Cloud Computing Compliance Criteria Catalogue, and in the 2026 edition they number 168, grouped under 17 objectives, each broken into basic subcriteria that define the minimum audit scope and additional subcriteria — sharpening or complementing — that a provider includes for customers with higher protection needs. The catalogue also carries six general conditions (GC-01 to GC-06) the provider discloses about jurisdiction, availability, recovery, investigation requests and certifications, and complementary customer criteria that mark where the customer has to implement controls of its own.
C5:2026 kept the 17 areas — BSI states they follow the structure of ISO/IEC 27001:2013 Annex A objectives while the content considered ISO/IEC 27001:2022 — restructured every criterion into subcriteria for EUCS compatibility, and added criteria on confidential computing, container management, supply chain, post-quantum-ready cryptography and product security. This guide lists the 17 objectives with their criterion counts and what each covers, explains the basic/additional/complementary mechanics and the identifier syntax, picks out the criteria that are new or hardest in 2026, and describes how a provider maps the catalogue to its own control set.
| Element | What it is | Identifier |
|---|---|---|
| Objective | One of 17 areas, each with an objective statement — e.g. OIS: ‘Plan, implement, maintain and continuously improve the information security framework within the organisation’ | Two- to four-letter code: OIS, SP, HR … |
| Criterion | A requirement within the area; 168 in total | OIS-01, OPS-27 |
| Basic subcriterion | One aspect of the criterion; the set of basic subcriteria is the basic criterion and defines the minimum audit scope — ‘the minimum level of information security that a cloud service has to offer’ for normal protection needs | OIS-01.01B |
| Additional sharpening subcriterion | A stricter replacement for one basic subcriterion, addressing the same aspect with sharper requirements | OIS-01.01AS |
| Additional complementing subcriterion | A new aspect not covered by any basic subcriterion, added alongside the basic set | OIS-01.01AC |
| Supplementary information | BSI’s guidance on the criterion — informative, not audited | Text under each criterion |
| Complementary customer criteria | Where the customer must set up controls of its own for the criterion to be met (CUEC) | Listed per criterion |
| General conditions | Six disclosure criteria about the service’s circumstances, audited alongside | GC-01 to GC-06 |
The subcriterion structure is the 2026 change with the most practical effect: a provider maps its controls at subcriterion level, an auditor documents tests at subcriterion level, and the report shows which additional subcriteria were in scope. Our guide to BSI C5 covers the 2026 revision as a whole.
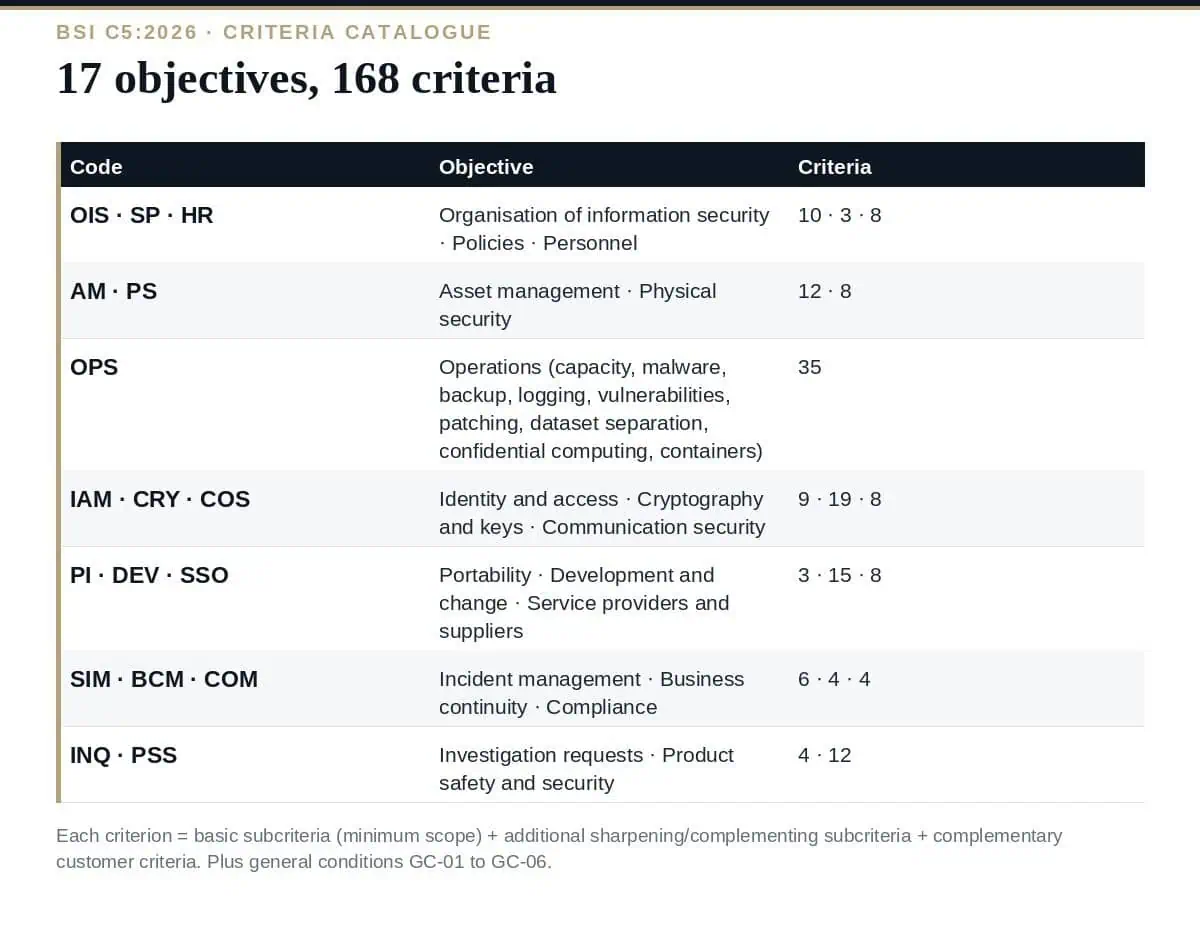
| Objective | Code | Criteria | What the criteria cover |
|---|---|---|---|
| Organisation of Information Security | OIS | 10 | An ISO/IEC 27001-compliant ISMS (OIS-01.01B requires it, with scope covering the cloud service), policy, interfaces and dependencies, segregation of duties, threat intelligence, contacts, risk management policy, assessment and treatment, security in projects |
| Security Policies and Procedures | SP | 3 | Documentation, communication and provision of policies; review and approval; exceptions |
| Personnel | HR | 8 | Qualification and trustworthiness checks, employment terms, training and awareness, disciplinary measures, termination, NDAs, remote working policy and implementation |
| Asset Management | AM | 12 | Framework, inventories (hardware, software), acceptable use, commissioning and decommissioning, return of assets, classification and labelling, hardware on hold, transfer, removable media and endpoints |
| Physical Security | PS | 8 | Requirements, redundancy model, perimeter, site access control, external and environmental threats, power and supply, monitoring of operational parameters, workplace security |
| Operations | OPS | 35 | Capacity, malware protection, backup and recovery, logging and monitoring (eight criteria), vulnerability, incident and crash management including penetration tests and scans, hardening, patch management, separation of datasets, confidential computing, container management |
| Identity and Access Management | IAM | 9 | Policy, granting and change, risk-based locking, withdrawal on role change, regular review, privileged access, access to customer data, authentication mechanisms, confidentiality of authentication information |
| Cryptography and Key Management | CRY | 19 | Policy, cryptographic change management, review of practices, transport protection, encryption at rest, key generation, rotation, certificate issuance, provisioning, storage, archival, transition, compromise, deactivation, pre-shared keys, continuity, lifecycle, external KMS, customer-managed keys |
| Communication Security | COS | 8 | Technical safeguards, connection requirements and monitoring, cross-network access, administration networks, traffic separation in shared networks, topology documentation, data transmission policies |
| Portability and Interoperability | PI | 3 | Interface safety, contractual data provision, secure deletion at contract end |
| Procurement, Development and Modification of Information Systems | DEV | 15 | Development and procurement policies, outsourced development, change policies, developer training, design documentation for security features, risk categorisation of changes, testing, logging of changes, version control, production approvals, protection and separation of environments, transparency about software components, secure use of third-party hardware and software, exceptions to change management |
| Control and Monitoring of Service Providers and Suppliers | SSO | 8 | Policies for service organisations, risk assessment of them, their data processing, a directory of service organisations, monitoring of compliance, contract termination strategy, transparency within service organisations, and control of exchanges with suppliers of functional components |
| Security Incident Management | SIM | 6 | Incident management policy, response plans, processing of incidents, documentation and reporting, the duty of personnel to report to a central body, evaluation and learning |
| Business Continuity Management | BCM | 4 | Business continuity and emergency management system, business impact analysis, continuity plans, testing |
| Compliance | COM | 4 | Identification of applicable legal, regulatory, self-imposed or contractual requirements; policy for planning and conducting audits; internal audits of the ISMS; information on information security performance and management assessment |
| Dealing with Investigation Requests from Government Agencies | INQ | 4 | Legal assessment of investigation requests, informing customers about them, limiting access to or disclosure of data, and communication of the technical procedures for disclosure — ‘Ensure appropriate handling of government investigation requests’ |
| Product Safety and Security | PSS | 12 | Guidelines for customers, identification of and information about vulnerabilities, error handling and logging, authentication mechanisms, session management, confidentiality of authentication information, roles and rights framework, authorisation, software-defined networking, images for VMs and containers, region of processing and storage |
The counts are from the C5:2026 catalogue’s own table of contents; check the copy you are audited against, because the identifiers — not the counts — are what the report cites.
| Criterion | What the provider discloses |
|---|---|
| GC-01 | Applicable law, jurisdiction, countries, partitions, regions, zones and locations of processing |
| GC-02 | Availability and incident handling during regular operation |
| GC-03 | Recovery parameters in emergency operation |
| GC-04 | The approach to ensuring service availability |
| GC-05 | How investigation requests from government agencies are handled |
| GC-06 | Certifications or attestations held |
The general conditions exist, in BSI’s words, to inform customers about matters they cannot verify alone and to make reports comparable between providers. They are audited as criteria and reported in the system description.
How many C5 criteria are there?
168 in C5:2026, under 17 objectives, plus six general conditions. Each criterion is broken into basic subcriteria — the minimum audit scope — and, where defined, additional sharpening or complementing subcriteria, with complementary customer criteria marking the customer’s obligations.
What are the 17 C5 objectives?
OIS organisation of information security, SP policies, HR personnel, AM asset management, PS physical security, OPS operations, IAM identity and access, CRY cryptography, COS communication security, PI portability and interoperability, DEV procurement and development, SSO service providers and suppliers, SIM incident management, BCM business continuity, COM compliance, INQ investigation requests, PSS product safety and security.
What is the difference between basic and additional criteria?
Basic subcriteria define the minimum level of security for normal protection needs and the minimum scope of a C5 audit. Additional subcriteria address higher protection needs: sharpening ones replace a basic subcriterion with a stricter version; complementing ones add a new aspect. The report states which additional criteria were in scope.
Does C5 require ISO 27001?
OIS-01.01B requires the provider to maintain an ISO/IEC 27001-compliant ISMS whose scope covers the cloud service. It does not require an ISO 27001 certificate, but a certified ISMS is the usual evidence.
What changed in the criteria in 2026?
Every criterion was restructured into subcriteria for EUCS compatibility; additional criteria were classified as sharpening or complementing; criteria were added for confidential computing, container management, dataset separation, supply chain, cryptographic transition and customer-managed keys, and product security; and the catalogue is published in YAML.
Work the C5 criteria at subcriterion level: 168 criteria under 17 objectives, basic subcriteria as the minimum scope, additional ones chosen for your market, complementary customer criteria stated, and six general conditions disclosed — each mapped to a control and evidenced across the period. The identifiers are what the report cites; the mapping is what the audit tests.
One control document per C5 area across all 17 objectives, the subcriterion-level control mapping, the general conditions disclosure and the complementary customer criteria statement are in the BSI C5:2026 Cloud Toolkit, or start with the free templates.

September 22, 2026

September 21, 2026

September 21, 2026

September 20, 2026

September 20, 2026

