
CART
No products in the cart.
ISO Compliance Insights & Best Practices
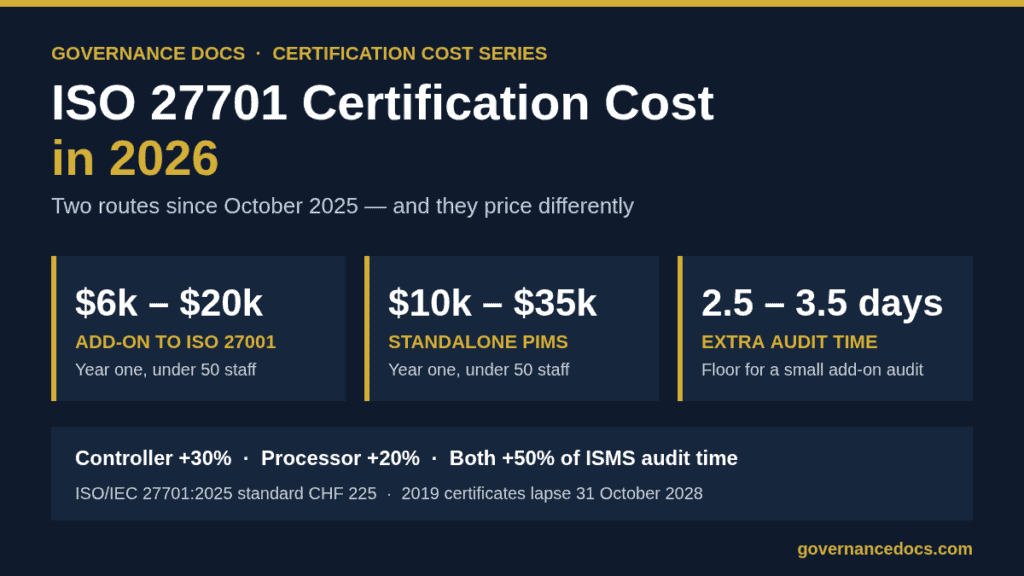
The ISO 27701 certification cost for a small US company in 2026 typically lands between $6,000 and $20,000 in the first year if you already hold ISO 27001, and up to $35,000 if you do not — and the gap comes from a decision most budgets skip: whether you add the privacy certificate to an ISO 27001 certificate you already hold, or certify a Privacy Information Management System (PIMS) on its own. Until 14 October 2025 there was only one route. ISO/IEC 27701:2025 opened the second one, and it prices differently. This guide sets out the line items, how certification bodies work out the audit days for each route, what a 2019 certificate holder pays to transition before the October 2028 cut-off, and the ranges to expect from an accredited body.
Split the spend into three buckets: what you pay to build the PIMS, what you pay the certification body, and what you keep paying every year to hold the certificate. The middle bucket is the only one anybody quotes, and it is rarely the largest.
The one fixed line item is the standard itself. ISO’s catalogue lists ISO/IEC 27701:2025 at CHF 225 (about $275) for a 64-page edition 2; the 2019 edition is withdrawn. The certification body’s own rulebook, ISO/IEC 27706:2025, is CHF 135 and you do not need to buy it — but knowing it exists tells you how your quote was built, which is the point of the next section.
| Line item | Typical 2026 US range | Notes |
|---|---|---|
| ISO/IEC 27701:2025 standard | CHF 225 (approx. $275) | Edition 2, October 2025; 2019 edition withdrawn |
| Gap analysis / privacy readiness review | $0 – $8,000 | Free if run internally against Annex A |
| PIMS documentation set | $99 – $15,000 | Template toolkit vs consultant-written |
| Records of processing, data map, PII inventory | $0 – $10,000 | The line item with the widest spread; scales with processing activities, not headcount |
| Control remediation (consent, rights handling, retention, transfers) | $0 – $20,000 | Highest for controllers with consumer-facing products |
| Internal audit | $2,000 – $6,000 | Auditor must be independent of what they audit |
| Certification audit, PIMS added to an existing ISO 27001 certificate | $3,500 – $9,000 | 2.5 – 3.5 extra auditor days for most firms under 65 staff |
| Certification audit, standalone PIMS (no ISO 27001) | $5,000 – $14,000 | Full Stage 1 + Stage 2 on its own; see the caveat on accreditation below |
| Internal staff time | 150 – 400 hours | Privacy lead plus process owners; rarely budgeted |
| Year-one total, under 50 employees, adding to ISO 27001 | $6,000 – $20,000 | Toolkit documentation, controls already largely in place |
| Year-one total, under 50 employees, standalone | $10,000 – $35,000 | You are also building the management system and the A.3 security controls |
These ranges are typical figures aggregated from published 2026 guidance by accredited certification bodies and consultancies, not a survey. UK guidance puts the same small-company bracket at roughly £12,000 to £25,000 in year one, and Australian consultancies quote AUD 15,000 to 25,000 in fees alone for a sub-50 firm that already holds ISO 27001. Treat every figure as a planning band and get three quotes.
This is the part that changed. Under the 2019 edition ISO 27701 was an extension to ISO 27001, so it could only be certified alongside an ISMS certificate, and the certification body priced it as a surcharge on the ISMS audit. The 2025 edition is a standalone management system standard with its own clauses 4 to 10 and a consolidated Annex A — controller controls in A.1, processor controls in A.2 and a set of information security controls in A.3 that every organization must address. If you have not read what that restructuring means for your documentation, start with our guide to ISO 27701:2025 vs 2019.
For the ISO 27701 certification cost, the consequence is simple. If you hold ISO 27001, the PIMS audit remains an add-on and is cheap. If you do not, you are paying for a complete management-system audit, and the ISO 27001 vs ISO 27701 decision becomes a cost decision — our comparison guide covers which certificate customers are actually asking for.
Certification bodies do not invent the audit days. For an ISMS they start from the audit-time table in ISO/IEC 27006 (Annex B of the 2015 edition, carried into the 2024 revision), which sets initial Stage 1 + Stage 2 days by the number of people under the organization’s control, and they cannot cut it by more than 30%. The PIMS was then priced by ISO/IEC TS 27006-2:2021 as a minimum percentage on top of that ISMS time, calculated for the same scope: 30% if you are a PII controller, 20% if you are a PII processor, 50% if you are both — with a floor for the first PIMS audit of about 2.5 days for a single role and 3.5 days for both, plus at least half a day if the PIMS audit is run separately from an ISMS surveillance or recertification visit. Certification bodies publish those rules in their own audit-duration procedures, and most are still quoting on them while they transition to ISO/IEC 27706.
| People in scope | ISMS initial audit days (ISO/IEC 27006 table) | PIMS add-on, single role (20 – 30%) | PIMS add-on, controller and processor (50%) | Indicative add-on fee at $1,400 – $2,500 per day |
|---|---|---|---|---|
| 1 – 10 | 5 | 1 – 1.5 → floor 2.5 – 3 | 2.5 → floor 3.5 | $3,500 – $8,750 |
| 11 – 25 | 6 – 7 | 1.2 – 2.1 → floor 2.5 – 3 | 3 – 3.5 → 3.5 | $3,500 – $8,750 |
| 26 – 45 | 8.5 | 1.7 – 2.55 → 2.5 – 3 | 4.25 | $3,500 – $10,600 |
| 46 – 65 | 10 | 2 – 3 → 2.5 – 3 | 5 | $3,500 – $12,500 |
| 86 – 125 | 12 | 2.4 – 3.6 | 6 | $3,400 – $15,000 |
| 176 – 275 | 14 | 2.8 – 4.2 | 7 | $3,900 – $17,500 |
| 276 – 425 | 15 | 3 – 4.5 | 7.5 | $4,200 – $18,750 |
Read the table from the floor up. Below roughly 65 people the percentage never beats the minimum, so a small controller pays for about 3 extra days and a small processor for about 2.5 whatever the headcount. The variable that actually moves a small company’s ISO 27701 certification cost is therefore not size but role: declaring yourself both controller and processor adds a day or more to every audit in the cycle. Declare the role your processing genuinely requires — a SaaS vendor processing customer data on instruction is a processor for that data even if it is a controller for its own staff and marketing records, and the scope statement can say so.
A standalone PIMS is audited as a management system in its own right under ISO/IEC 27706:2025, which replaced the 2021 technical specification and aligns its clause structure to ISO/IEC 17021-1 rather than to the ISMS rulebook. With no ISMS audit to piggyback on, the body has to cover context, leadership, planning, support, operation, performance evaluation and improvement, plus the A.3 security controls, plus the privacy controls — roughly the ground an initial ISO 27001 audit covers for the same headcount. Budget it that way: for a company under 50 people the standalone ISO 27701 certification cost at the certification body is a Stage 1 + Stage 2 quote in the $5,000 to $14,000 territory; compare it with the ISO 27001 certification cost for the same scope before deciding which certificate to buy first.
One caveat outranks the price. Accreditation bodies only began assessing certification bodies against ISO/IEC 27706 in May 2026, and UKAS has given its bodies until 31 October 2027 to complete the transition. A standalone PIMS certificate from a body that has not yet been assessed is not an accredited certificate, and an unaccredited certificate is the one line item you should never pay for. Before you sign, ask the body in writing whether its ISO/IEC 27706 accreditation is in place, and if not, when.
The certificate runs on a three-year cycle: surveillance audits at roughly twelve and twenty-four months, then recertification. For an add-on PIMS the surveillance surcharge follows the same percentage logic on the smaller ISMS surveillance visit, so for most small firms it is half a day to a day of extra auditor time — $700 to $2,500 a year on top of the ISMS surveillance fee. Recertification sits closer to the original Stage 2. Certification bodies’ published ranges for the whole three-year cycle cluster around 2 to 2.5 times the initial audit fee, and a standalone PIMS carries the full ISMS-sized surveillance and recertification visits rather than a surcharge on somebody else’s.
| Cycle year | Add-on PIMS (ISO 27001 already held) | Standalone PIMS |
|---|---|---|
| Year 1: Stage 1 + Stage 2 | $3,500 – $9,000 | $5,000 – $14,000 |
| Year 2: surveillance | $700 – $2,500 | $2,000 – $5,000 |
| Year 3: surveillance | $700 – $2,500 | $2,000 – $5,000 |
| Year 4: recertification | $2,300 – $6,000 | $3,500 – $9,500 |
| Three-year cycle, audit fees only | $5,000 – $14,000 | $9,000 – $24,000 |
The three-year ISO 27701 certification cost also carries the recurring internal work the table leaves out: an internal audit and management review every year, records of processing kept current, and the privacy lead’s time. Published guidance puts ongoing PIMS maintenance at one to two days a week for a small organization, which is the real reason a certificate is cheaper to keep integrated with an ISMS than to run beside one.
Certificates issued against ISO/IEC 27701:2019 stay valid until 31 October 2028 and then lapse; the UKAS transition bulletin requires certification bodies to have transitioned every certified client by that date. Getting there means a transition audit at some point in the next two cycles, and the pricing rule that holds across bodies is the same one that applied to the 2022 edition of ISO 27001: close to free if it is folded into a recertification audit, whose duration already covers every clause; a surcharge of about 0.5 to 1.5 auditor days if it is added to a surveillance visit; and $3,000 to $10,000 if you insist on a standalone transition audit.
The hidden cost is documentation, not audit fees. The 2019 edition’s controller and processor annexes were remapped into the three-table Annex A, and your applicability statement has to answer the new list — our guide to the ISO 27701 controls walks through the tables and why A.3 now applies to everyone. Budget 20 to 60 hours of internal rewriting for a typical small PIMS. Bodies say the same thing about every transition: the organizations that pay extra audit days are the ones that arrive at the visit with 2019 paperwork.
Buying it for the wrong reason. ISO 27701 is a management-system certification, not a GDPR Article 42 certification — those must be approved by the European Data Protection Board and certify processing activities, which is what schemes such as Europrivacy do. If a customer’s procurement team asked for “GDPR certification”, confirm which one they mean before spending anything.
Role declared too broadly. Both roles means a 50% surcharge and a higher floor on every audit for three years.
Scope drawn too wide. Every extra site and processing activity adds evidence and, above 65 people, audit days. Certify the services customers are asking about.
No records of processing. The data map is the largest single implementation task for a first-time controller and the item consultants charge the most for. Start it before you engage anyone.
Unaccredited standalone certificates. In 2026 the standalone route is new and not every body offering it has been assessed against ISO/IEC 27706. Check.
Consultant writing the documents. A Privacy Policy, a Data Subject Rights Procedure or a Retention Schedule looks much the same in any organization of your size. Pay a consultant, if at all, for judgement on role, scope and lawful basis — not for typing. Our ISO 27701 Toolkit supplies 75+ PIMS templates aligned to the 2025 edition, including the applicability statement and records of processing, for $99.
Certify the PIMS at the same visit as an ISO 27001 audit wherever possible — you touch each process once and avoid the half-day separate-visit surcharge. Ask every certification body for the audit-day count and the day rate separately, and for the role and headcount assumptions behind the days; that is the only way to compare three quotes. Time the transition of a 2019 certificate to fall at recertification, not at a surveillance visit. Run the gap analysis and internal audit in-house against Annex A, and spend the money you save on remediation. And if you are starting from nothing, price the standalone route and the ISO 27001-first route side by side before assuming the new option is the cheaper one — for many small companies in 2026 it is not, because the ISMS certificate is what most customers ask for and the PIMS then costs 2.5 to 3.5 days on top. Our complete guide to ISO 27701 covers the implementation side in full.
If you already hold ISO 27001, typically $3,500 to $9,000 for the initial PIMS audit at a small company, based on 2.5 to 3.5 extra auditor days at $1,400 to $2,500 per day, then $700 to $2,500 a year in surveillance surcharges. A standalone PIMS audit for the same company runs closer to $5,000 to $14,000 initially. Travel is usually billed separately.
No. Since ISO/IEC 27701:2025 was published on 14 October 2025 the standard is standalone and a PIMS can be certified on its own. In practice, however, the add-on route is cheaper for anyone who already holds ISO 27001, and accredited standalone certification is only becoming available as bodies complete their ISO/IEC 27706 assessments through 2027.
The controller control set is longer — lawful basis, consent, notices, rights handling and transfers all sit with the controller — so the audit-time rules allocated a larger minimum surcharge to controllers (30% of ISMS audit time) than to processors (20%), and 50% to organizations that are both. The floor of 2.5 to 3.5 days matters more than the percentage for most small companies.
The transition adds very little to the ISO 27701 certification cost if you fold it into a recertification audit before 31 October 2028; about 0.5 to 1.5 extra auditor days at a surveillance visit; and $3,000 to $10,000 as a separate transition audit. The larger cost is rewriting your documentation to the three-table Annex A.
No. GDPR Article 42 certifications must be approved by the European Data Protection Board and certify processing activities. ISO 27701 certifies a management system. It is strong evidence of accountability, and it is what most security questionnaires ask for, but it is not an Article 42 seal.
For most small US companies the realistic ISO 27701 certification cost in 2026 is $6,000 to $20,000 in year one if you already hold ISO 27001 and $10,000 to $35,000 if you certify a standalone PIMS, with the certification body’s share set by two things you control: the role you declare and whether the visit shares an audit with your ISMS. Fix those two, buy the documentation rather than commissioning it, and check the body’s ISO/IEC 27706 accreditation before you pay for a standalone certificate.


September 21, 2026

September 20, 2026

September 20, 2026

September 19, 2026

September 19, 2026
