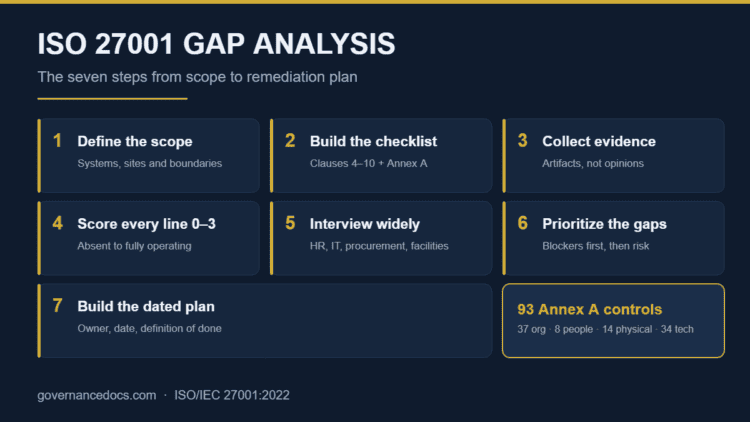
ISO 27001 Gap Analysis: The Complete 2026 Step-by-Step Guide Governance Docs09th August 2026 An ISO 27001 gap analysis compares what you actually do against clauses 4-10 and the 93 Annex A… Read More
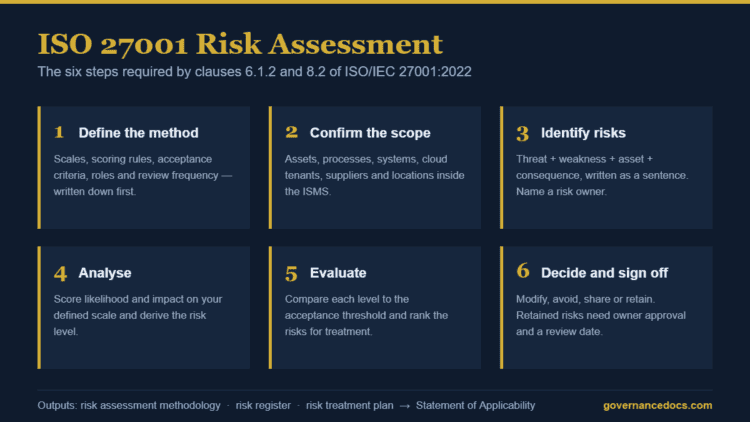
ISO 27001 Risk Assessment: The Complete 2026 Method Governance Docs07th August 2026 How to run an ISO 27001 risk assessment that survives an audit: what clause 6.1.2 actually requires, the… Read More
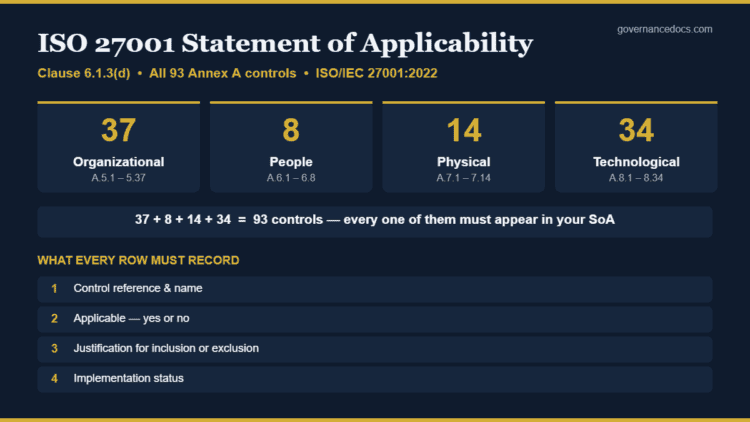
ISO 27001 Statement of Applicability: The Complete 2026 Guide Governance Docs06th August 2026 The ISO 27001 Statement of Applicability is mandatory under clause 6.1.3(d). What it must contain for all 93… Read More
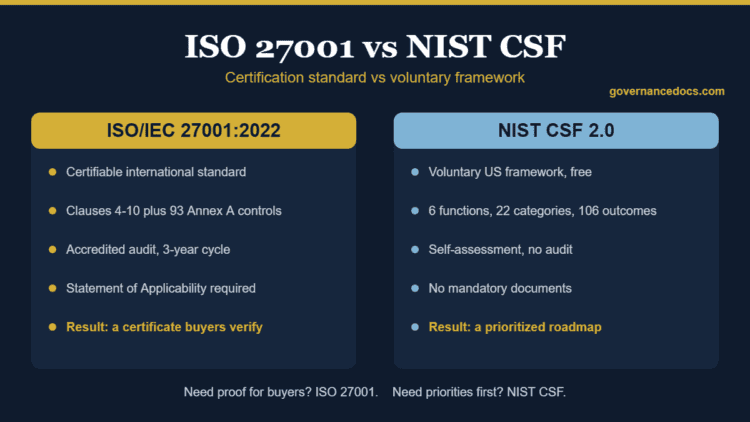
ISO 27001 vs NIST CSF: Which One Do You Need? (Complete 2026 Guide) Governance Docs05th August 2026 ISO 27001 vs NIST CSF compared: certification versus self-assessment, 93 Annex A controls versus 106 CSF outcomes, and… Read More
ISO 27001 Timeline: How Long Does Certification Take? Governance Docs22nd July 2026 A realistic look at the ISO 27001 timeline: how long certification takes by company size, the seven phases… Read More
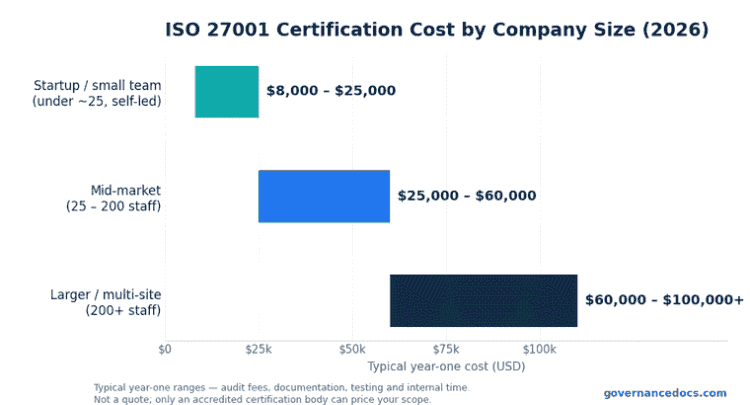
How Much Does ISO 27001 Certification Cost? (Complete 2026 Breakdown) Governance Docs22nd July 2026 A practical 2026 breakdown of what ISO 27001 certification actually costs, from certification-body audit fees to the internal… Read More
SOC 2 Cost & Timeline: What to Expect Governance Docs17th July 2026 What does SOC 2 cost and how long does it take? Here are the main cost factors, the… Read More
How to Prepare for a SOC 2 Audit Governance Docs17th July 2026 The SOC 2 audit tests your controls independently. Here is what it involves, the process, how to prepare,… Read More
SOC 2 Policies & Documentation Checklist Governance Docs17th July 2026 SOC 2 documentation turns security practice into an auditable report. Here are the essential policies, the evidence you… Read More
SOC 2 Type 1 vs Type 2: What’s the Difference? Governance Docs17th July 2026 SOC 2 Type 1 vs Type 2: one tests control design at a point in time, the other… Read More
SOC 2 Trust Services Criteria Explained Governance Docs17th July 2026 The SOC 2 Trust Services Criteria define what your auditor evaluates. Here are all five - security, availability,… Read More
ISO 27001 Policy Templates & Examples Governance Docs17th July 2026 The right ISO 27001 policy templates turn documentation from daunting to achievable. Here are the policies you need… Read More