About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesGap AssessmentsBusiness Impact AnalysisAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Tag: Topic: Information Security

Derived from the related-toolkit resolver (WPCode 12925). Used to scope MailPoet post-notification digests. Archives noindexed.

VDA ISA2027 for TISAX assessments

VDA ISA2027: What Changed and What It Means for Your TISAX Assessment

Governance Docs14th August 2026

VDA ISA2027 replaces ISA 6 for every TISAX assessment ordered from 1 January 2027. What changed in the…
Read More
ISO 27001 vs ISO 22301 — guide from Governance Docs

ISO 27001 vs ISO 22301: Which One Do You Actually Need?

Governance Docs13th August 2026

ISO 27001 vs ISO 22301 compared: information security versus business continuity, where the two overlap, and why 27001's…
Read More
ISO 27001 Implementation — guide from Governance Docs

How to Implement ISO 27001: A Ten-Step Plan

Governance Docs13th August 2026

A practical ISO 27001 implementation plan in ten steps for the 2022 edition, with realistic timings and the…
Read More
ISO 27017 and ISO 27018 cloud security controls

ISO 27017: Cloud Security Controls and What the 2026 Edition Changes

Governance Docs12th August 2026

ISO 27017 is not a certification. Here is what the standard actually contains, how it differs from ISO…
Read More
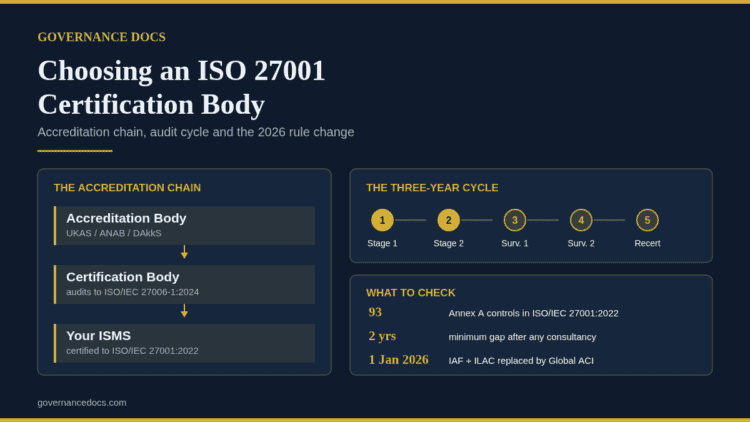
ISO 27001 certification body accreditation chain and three-year audit cycle

How to Choose an ISO 27001 Certification Body: The Complete 2026 Guide

Governance Docs12th August 2026

A practical 2026 guide to choosing an accredited ISO 27001 certification body: what changed on 1 January 2026,…
Read More
SWIFT CSP attestation: the five steps from architecture type to KYC-SA submission

SWIFT CSP Attestation: 5 Essential Steps to Comply

Governance Docs12th August 2026

If your institution is on the SWIFT network, security is not a matter of internal policy. SWIFT CSP attestation is an annual obligation: every member must attest against the Customer
Read More
HITRUST vs HIPAA compared: the federal law and the certifiable framework

HITRUST vs HIPAA: 5 Essential Differences and When to Certify

Governance Docs12th August 2026

Healthcare vendors get asked for HIPAA compliance constantly, and increasingly for HITRUST certification as well. The two are often spoken of as if they were alternatives, which they are not.
Read More
Cloud security certification routes compared: FedRAMP, StateRAMP, CSA STAR and BSI C5

Cloud Security Certification: 4 Essential Routes Compared

Governance Docs12th August 2026

Sooner or later a prospect asks a cloud provider to prove its security, and the honest first answer is a question: prove it to whom? There is no single cloud
Read More
NIST SP 800-30 risk assessment — the four-step method for assessing information security risk

NIST SP 800-30 Risk Assessment: The 4 Essential Steps

Governance Docs12th August 2026

A NIST SP 800-30 risk assessment is how you work out which risks actually matter to your organisation. The NIST Cybersecurity Framework tells you what good security looks like. It
Read More
Cybersecurity KRIs versus KPIs — what each indicator measures and what belongs in a board report

Cybersecurity KRIs vs KPIs: 5 Clear Rules for Board Reporting

Governance Docs12th August 2026

Every security team is asked the same question by its board sooner or later: are we getting safer? Answering it means reporting numbers — and that is where cybersecurity KRIs

Read More
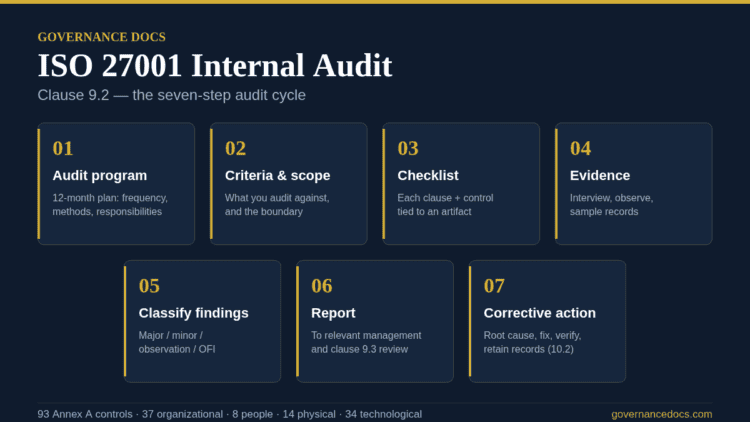
ISO 27001 internal audit seven-step cycle under clause 9.2, from audit program to corrective action

ISO 27001 Internal Audit: The Complete 2026 Guide to Clause 9.2

Governance Docs11th August 2026

What ISO 27001 clause 9.2 requires from an internal audit, who can run it, a seven-step method, and…
Read More
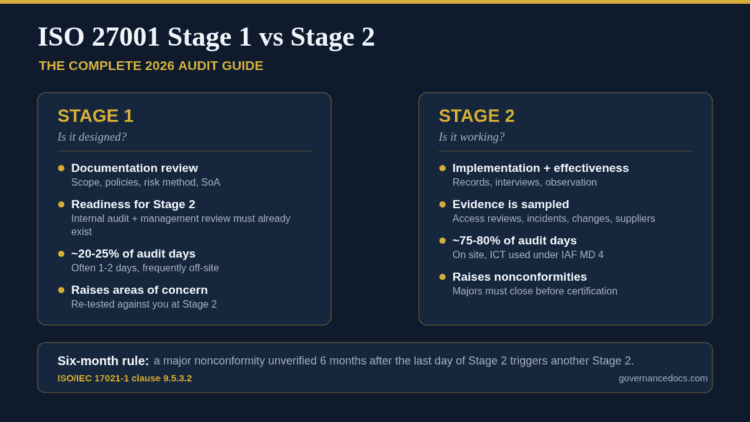
ISO 27001 Stage 1 vs Stage 2 audit comparison infographic

ISO 27001 Stage 1 vs Stage 2: The Complete 2026 Audit Guide

Governance Docs10th August 2026

ISO 27001 Stage 1 vs Stage 2 explained by clause: what each audit checks, how audit days are…
Read More
    ←
  • 1
  • …
  • 14
  • 15
  • 16
  • 17
  • 18
  • 19
  • →

Recent Posts

Business Impact Analysis questionnaire with 30 essential questions for governance and risk.
Business Impact Analysis Questionnaire: 30 Essential Questions (2026)

September 26, 2026

Comparison of BIA and Risk Assessment for governance and business continuity planning.
BIA vs Risk Assessment: The Definitive 2026 Comparison

September 25, 2026

Business Impact Analysis example from Governance Docs website.
Business Impact Analysis Example: A Complete Worked BIA (2026)

September 25, 2026

Infographic answering is ISO 13485 worth it in 2026 with audit days, QMSR date and MDSAP regulators
Is ISO 13485 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Is ISO 42001 worth it in 2026 — audit days, first-year cost and Annex A controls at a glance
Is ISO 42001 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Gap assessments
  • Business impact analysis
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA